

Airachnid-Burp-Extension
 spiderlabs/airachnid-burp-extension
A Burp Extension to test applications for vulnerability to the Web Cache Deception attack
penetration-testingvulnerability-scannersweb-application-exploitation+1
141
spiderlabs/airachnid-burp-extensionA Burp Extension to test applications for vulnerability to the Web Cache Deception attack
 hood3drob1n/cve-2016-3714
ImaegMagick Code Execution (CVE-2016-3714)
 dxc-strikeforce/burp-log4j-hammertime
Burp Active Scan extension to identify Log4j vulnerabilities CVE-2021-44228 and CVE-2021-45046
 mallo-m/cve-2024-47051
Mautic < 5.2.3 Authenticated RCE
 ll104567/cve-2023-5966
Proof-of-concept exploit for CVE-2023-5966, an arbitrary file upload vulnerability in EspoCRM 2.7.4 and earlier, enabling remote code execution via a…
 murrez/cve-2026-65891
CVE-2026-65891 PoC — Joomla Content Editor file rename vulnerability (auth required, fixed in JCE 2.20.2)
 yahiahamza/cve-2026-25099
Python exploit for Bludit CMS API unrestricted file upload leading to remote code execution, providing command execution and interactive shell for…
 fevar54/poc-funcional---cve-2026-45247-mirasvit-full-page-cache-warmer-rce-
PoC funcional de CVE-2026-45247: PHP Object Injection a RCE no autenticado en Mirasvit Full Page Cache (Magento 2).
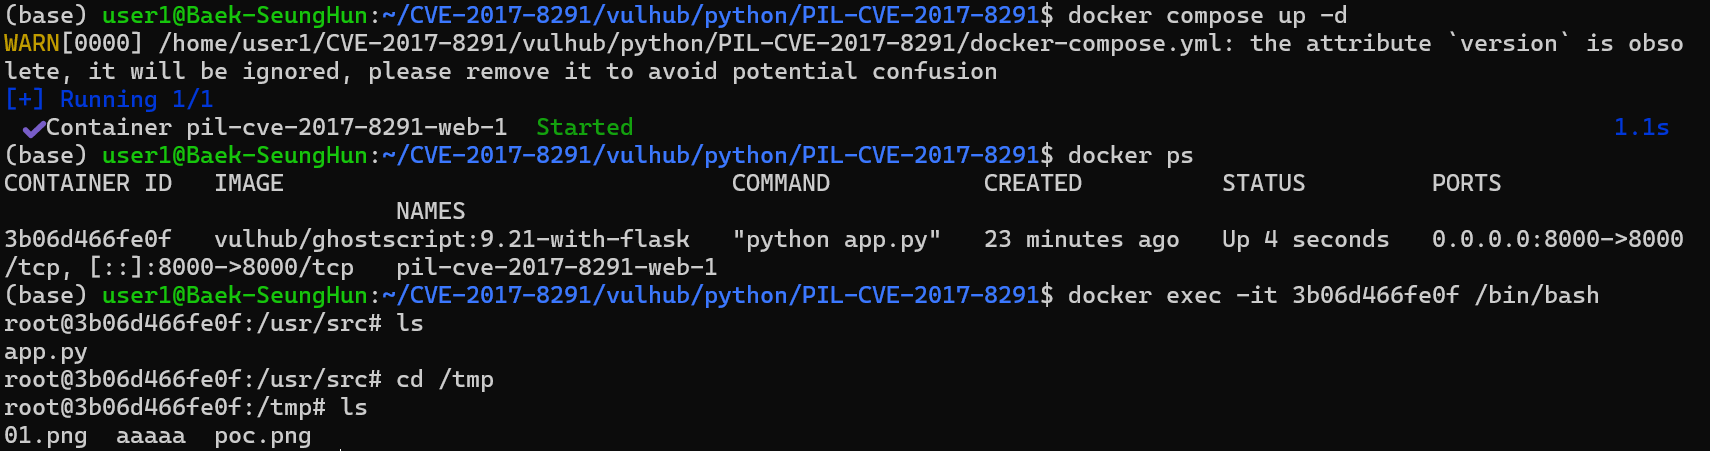 shun1403/pil-cve-2017-8291-study
Educational lab demonstrating CVE-2017-8291 (PIL/GhostScript RCE) via crafted EPS file upload with PNG extension, including Docker setup and PoC…
 ywh-jfellus/cve-2026-65761
Proof of Concept for CVE-2026-65761 - EasyStore Pro Unauthenticated SQL Injection via `filter_sortby`
 kimtangker/cve-2025-24893
CVE-2025-24893 tool
 george0papasotiriou/cve-2026-4040-race-condition-in-file-upload-leading-to-rce
Reproduces CVE-2026-4040: Flask upload server with TOCTOU race condition and exploit script demonstrating arbitrary remote code execution.
 oscar-mine/r2sae
Firefox extension for detecting and exploiting CVE-2025-55182 — Prototype Pollution RCE in Next.js React Server Actions
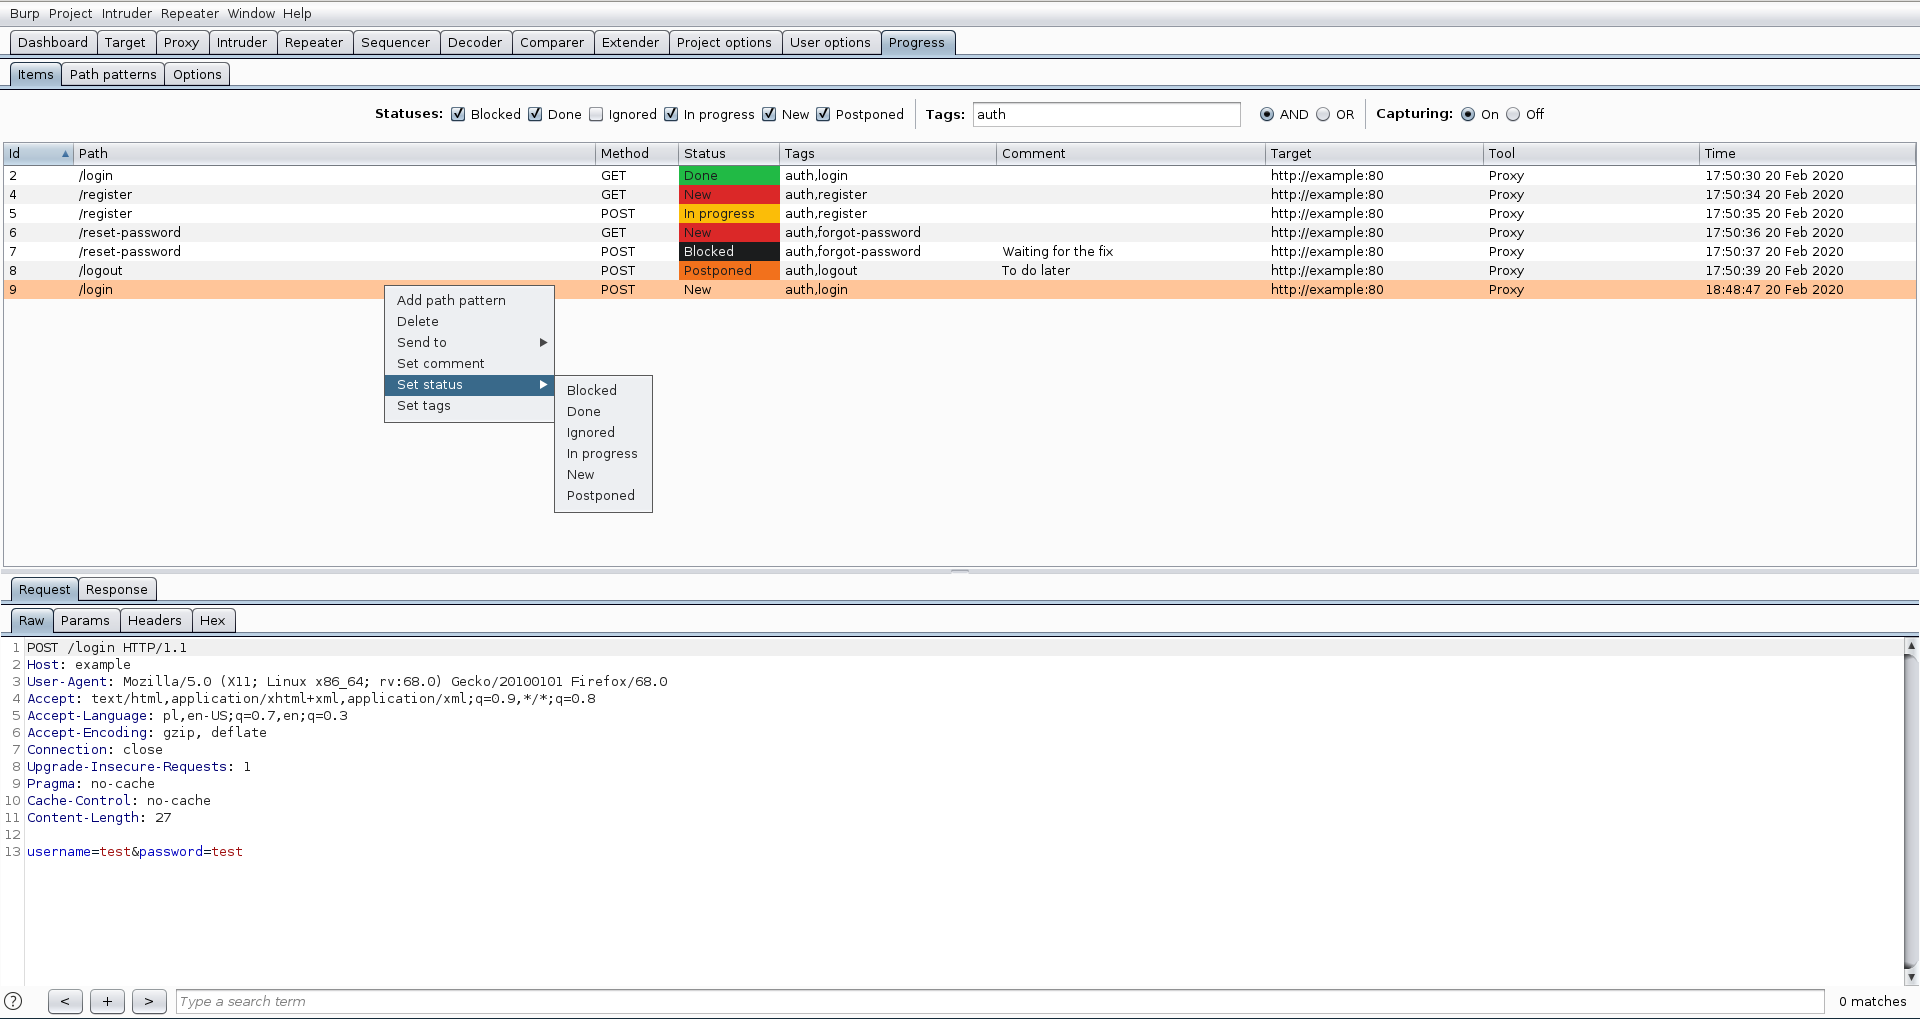 dariusztytko/progress-burp
Burp Suite extension to track vulnerability assessment progress
 ztgrace/mole
Framework for identifying and exploiting out-of-band (OOB) application vulnerabilities with a custom DNS/token server, Burp Suite extension, and…
 vulnbe/burpsuite-copy-as-xmlhttprequest
BurpSuite extension that converts HTTP requests into JavaScript XMLHttpRequest code for streamlined XSS proof-of-concept generation and web…
 nu11secur1ty/sqlmap-nu11secur1ty
Professional extension of sqlmap project
 chrissec2014/amasty-chekout-poc-rce
my poc for CVE-2026-53787