
mcpshield
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
api-security-testingcode-analysiscommand-and-control+3
csinexus/mcpshieldDrop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 shoucheng3/esapi__esapi-java-legacy_cve-2022-24891_2-2-3-1
OWASP Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input…
 d0n601/cve-2025-12720
g-FFL Cockpit <= 1.7.1 - Improper Authorization to Unauthenticated Product Deletion
 owasp/teach-appsec
OWASP teaching modules covering application security fundamentals including risk management, secure software development, and operations security for…
 imzanggg/cve-2026-24055-oauth-langfuse
 erev0s/vampi
Vulnerable REST API with OWASP top 10 vulnerabilities for security testing
 ine-labs/azuregoat
AzureGoat : A Damn Vulnerable Azure Infrastructure
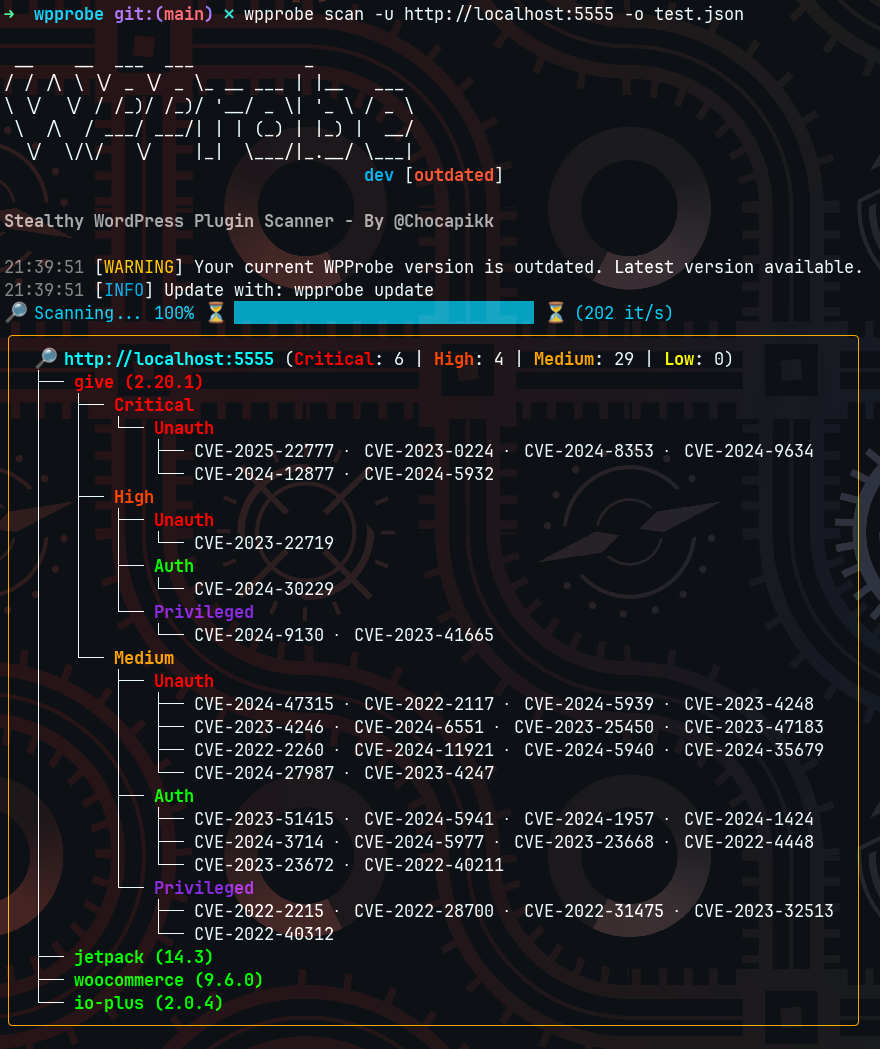 chocapikk/wpprobe
A fast WordPress plugin enumeration tool
 chrislockard/api_wordlist
A wordlist of API names for web application assessments
 owasp/apts
OWASP Autonomous Penetration Testing Standard
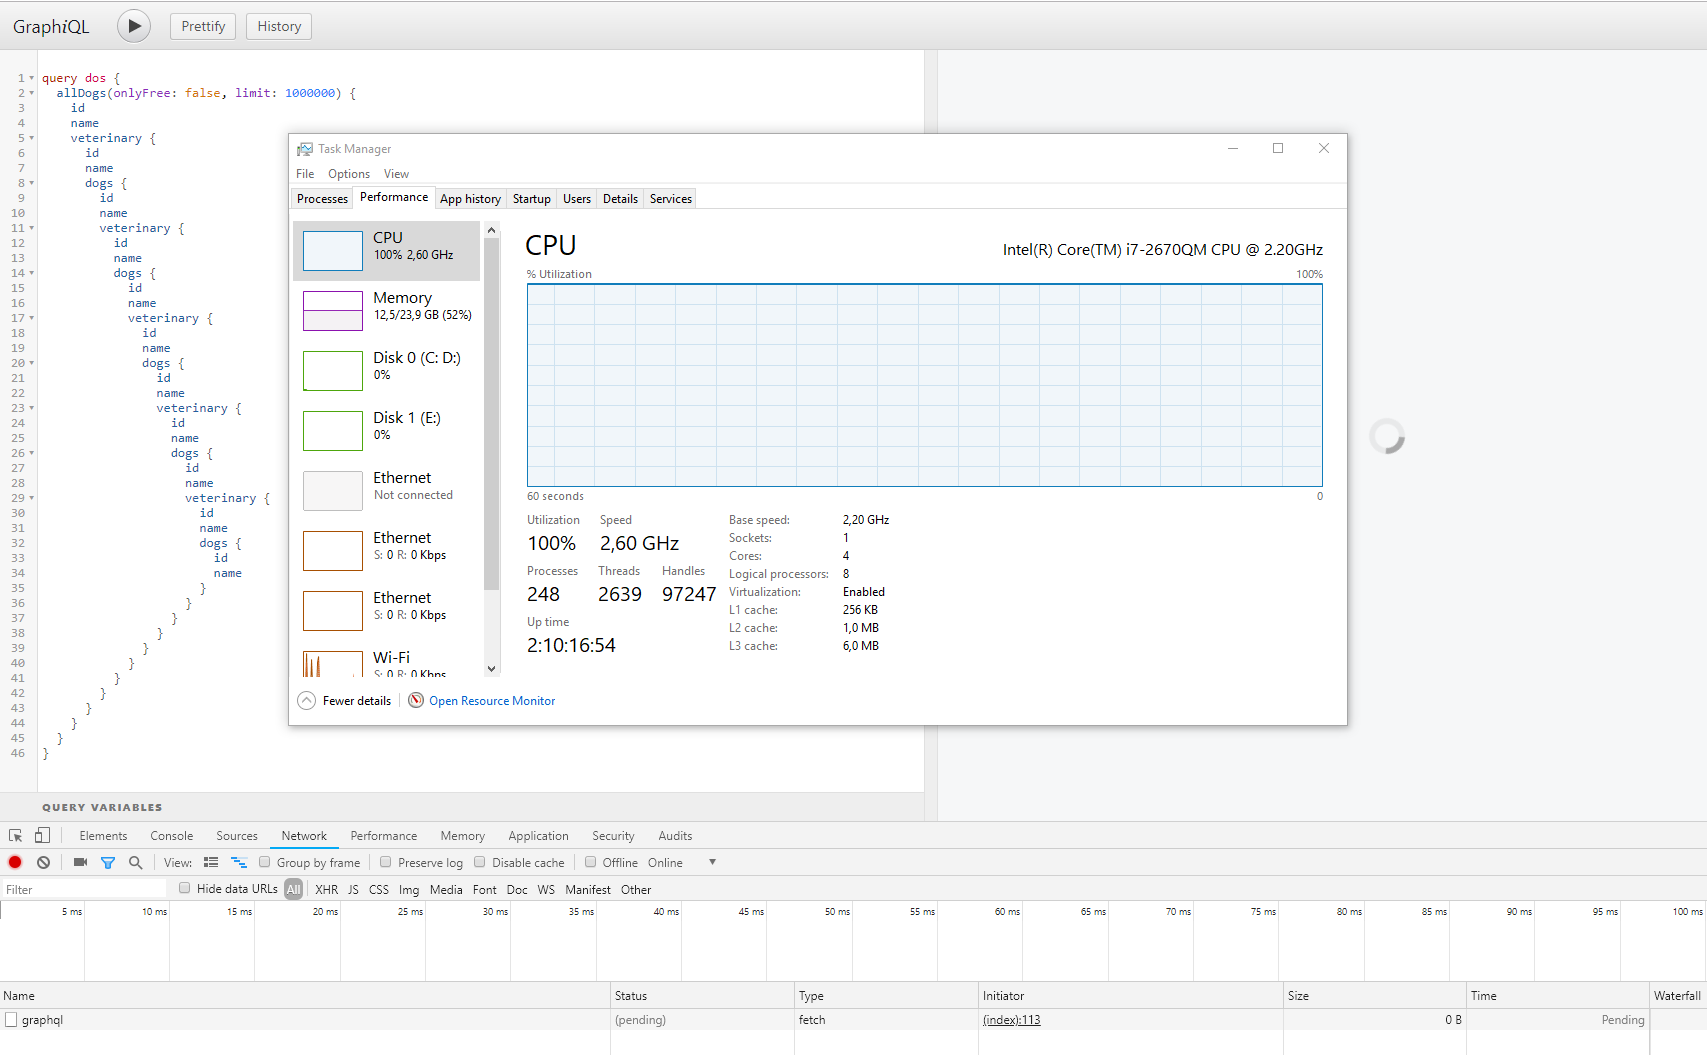 righettod/poc-graphql
Research on GraphQL from an AppSec point of view.
 mseclab/pyjfuzz
PyJFuzz - Python JSON Fuzzer
 aws/http-desync-guardian
Analyze HTTP requests to minimize risks of HTTP Desync attacks (precursor for HTTP request smuggling/splitting).
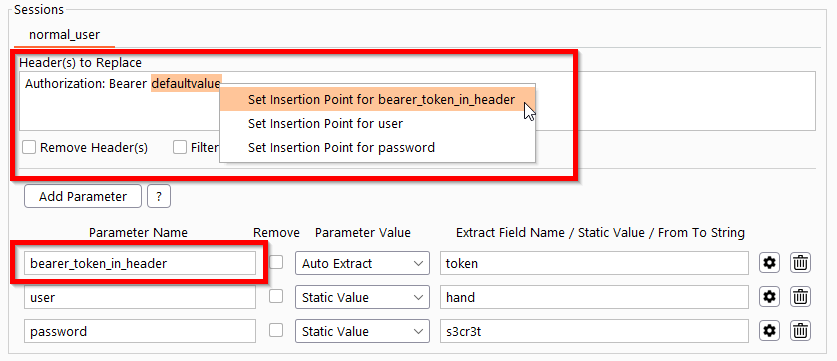 simioni87/auth_analyzer
Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.
 securityrat/securityrat
OWASP SecurityRAT (version 1.x) - Tool for handling security requirements in development
 dipakpanchal05/cve-2022-23808
Proof-of-concept exploit for CVE-2022-23808, a stored XSS vulnerability in phpMyAdmin 5.1.1 setup script, with payload and reproduction steps for…
 rub-nds/rest-attacker
Automated penetration testing framework for REST APIs with OpenAPI-driven test generation, 32 OWASP-based security tests, and built-in access control…