
EventLogin-CVE-2025-29969
 safebreach-labs/eventlogin-cve-2025-29969
Exploitation of CVE-2025-29969
exploitationlateral-movementpenetration-testing+3
68
safebreach-labs/eventlogin-cve-2025-29969Exploitation of CVE-2025-29969
 devbuihieu/cve-2025-33053-proof-of-concept
CVE-2025-33053 Proof Of Concept (PoC)
 synacktiv/kcmdump
Dump Kerberos tickets from the KCM database of SSSD
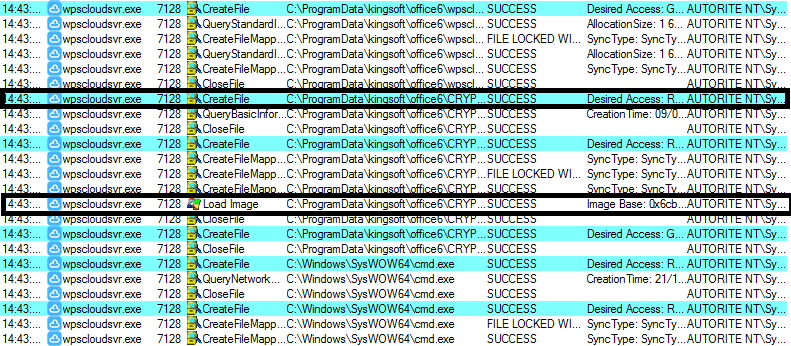 hadimed/kingsoft-wps-office-lpe
CVE-2022-25943
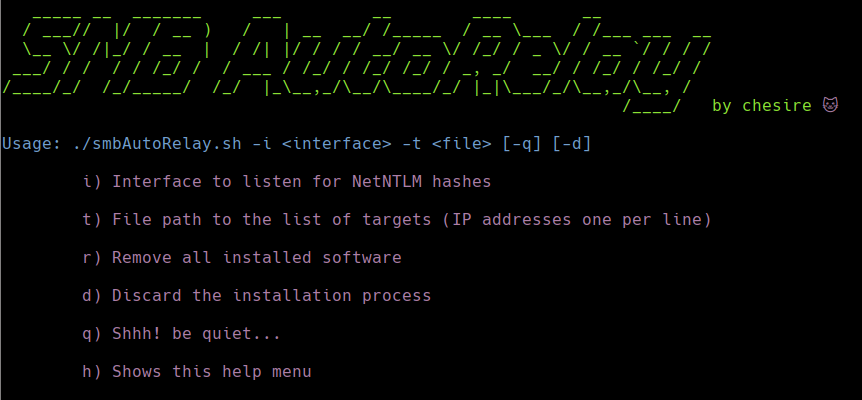 cheshireca7/smbautorelay
SMB Auto Relay provides the automation of SMB/NTLM Relay technique for pentesting and red teaming exercises in active directory environments.
 marcorosa/cnc-botnet-in-python
C&C Botnet written in Python with fabric
 davidcarliez/cve-2026-58635-poc
PoC for CVE-2026-58635: Windows Narrator Braille Local Privilege Escalation
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
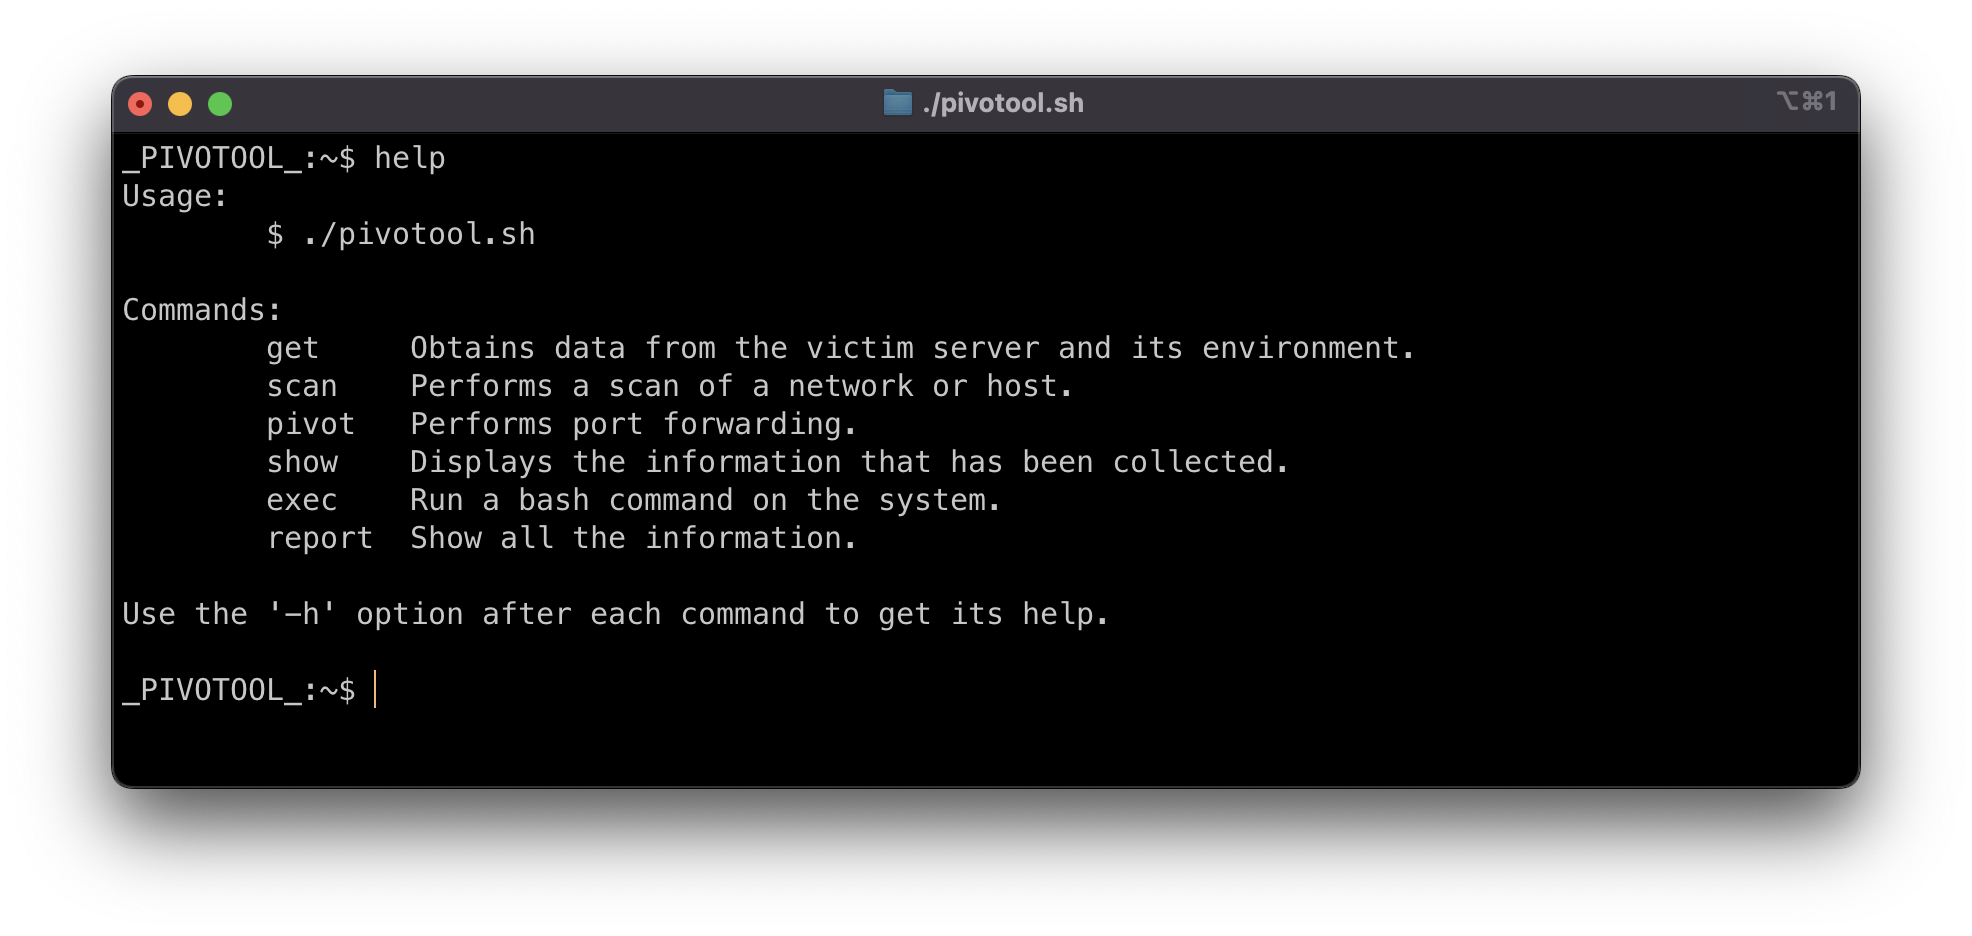 artusec/pivotool
Bash-based post-exploitation tool for semi-automated network pivoting, enabling lateral movement through compromised systems during penetration tests.
 auduongxuan/cve-2022-26809
Impacket-based exploit for PrintNightmare (CVE-2021-1675/CVE-2021-34527) enabling remote DLL execution via SMB, with scanning and mitigation guidance.
 al1ex/cve-2020-11652
Exploit for SaltStack CVEs (CVE-2020-11651/11652) enabling remote command execution on master/minions, file read/upload, and reverse shell.
 jackalkarlos/evilahenk
CVE-2026-6508 LiderAhenk Merkezi Yönetim Sistemi mimarisinde, uç birimler (agents) arası tüm istemcilerin birbirleri üzerinde 'root' yetkisiyle kod…
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
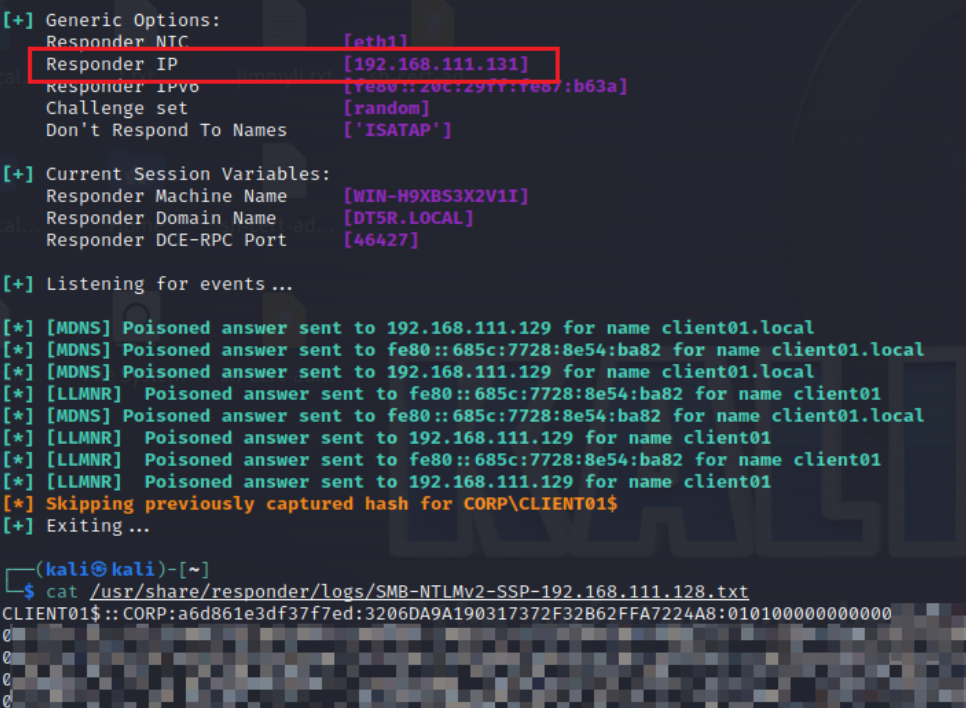 hagrid29/cve-2024-40586-windows-coerced-authentication-in-forticlient
Exploit for CVE-2024-40586: coerces Windows hosts to authenticate via a vulnerable FortiClient named pipe, enabling privilege escalation to SYSTEM or…
 3t4n/samba-3.0.24-cve-2007-2447-vunerable-
Vulnerable Samba 3.0.24 environment for reproducing CVE-2007-2447 command execution, intended for exploit testing and security research.
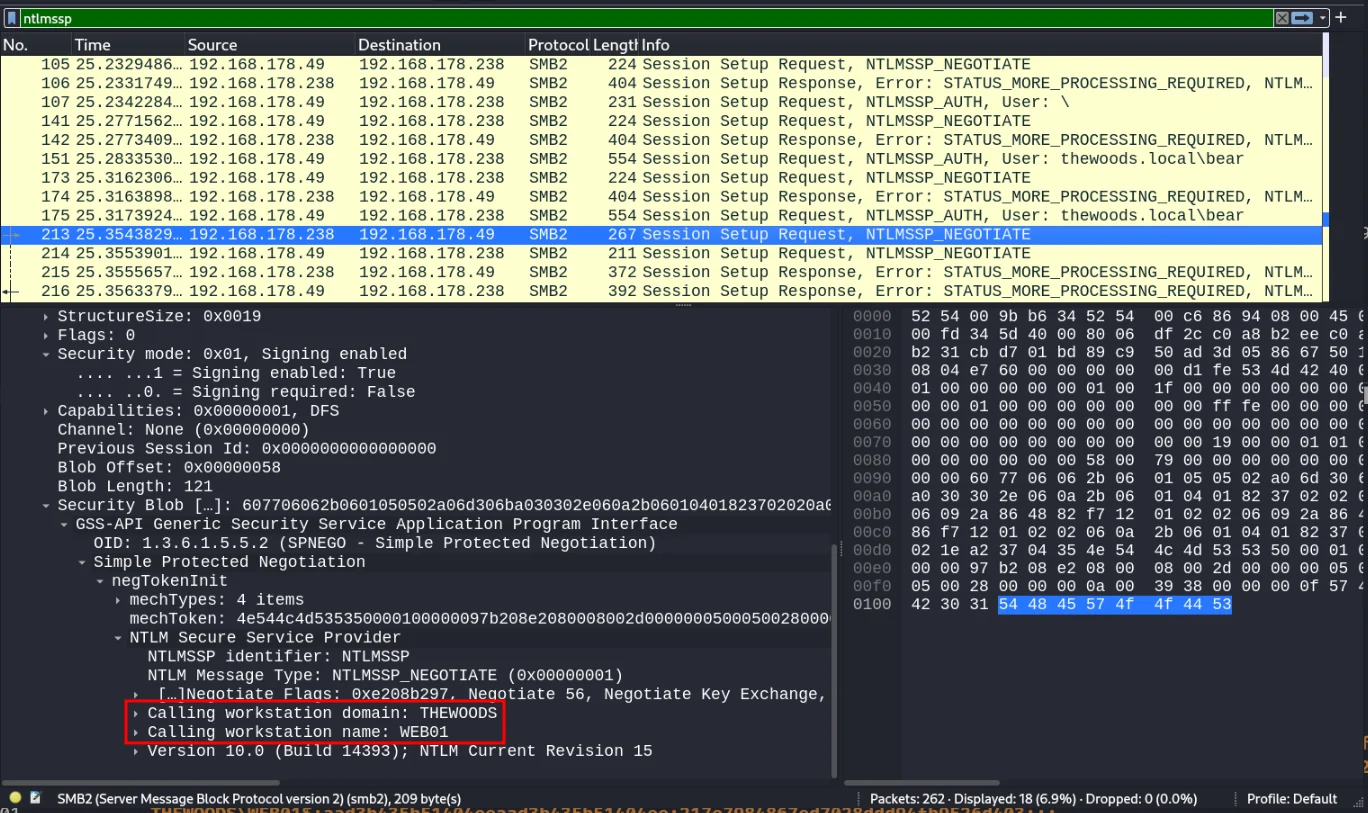 starscow/cve-2025-33073
PoC Exploit for the NTLM reflection SMB flaw.
 z50913/cve-2020-27955
Proof-of-concept exploit for CVE-2020-27955 in Git-LFS, demonstrating remote code execution via a crafted git clone operation to obtain a reverse…