CVE-2023-52709-PoC
PoC for 2023-52709 - TI Bluetooth stack can fail to generate a resolvable Random Private Address (RPA) leading to DoS for already bonded peer devices.

PoC for 2023-52709 - TI Bluetooth stack can fail to generate a resolvable Random Private Address (RPA) leading to DoS for already bonded peer devices.

Bluetooth Low Energy (BLE) scanner with Resolvable Private Address (RPA) resolution using Identity Resolving Keys (IRKs)

IPv6 address spoofing with the Neighbor Discovery Protocol

Wi-Fi portal authentication bypass exploit using MAC address spoofing to gain unauthorized network access, demonstrated on enterprise AC and AP…

Python PoC for CVE-2026-0101 demonstrating BLE address spoofing via replay of a captured Resolvable Private Address to impersonate a trusted…

Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…

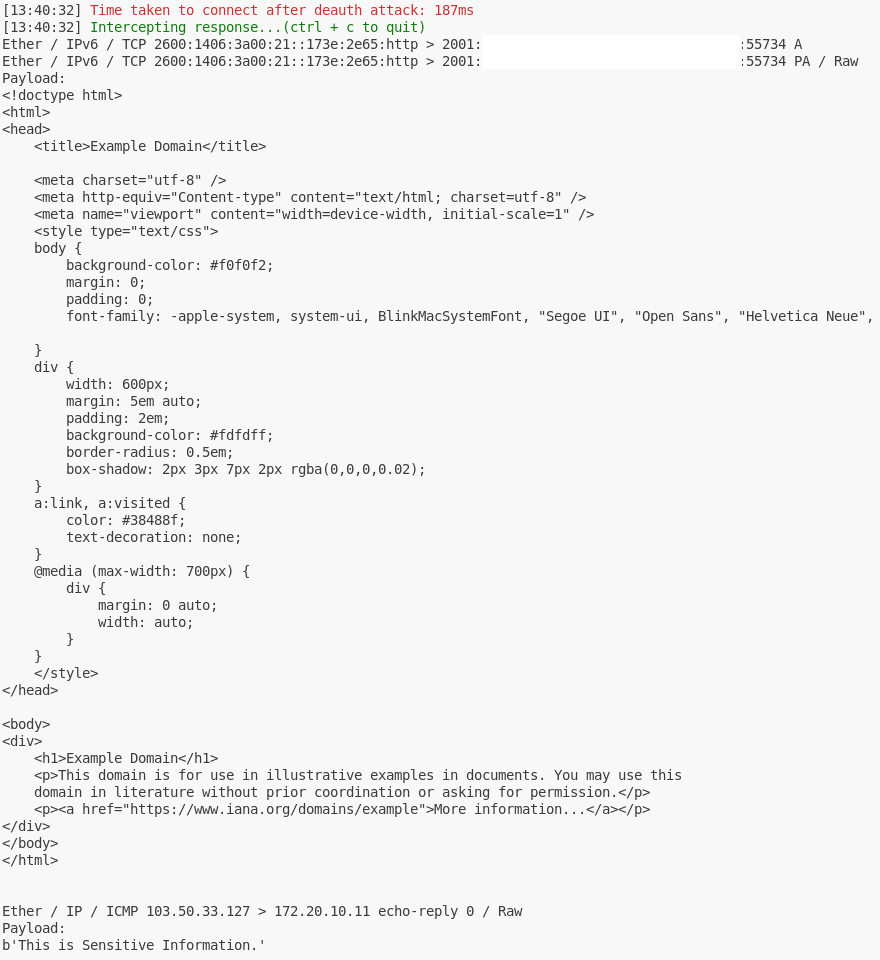
Proof-of-concept exploit for CVE-2022-47522 demonstrating Wi-Fi frame interception via deauthentication attack and MAC address spoofing to capture…

wireless hacking - This is automated wireless hacking tool

WiFi Penetration Testing Guide

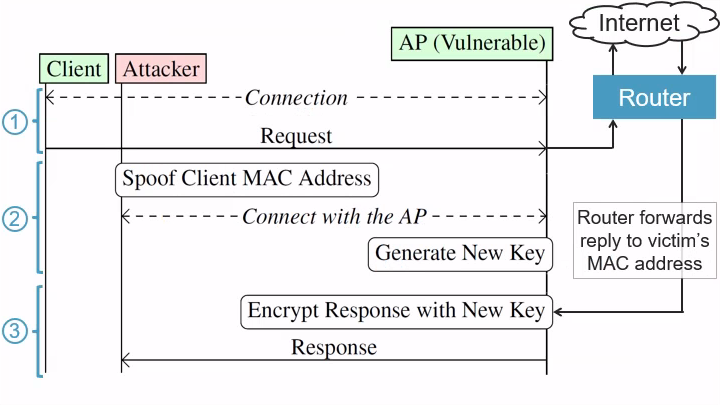
MacStealer: Wi-Fi Client Isolation Bypass

nOBEX allows emulating the PBAP, MAP, and HFP profiles to test vehicle infotainment systems and similar devices using these profiles

Details of CVE-2020-14292