
CVE-2021-1965
 sqrtrev/cve-2021-1965
Proof-of-concept exploit for CVE-2021-1965, a WiFi zero-click RCE in Android's MBSSID parsing, causing buffer overflow and device reboot.
exploitationmobile-securitypenetration-testing+2
3
sqrtrev/cve-2021-1965Proof-of-concept exploit for CVE-2021-1965, a WiFi zero-click RCE in Android's MBSSID parsing, causing buffer overflow and device reboot.
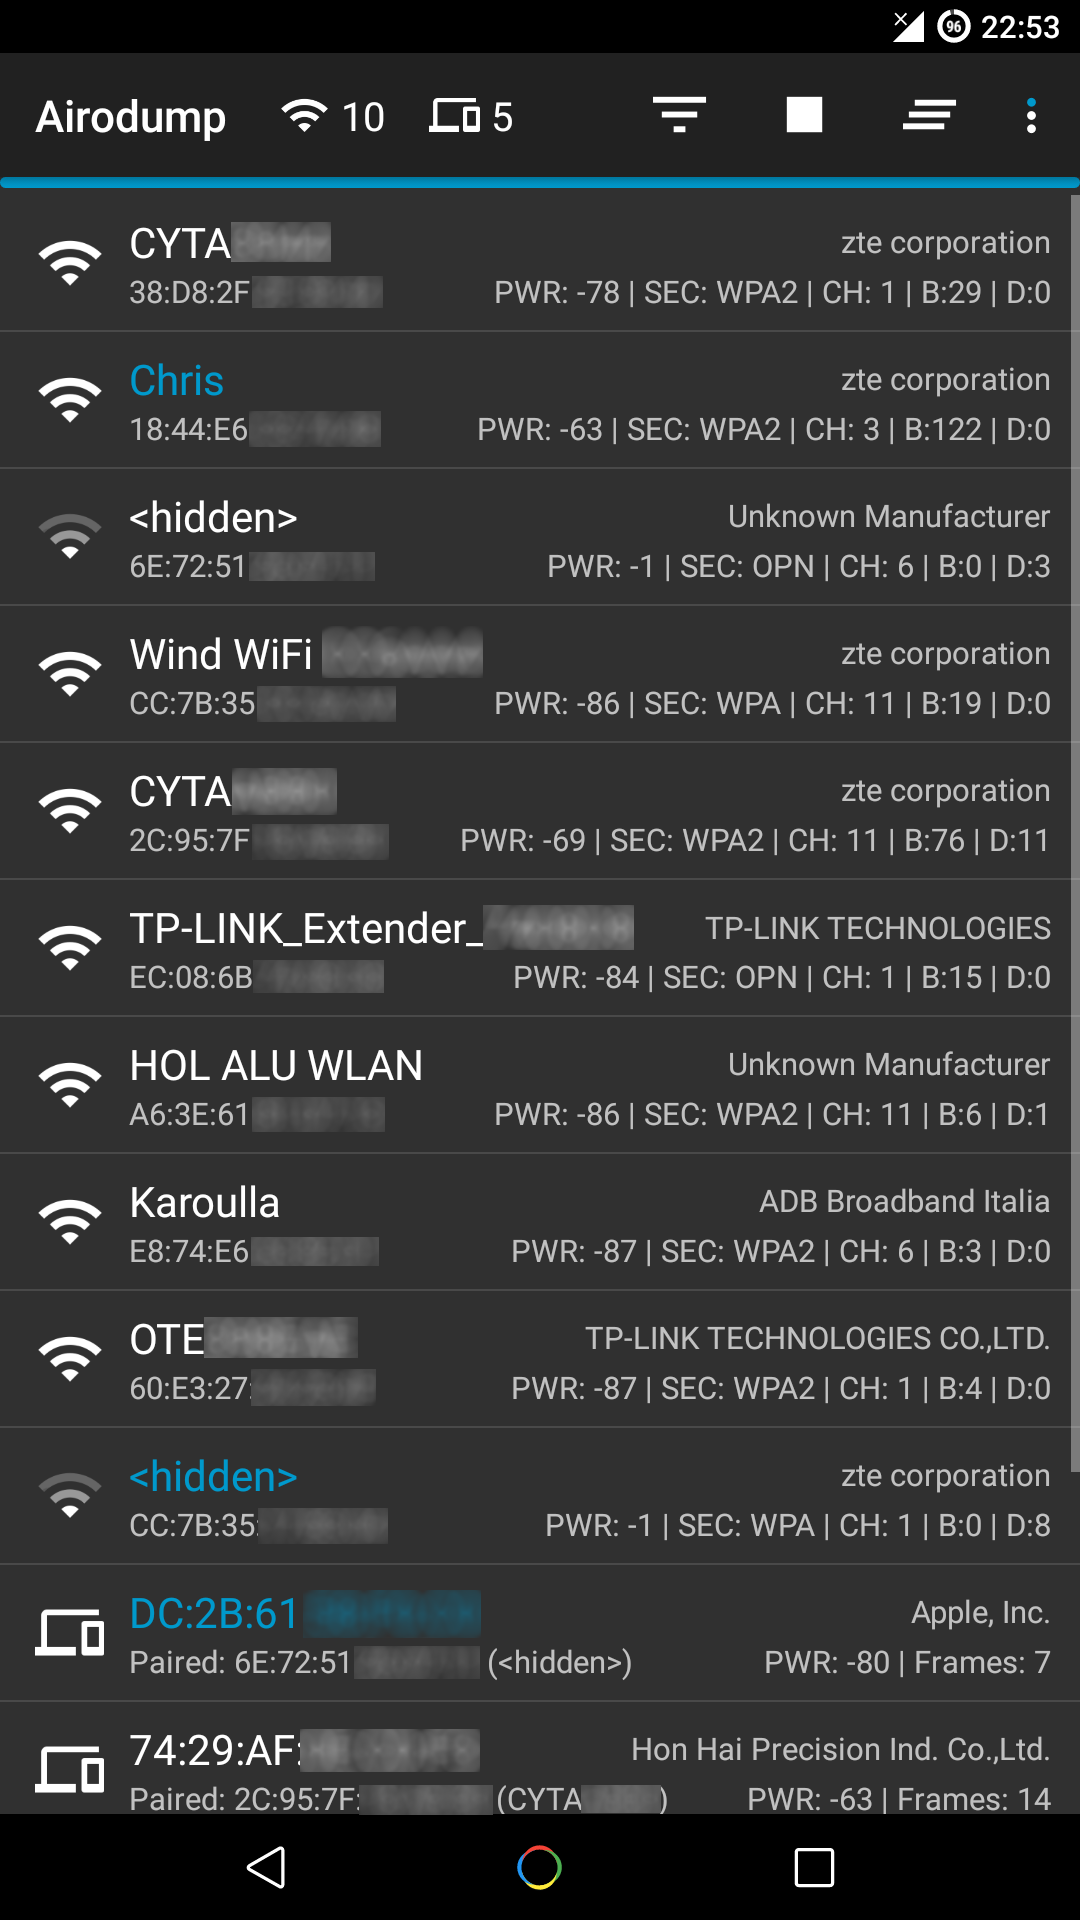 chrisk44/hijacker
Aircrack, Airodump, Aireplay, MDK3 and Reaver GUI Application for Android
 nanopathi/system_bt_aosp10_r33_cve-2021-0476
Android Bluetooth stack (AOSP 10 r33) containing CVE-2021-0476 for vulnerability analysis, exploitation testing, and security research.
 shaikusaf/external_wpa_supplicant_8_aosp10_r33cve-2021-0326
Android Wi-Fi vulnerability research repository containing patched wpa_supplicant source for CVE-2021-0326, enabling analysis and testing of the…
 0n1con3/fluxer
FluxER - The bash script which installs and runs the Fluxion tool inside Termux. The wireless security auditing tool used to perform WPA/WPA2…
 librepods-org/librepods
AirPods liberated from Apple's ecosystem.
 permissionlesstech/bitchat-android
Decentralized, encrypted peer-to-peer messaging app over Bluetooth mesh networks. No internet, servers, or phone numbers required. Features X25519 +…
 may215/awesome-termux-hacking
⚡️An awesome list of the best Termux hacking tools
 nfcgate/nfcgate
An NFC research toolkit application for Android
 fo-000/bluing
An intelligence gathering tool for hacking Bluetooth
 zalexdev/wpair-app
WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…
 ojasookert/cve-2017-0781
Blueborne CVE-2017-0781 Android heap overflow vulnerability
 mailinneberg/broadpwn
Broadpwn bug (CVE-2017-9417)
 loukious/android_kernel_xiaomi_sm8150
Nethunter kernel for the POCO X3 Pro (vayu) based on crDroid's kernel.
 spiralbl0ck/remote-buffer-overflow-over-wifi_stack-in-wpa_supplicant-binary-in-android-11-platform-samsung-a20e
Remote buffer overflow over wifi_stack in wpa_supplicant binary in android 11, platform:samsung a20e, stock options so like works out of the box
 zhuowei/blueshrimp
Proof-of-concept for CVE-2025-48593
 irsl/lgosp-poc
LG On Screen Phone authentication bypass PoC (CVE-2014-8757)
 pushkarreddyy/radioguard
Zero-Trust Cellular Defense Sub-Service for Android (IMSI-Catcher, 2G SMS Blaster, and 4G aLTEr Detection & Safe Routing)