AirStrike
 redcode-labs/airstrike
Automatically grab and crack WPA-2 handshakes with distributed client-server architecture
password-crackingpenetration-testingwi-fi-auditing+1
198
redcode-labs/airstrikeAutomatically grab and crack WPA-2 handshakes with distributed client-server architecture
 jpaulmora/pyrit
The famous WPA precomputed cracker, Migrated from Google.
 hash3lizer/wifibroot
A Wireless (WPA/WPA2) Pentest/Cracking tool. Captures & Crack 4-way handshake and PMKID key. Also, supports a deauthentication/jammer mode for stress…
 blunderbuss-wctf/wacker
A WPA3 dictionary cracker
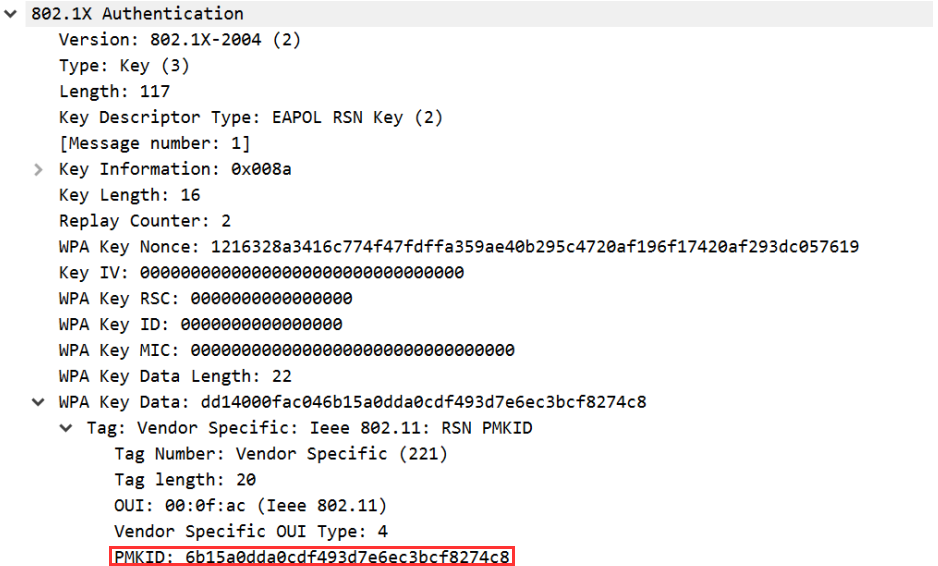 n0mi1k/pmkidcracker
A tool to crack WPA2 passphrase with PMKID value without clients or de-authentication
 wiire-a/cve-2017-9476
Hidden AP with Deterministic Credentials
 silentghostx/ht-wps-breaker
HT-WPS Breaker (High Touch WPS Breaker)
 derv82/wifite2
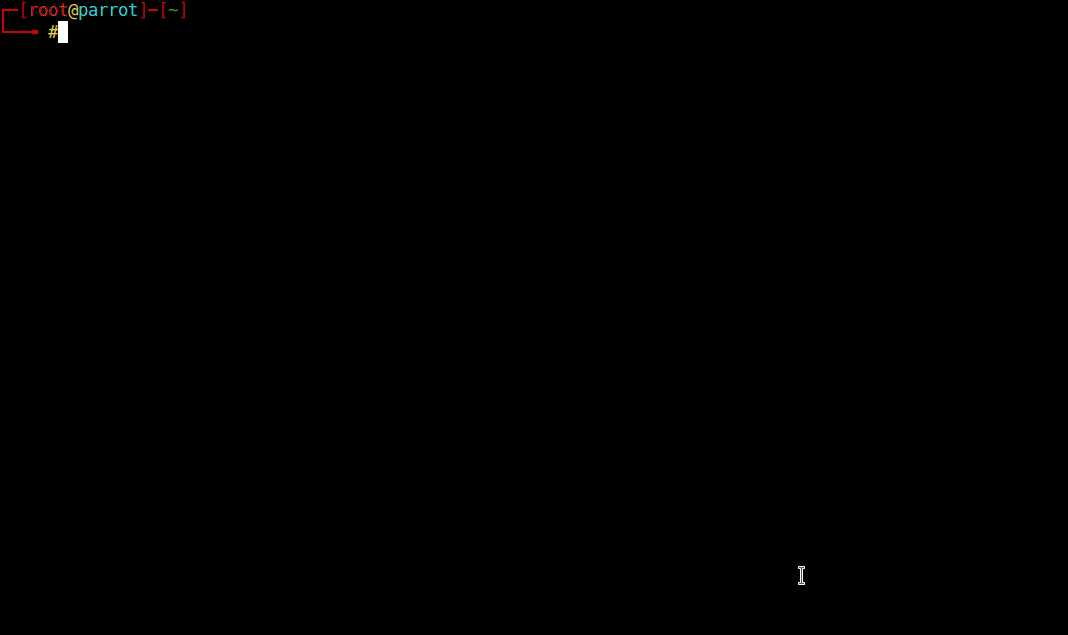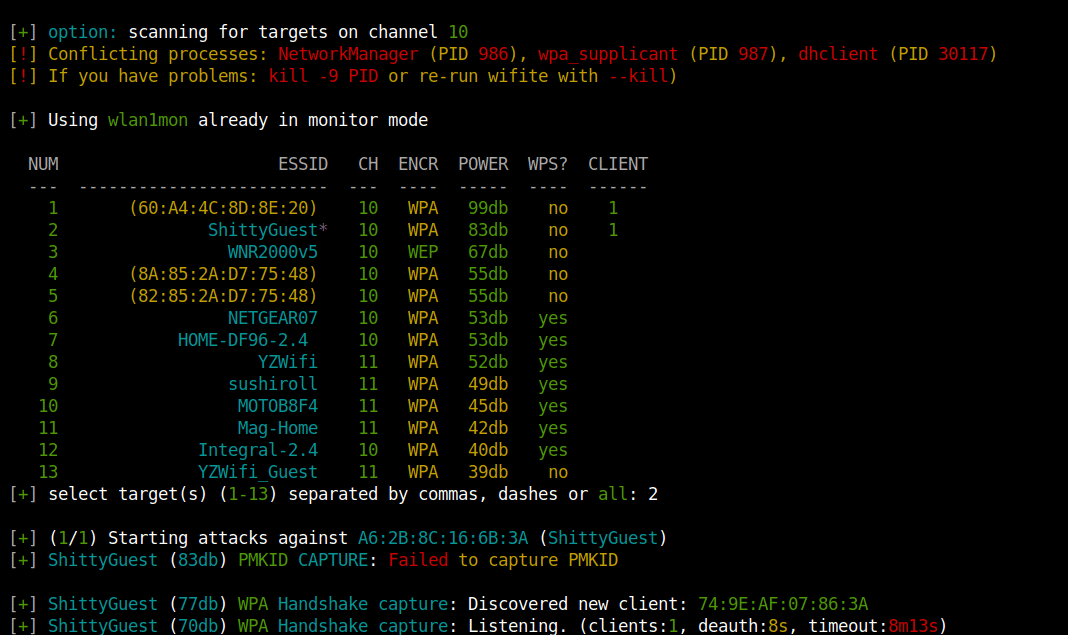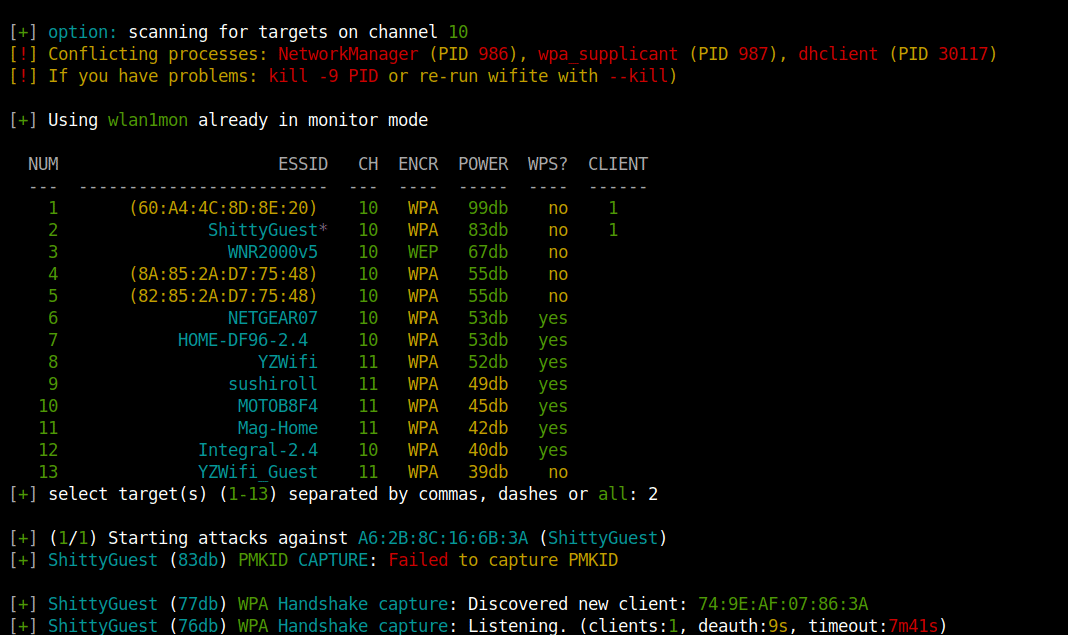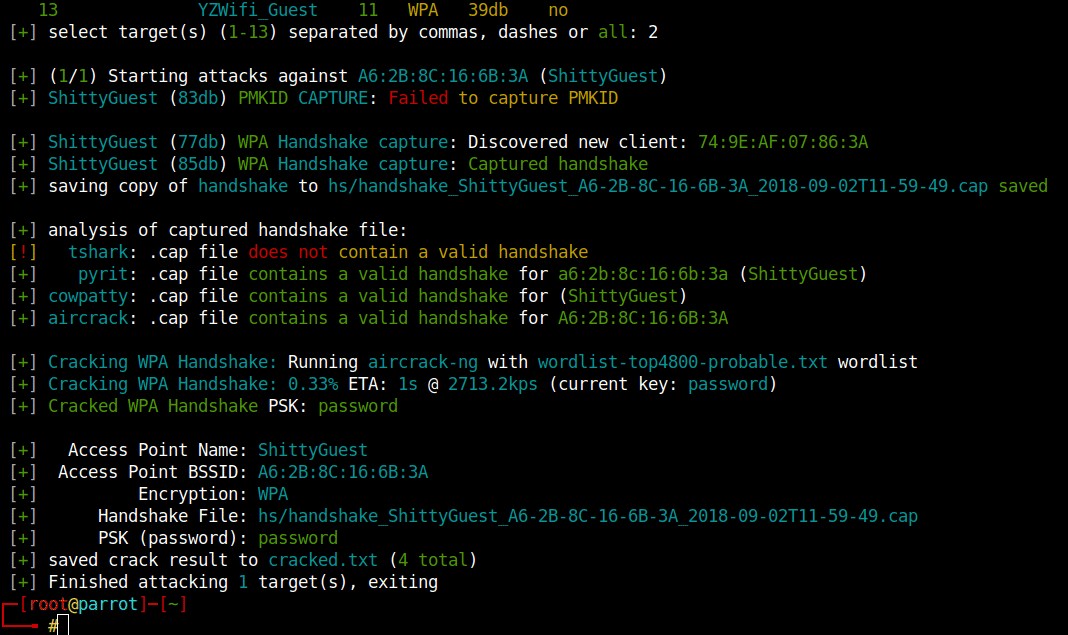
Rewrite of the popular wireless network auditor, "wifite"
 esc0rtd3w/wifi-hacker
Shell Script For Attacking Wireless Connections Using Built-In Kali Tools. Supports All Securities (WEP, WPS, WPA, WPA2)
 t6x/reaver-wps-fork-t6x
Brute-force attack tool against WPS registrar PINs to recover WPA/WPA2 passphrases, supporting online brute force and offline Pixie Dust attacks on…
 tylous/auto_eap
Automated Brute-Force Login Attacks Against EAP Networks.
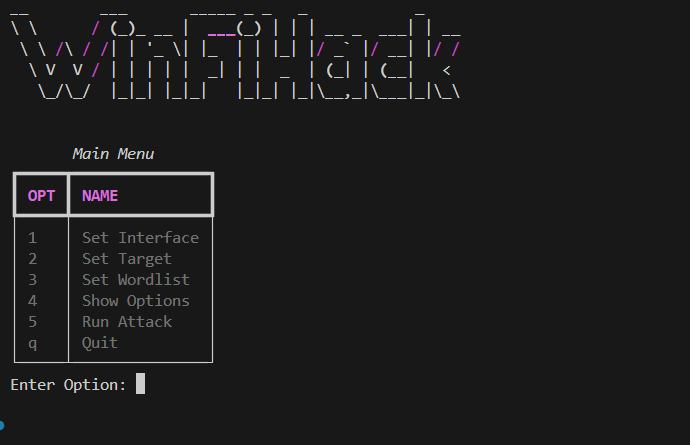 morpheuslord/winfihack
A windows Wifi Brute forcing utility which is an extremely old method but still works without the requirement of external dependencies.
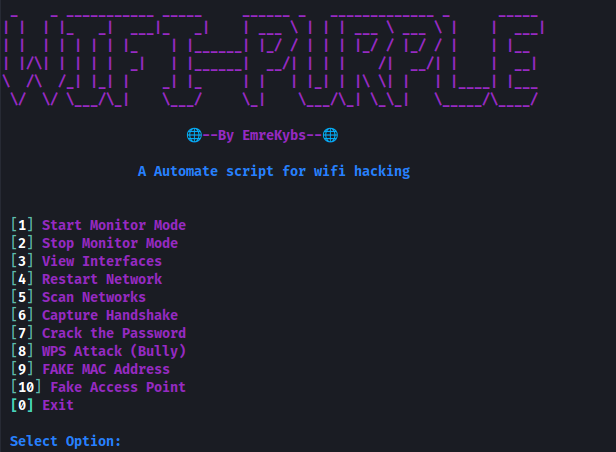 emrekybs/wifi-purple
Automated WiFi security testing script that captures handshakes and performs deauthentication attacks using airmon-ng and wifite for wireless…
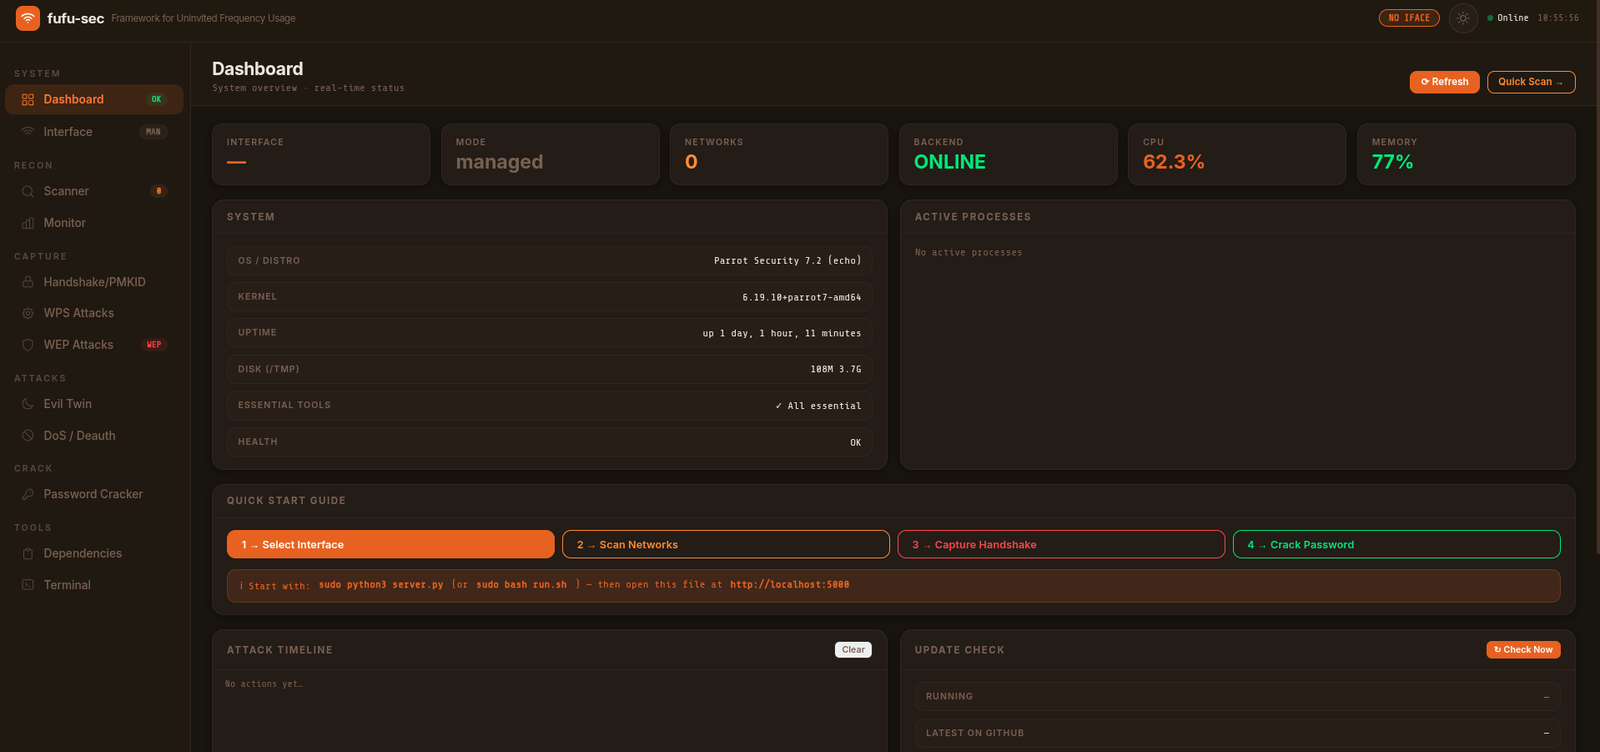 kyllr-qwen/fufu-sec
Framework for Uninvited Frequency Usage