
CVE-2025-36911-exploit
 penthertz/cve-2025-36911-exploit
Exploit of the CVE-2025-36911 vulnerability in Python for testing our own equipment
bluetooth-securityexploitationpenetration-testing+3
27
penthertz/cve-2025-36911-exploitExploit of the CVE-2025-36911 vulnerability in Python for testing our own equipment
 syss-research/radio-hackbox
PoC tool to demonstrate vulnerabilities in wireless input devices
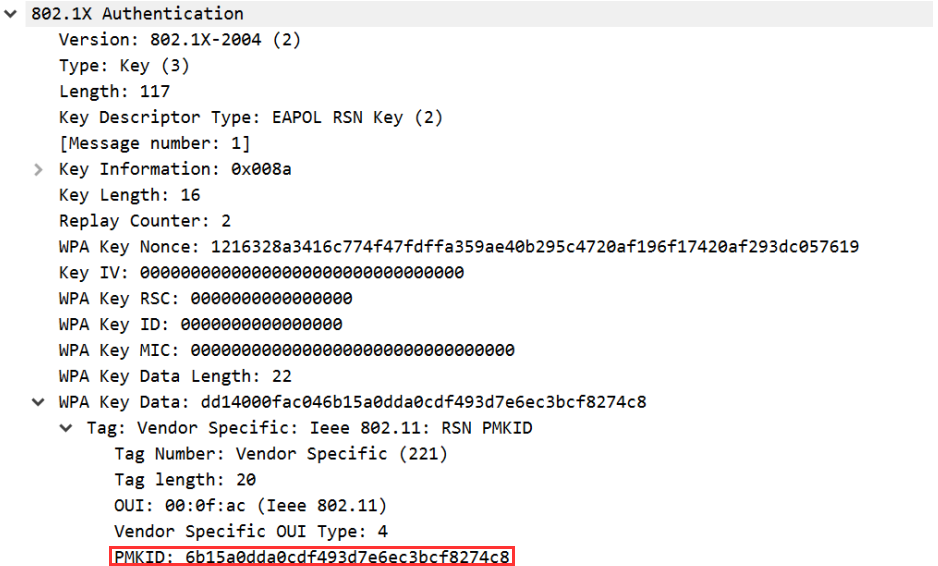 n0mi1k/pmkidcracker
A tool to crack WPA2 passphrase with PMKID value without clients or de-authentication
 eldraco/salamandra
Salamandra is a tool to find spy microphones that use radio freq to transmit. It uses SDR.
 cracksoft900/blue-borne
BlueBorne Exploits & Framework This repository contains a PoC code of various exploits for the BlueBorne vulnerabilities. Under 'android' exploits…
 t6x/reaver-wps-fork-t6x
Brute-force attack tool against WPS registrar PINs to recover WPA/WPA2 passphrases, supporting online brute force and offline Pixie Dust attacks on…
 syworks/wireless-ids
Ability to detect suspicious activity such as (WEP/WPA/WPS) attack by sniffing the air for wireless packets.
 silentghostx/ht-wps-breaker
HT-WPS Breaker (High Touch WPS Breaker)
 zerbea/hcxdumptool
Small tool to capture packets from wlan devices.
 z4nzu/hackingtool
All-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing,…
 xtr4nge/fruitywifi
FruityWiFi is a wireless network auditing tool. The application can be installed in any Debian based system (Jessie) adding the extra packages.…
 akabe1/kr00ker
An experimental script PoC for Kr00k vulnerability (CVE-2019-15126)
 x3omdax/penbox
PenBox - A Penetration Testing Framework - The Tool With All The Tools , The Hacker's Repo
 salgio/esptouchcatcher
eWeLinkESPT is a tool that automatically decodes and decrypts the WiFi network credentials transmitted to a supported ESP-based IoT device by the…
 fluxionnetwork/fluxion
Automated WPA/WPA2 phishing tool that captures handshakes, spawns a rogue access point, and lures users to a captive portal to harvest credentials…
 aalex954/whisperpair-poc-tool
A security research tool that identifies and demonstrates the CVE-2025-36911: Fast Pair Pairing Mode Bypass vulnerability
