
nfcgate
 nfcgate/nfcgate
An NFC research toolkit application for Android
android-securityeducationexploitation+5
nfcgate/nfcgateAn NFC research toolkit application for Android
 pushkarreddyy/radioguard
Zero-Trust Cellular Defense Sub-Service for Android (IMSI-Catcher, 2G SMS Blaster, and 4G aLTEr Detection & Safe Routing)
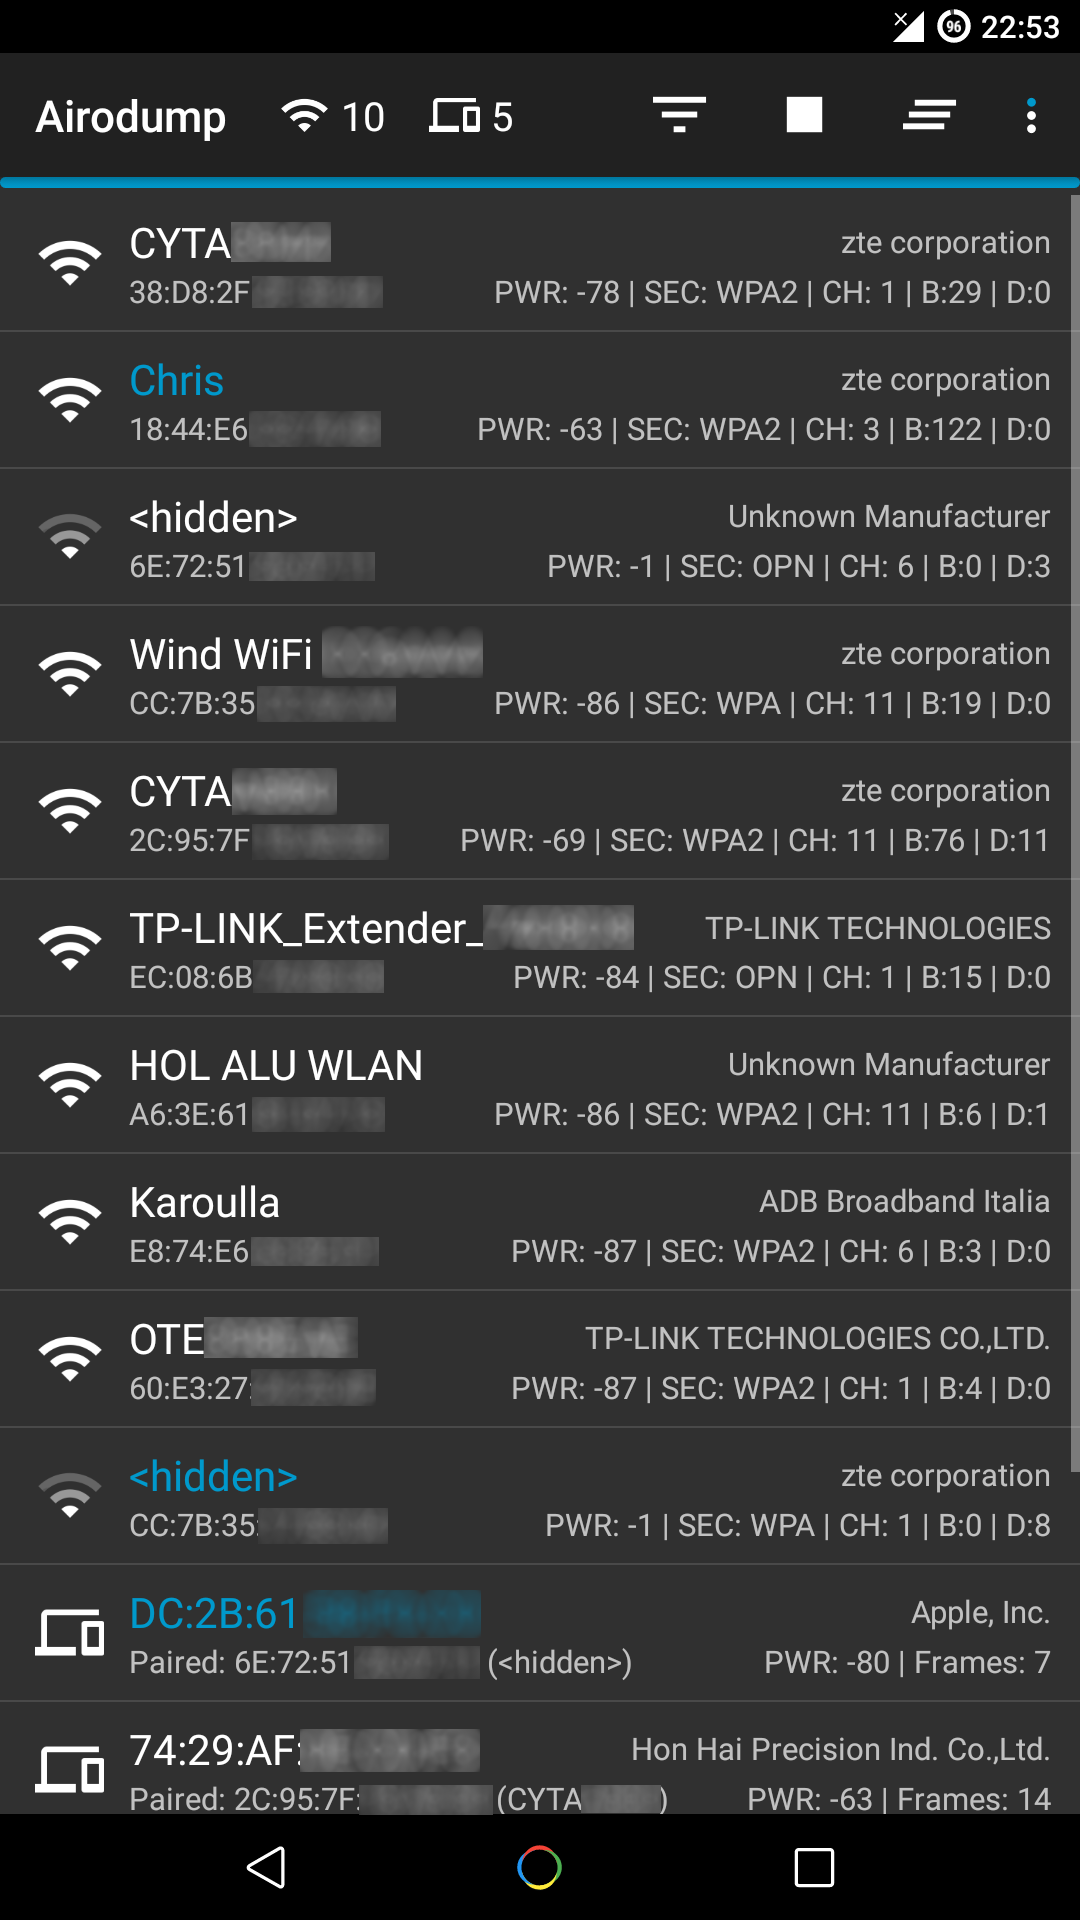 chrisk44/hijacker
Aircrack, Airodump, Aireplay, MDK3 and Reaver GUI Application for Android
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 ojasookert/cve-2017-0781
Blueborne CVE-2017-0781 Android heap overflow vulnerability
 spiralbl0ck/remote-buffer-overflow-over-wifi_stack-in-wpa_supplicant-binary-in-android-11-platform-samsung-a20e
Remote buffer overflow over wifi_stack in wpa_supplicant binary in android 11, platform:samsung a20e, stock options so like works out of the box
 mretallack/androidauto
Open-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025
 bloodcode-spasov/ble-cve2025-attack-new-version
# android-ble-cve-2025-4866 🔐 **PoC za CVE-2025-4866 — Android BLE ranjivost (javna verzija)** 📡 Iskorišćavanje slabosti u BLE autorizaciji na…
 fredevsec/cve-2026-0073
0-Click RCE Android Adb TLS Wireless Debugging
 uthrasri/frameworks_opt_net_wifi_cve-2021-0390
Android Wi-Fi framework patch for CVE-2021-0390, addressing a remote code execution vulnerability in the Wi-Fi subsystem.
 nanopathi/system_bt_aosp10_r33_cve-2021-0476
Android Bluetooth stack (AOSP 10 r33) containing CVE-2021-0476 for vulnerability analysis, exploitation testing, and security research.
 nanopathi/system_bt_aosp10_r33_cve-2021-0522
Android Bluetooth stack (system/bt) source code including patch for CVE-2021-0522 privilege escalation vulnerability.
 trinadh465/system_bt_aosp10_r33_cve-2021-0589
Patched Android Bluetooth stack (AOSP10) addressing CVE-2021-0589, with build instructions for AOSP and Linux.
 trinadh465/packages_apps_nfc_aosp10_r33_cve-2020-0453
Android NFC package patched for CVE-2020-0453, addressing a security vulnerability in the NFC component.
 satheesh575555/external_wpa_supplicant_8_aosp10_r33_cve-2021-0326
Patched wpa_supplicant and hostapd for Android 10 (r33) addressing CVE-2021-0326 vulnerability in Wi-Fi client and AP components, enhancing wireless…
 shaikusaf/external_wpa_supplicant_8_aosp10_r33cve-2021-0326
Android Wi-Fi vulnerability research repository containing patched wpa_supplicant source for CVE-2021-0326, enabling analysis and testing of the…
 761669642/mahesh-970-cve-2023-21125_bluedriod_repo
Targeted reference for CVE-2023-21125, an Android BlueDroid Bluetooth vulnerability, with code and documentation focused on the affected component.