ChameleonUltra
The new generation chameleon based on NRF52840 makes the performance of card emulation more stable. And gave the chameleon the ability to read,…

The new generation chameleon based on NRF52840 makes the performance of card emulation more stable. And gave the chameleon the ability to read,…

Raspberry Pi Pico Arduino core, for all RP2040 and RP2350 boards

Python library and tools for exploring RFID/NFC tags and readers: read, write, clone, and analyze supported ACG serial hardware for research and…

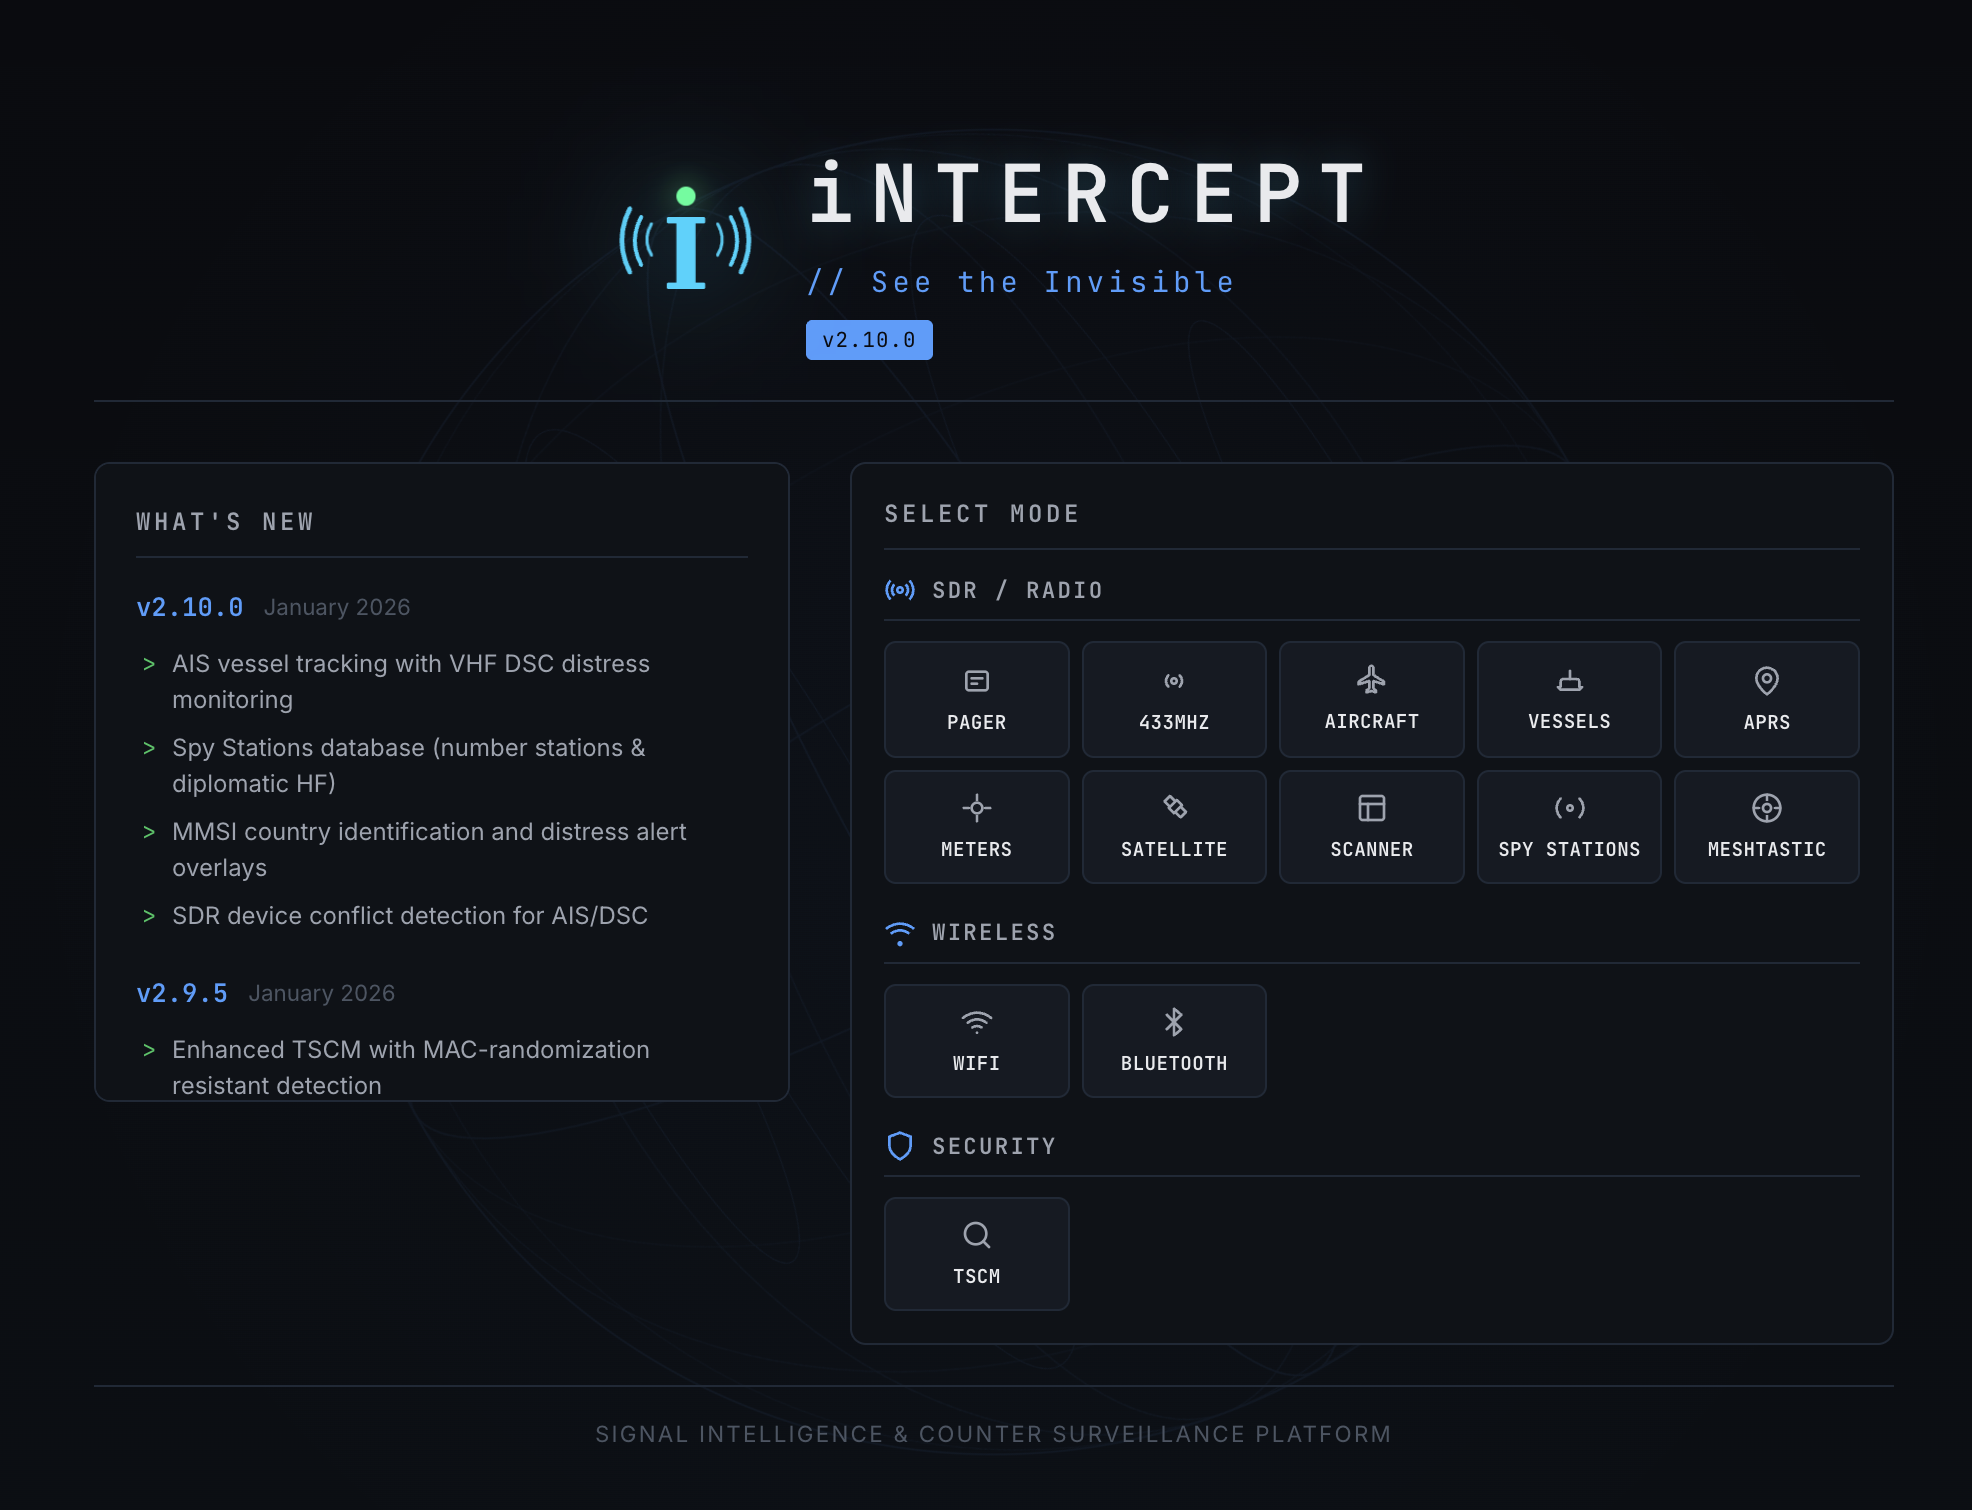
iNTERCEPT, a free and open-source platform that unites the best signal intelligence tools into a single, accessible interface.

Linux/Android kernel driver for RTL8812AU/21AU and RTL8814AU chipsets with monitor mode and frame injection support for wireless security testing.

PacketFence is a fully supported, trusted, Free and Open Source network access control (NAC) solution. Boasting an impressive feature set including a…

A cross-platform java application for decoding, monitoring, recording and streaming trunked mobile and related radio protocols using Software Defined…

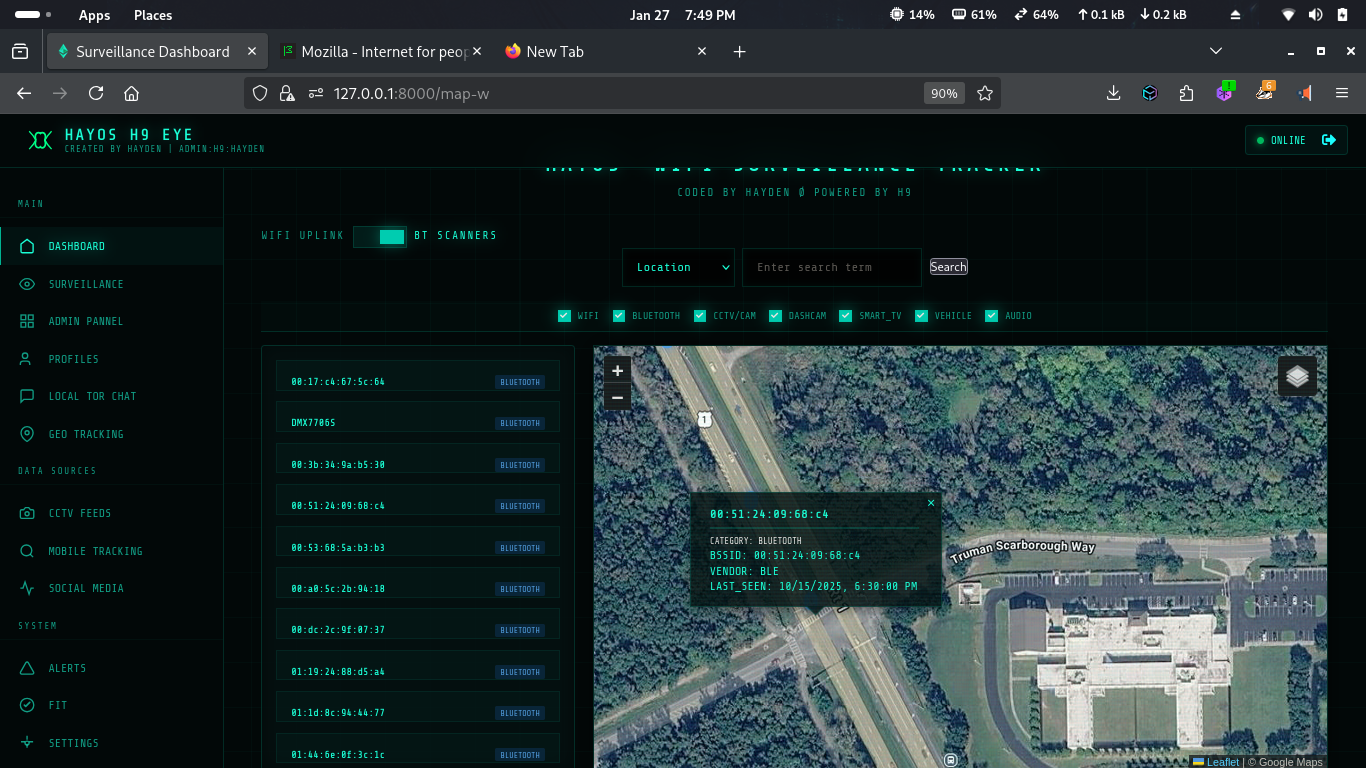
Passive wireless OSINT platform that detects and maps Wi-Fi, Bluetooth, CCTV, IoT devices, and cell towers using radio signal intelligence for…

Scripts to verify WPA2 clients and APs for KRACK key reinstallation vulnerabilities using modified hostapd and monitor-mode frame replay.

A drone engineered to autonomously seek out, hack, and wirelessly take full control over any other Parrot or 3DR drones within wireless or flying…

The RF and reverse engineering framework for everyone. Follow and ★ to show your support!

mac80211 driver for MediaTek MT76x0e, MT76x2e, MT7603, MT7615, MT7628 and MT7688

Flipper Zero app for infrared electronic shelf-label (ESL) protocol research, featuring custom image transmission, NFC tag scanning, and a web-based…

Linux Bluetooth protocol stack with daemons, command-line clients, HCI monitor, and support for BR/EDR, LE, Mesh, audio profiles, providing device…

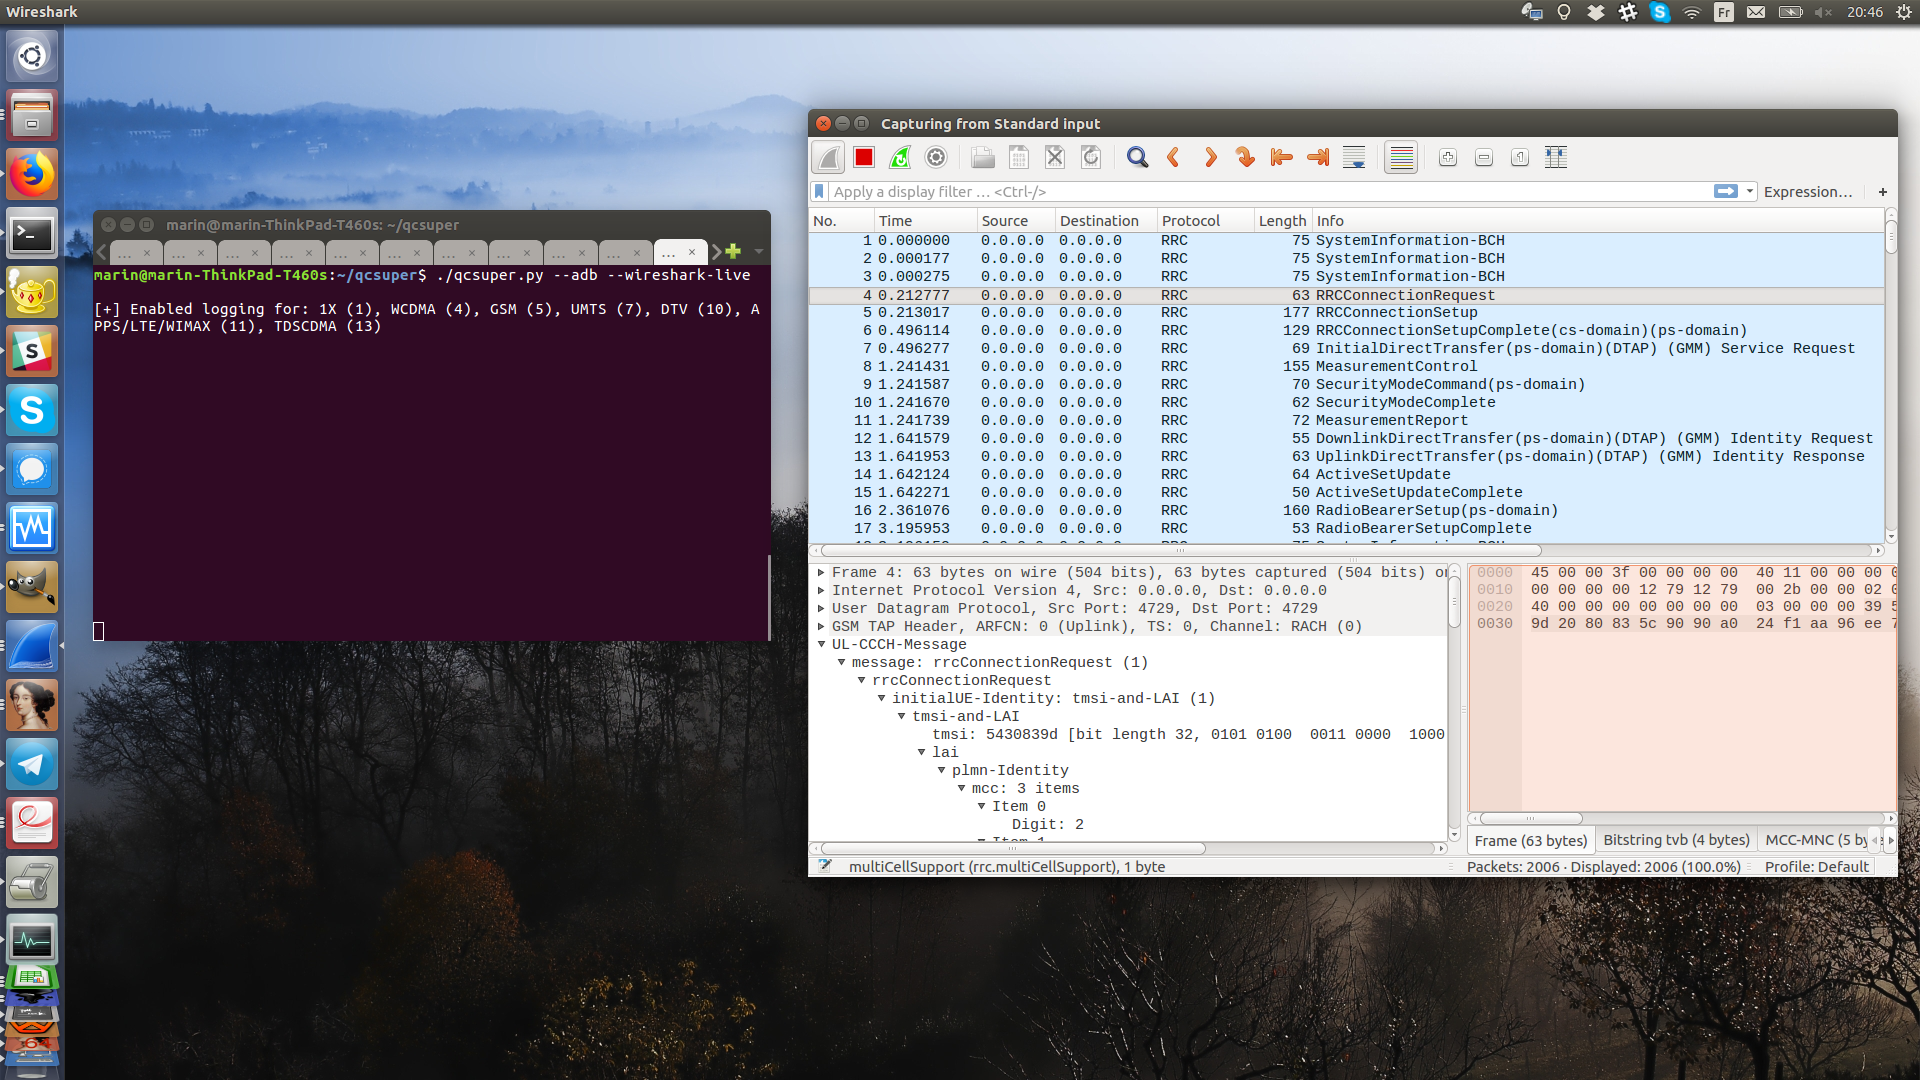
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.

Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…

Source code for the book "Violent Python" by TJ O'Connor. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…

BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.