

CVE-2025-32407
 diegovargasj/cve-2025-32407
Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…
dns-analysisexploitationmobile-security+6
diegovargasj/cve-2025-32407Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…
 yash-chandna/cve-2024-34463
Proof-of-concept exploit for CVE-2024-34463 targeting insufficient Bluetooth security in BPL Smart Weighing Scale PWS-01-BT. Includes BLE scanner and…
 d4rks1d33/c-poc-for-cve-2024-21306
Proof-of-concept exploit for CVE-2024-21306 targeting Bluetooth stacks. Demonstrates vulnerability exploitation via Bluetooth interface manipulation…
 amirasaiyad/ble-tpms
CVE-2024-39081. BLE TPMS data manipulation over bluetooth communication.
 lukejenkins/cve-2021-34767
Cisco IOS XE Software for Catalyst 9800 Series Wireless Controllers IPv6 Denial of Service Vulnerability
 uthrasri/frameworks_opt_net_wifi_cve-2021-0466
 dybrkr/wifi_leak
Proof-of-concept exploit for CVE-2018-4084, a WiFi credential leak vulnerability in macOS High Sierra, demonstrating interception of plaintext Wi-Fi…

 lixiang957/cve-2021-36630
Proof-of-concept exploit for CVE-2021-36630 targeting Ruckus SmartZone wireless controllers via UDP command injection on port 9001.
 alwentiu/cve-2020-14292
Details of CVE-2020-14292
 adminempire/meshdeck
MeshDeck port for Arch Linux ARM - Wilson
 yashodhanvivek/firebolt-wristphone-vulnerability
This repository is for Firebolt wristphone vulnerability for CVE ID CVE-2024-30656 suggested by MITRE. Mitre yet to confirm on ID
 ov3rwatch/detection-and-mitigation-for-cve-2022-1679
Shell script to detect and mitigate CVE-2022-1679, a use-after-free vulnerability in the Linux kernel's ath9k wireless driver that allows local…
 ekamsinghwalia/-detection-and-mitigation-for-cve-2022-1679
Shell script to detect and mitigate CVE-2022-1679, a use-after-free vulnerability in the Linux kernel's ath9k wireless driver that allows local…
 saruman9/ble_connect_rust
Norton Core Secure WiFi PoC (CVE-2018-5234) on Rust.
 osqzss/gps-sdr-sim
Software-Defined GPS Signal Simulator
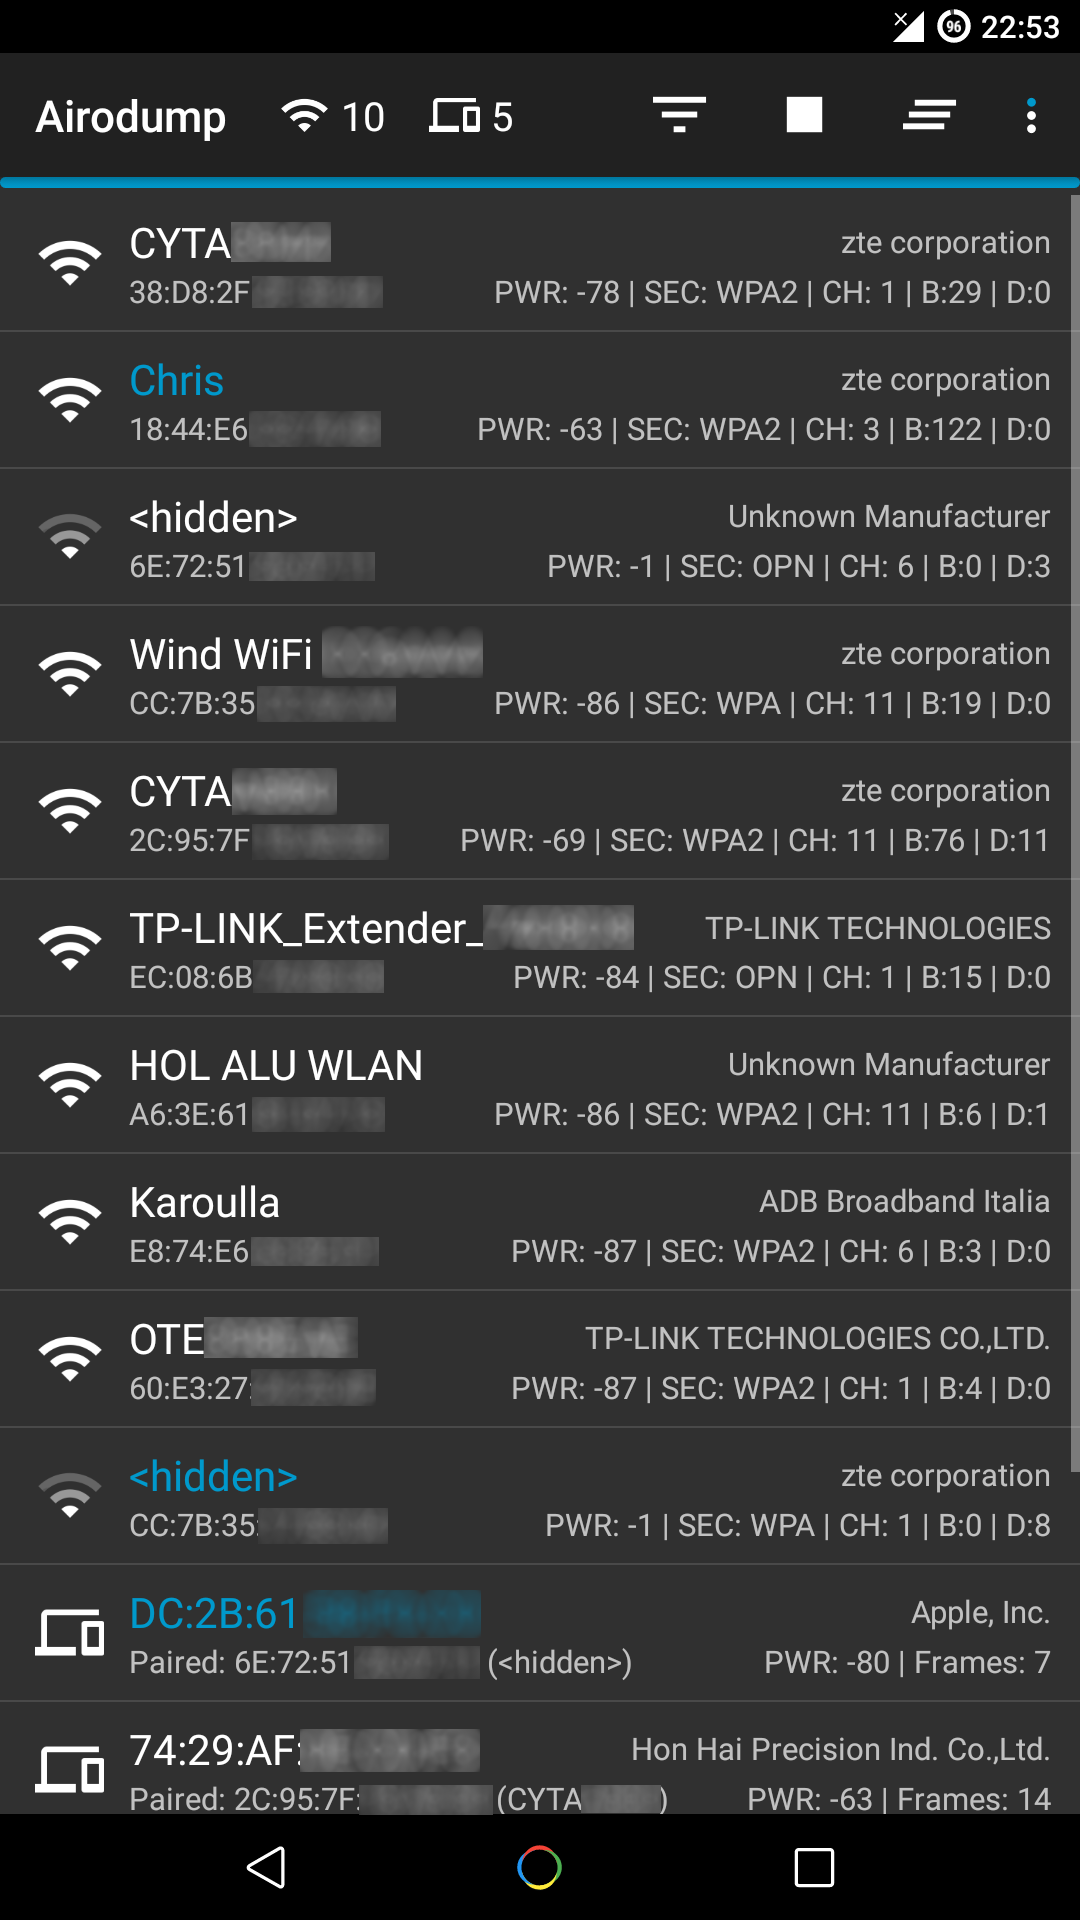 chrisk44/hijacker
Aircrack, Airodump, Aireplay, MDK3 and Reaver GUI Application for Android
 virtualabs/btlejuice
BLE Man-in-the-Middle framework that intercepts, replays, and modifies GATT traffic between Bluetooth Smart devices and mobile apps via a web-based…