

M5PORKCHOP
 0ct0sec/m5porkchop
ON NO! Someone put an RPG in a packet sniffer
bluetooth-securityeducationembedded-systems-security+6
0ct0sec/m5porkchopON NO! Someone put an RPG in a packet sniffer
 adamhrv/skylift
Wi-Fi Geolocation Spoofing with ESP8266 / ESP32
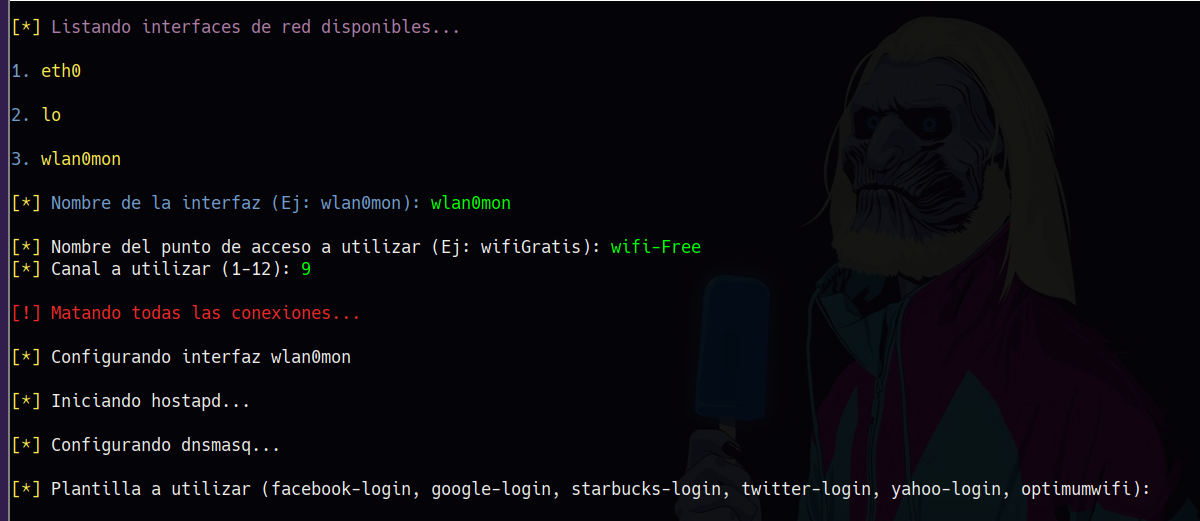 s4vitar/eviltrust
Herramienta ideal para el despliegue automatizado de un Rogue AP con capacidad de selección de plantilla + 2FA. No requiere de conexión cableada.
 wh00hw/pyflipper
Flipper Zero Python CLI Wrapper
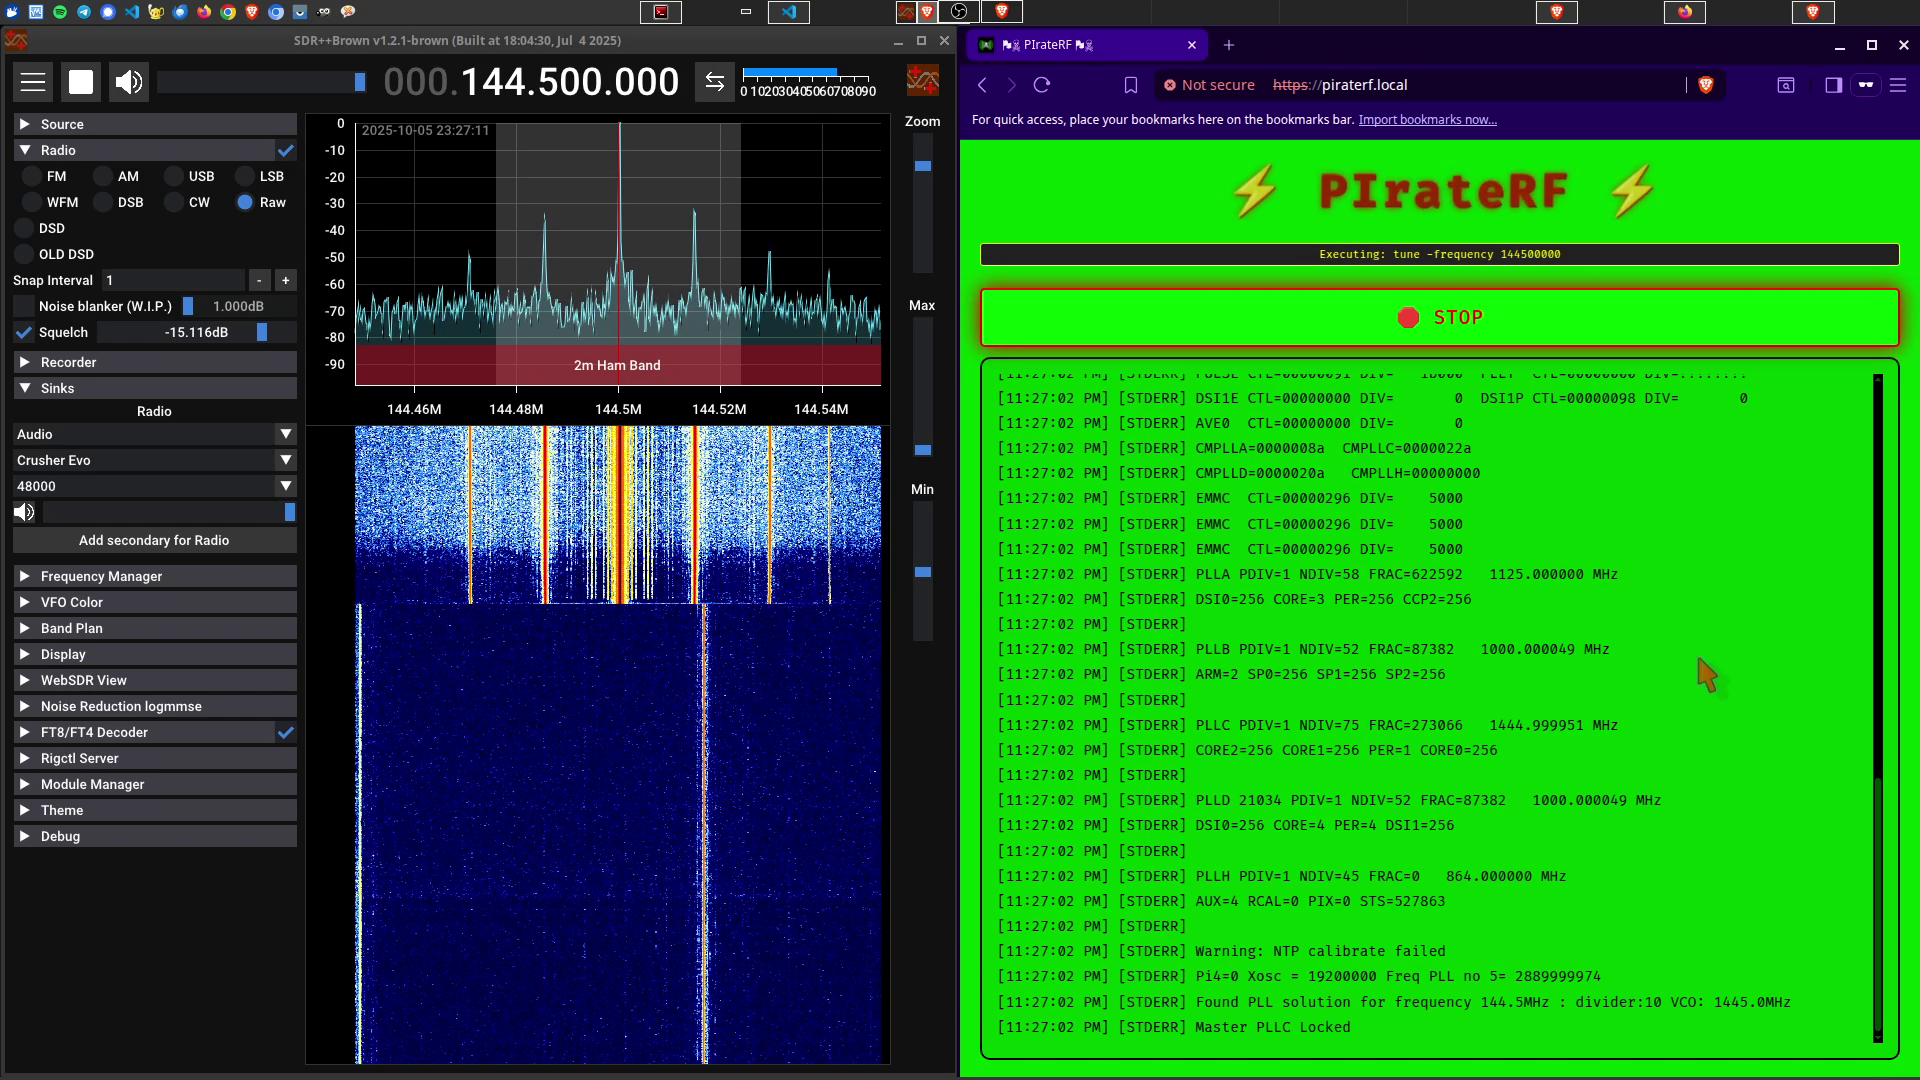 psyb0t/piraterf
PIrateRF transforms your Raspberry Pi Zero W into a portable RF signal generator that spawns its own WiFi hotspot. Control everything from FM…
 hackingdave/btrpa-scan
Bluetooth Low Energy (BLE) scanner with Resolvable Private Address (RPA) resolution using Identity Resolving Keys (IRKs)
 bishopfox/zigdiggity
A ZigBee hacking toolkit by Bishop Fox
 silverfoxx/pwnstar
PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!
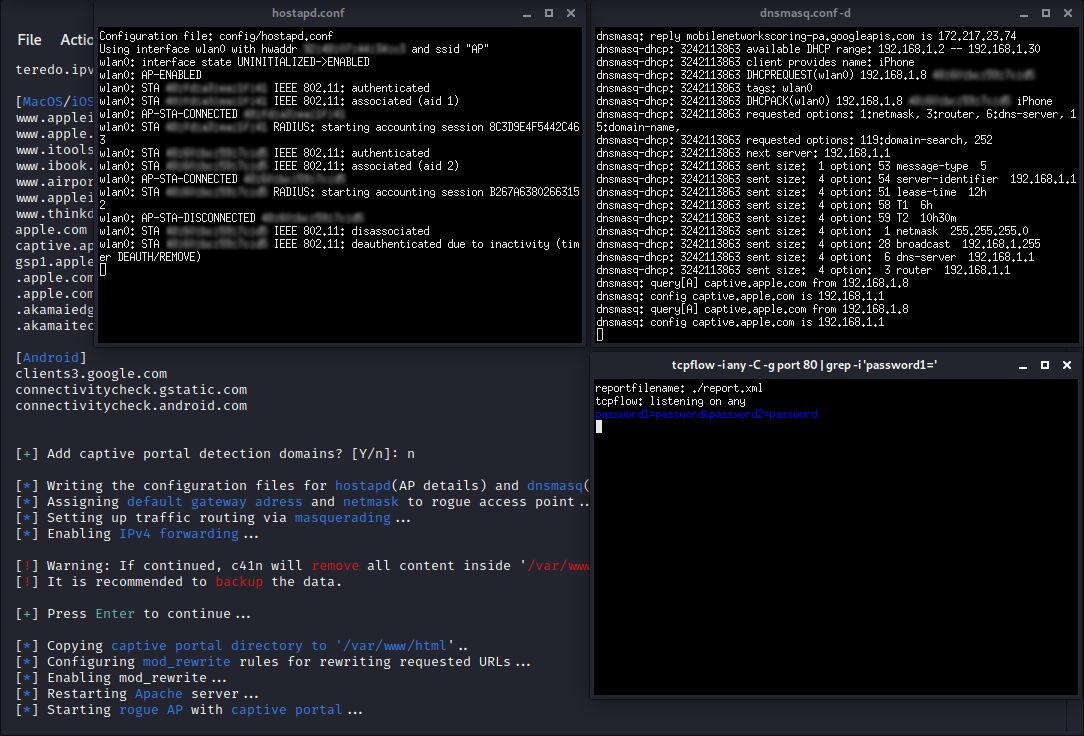 ms-web-bn/c41n
Automated rogue access point setup tool.
 insecurityofthings/uc_mousejack
Mousejack for ATmega32u4
 gdssecurity/wifitap
wifitap updated for BT5r3
 clu3bot/owt
Update Version 3.1 added free SMS messaging.

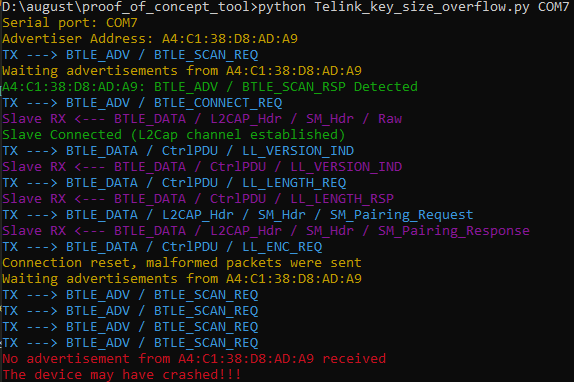 matheus-garbelini/sweyntooth_bluetooth_low_energy_attacks
Proof of Concept of Sweyntooth Bluetooth Low Energy (BLE) vulnerabilities.
 hexway/r00kie-kr00kie
PoC exploit for the CVE-2019-15126 kr00k vulnerability
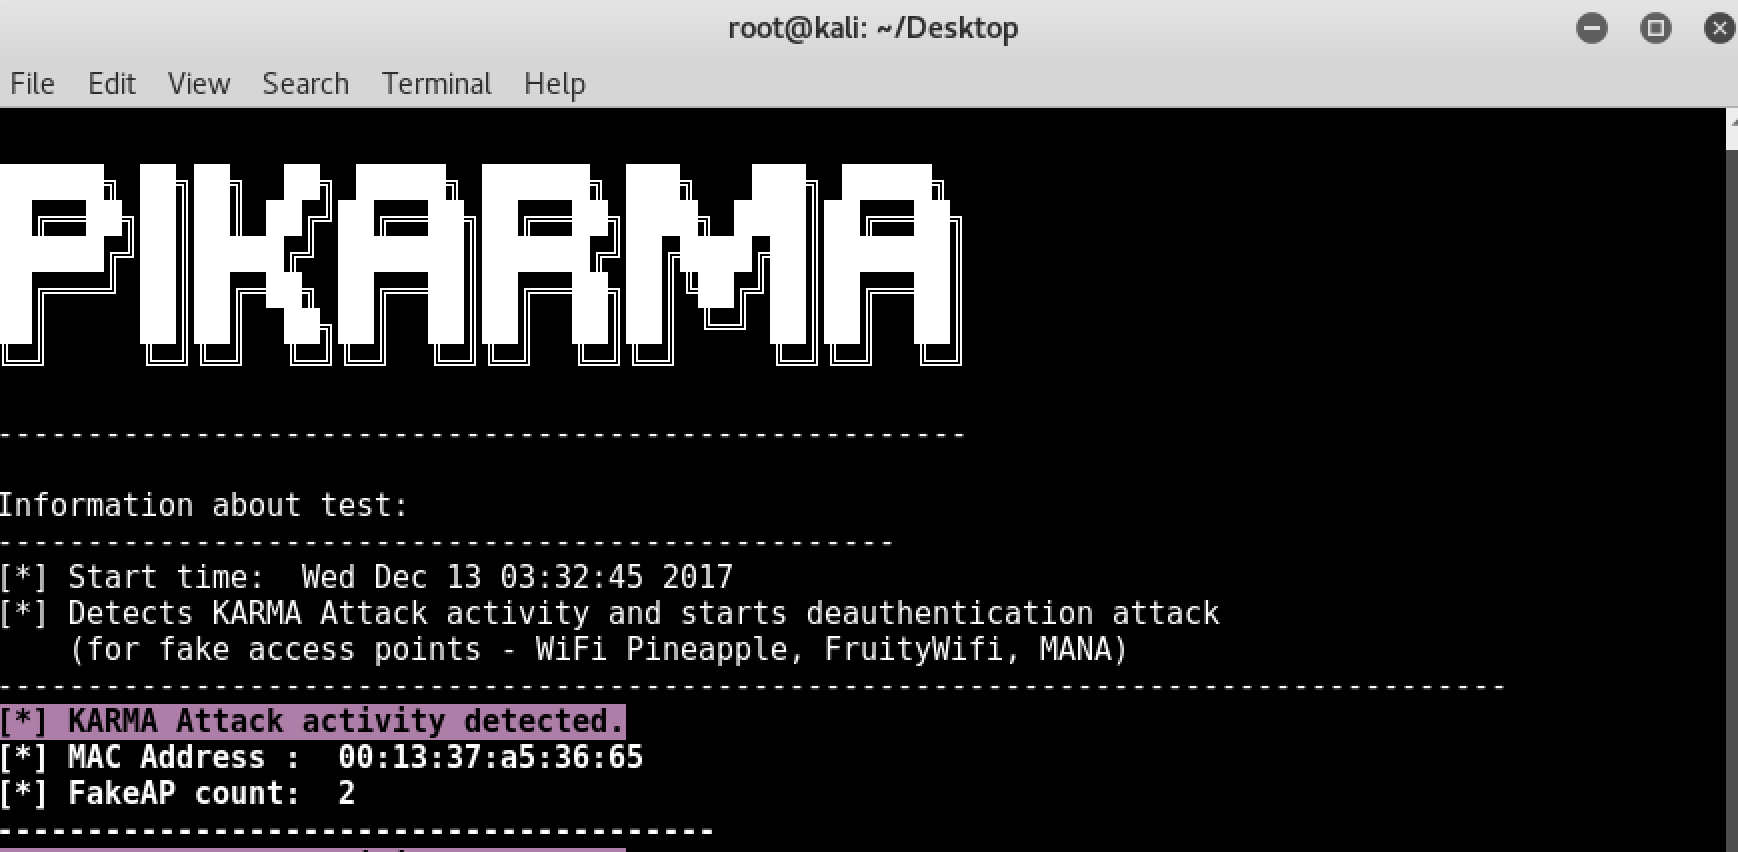 wipi-hunter/pikarma
📡🍓🍍 Detects wireless network attacks performed by KARMA module (fake AP). Starts deauthentication attack (for fake access points)
 generaldussduss/poseidon
80+ feature pentesting firmware for M5Stack Cardputer-Adv. WiFi, BLE, sub-GHz (CC1101), 2.4GHz (nRF24), LoRa (SX1262), IR, BadUSB, DHCP attacks,…
 1n3/prism-ap
An automated Wireless RogueAP MITM attack framework.