
Awesome-Cellular-Hacking
 w00t3k/awesome-cellular-hacking
Awesome-Cellular-Hacking
curated-resourceseducationexploitation+6
4.0k
w00t3k/awesome-cellular-hackingAwesome-Cellular-Hacking
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 vanhoefm/krackattacks-scripts
Scripts to verify WPA2 clients and APs for KRACK key reinstallation vulnerabilities using modified hostapd and monitor-mode frame replay.
 greatscottgadgets/ubertooth
BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.
 insecurityofthings/uc_mousejack
Mousejack for ATmega32u4
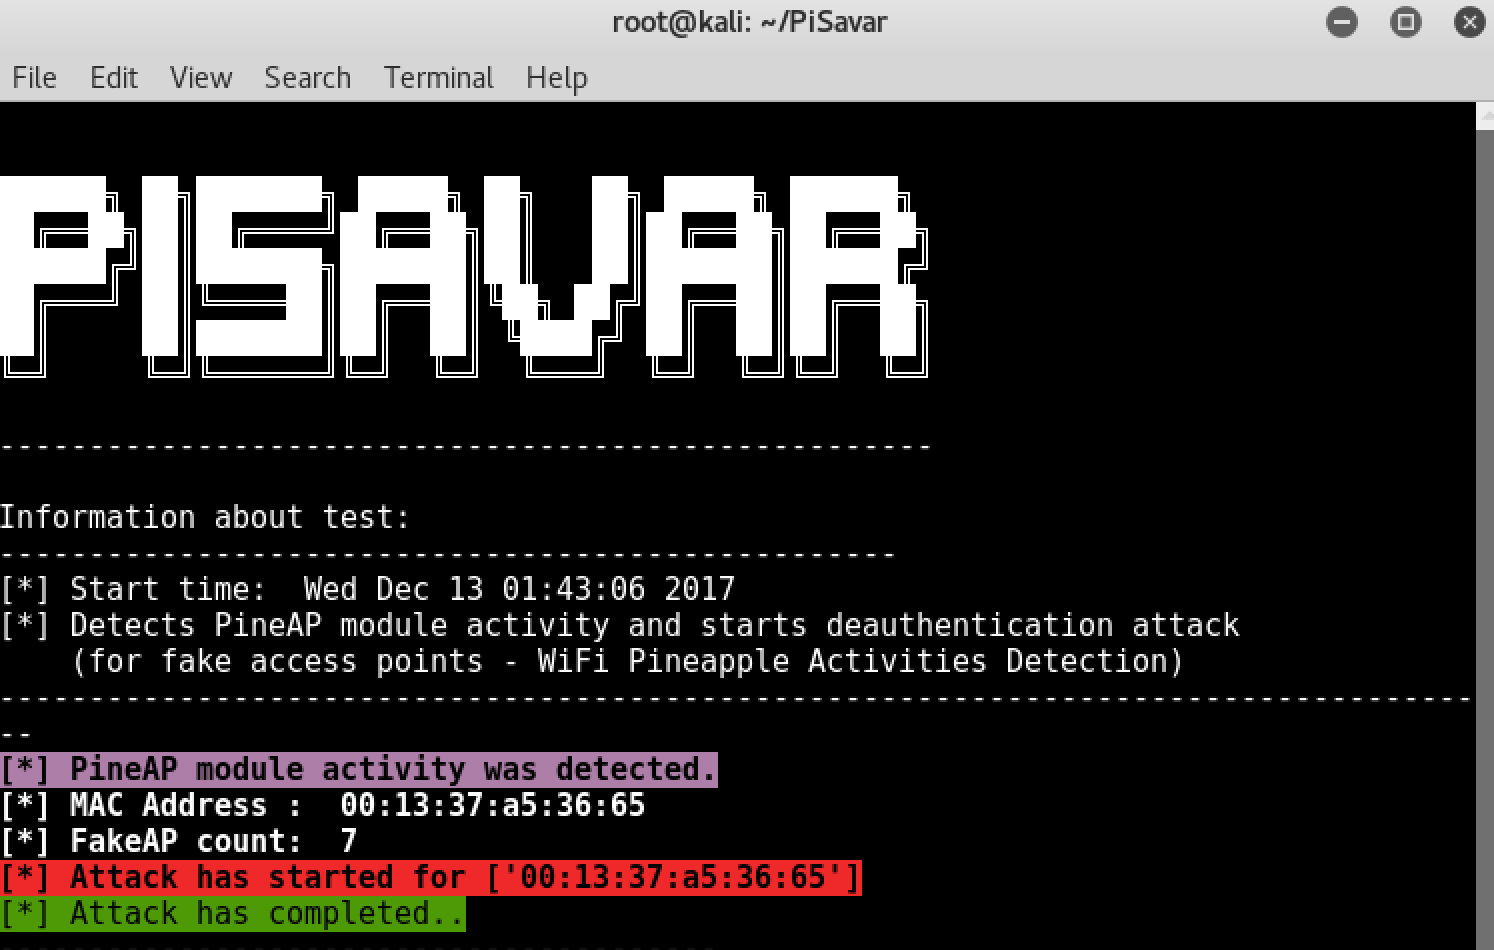 wipi-hunter/pisavar
📡 🍍Detects activities of PineAP module and starts deauthentication attack (for fake access points - WiFi Pineapple Activities Detection)
 greatscottgadgets/libbtbb
C library for decoding Bluetooth baseband packets and extracting piconet information from Ubertooth and USRP hardware for wireless analysis.
 efchatz/wpaxfuzz
A full-featured open-source Wi-Fi fuzzer
 wipi-hunter/pifinger
📡🔍Searches for wifi-pineapple traces and calculate wireless network security score 🍍
 luispl77/433screen-signalhacker
Full duplex 433 MHz Signal jammer, recorder, decoder and hacking multitool device based on ESP32 microcontroller and RFM69HW radios. This version of…
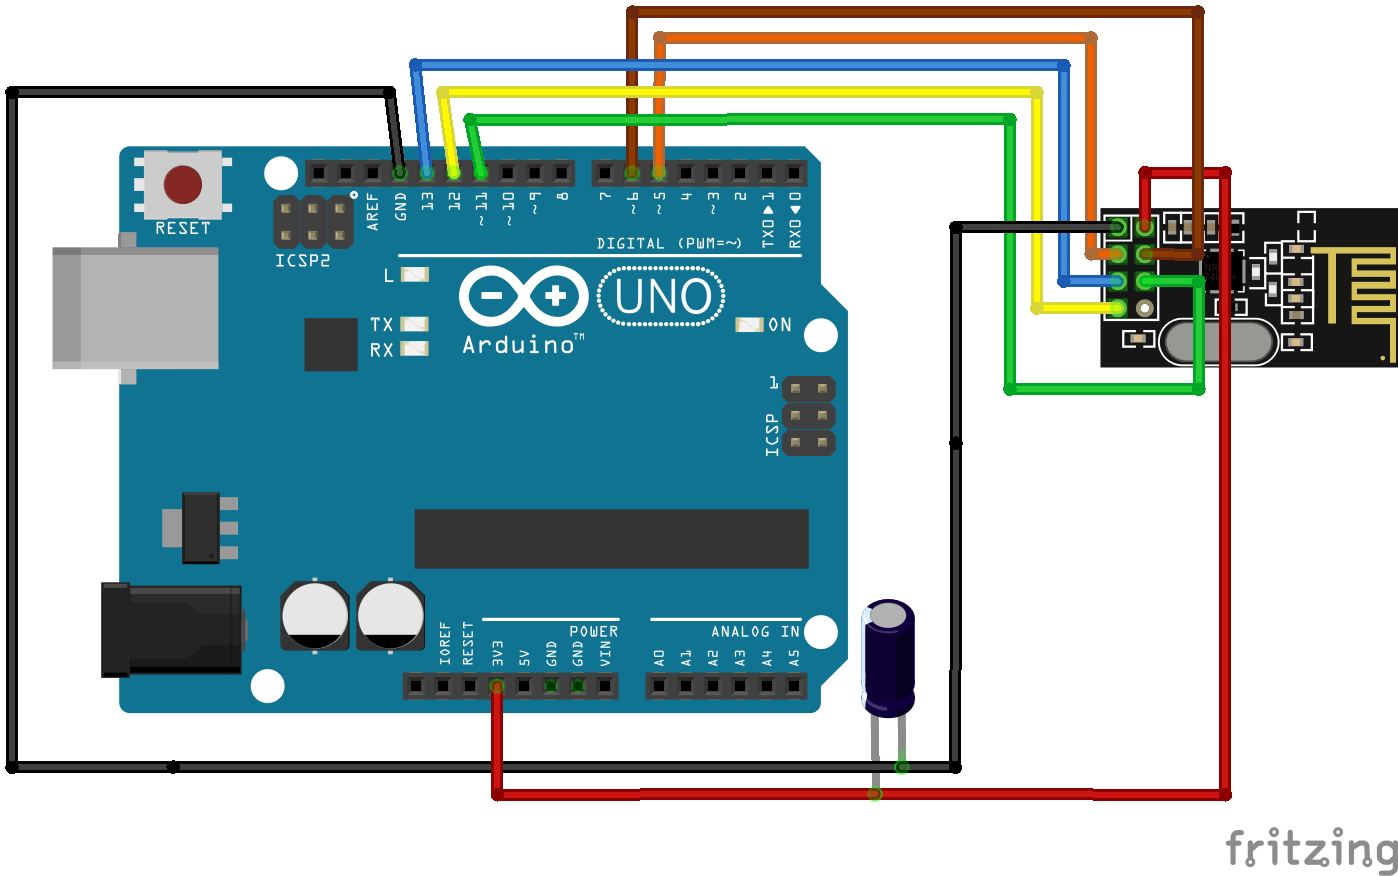 dnatividade/arduino_mousejack
Mousejack for Arduino UNO
 gentilkiwi/st25tb_kiemul
ST25TB / SRx NFC Emulator / Initiator based on TI TRF7970A with MSP430
 pieterbork/blueborne
Scan/Exploit Blueborne CVE-2017-0785
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
 rianhanft/marauderbox
A fork of the marauder firmware with Nyan box capabilities
 msdmehdipour/meshtastic-cve-2025-52464-poc
Software-only proof of concept for CVE-2025-52464 in Meshtastic Direct Messages
 xg3nesis/rustyinjector
Rust implementation of Marc Newlin's keystroke injection proof of concept (CVE-2023-45866).
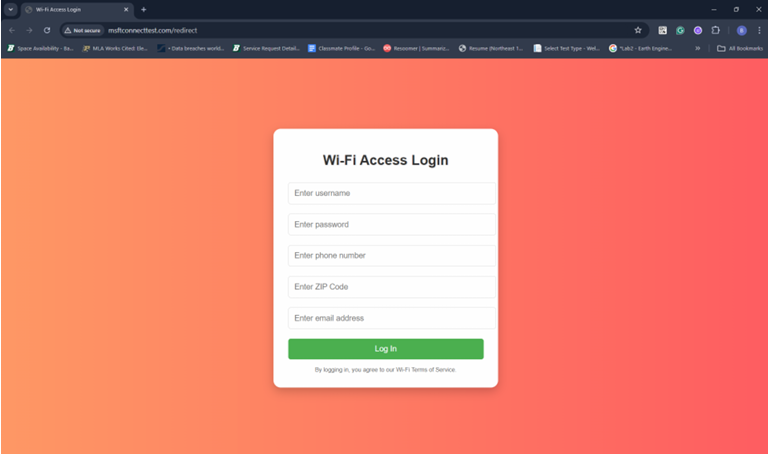
 yashubitra/evil_twin_attack
Rogue access point attack and defense on Kali Linux: deauth with aireplay-ng, an airbase-ng evil twin with a captive portal, plus real-time…