
-CVE-2017-0785-BlueBorne-PoC
 alfa100001/-cve-2017-0785-blueborne-poc
CVE-2017-0785 BlueBorne PoC
bluetooth-securityexploitationinformation-gathering+4
40
alfa100001/-cve-2017-0785-blueborne-pocCVE-2017-0785 BlueBorne PoC
 francozappa/blur
BLURtooth: Exploiting Cross-Transport Key Derivation in Bluetooth Classic and Bluetooth Low Energy [CVE-2020-15802] [CVE-2022-20361]
 unsignedchad/bcm4360-wpa3
wpa3 functionality for the wifi chip in a 2014 macbook pro
 naren-jayram/linux-heap-based-type-confusion-in-l2cap
CVE-2020-12351
 hexway/r00kie-kr00kie
PoC exploit for the CVE-2019-15126 kr00k vulnerability
 embedi/ble_norton_core
Proof-of-concept exploit demonstrating command injection via BLE service in Norton Core Secure WiFi Router (CVE-2018-5234). Includes SSH access setup…
 hunt-benito/mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce
Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…
 sastraadiwiguna-purpleeliteteaming/cve-2025-13834-a-bluetooth-rfcomm-out-of-bounds-read-vulnerability-in-modern-wireless-devices
CVE-2025-13834 Technical Summary Vulnerability Type: Memory Disclosure / Out-of-Bounds (OOB) Read (CWE-125). CVSS Score: 7.5–8.1 (High/Critical). …
 h4ckusaur/cve-2024-57366
Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…
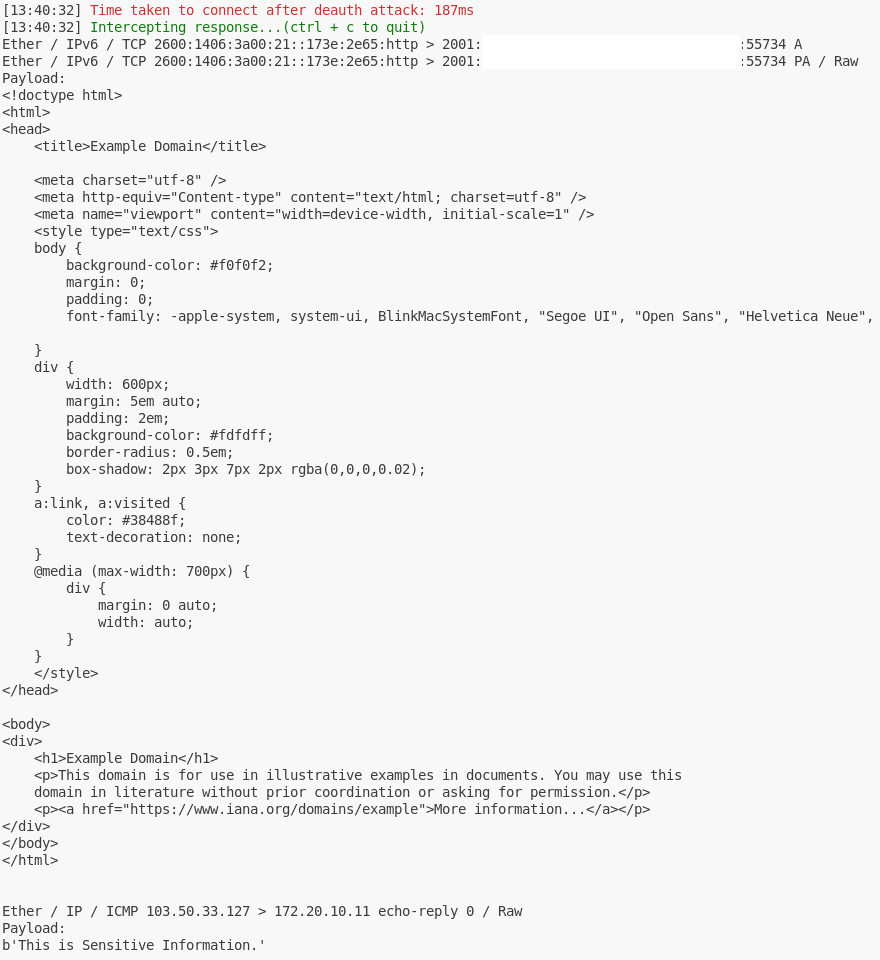 toffeenutt/cve-2022-47522-poc
Proof-of-concept exploit for CVE-2022-47522 demonstrating Wi-Fi frame interception via deauthentication attack and MAC address spoofing to capture…
 librepods-org/librepods
AirPods liberated from Apple's ecosystem.
 thehackingsage/hacktronian
Tools for Pentesting
 seemoo-lab/internalblue
Bluetooth experimentation framework for Broadcom and Cypress chips.
 cosmic-zip/witchcraft
WITCHCRAFT is a cyberdeck toolkit built for runners who dive deep into the mesh. It’s your all-in-one rig for data-ghosting, ICE-breaking, and…
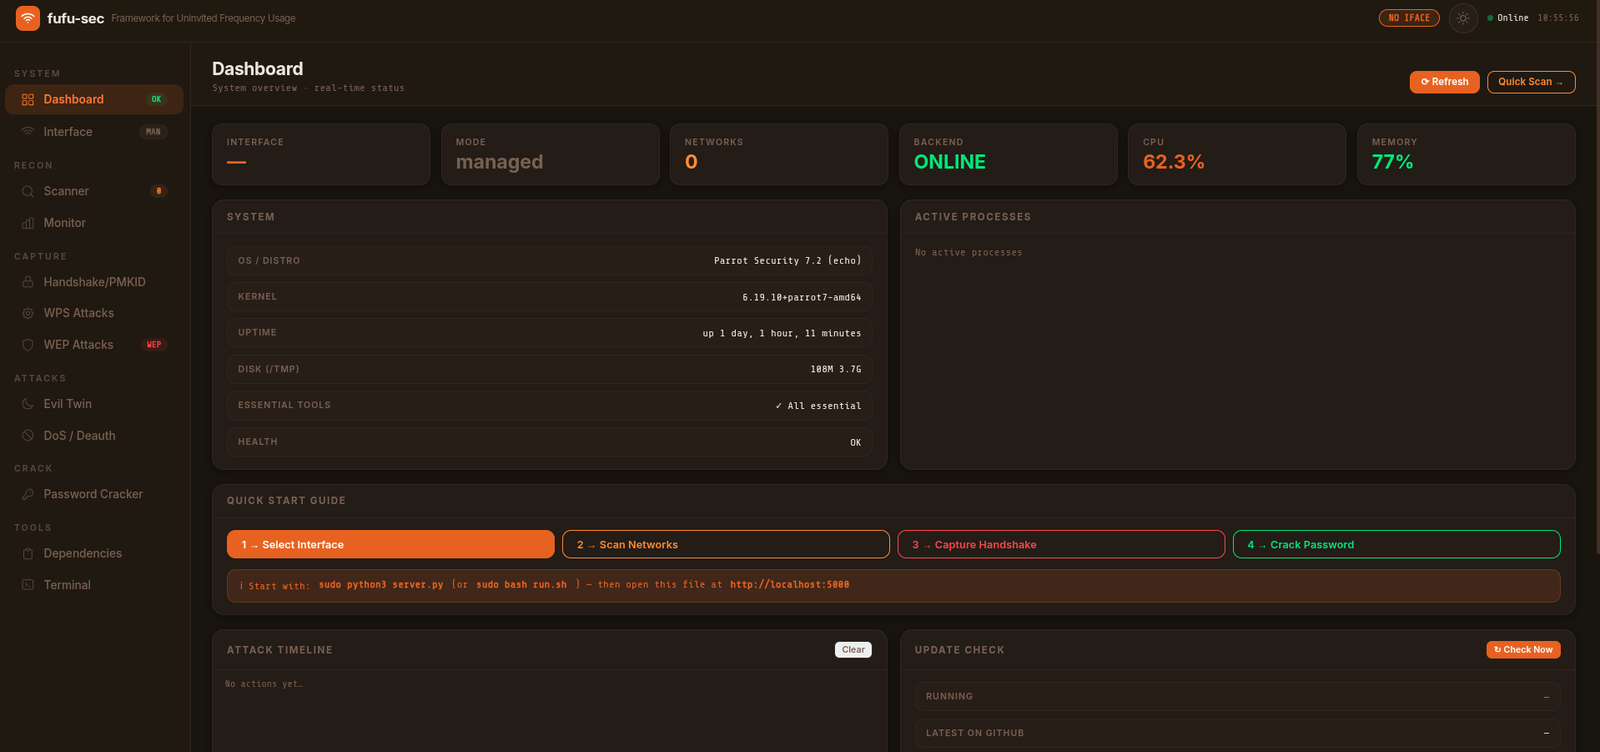 kyllr-qwen/fufu-sec
Framework for Uninvited Frequency Usage
 esperto-input/esperto-wiimote
Advanced Wiimote remapping software
 qkaiser/broadcom-wps
Tools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…