
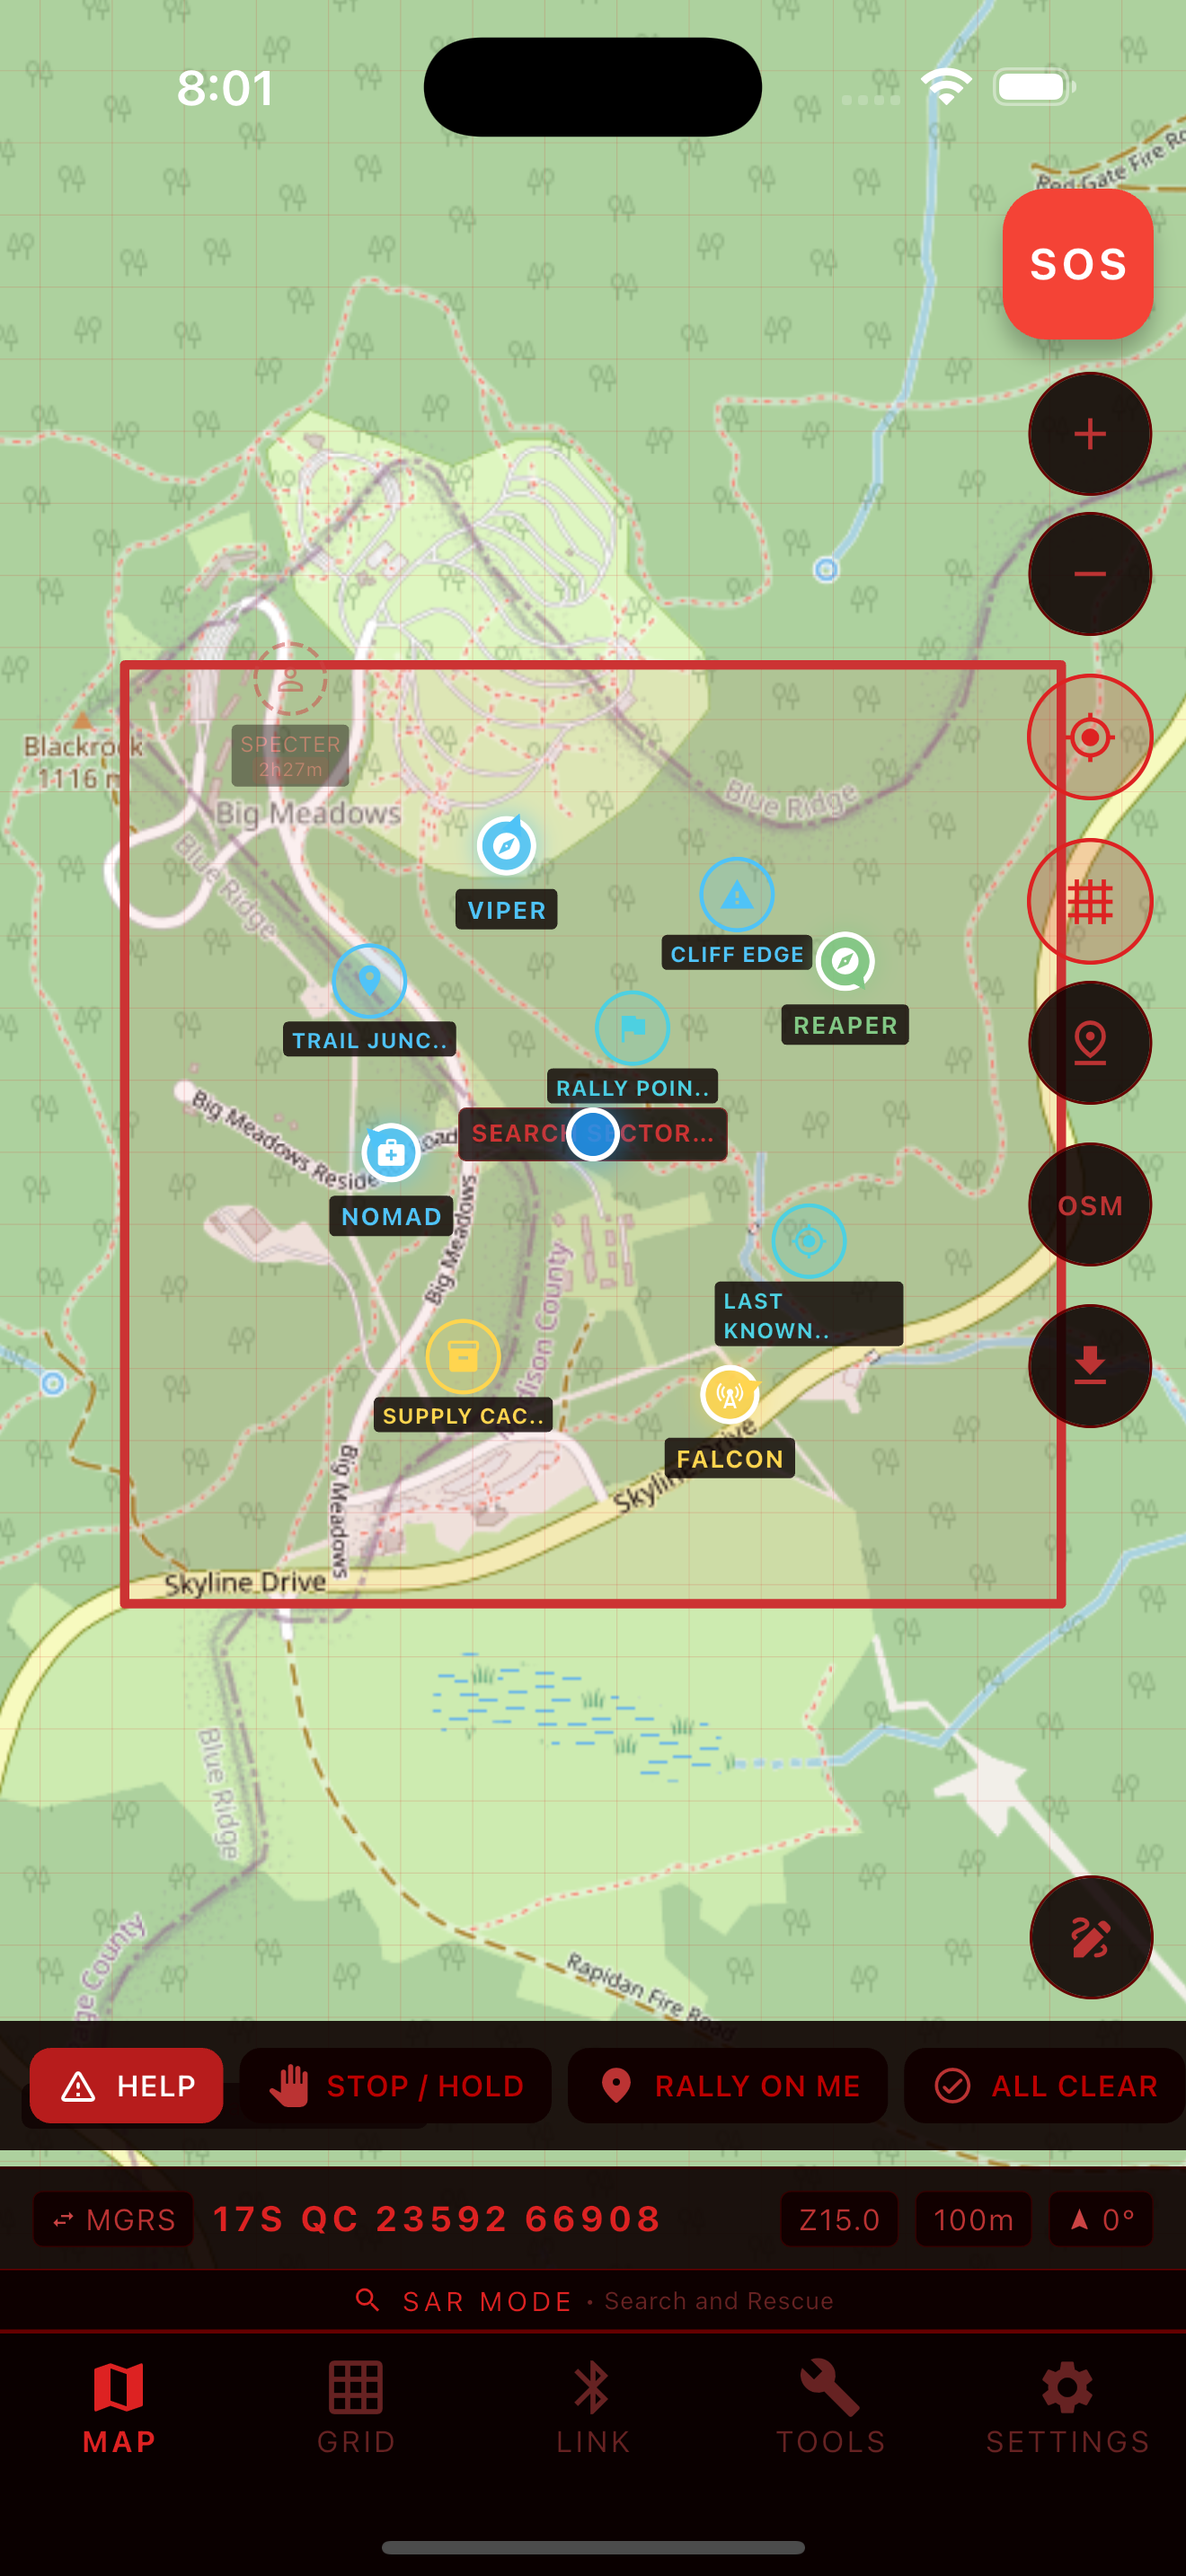
RedGridLink
 redgridtactical/redgridlink
Retired September 27, 2026. Final v1.7.0 source retained for reference; no new store downloads or purchases. Development continues in Red Grid MGRS,…
bluetooth-securityctfeducation+6
96
redgridtactical/redgridlinkRetired September 27, 2026. Final v1.7.0 source retained for reference; no new store downloads or purchases. Development continues in Red Grid MGRS,…
 mailinneberg/broadpwn
Broadpwn bug (CVE-2017-9417)
 atao/raspberrypi-setup
Ansible playbook for rapid Raspberry Pi setup with modular roles for wireless security testing, RFID/NFC tools, SDR, Docker, Tor proxy, and standard…
 thehappydinoa/tp-link-defaults
Python script for trying default passwords for some TP-Link Hotspots
 mretallack/androidauto
Open-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…
 irsl/lgosp-poc
LG On Screen Phone authentication bypass PoC (CVE-2014-8757)
 bttea/cve-2018-14714-rce-exploit
ASUS wifi router RCE vulnerability
 raddad87/rayhunter-web-flasher
Interactive wizard to flash EFF's Rayhunter on Orbic RC400L — auto-detects OS
 inartin/365cam-stream
Local streaming tool for cheap WiFi cameras that bypasses cloud services and phone apps. Discovers cameras on your network, authenticates via PPPP…
 jean-nestor/evil-twin-ap
Automated evil twin access point toolkit with traffic capture and real-time monitoring for wireless penetration testing and security research.
 pushkarreddyy/radioguard
Zero-Trust Cellular Defense Sub-Service for Android (IMSI-Catcher, 2G SMS Blaster, and 4G aLTEr Detection & Safe Routing)
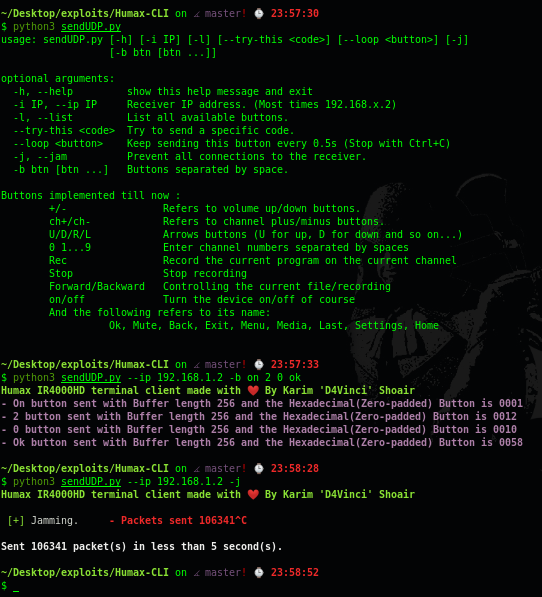 d4vinci/humax-cli
An unofficial Humax IR4000HD terminal client with enhanced features.
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025
 geniuszly/genwififaker
is a tool for creating fake WiFi access points
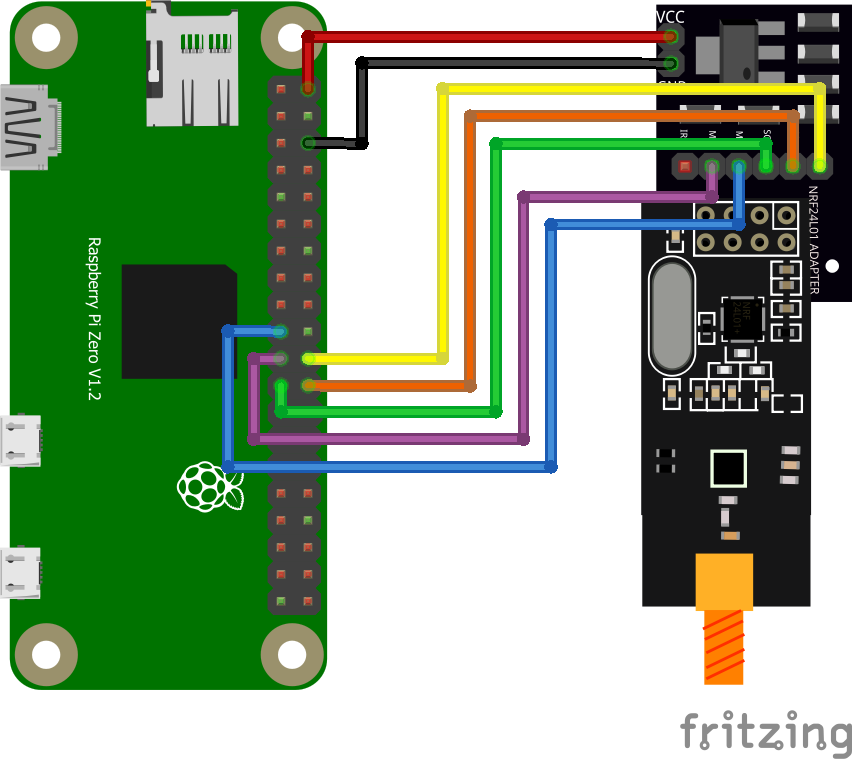 b1narygl1tch/zerojack
A tool for performing MouseJack keystrokes injection attack.

 bloodcode-spasov/ble-cve2025-attack-new-version
# android-ble-cve-2025-4866 🔐 **PoC za CVE-2025-4866 — Android BLE ranjivost (javna verzija)** 📡 Iskorišćavanje slabosti u BLE autorizaciji na…
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…