BLEBoy
 nccgroup/bleboy
BLEBoy is a training tool to teach users about BLE security by providing a single BLE peripheral that can be used to experiment with each BLE pairing…
bluetooth-securityeducationembedded-systems-security+3
49
nccgroup/bleboyBLEBoy is a training tool to teach users about BLE security by providing a single BLE peripheral that can be used to experiment with each BLE pairing…
 0xsamy/sweet-pineapple-builder
Build your own custom WiFi Pineapple Tetra firmware tailored to any based MIPS 24Kc architecture router. (WiFi Pineapple Tetra DIY)
 pieterbork/blueborne
Scan/Exploit Blueborne CVE-2017-0785
 saimanish1/logitech-ipc-protocol
Reverse-engineered Logi Options+ agent IPC protocol. Switch Logitech multi-host devices programmatically via Unix socket (macOS) or named pipe…
 zhuowei/blueshrimp
Proof-of-concept for CVE-2025-48593
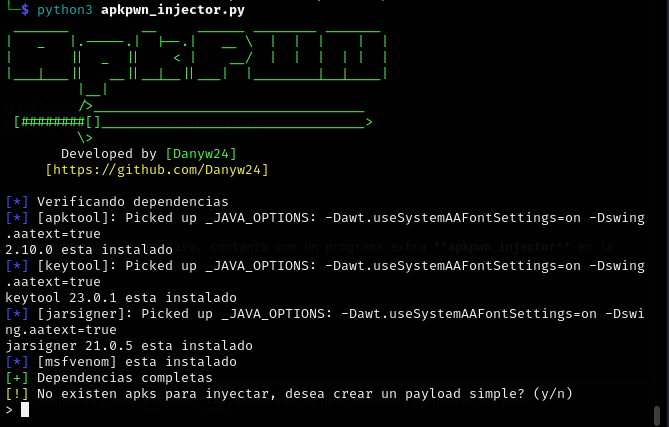 danyw24/bluexploit
Exploit basado en vulnerabilidades criticas Bluetooth (CVE-2023-45866, CVE-2024-21306)
 alkersan/om-research
Documenting Osmo Mobile BLE protocol
 phuchaudeveloper/badblue
CVE-2024-21306 BadBlue implementation (Using DuckyScript)
 sqrtrev/cve-2021-1965
Proof-of-concept exploit for CVE-2021-1965, a WiFi zero-click RCE in Android's MBSSID parsing, causing buffer overflow and device reboot.
 joshuapassos/cmf-watch-pro-2-ble-protocol
Reverse-engineered BLE protocol for the CMF Watch Pro 2, documenting GATT layout, AES-128-CBC encrypted command frames, authentication handshake, and…
 alainx277/cve-2025-24797
Meshtastic buffer overflow vulnerability - CVE-2025-24797
 xqi1337/poc-cve-2026-0073
CVE-2026-0073 - ADB Wireless Mutual Authentication Bypass PoC
 barghest-ngo/cve-2026-51376
Proof-of-concept exploit for BLE cache poisoning in Bitchat 1.15.0, demonstrating a man-in-the-middle attack that poisons the Bluetooth Low Energy…
 aprkr/cve-2023-48034
Weak encryption in Acer Wireless Keyboard SK-9662 allows attacker in physical proximity to both decrypt wireless keystrokes and inject wireless…

 diegovargasj/cve-2025-32407
Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…
 lixiang957/cve-2021-36630
Proof-of-concept exploit for CVE-2021-36630 targeting Ruckus SmartZone wireless controllers via UDP command injection on port 9001.