
unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.

Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.

High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…

RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…

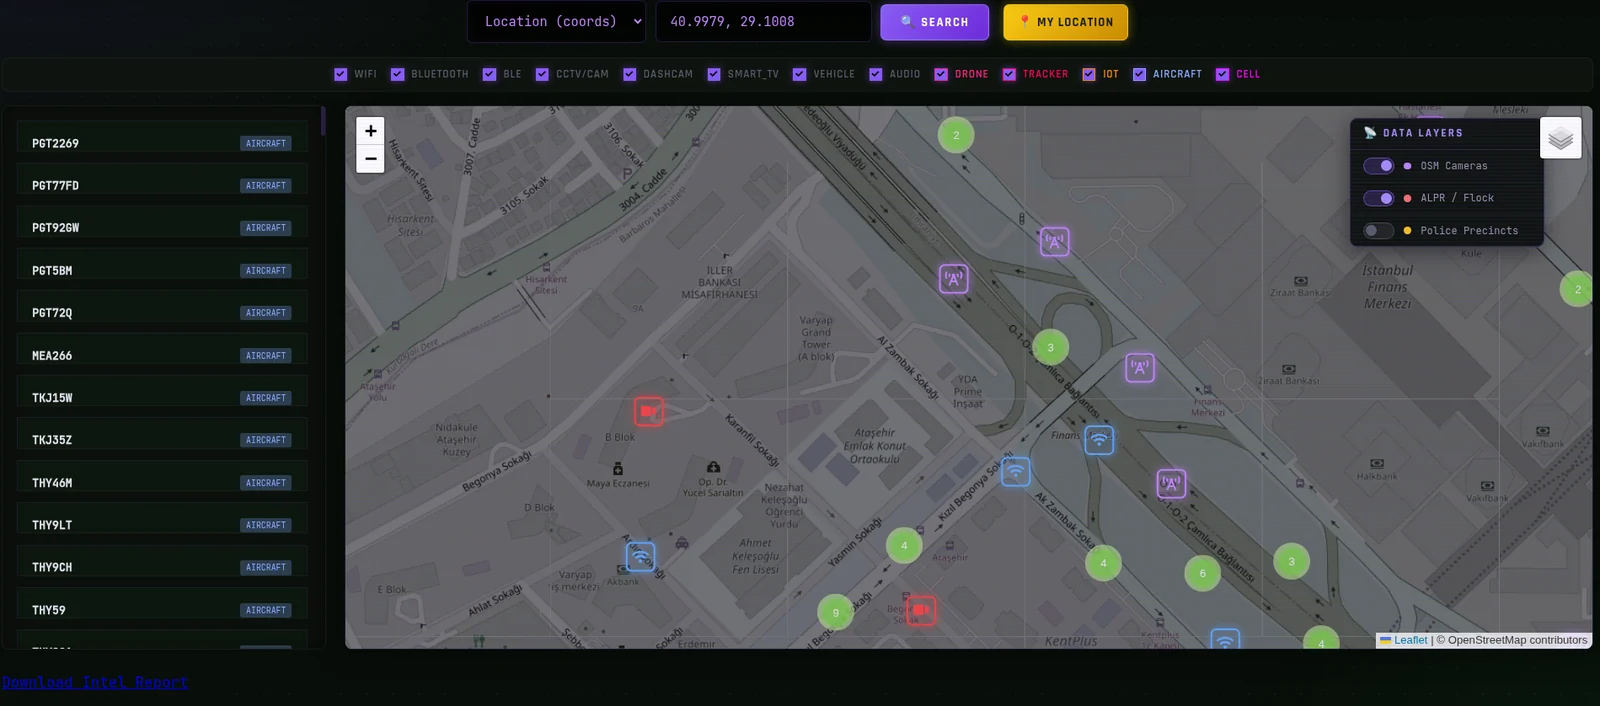
All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…

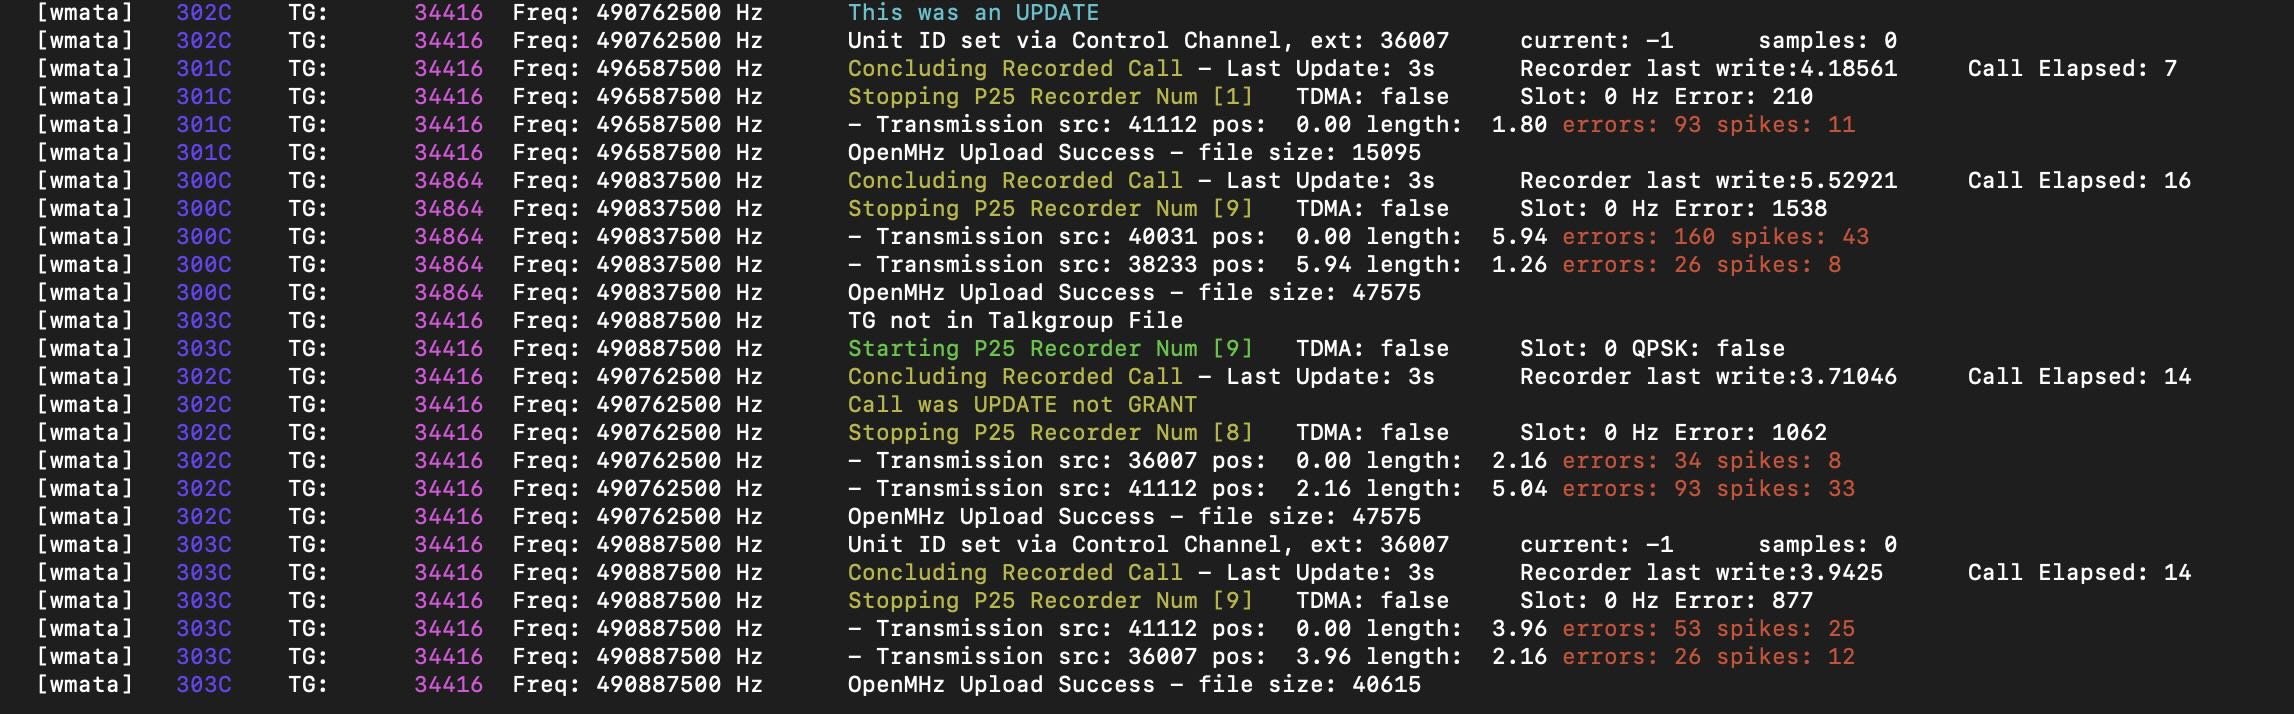
Records calls from a Trunked Radio System (P25 & SmartNet)

All-in-One Hacking Tools For Hackers! And more hacking tools! For termux.

A comprehensive collection of penetration testing cheatsheets, guides, and tools.

Ansible playbook for rapid Raspberry Pi setup with modular roles for wireless security testing, RFID/NFC tools, SDR, Docker, Tor proxy, and standard…

Proof of Concept for the CVE-2026-22226

An NFC research toolkit application for Android

0-Click RCE Android Adb TLS Wireless Debugging

Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…

PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…

A comprehensive security toolkit with 1000+ penetration testing and security assessment tools.

Practical labs, notes, and reports for CEH v13 modules — covering web hacking, network pentesting, malware analysis, social engineering, and security…

Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…

Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability

Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…