
hostapd-mana
 sensepost/hostapd-mana
SensePost's modified hostapd for wifi attacks.
penetration-testingred-teamingwi-fi-auditing+1
sensepost/hostapd-manaSensePost's modified hostapd for wifi attacks.
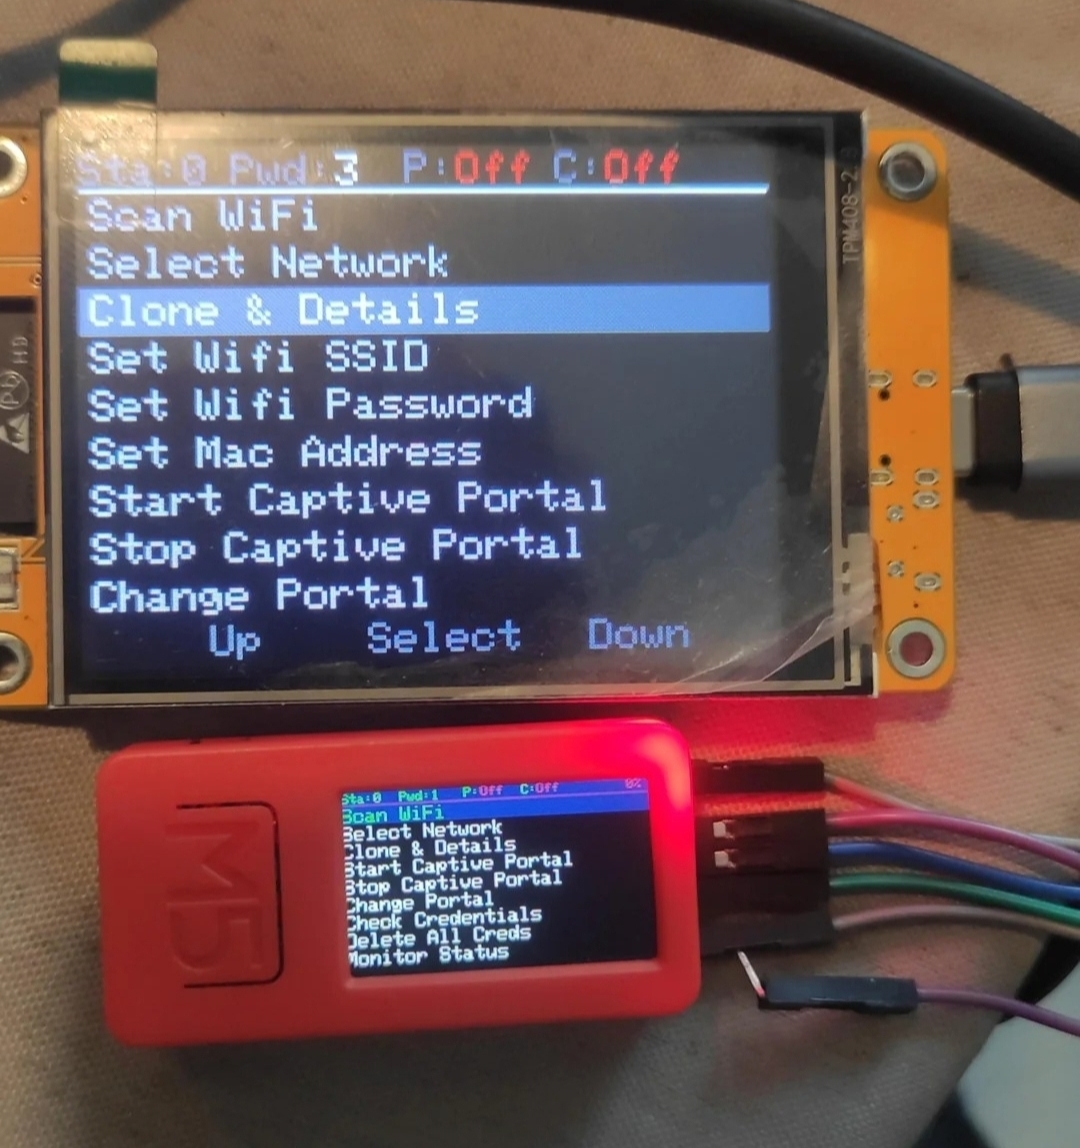 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
 meshcore-dev/meshcore
A new lightweight, hybrid routing mesh protocol for packet radios
 feedbeef/dji_ble_vuln
DJI Drone DUML Command Injection over Bluetooth — Proof of Concept for CVE-2026-78306
 fluxionnetwork/fluxion
Automated WPA/WPA2 phishing tool that captures handshakes, spawns a rogue access point, and lures users to a captive portal to harvest credentials…
 mahmoud-sadder/airstrike
AirStrike is an advanced wireless security assessment framework designed to simplify and enhance Wi-Fi penetration testing through an integrated,…
 lucasvanhaaren/cve-2026-22226
Proof of Concept for the CVE-2026-22226
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
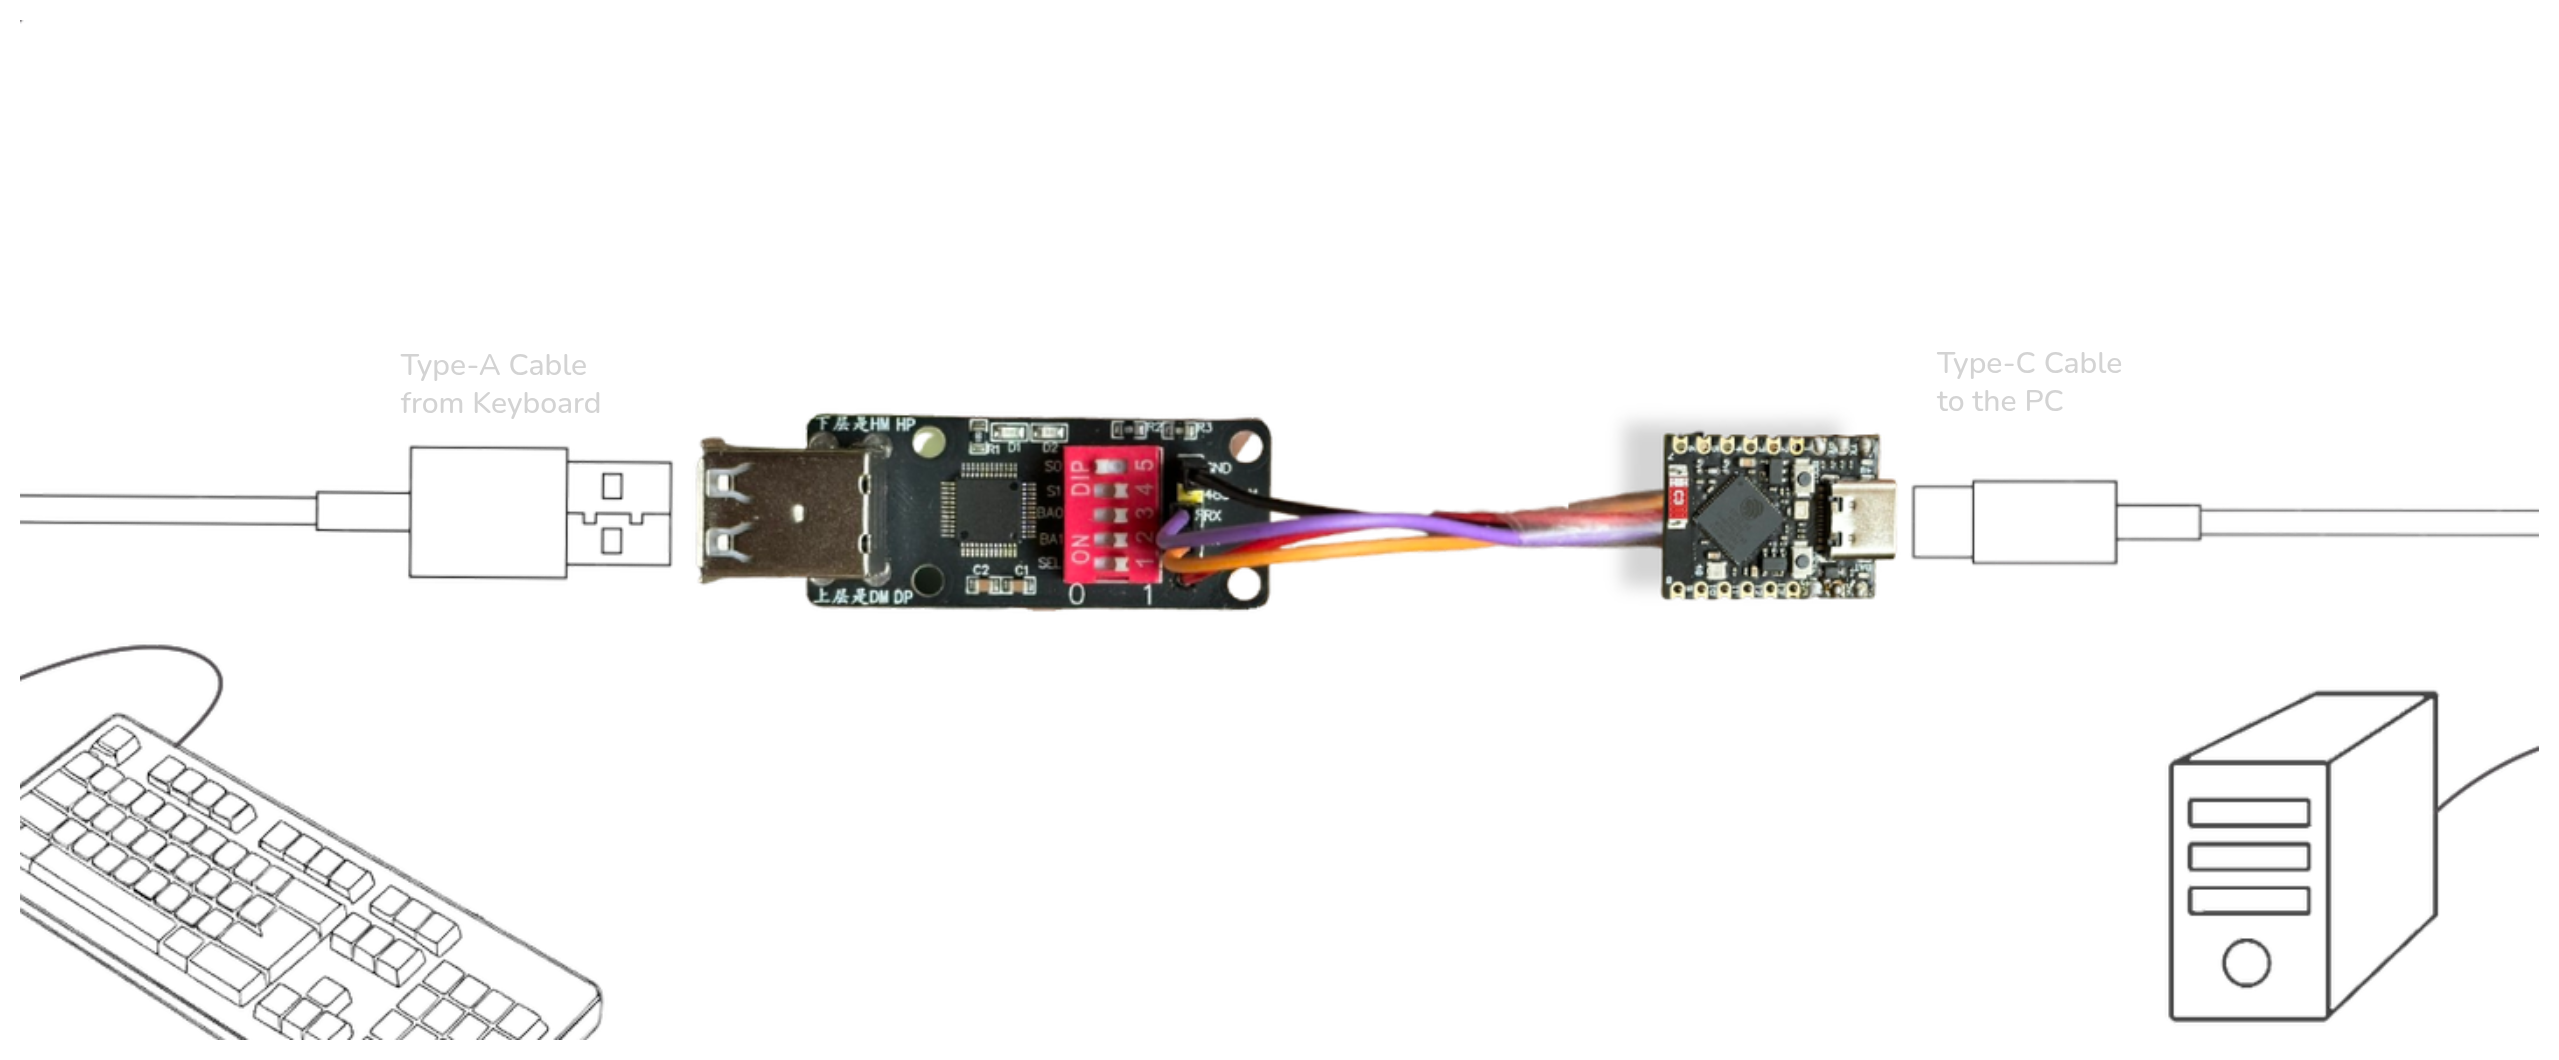 itsmmdoha/ducklogger
A ESP32-S3–based usb keylogger with wifi, easy DIY-able with widely available hardware.
 gryfman/dlpwn
Red Team tool for covert file exfiltration via Bluetooth audio transmission, encoding binary data into FLAC signals to bypass EDR, XDR, and DLP…
 h4ckusaur/cve-2024-57366
Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…
 explxx/cve-2023-33538
Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability
 d3adp3nguin/cve-2023-33105-transient-dos-in-wlan-host-and-firmware
This repository contains the exploit code for CVE-2023-33105, a vulnerability identified in Qualcomm devices. The exploit leverages authentication…
 tw-d/wifi-pineapple-mk7_evil-portal
Rogue access point toolkit for WiFi penetration testing, deploying evil portal phishing payloads to capture credentials and perform social…
 p0cl4bs/wifipumpkin3
Powerful framework for rogue access point attack.
 oblique/create_ap
[NOT MAINTAINED] This script creates a NATed or Bridged WiFi Access Point.
 danmcinerney/wifijammer
Continuously jam all wifi clients/routers
 chertogun/cve-2020-27301-hostapd
Proof-of-concept exploit for CVE-2020-27301 in hostapd, enabling rogue access point creation to test and demonstrate the vulnerability in WPA2/WPA3…