
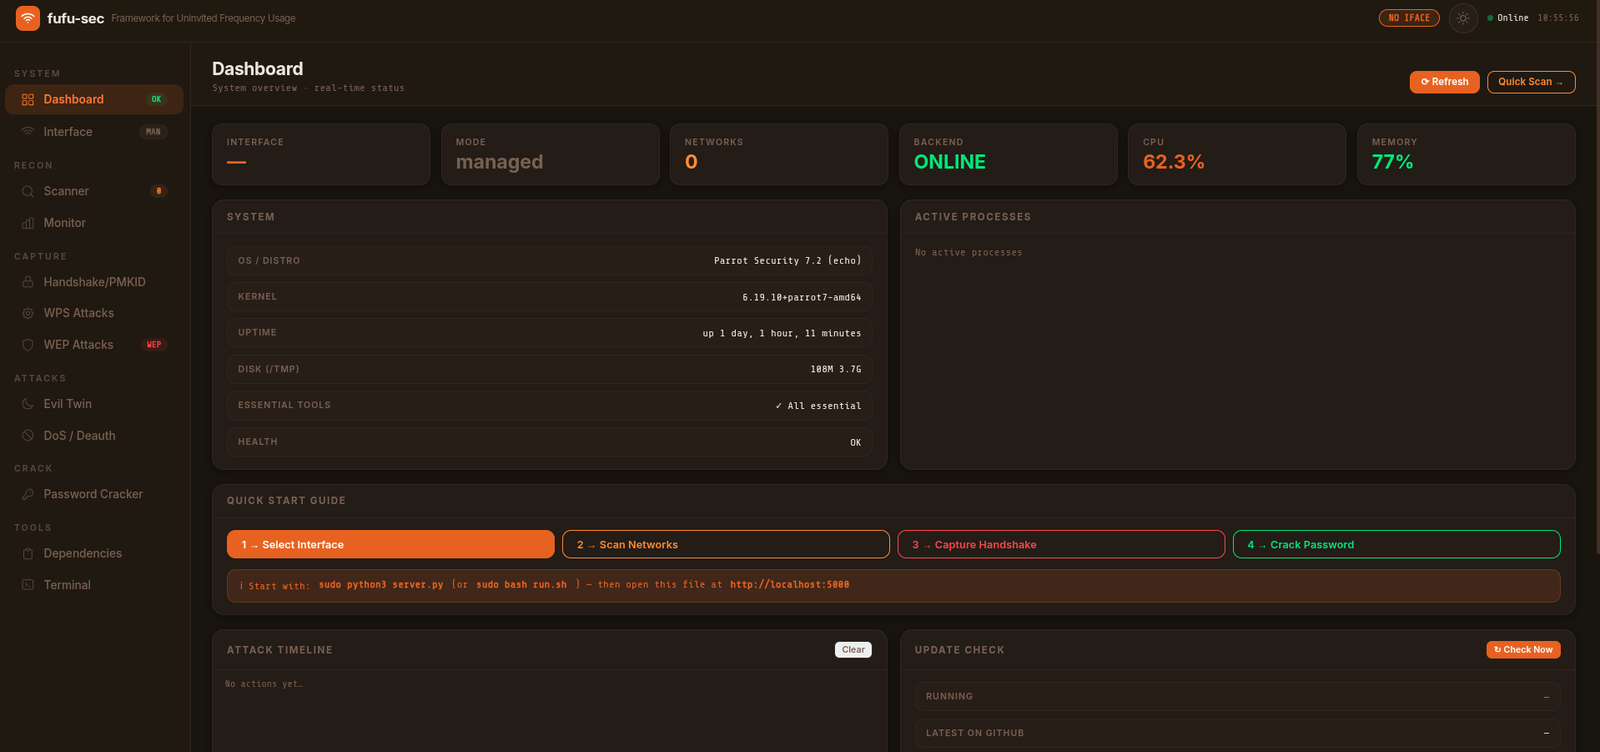
fufu-sec
 kyllr-qwen/fufu-sec
Framework for Uninvited Frequency Usage
exploitationnetwork-securitypassword-attacks+4
11
kyllr-qwen/fufu-secFramework for Uninvited Frequency Usage
 sqrtrev/cve-2021-1965
Proof-of-concept exploit for CVE-2021-1965, a WiFi zero-click RCE in Android's MBSSID parsing, causing buffer overflow and device reboot.
 vanhoefm/krackattacks-scripts
Scripts to verify WPA2 clients and APs for KRACK key reinstallation vulnerabilities using modified hostapd and monitor-mode frame replay.
 vanhoefm/fragattacks
Automated vulnerability tester for Wi-Fi clients and access points, detecting FragAttacks fragmentation/aggregation flaws through frame injection,…
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 kimocoder/android_kernel_oneplus_avicii
OnePlus Nord (avicii) NeverSettle Kernel Source
 loukious/android_kernel_xiaomi_sm8150
Nethunter kernel for the POCO X3 Pro (vayu) based on crDroid's kernel.
 sensepost/hostapd-mana
SensePost's modified hostapd for wifi attacks.
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 cappricio-securities/wifispammer
A nodemcu powered wifi spammer
 spiralbl0ck/remote-buffer-overflow-over-wifi_stack-in-wpa_supplicant-binary-in-android-11-platform-samsung-a20e
Remote buffer overflow over wifi_stack in wpa_supplicant binary in android 11, platform:samsung a20e, stock options so like works out of the box
 satheesh575555/external_wpa_supplicant_8_aosp10_r33_cve-2021-0326
Patched wpa_supplicant and hostapd for Android 10 (r33) addressing CVE-2021-0326 vulnerability in Wi-Fi client and AP components, enhancing wireless…
 satheesh575555/external_wpa_supplicant_8_aosp10_r33_cve-2021-0516
Proof-of-concept exploit for CVE-2021-0516 in wpa_supplicant on AOSP 10, demonstrating a buffer overflow vulnerability in Wi-Fi authentication.
 bishopfox/zigdiggity
A ZigBee hacking toolkit by Bishop Fox
 nanopathi/system_bt_aosp10_r33_cve-2021-0476
Android Bluetooth stack (AOSP 10 r33) containing CVE-2021-0476 for vulnerability analysis, exploitation testing, and security research.
 nanopathi/system_bt_aosp10_r33_cve-2021-0522
Android Bluetooth stack (system/bt) source code including patch for CVE-2021-0522 privilege escalation vulnerability.

 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…