wpa_supplicant_8_CVE-2021-0326.

Implementation of wpa_supplicant and hostapd with documented CVE-2021-0326 vulnerability, intended for security research and vulnerability analysis.

Implementation of wpa_supplicant and hostapd with documented CVE-2021-0326 vulnerability, intended for security research and vulnerability analysis.

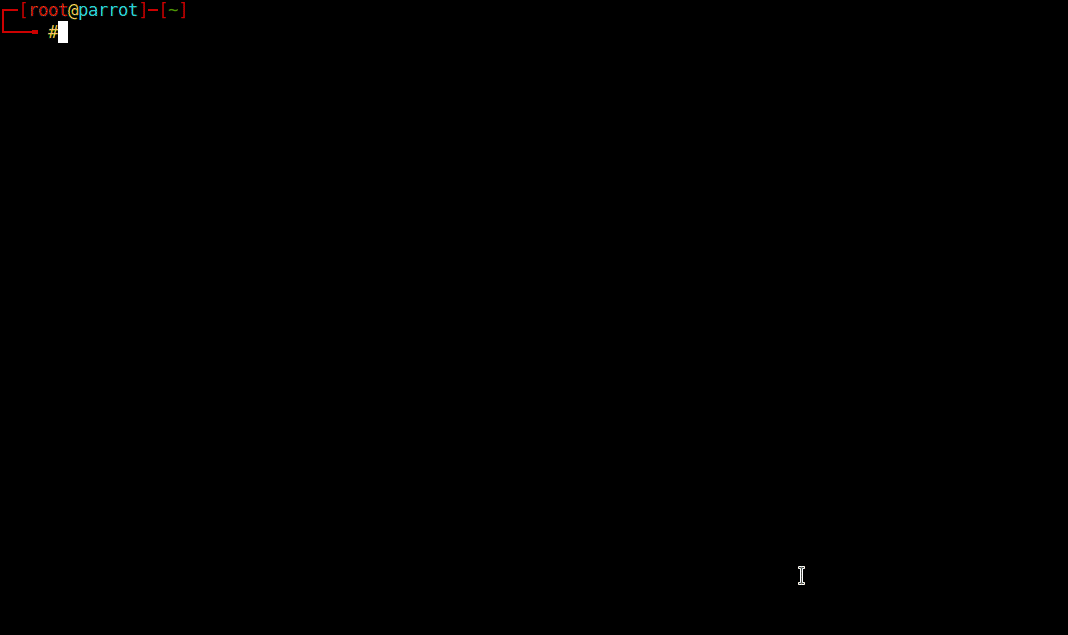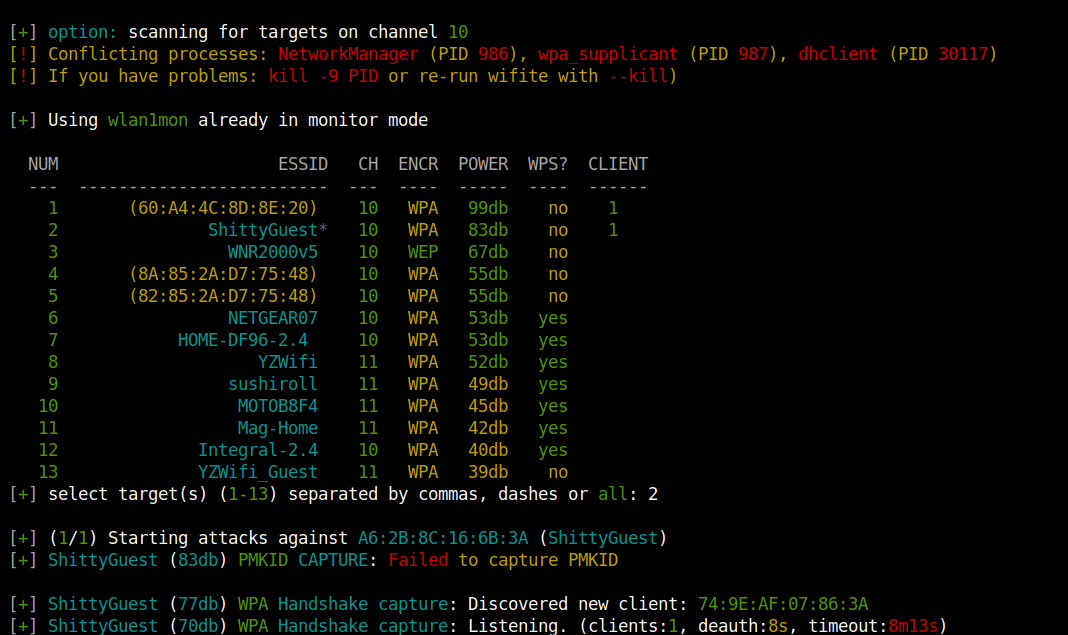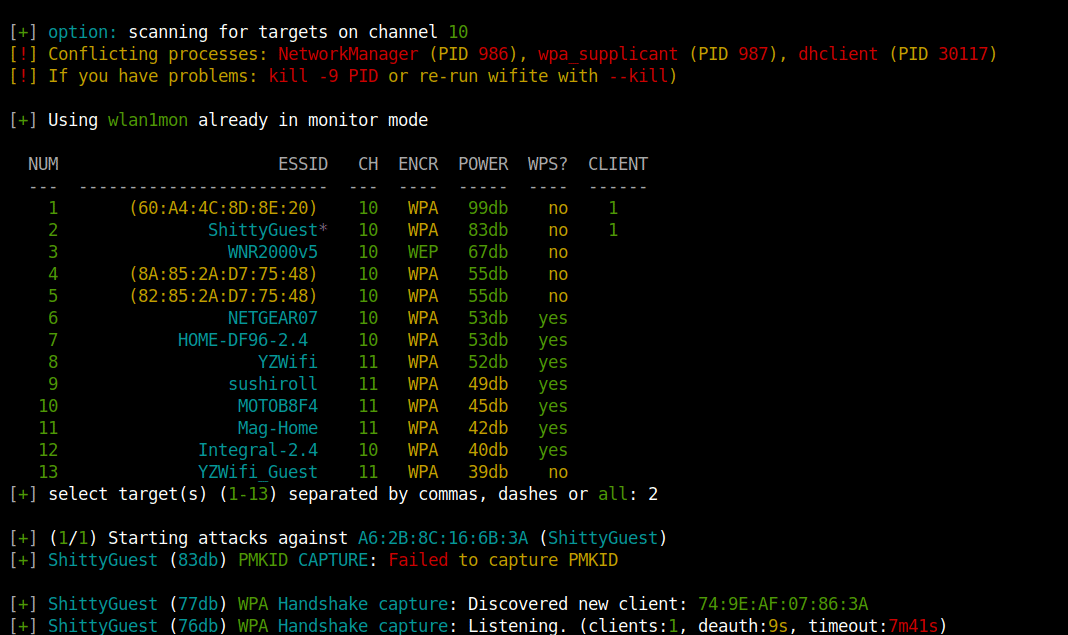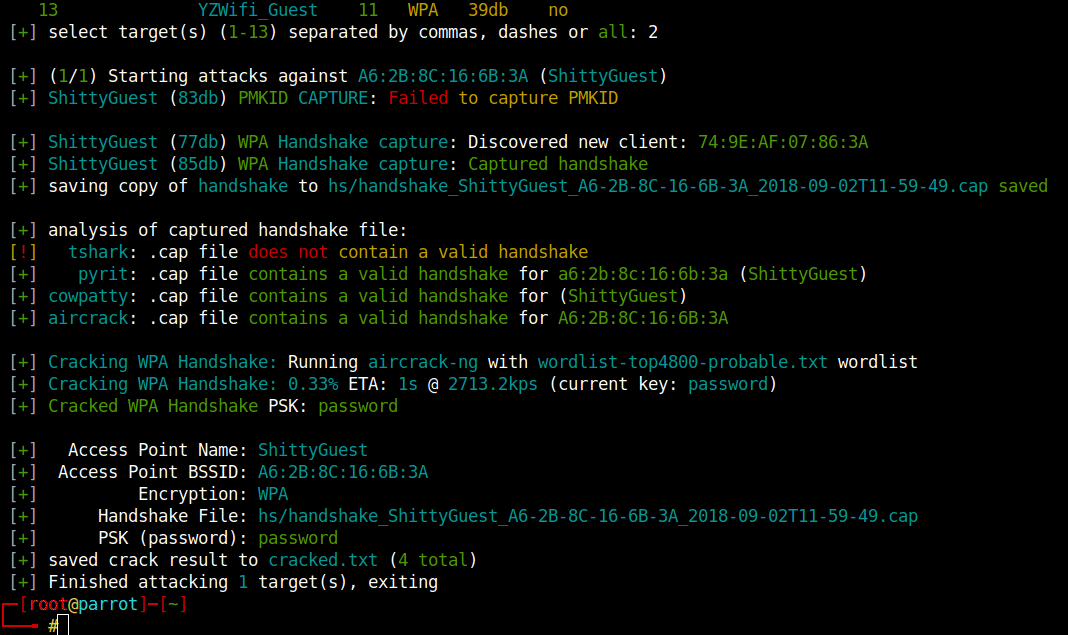
Rewrite of the popular wireless network auditor, "wifite"

Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…

Scripts to verify WPA2 clients and APs for KRACK key reinstallation vulnerabilities using modified hostapd and monitor-mode frame replay.

Automated evil twin access point toolkit with traffic capture and real-time monitoring for wireless penetration testing and security research.

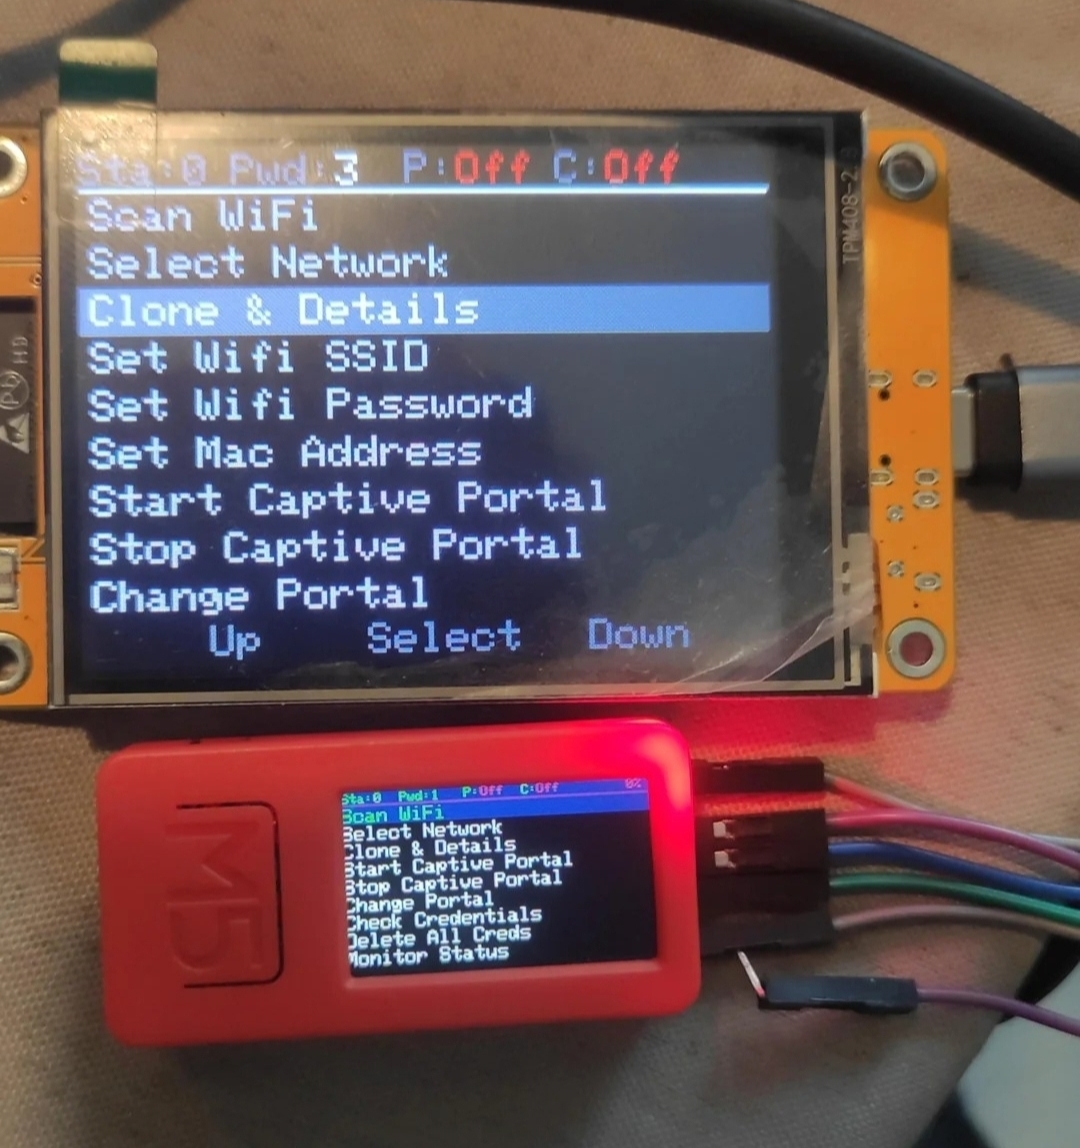
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…

Wireless Intrusion Detection System for Hak5's WiFi Coconut

Shell Script For Attacking Wireless Connections Using Built-In Kali Tools. Supports All Securities (WEP, WPS, WPA, WPA2)

A windows Wifi Brute forcing utility which is an extremely old method but still works without the requirement of external dependencies.

Continuously jam all wifi clients/routers

Targeted evil twin attacks against WPA2-Enterprise networks. Indirect wireless pivots using hostile portal attacks.

SensePost's modified hostapd for wifi attacks.

WiFi Penetration Testing & Auditing Tool

Update Version 3.1 added free SMS messaging.

HT-WPS Breaker (High Touch WPS Breaker)

Automated WiFi security testing script that captures handshakes and performs deauthentication attacks using airmon-ng and wifite for wireless…

Brute-force attack tool against WPS registrar PINs to recover WPA/WPA2 passphrases, supporting online brute force and offline Pixie Dust attacks on…