
Preferred-Network-List-Sniffer
 aleksamcode/preferred-network-list-sniffer
A reconnaissance tool for capturing and displaying SSIDs from device's Preferred Network List.
information-gatheringpacket-sniffing-analysisreconnaissance+3
178
aleksamcode/preferred-network-list-snifferA reconnaissance tool for capturing and displaying SSIDs from device's Preferred Network List.
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
 medpaf/hawk
Network, recon and offensive-security tool for Linux.
 igrsoft/kismac2
KisMAC is a free, open source wireless stumbling and security tool for Mac OS X.
 risinek/esp32-wifi-penetration-tool
Exploring possibilities of ESP32 platform to attack on nearby Wi-Fi networks.
 emrekybs/wifi-purple
Automated WiFi security testing script that captures handshakes and performs deauthentication attacks using airmon-ng and wifite for wireless…
 ymsniper/kto
Automated Wi-Fi deauthentication tool that continuously scans for clients on a target SSID and kicks non-whitelisted devices. Features whitelist…
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
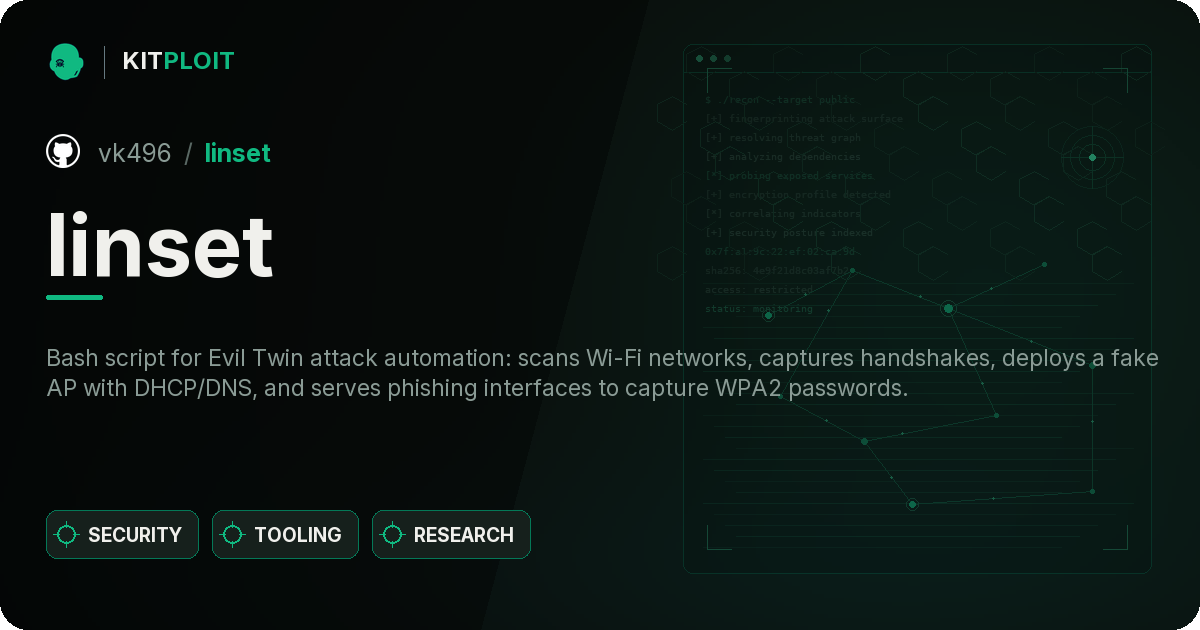
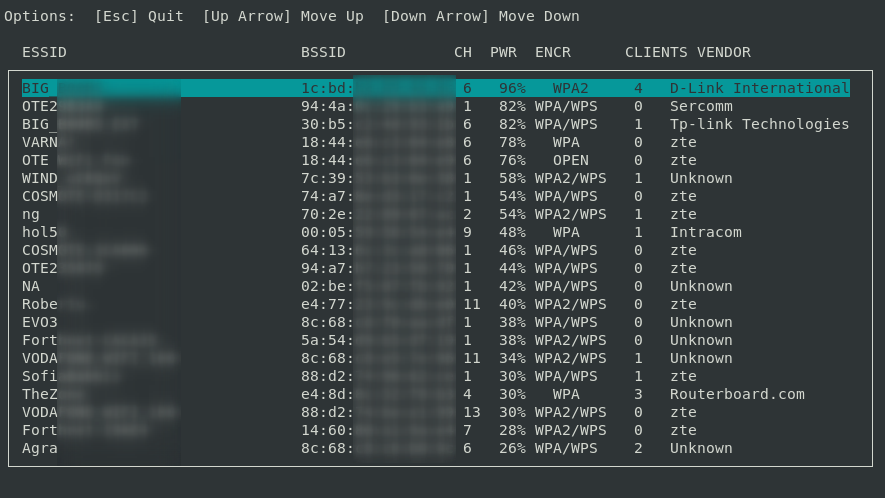 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 syworks/wireless-ids
Ability to detect suspicious activity such as (WEP/WPA/WPS) attack by sniffing the air for wireless packets.
 fluxionnetwork/fluxion
Automated WPA/WPA2 phishing tool that captures handshakes, spawns a rogue access point, and lures users to a captive portal to harvest credentials…
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 xtr4nge/fruitywifi
FruityWiFi is a wireless network auditing tool. The application can be installed in any Debian based system (Jessie) adding the extra packages.…
 entropy1337/infernal-twin
wireless hacking - This is automated wireless hacking tool
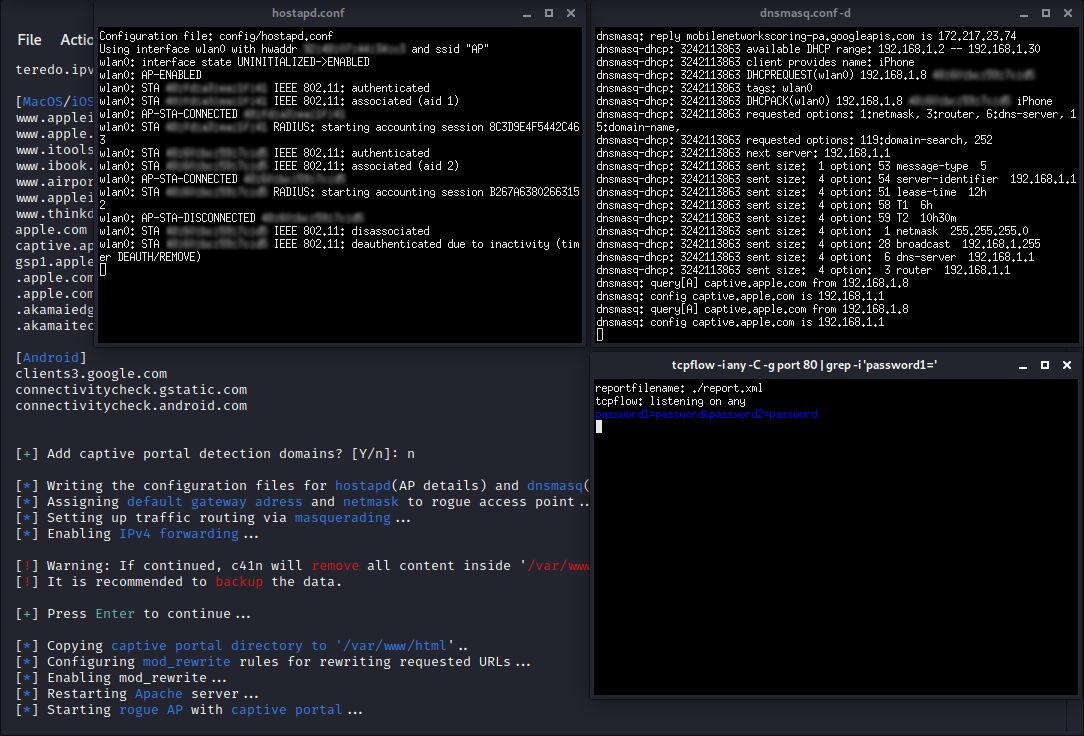 ms-web-bn/c41n
Automated rogue access point setup tool.
