

wifipumpkin3
 p0cl4bs/wifipumpkin3
Powerful framework for rogue access point attack.
captcha-bypassdns-analysisphishing+5
p0cl4bs/wifipumpkin3Powerful framework for rogue access point attack.
 aress31/wirespy
Framework designed to automate various wireless networks attacks (the project was presented on Pentester Academy TV's toolbox in 2017).
 chertogun/cve-2020-27301-hostapd
Proof-of-concept exploit for CVE-2020-27301 in hostapd, enabling rogue access point creation to test and demonstrate the vulnerability in WPA2/WPA3…
 dybrkr/wifi_leak
Proof-of-concept exploit for CVE-2018-4084, a WiFi credential leak vulnerability in macOS High Sierra, demonstrating interception of plaintext Wi-Fi…
 xtr4nge/fruitywifi
FruityWiFi is a wireless network auditing tool. The application can be installed in any Debian based system (Jessie) adding the extra packages.…
 seemoo-lab/openwifipass
An open source implementation of Apple's Wi-Fi Password Sharing protocol in Python.
 0ct0sec/m5porkchop
ON NO! Someone put an RPG in a packet sniffer
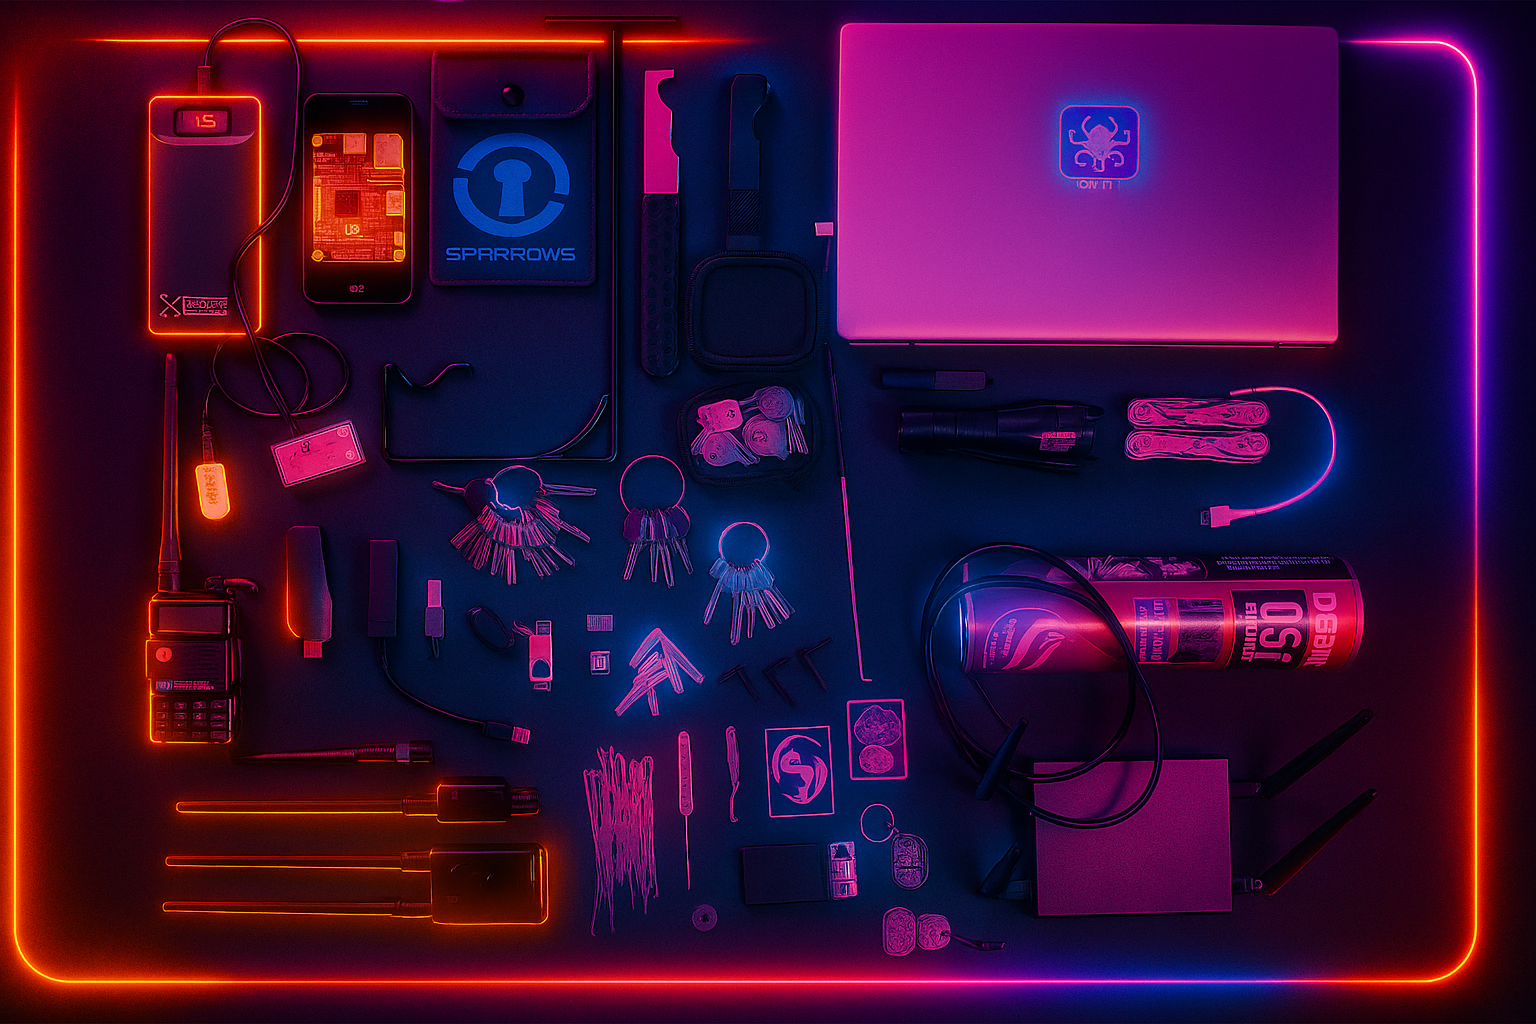 davidprobinsky/redteam-physical-tools
Red Team Toolkit - A curated list of tools that are commonly used in the field for Physical Security, Red Teaming, and Tactical Covert Entry.
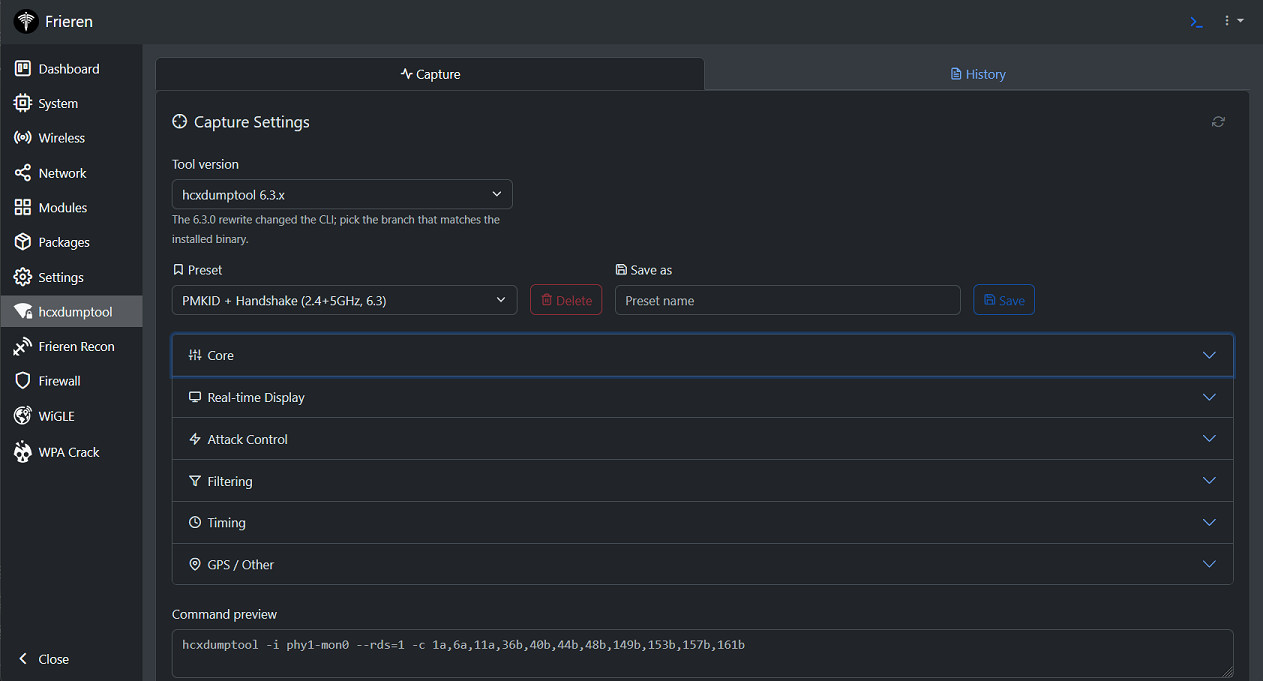 xchwarze/frieren
Frieren is a micro-framework designed for use in routers and Single Board Computers (SBCs). This framework is built to be lightweight, efficient, and…
 souravbaghz/radareeye
Tool for especially scanning nearby devices and execute a given command on its own system while the target device comes in range.
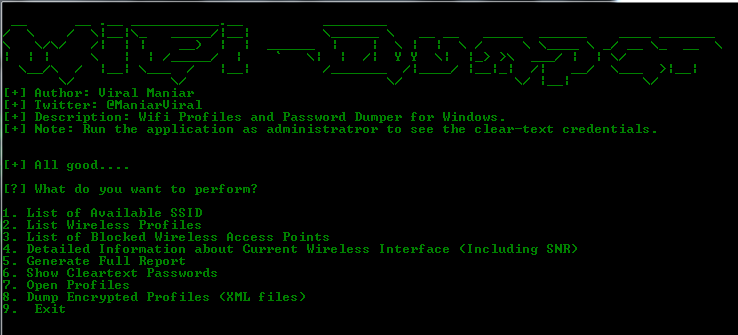 viralmaniar/wifi-dumper
This is an open source tool to dump the wifi profiles and cleartext passwords of the connected access points on the Windows machine. This tool will…
 momenbasel/autowifi
Wireless penetration testing framework. Automates WPA/WPA2/WEP/WPS attacks - recon to exploitation in one command. aircrack-ng + hashcat + PMKID.
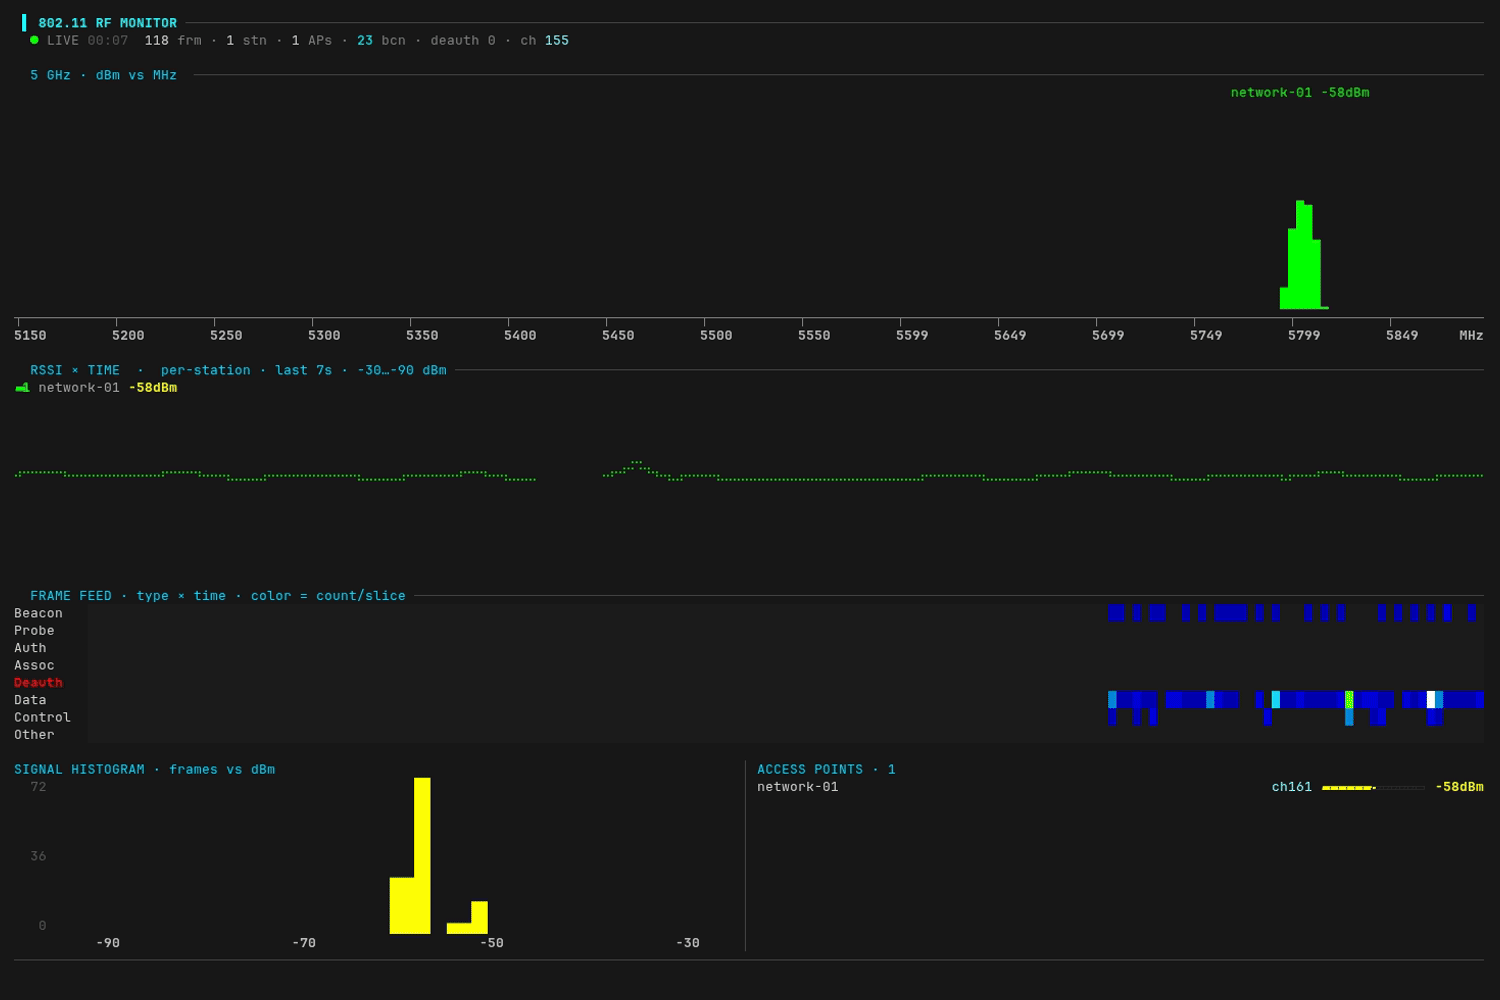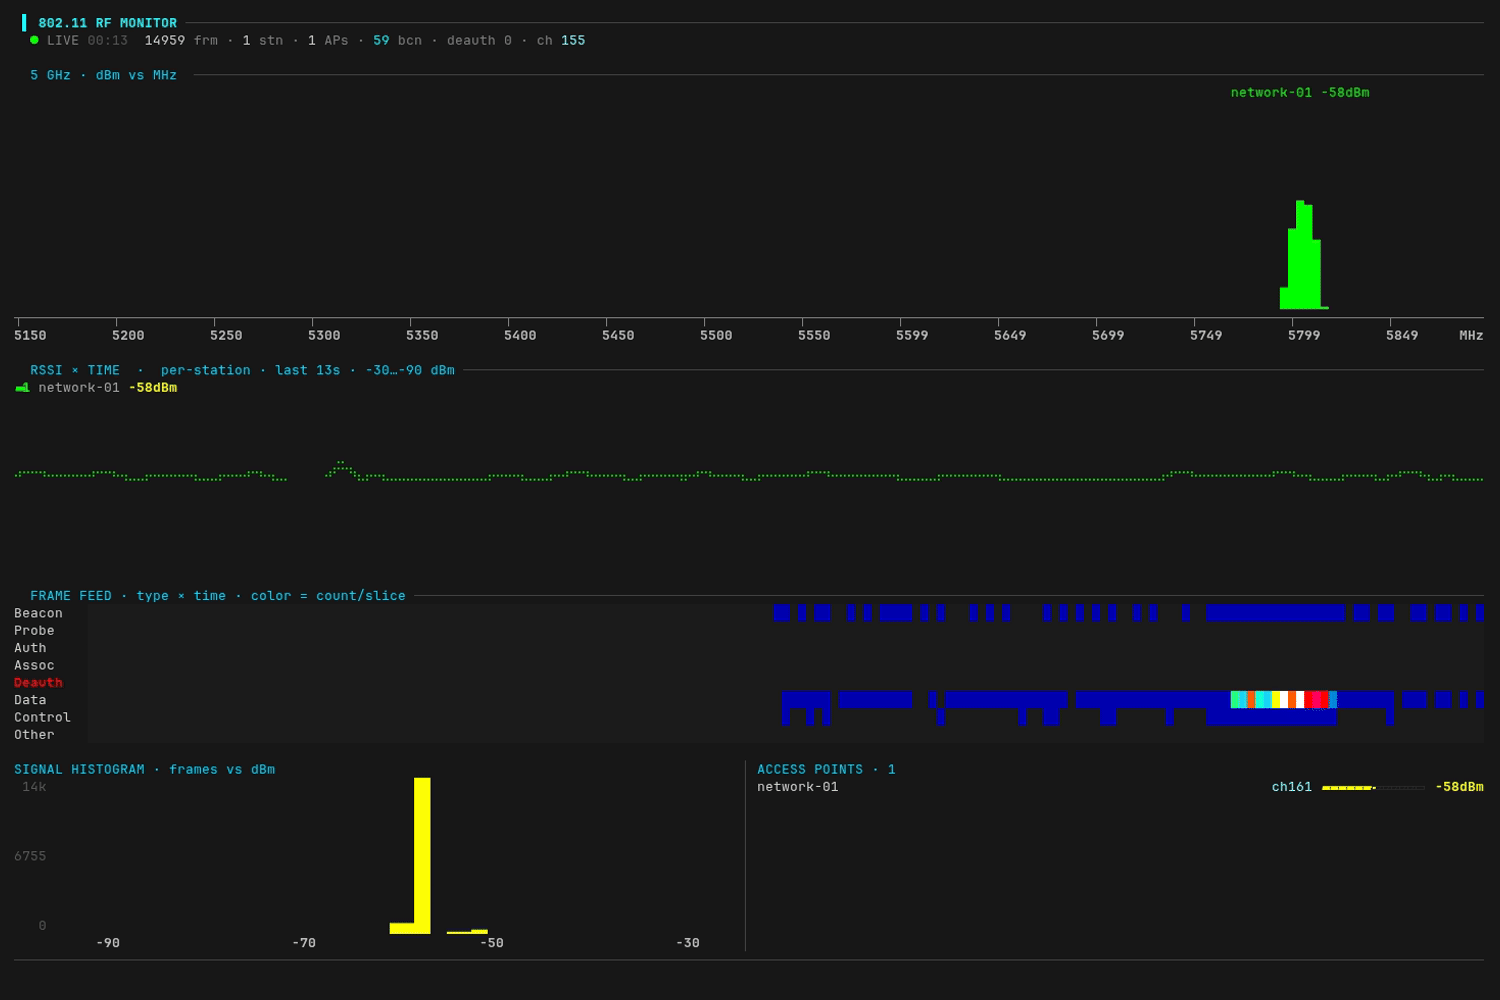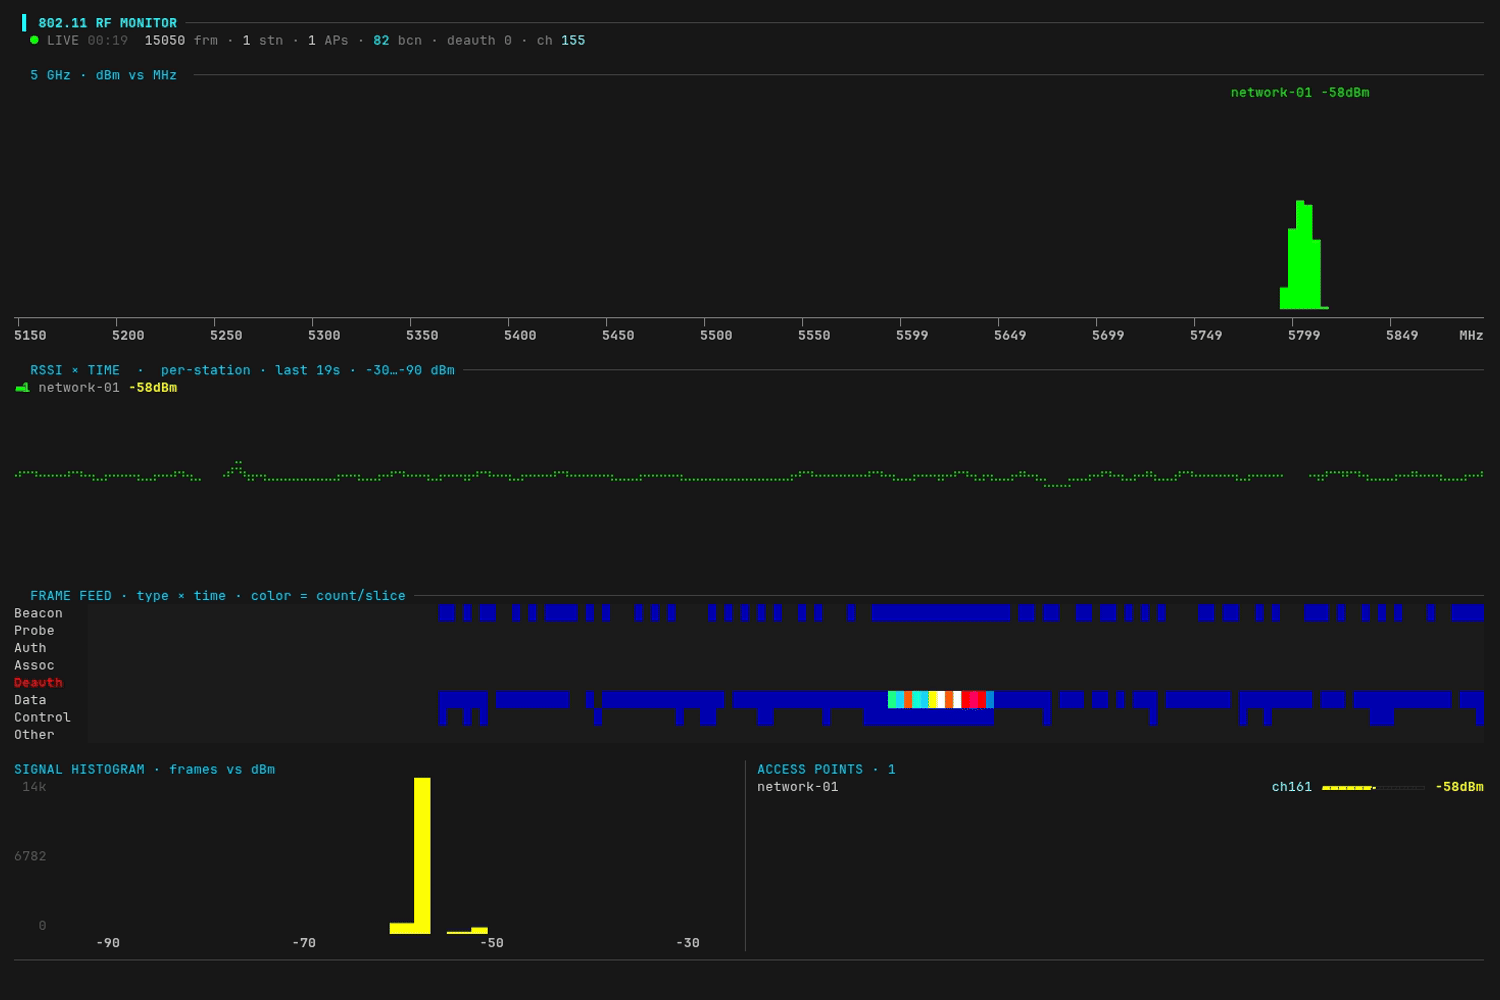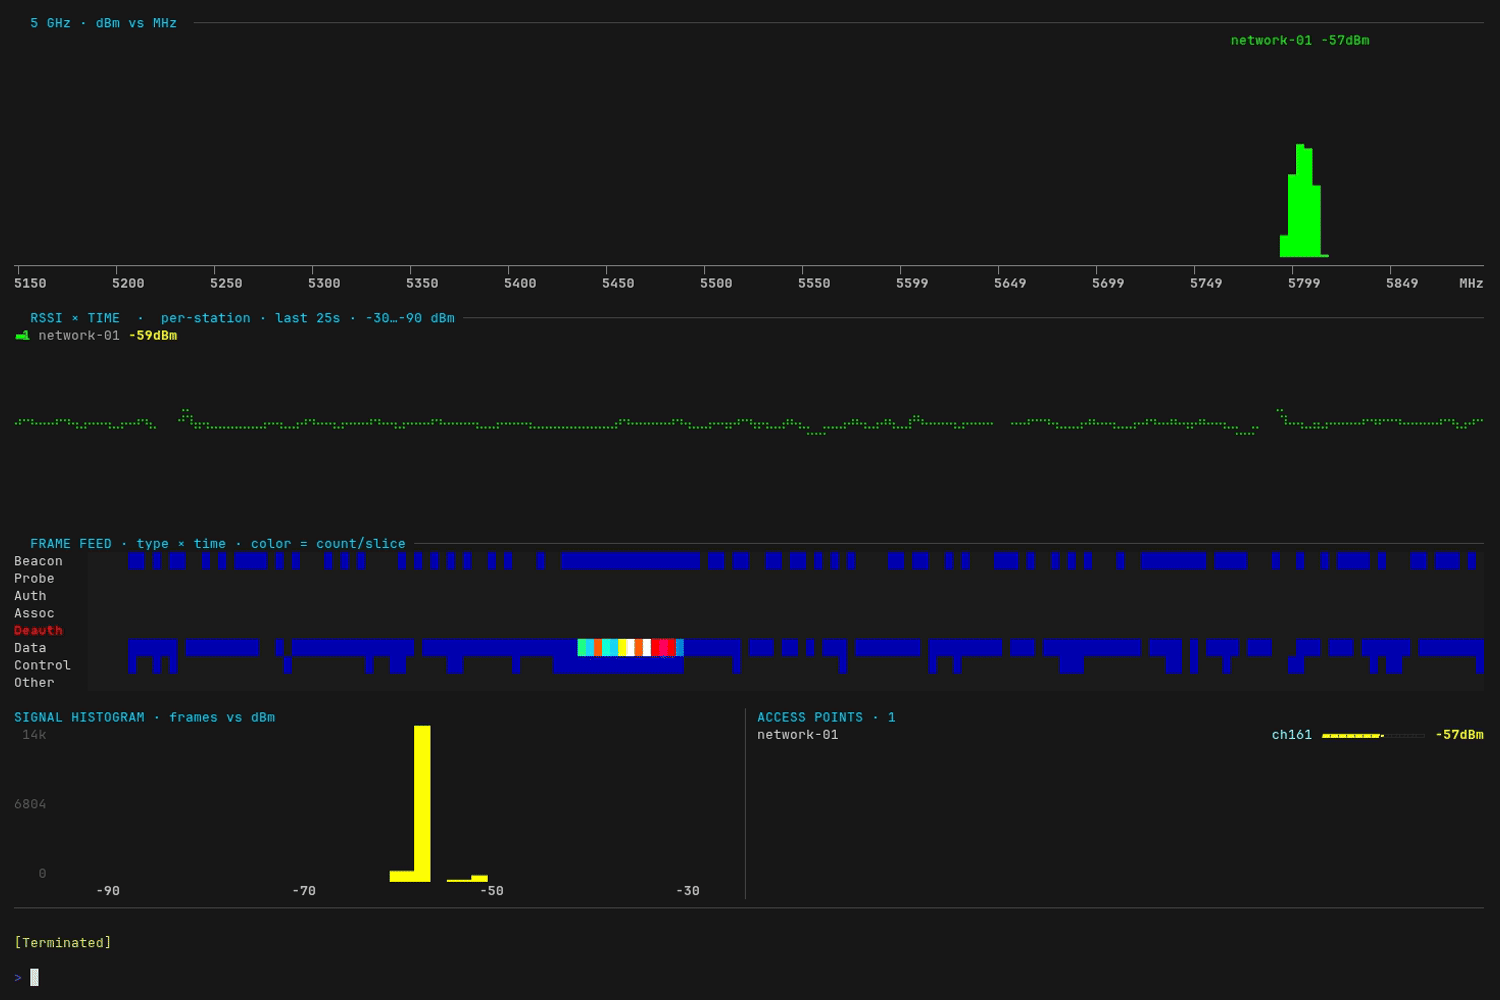 yeet-src/airtop
htop for the airwaves — a live 802.11 (Wi-Fi) RF dashboard in your terminal
 s0c5/remotepasswordwifi
Script in Ruby. Break Remote router wifi passwords.
 unsignedchad/bcm4360-wpa3
wpa3 functionality for the wifi chip in a 2014 macbook pro
 hunt-benito/mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce
Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…
 uthrasri/frameworks_opt_net_wifi_cve-2021-0390
Android Wi-Fi framework patch for CVE-2021-0390, addressing a remote code execution vulnerability in the Wi-Fi subsystem.
 satheesh575555/external_wpa_supplicant_8_aosp10_r33_cve-2021-0516
Proof-of-concept exploit for CVE-2021-0516 in wpa_supplicant on AOSP 10, demonstrating a buffer overflow vulnerability in Wi-Fi authentication.