
hcxtools
 zerbea/hcxtools
A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
hash-analysispassword-crackingpenetration-testing-frameworks+2
2.5k
zerbea/hcxtoolsA small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
 qkaiser/broadcom-wps
Tools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.
 justcallmekoko/esp32marauder
A suite of WiFi/Bluetooth offensive and defensive tools for the ESP32
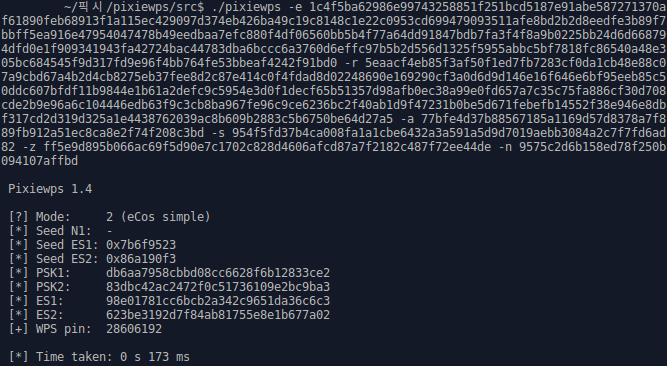 wiire-a/pixiewps
An offline Wi-Fi Protected Setup brute-force utility
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 buybitart/cyclepatrol
Bash tool for on-foot Wi-Fi security checks in a loop, with evidence reports. (re-invented wifi WarDriving)
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 phantom-brigade1/wifisting
GTK4 and CLI wireless security toolkit with 57 standalone modules for Wi-Fi, Bluetooth, 802.15.4, SDR/RF, NFC and router-side or network MITM testing…
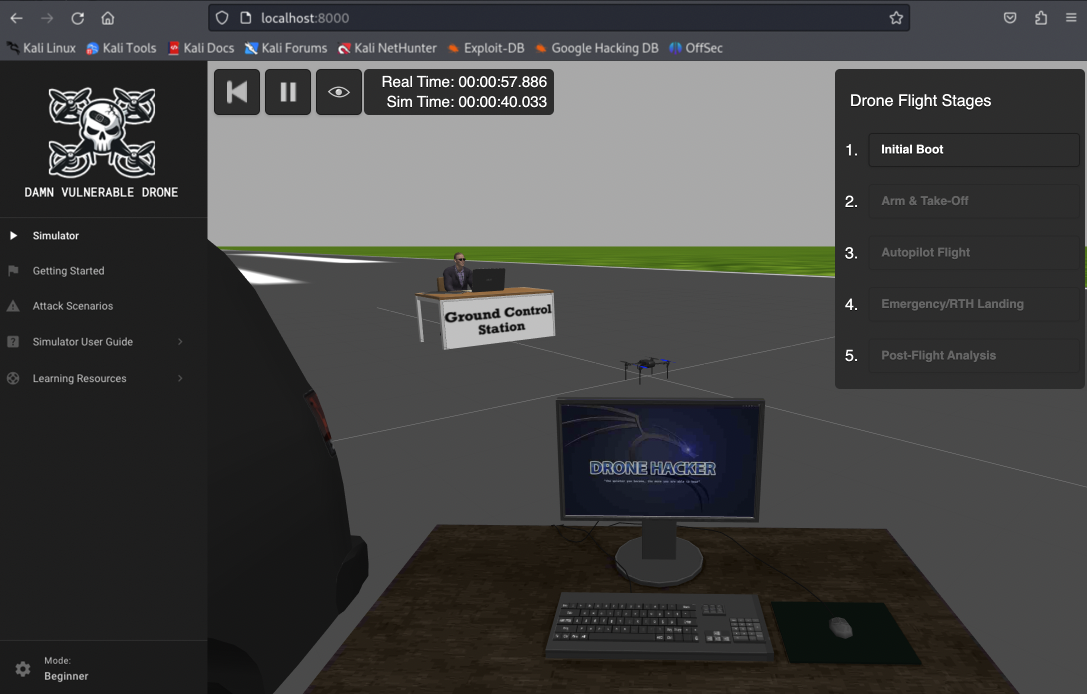 nicholasaleks/damn-vulnerable-drone
Damn Vulnerable Drone is an intentionally vulnerable drone hacking simulator based on the popular ArduPilot/MAVLink architecture, providing a…
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
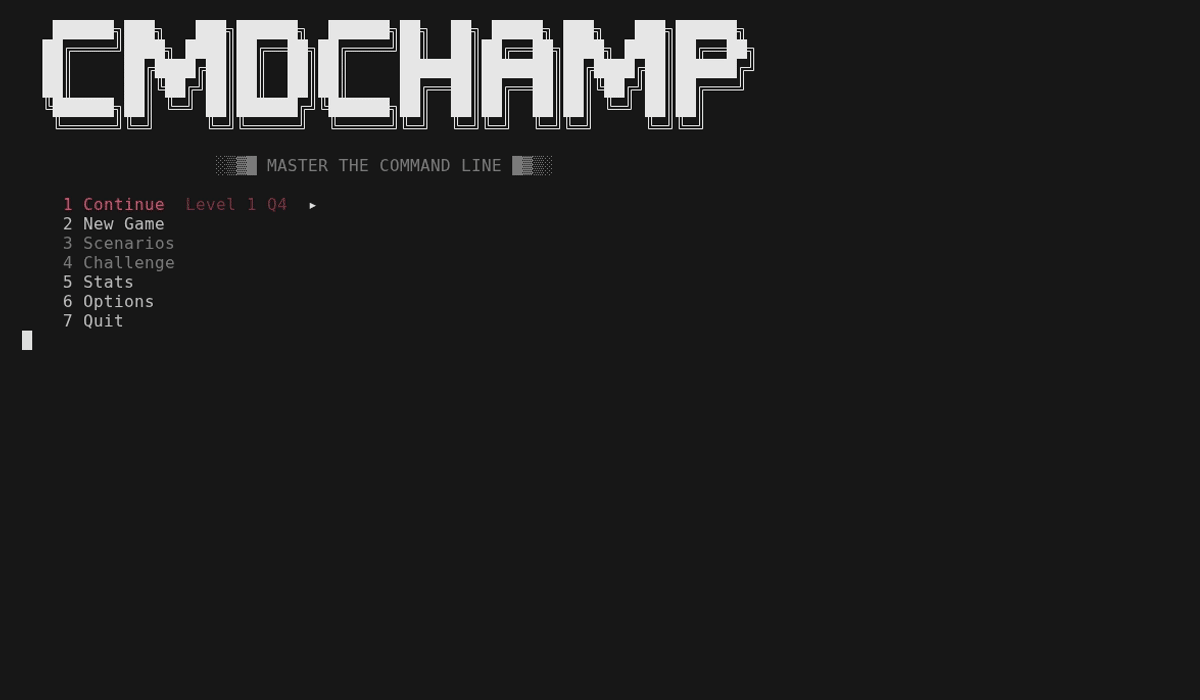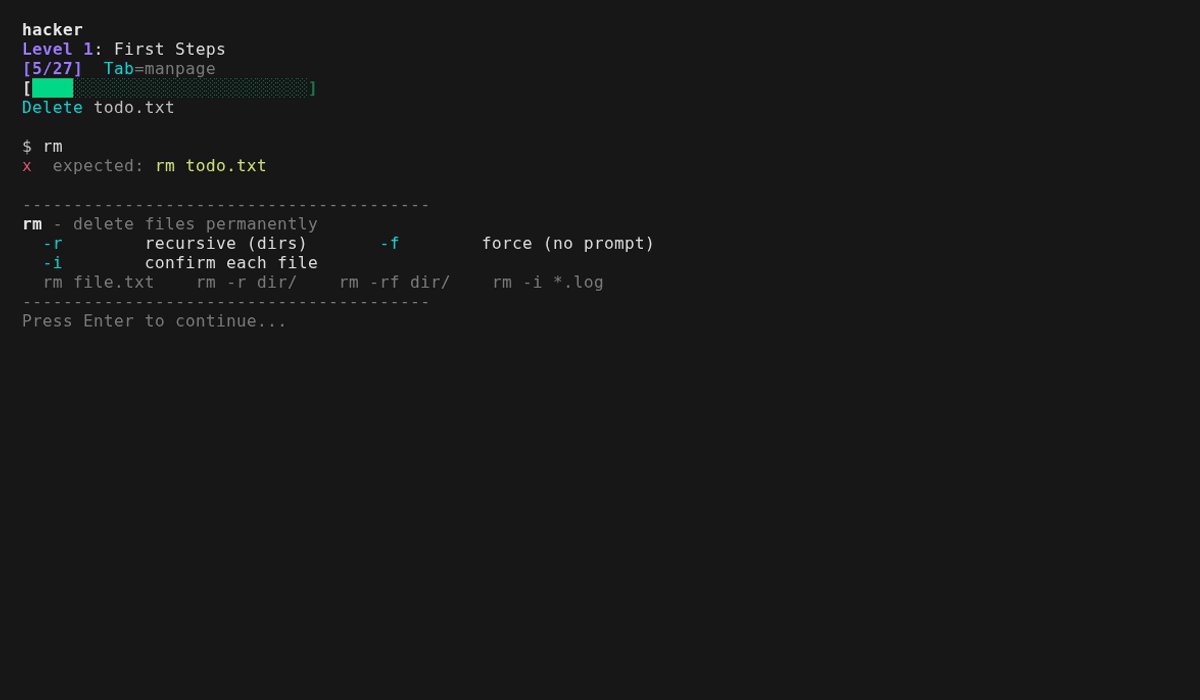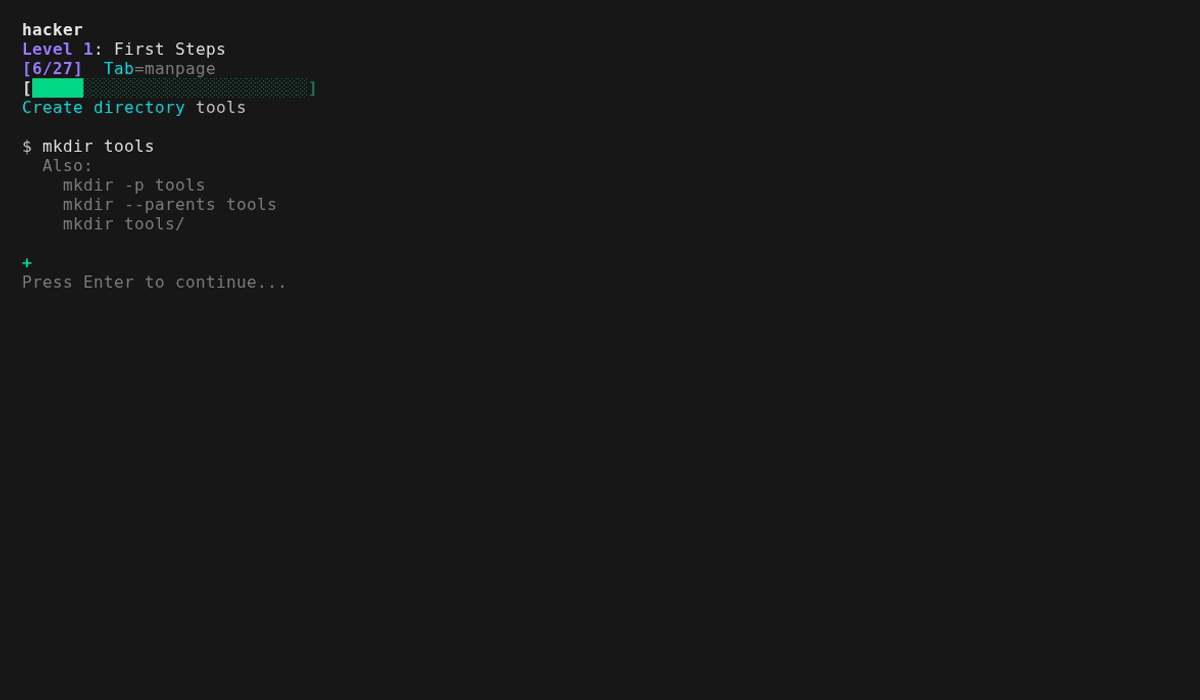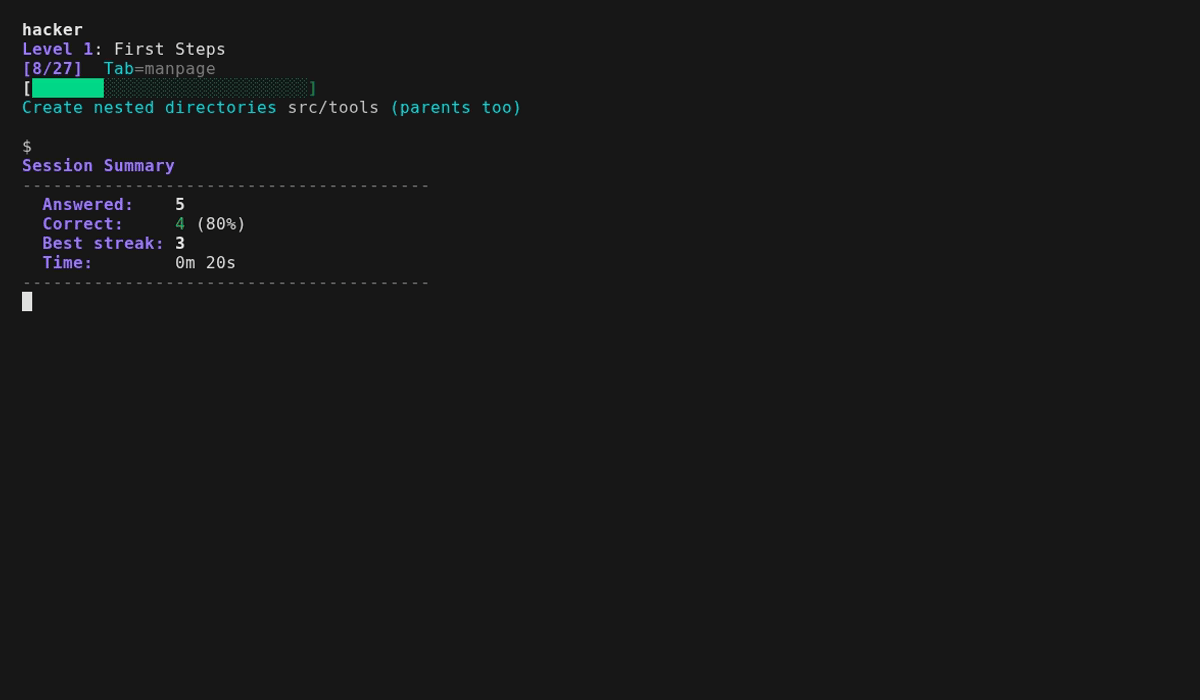 mellen9999/cmdchamp
bash CLI trainer — 30 levels from ls to privilege escalation
 seemoo-lab/openwifipass
An open source implementation of Apple's Wi-Fi Password Sharing protocol in Python.
 bettercap/caplets
caplets and proxy modules.
 unsignedchad/bcm4360-wpa3
wpa3 functionality for the wifi chip in a 2014 macbook pro
 hunt-benito/mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce
Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…