
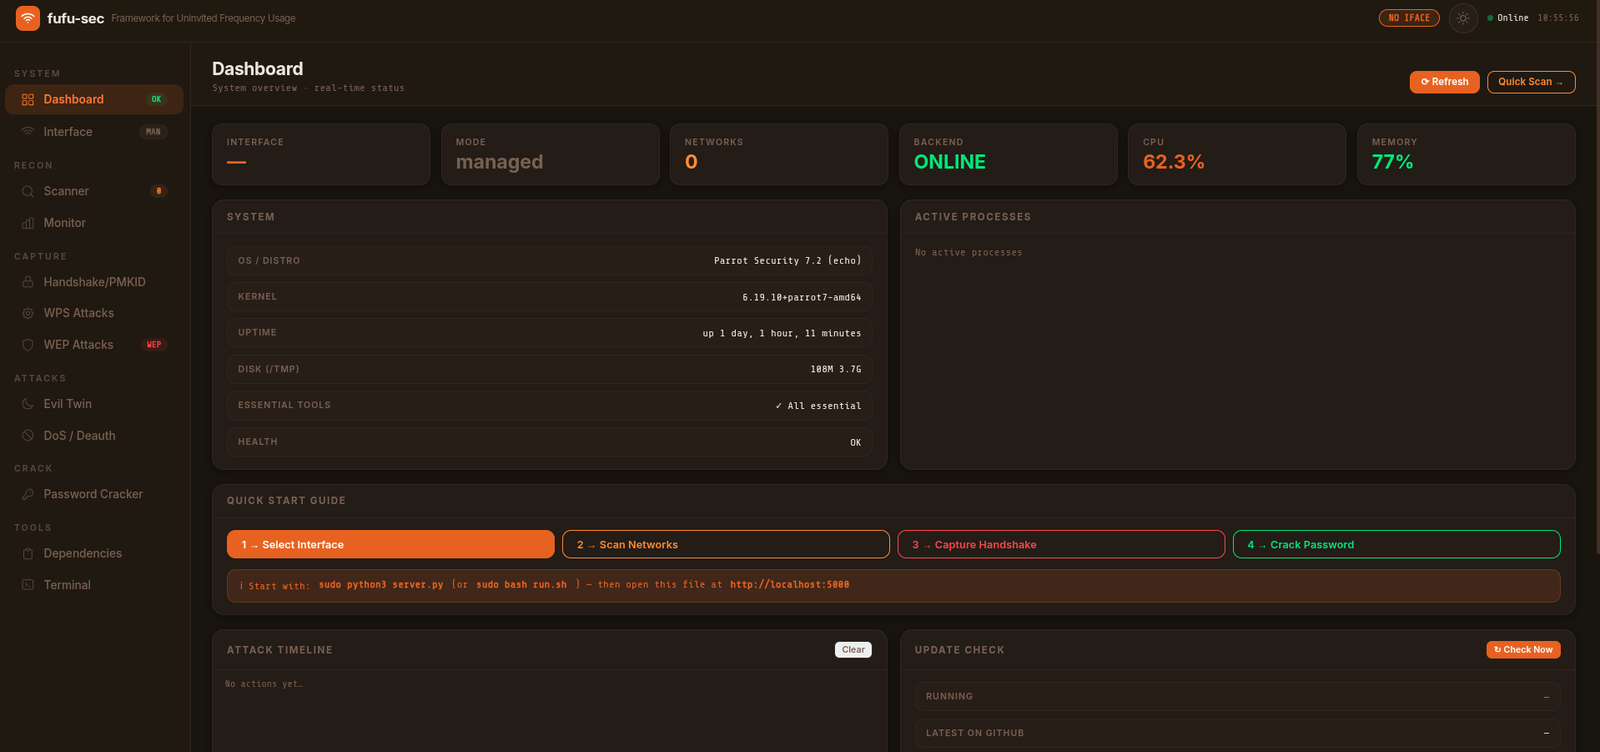
fufu-sec
 kyllr-qwen/fufu-sec
Framework for Uninvited Frequency Usage
exploitationnetwork-securitypassword-attacks+4
kyllr-qwen/fufu-secFramework for Uninvited Frequency Usage
 vanhoefm/krackattacks-scripts
Scripts to verify WPA2 clients and APs for KRACK key reinstallation vulnerabilities using modified hostapd and monitor-mode frame replay.
 vanhoefm/fragattacks
Automated vulnerability tester for Wi-Fi clients and access points, detecting FragAttacks fragmentation/aggregation flaws through frame injection,…
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
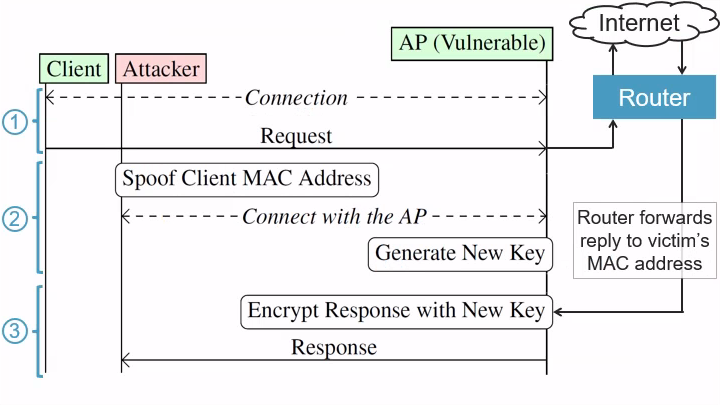 vanhoefm/macstealer
MacStealer: Wi-Fi Client Isolation Bypass
 sensepost/hostapd-mana
SensePost's modified hostapd for wifi attacks.
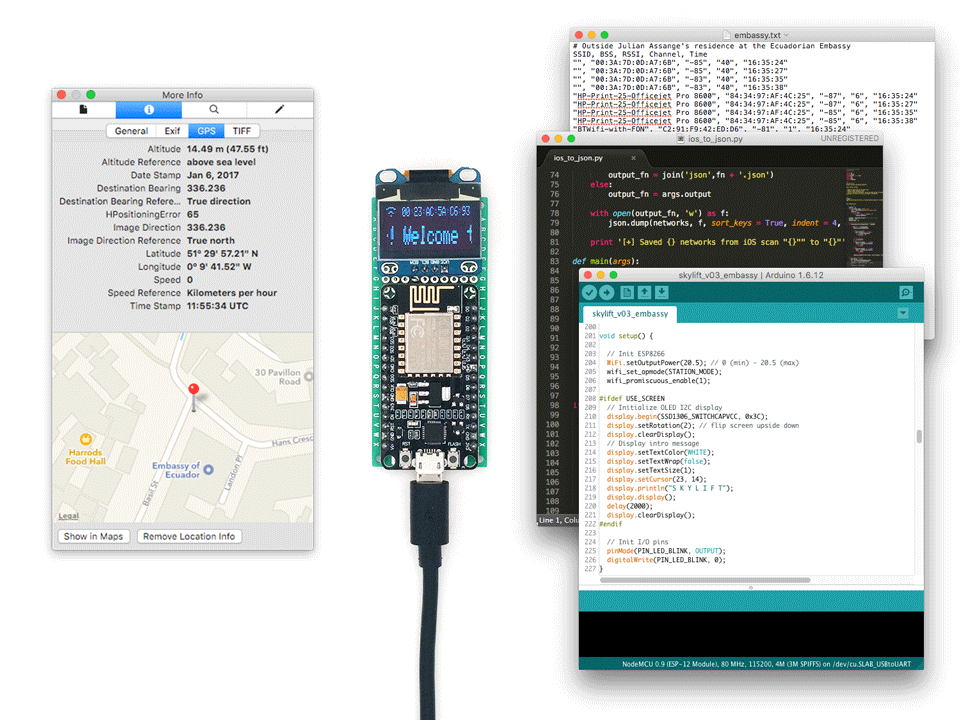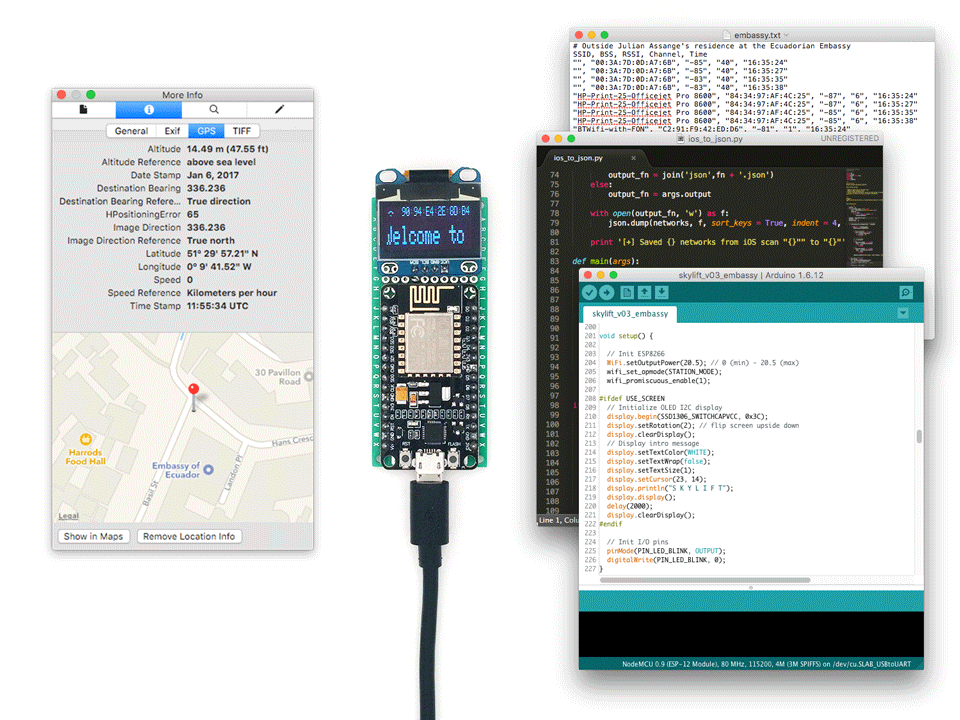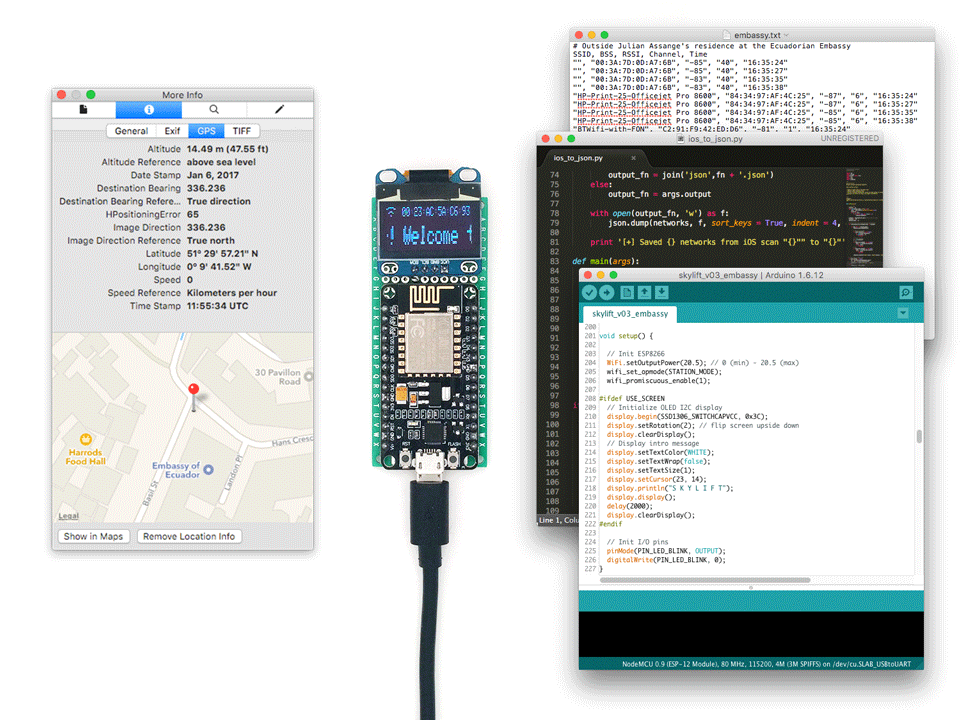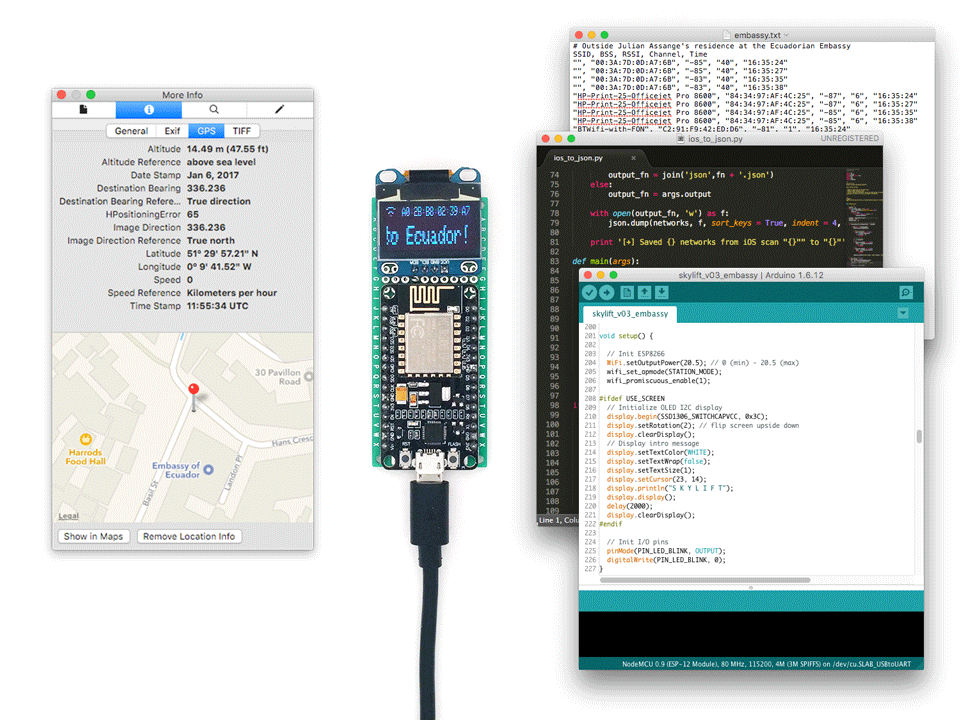 awesome-pentest-gadgets/skylift
WiFi Geolocation Spoofing with the ESP8266
 adamhrv/skylift
Wi-Fi Geolocation Spoofing with ESP8266 / ESP32
 cappricio-securities/wifispammer
A nodemcu powered wifi spammer
 satheesh575555/external_wpa_supplicant_8_aosp10_r33_cve-2021-0516
Proof-of-concept exploit for CVE-2021-0516 in wpa_supplicant on AOSP 10, demonstrating a buffer overflow vulnerability in Wi-Fi authentication.
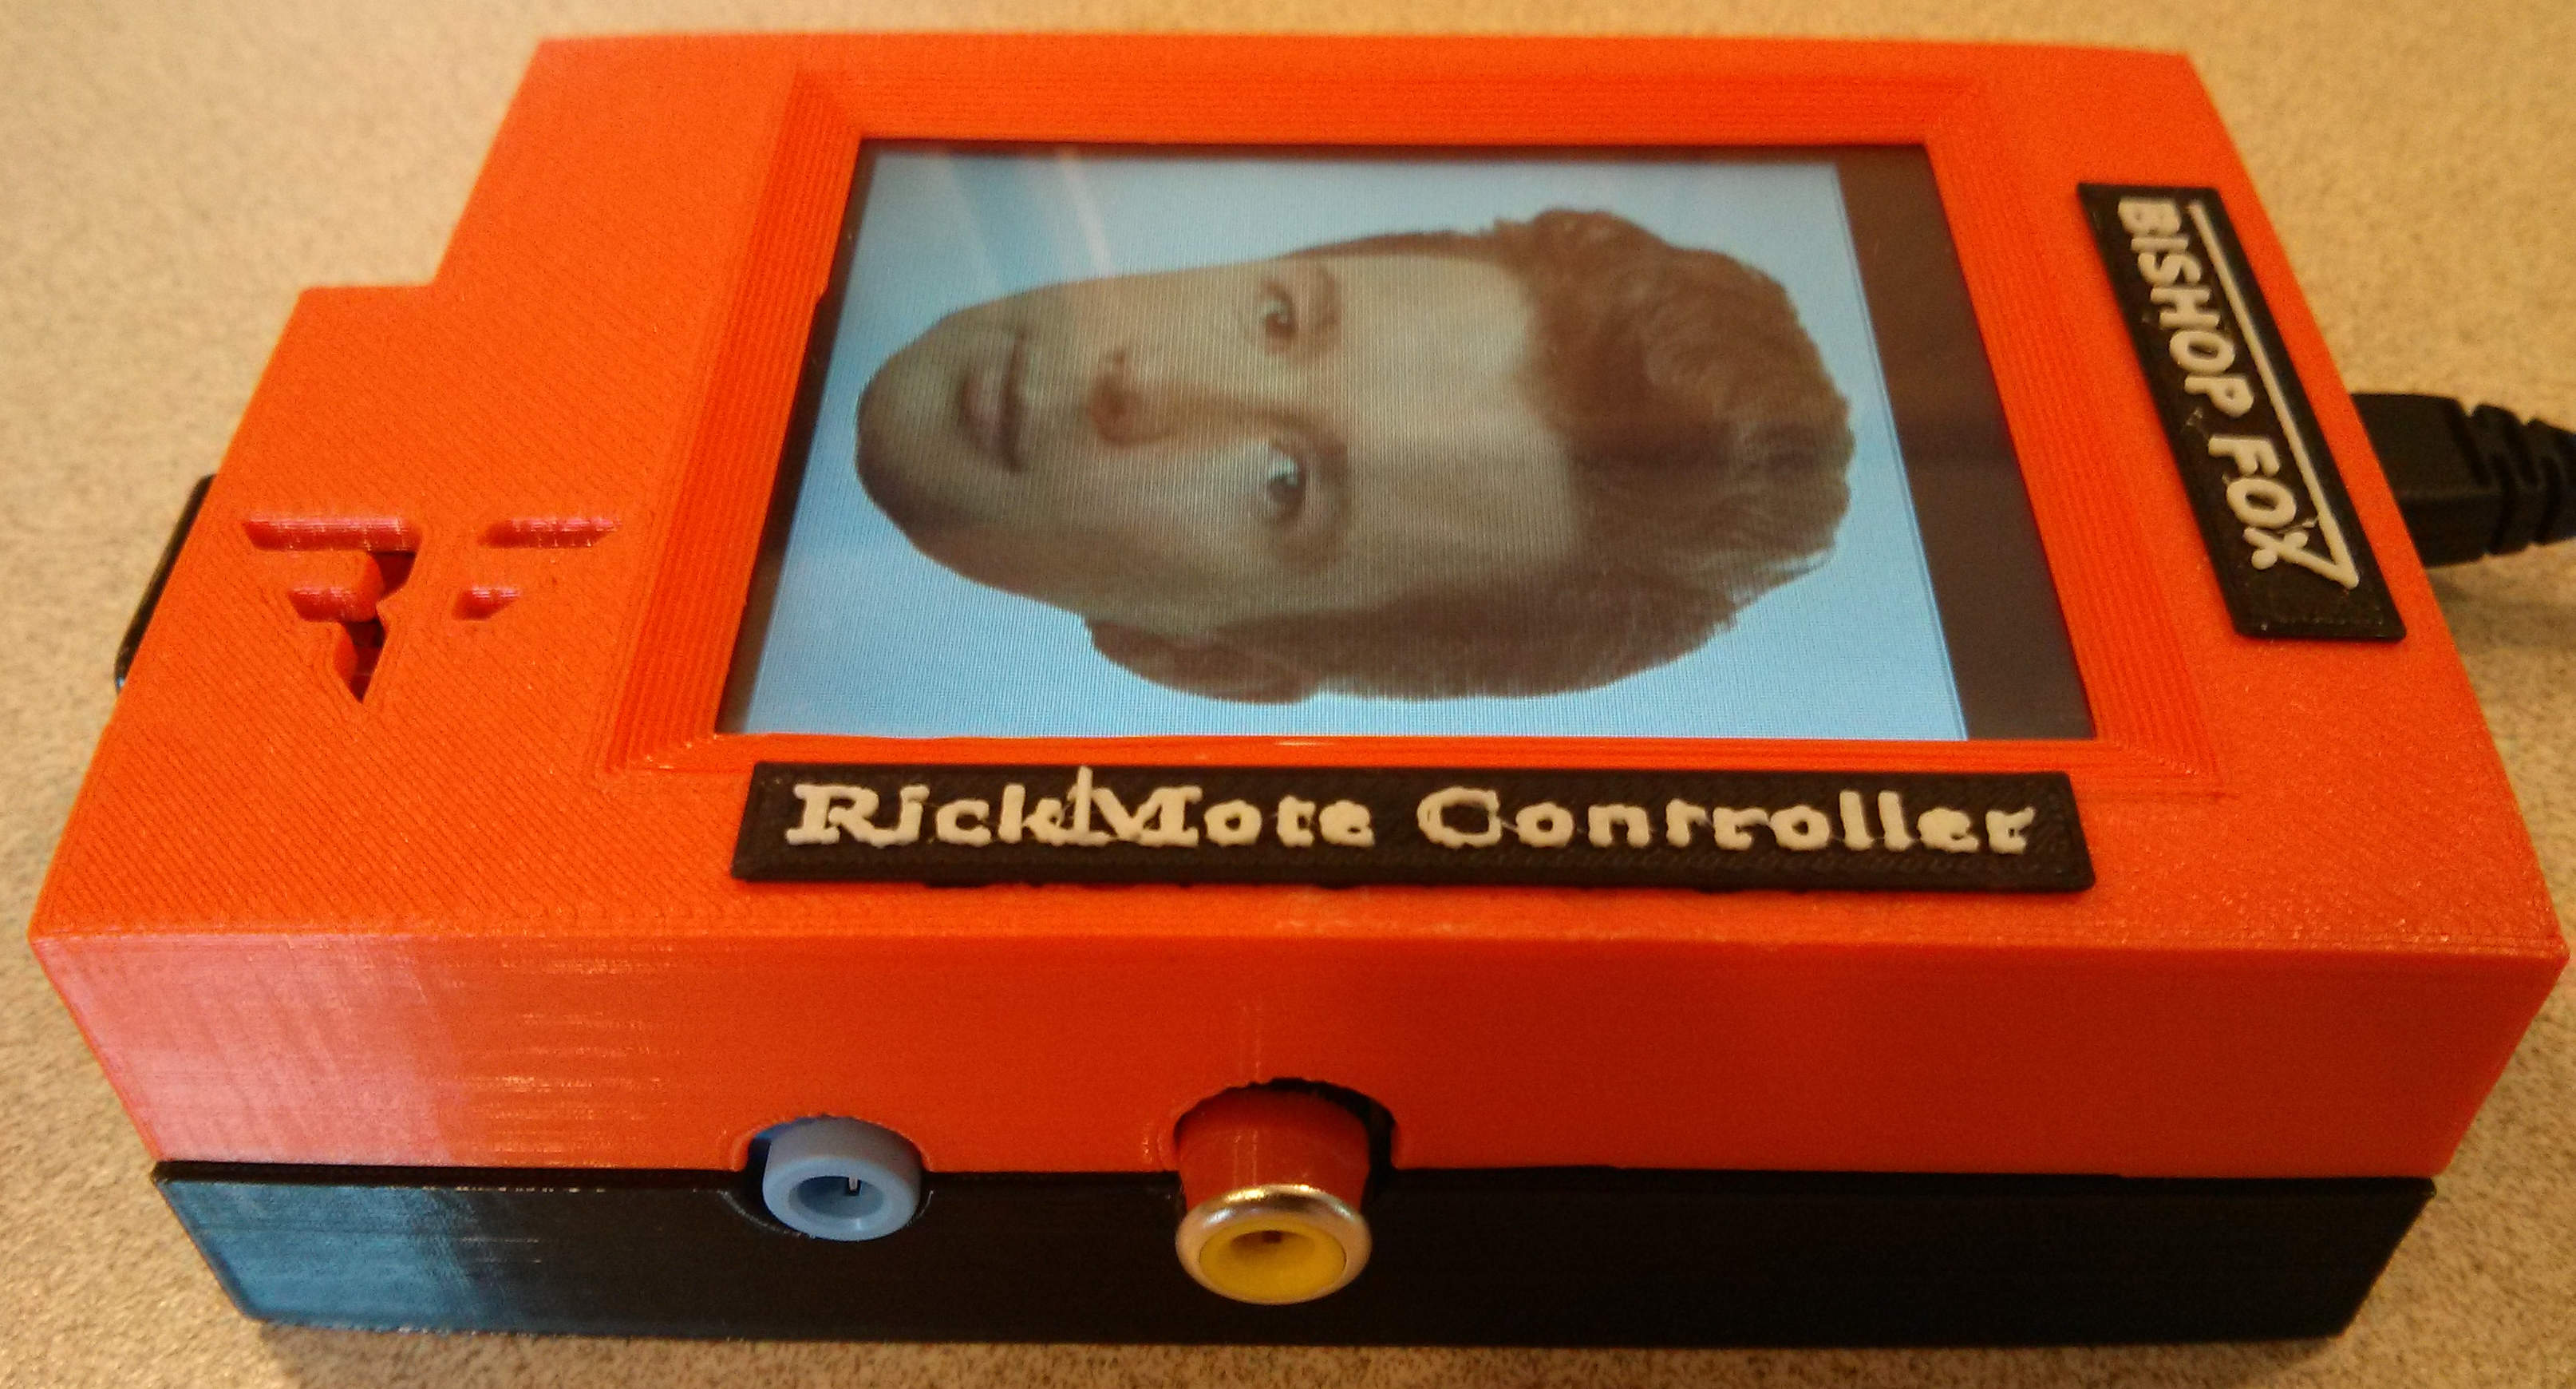 bishopfox/rickmote
The Rickmote Controller: Hijack TVs using Google Chromecast
 nanopathi/wpa_supplicant_8_cve-2021-0326.
Implementation of wpa_supplicant and hostapd with documented CVE-2021-0326 vulnerability, intended for security research and vulnerability analysis.
 jmalinen/hostap
Clone of w1.fi hostap.git - NOTE: This is not the main development location and pull requests for this repository are ignored. See the upstream…
 danmcinerney/wifi-monitor
Prints the IPs on your local network that're sending the most packets
 s0c5/remotepasswordwifi
Script in Ruby. Break Remote router wifi passwords.
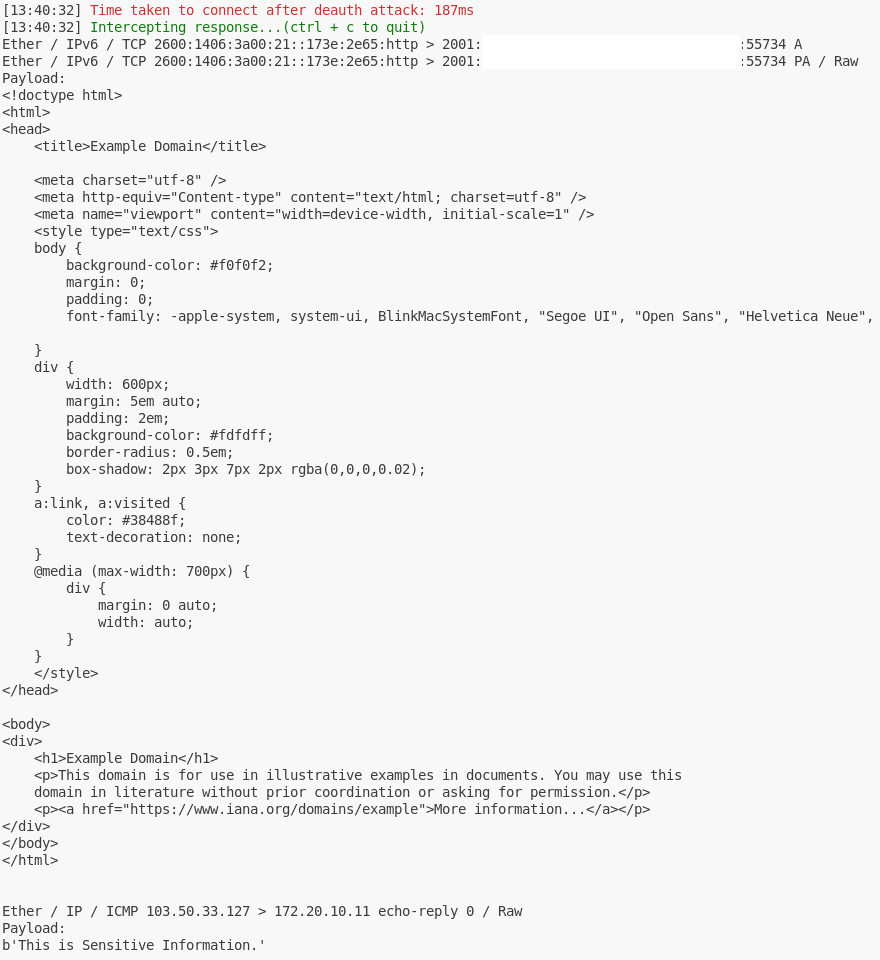 toffeenutt/cve-2022-47522-poc
Proof-of-concept exploit for CVE-2022-47522 demonstrating Wi-Fi frame interception via deauthentication attack and MAC address spoofing to capture…