

altair
 evilsocket/altair
Modular web vulnerability scanner with template-driven detection engine for automated testing of XSS, SQLi, LFI, RFI, and sensitive file/directory…
penetration-testingvulnerability-analysisweb-security+1
51
evilsocket/altairModular web vulnerability scanner with template-driven detection engine for automated testing of XSS, SQLi, LFI, RFI, and sensitive file/directory…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 vulnquest58/pressvector
PressVector - Advanced WordPress Vulnerability Scanner CVE-2026-63030 (REST batch route confusion) / CVE-2026-60137 (SQLi) Developer: Vulnquest
 zhzyker/vulmap
Web vulnerability scanner and exploitation tool with POC/EXP modes for known CVEs across webapps such as Weblogic, Shiro, Struts2, and Tomcat;…
 malwareman007/scanner-and-patcher
A Web Vulnerability Scanner and Patcher
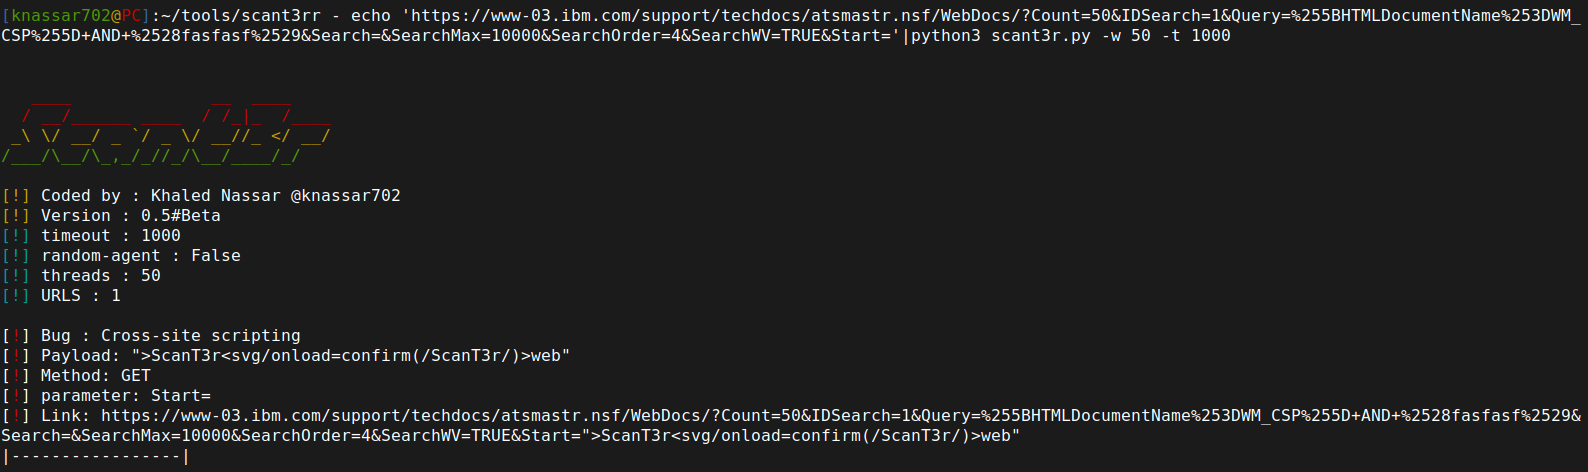 mindpatch/scant3r
Module-based web vulnerability scanner and bug bounty automation framework with built-in XSS, SSTI, SSRF, and Firebase detection engines. Designed to…
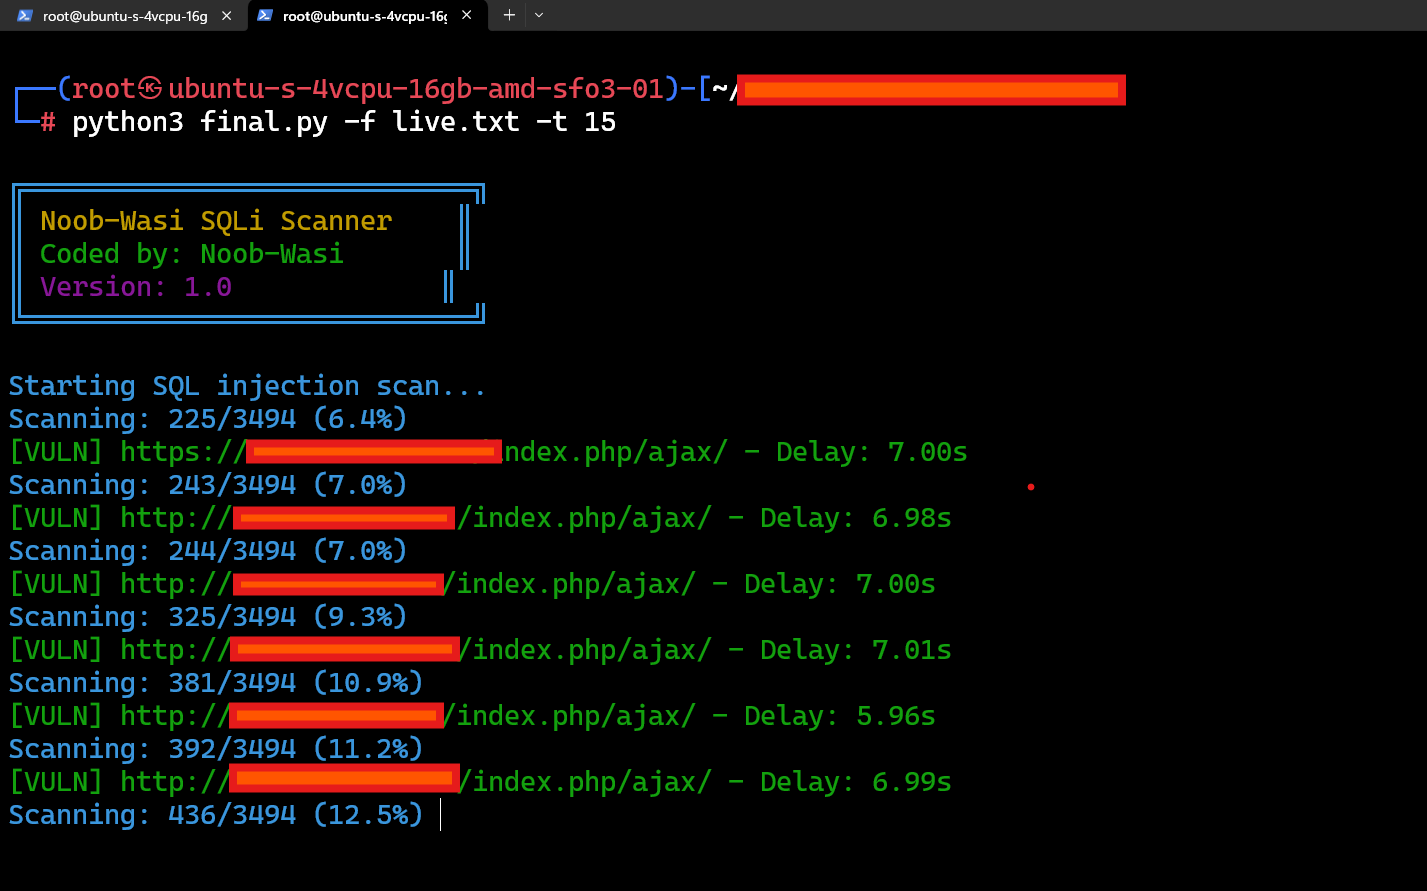 muhammadwaseem29/cve-2025-24799
CVE-2025-24799 SQLi Scanner
 fgeek/pyfiscan
Free web-application vulnerability and version scanner
 0xlipon/xss2shell
🔥 XSS2Shell — CVE-2026-64638 Scanner & PoC Toolkit
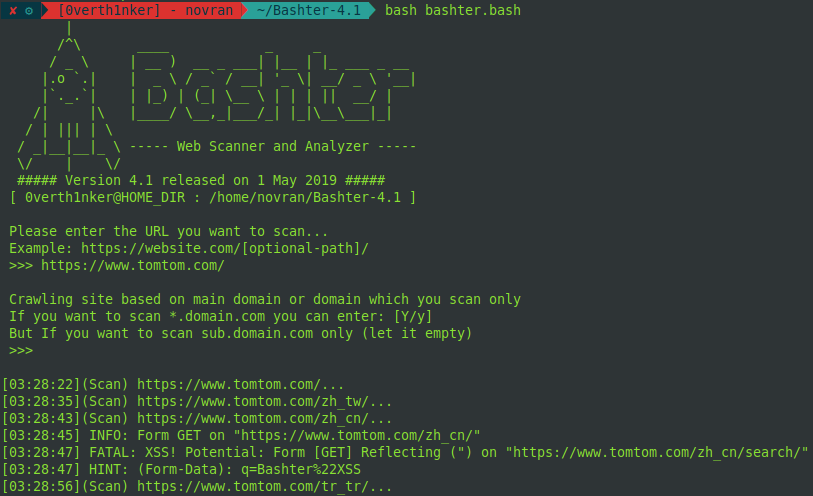 zerobyte-id/bashter
Web Vulnerability Scanner using Shell Script
 rk-000/log4j_scan_advance
A fully automated, accurate, and extensive scanner for finding log4j RCE CVE-2021-44228
 mrmahile/massscanning-cve-2025-55182
A lightweight orchestrator and worker scanner setup for running large/continuous scans across split input files. This repository contains…
 andresriancho/w3af
Open-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
 iteride/cve-2025-2294
Proof-of-concept exploit for CVE-2025-2294, a critical LFI vulnerability in Kubio AI Page Builder for WordPress. Includes a Python scanner, nuclei…
 hackmanit/web-cache-vulnerability-scanner
Go-based CLI scanner for web cache poisoning and deception. Supports 10 poisoning techniques, multiple deception methods, built-in crawler, JSON…
 spinkham/skipfish
Web application security scanner created by lcamtuf for google - Unofficial Mirror
 stamparm/dsxs
Damn Small XSS Scanner
 dinosn/cve-2026-87902-wordpress-lfi-lab
Reproduction lab + URL-list scanner + PoC for CVE-2026-87902 / GHSA-7hp8-65ch-5whp — WordPress get_page_template() unauthenticated LFI to conditional…