
barrido
 zer1t0/barrido
Tool to discover paths in web applications
fuzzinginformation-gatheringreconnaissance+2
zer1t0/barridoTool to discover paths in web applications
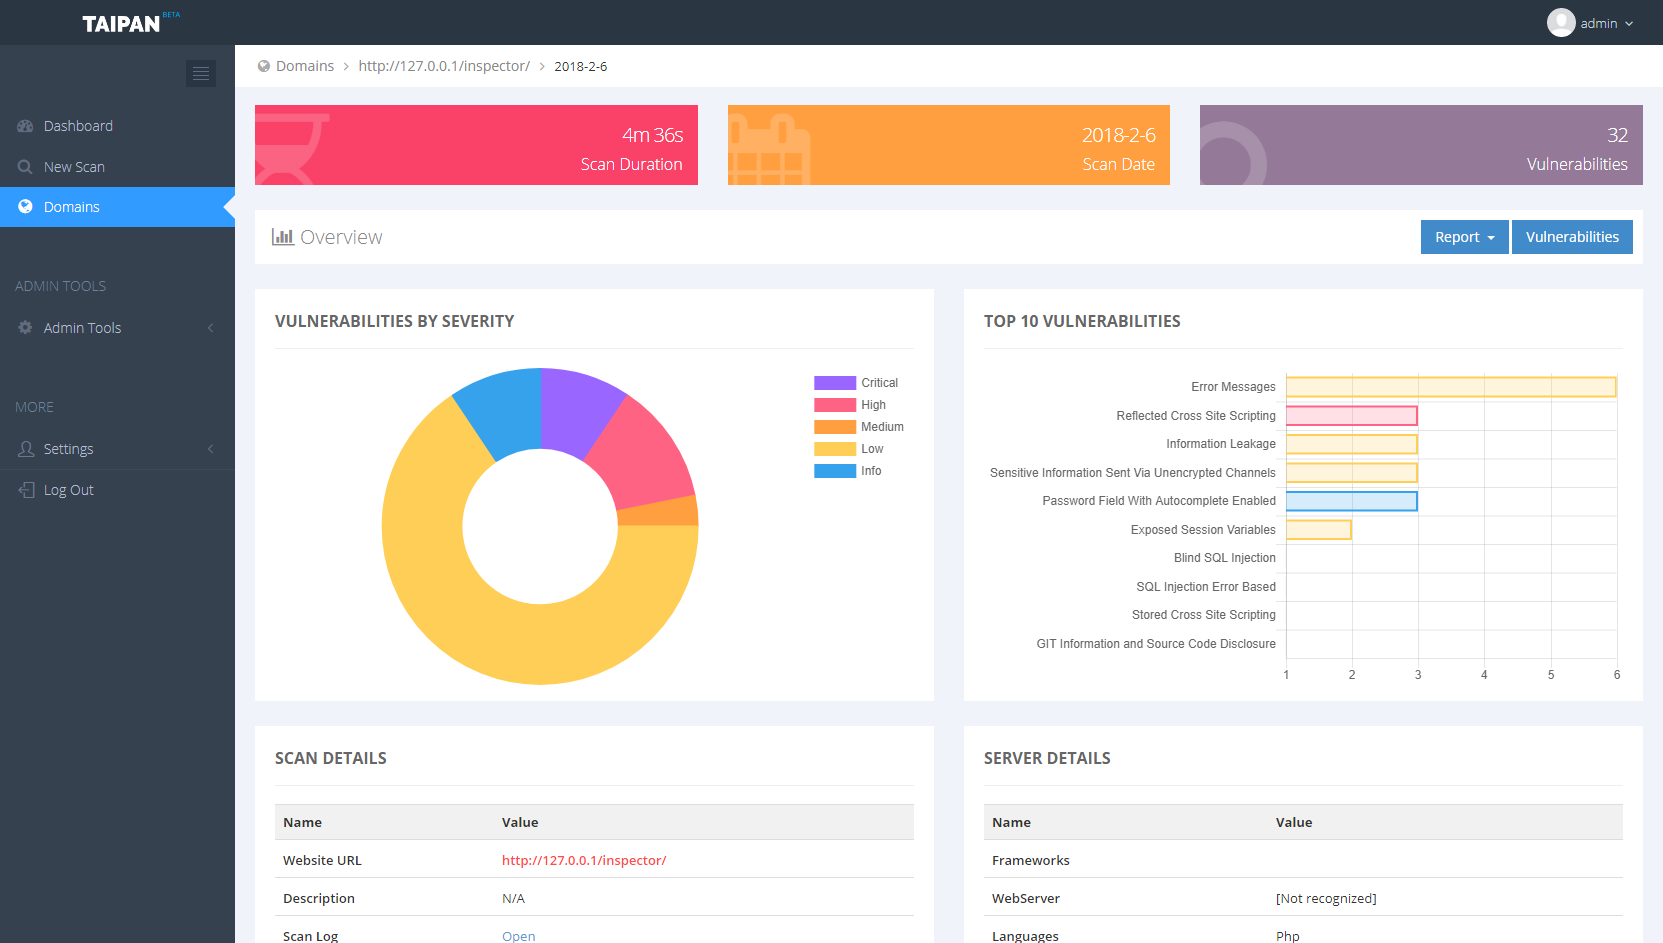
 enkomio/taipan
Web application vulnerability scanner
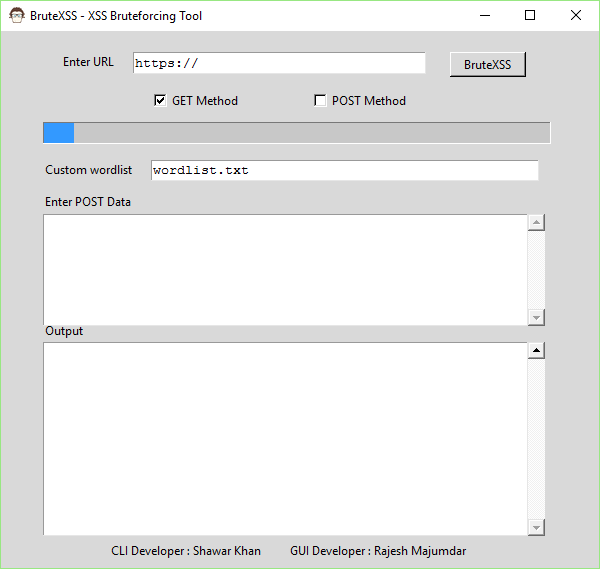 rajeshmajumdar/brutexss
BruteXSS is a tool written in python simply to find XSS vulnerabilities in web application. This tool was originally developed by Shawar Khan in CLI.…
 gotr00t0day/cve-2025-68461
A C++ security scanner tool to detect Cross-Site Scripting (XSS) vulnerabilities in Roundcube Webmail installations.
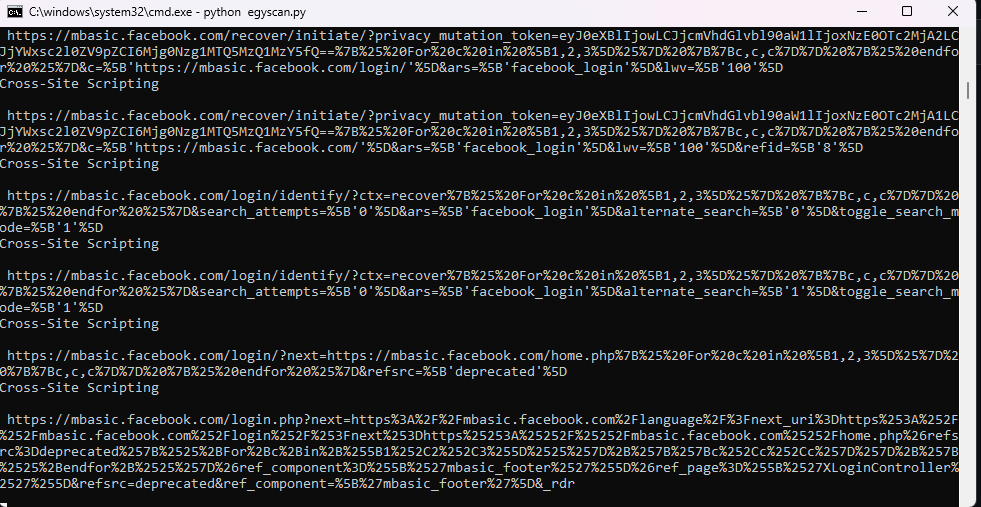 dragonked2/egyscan
Egyscan The Best web vulnerability scanner; it's a multifaceted security powerhouse designed to fortify your web applications against malicious…
 joker25000/optiva-framework
Optiva-Framework 🔎 Web Application Scanner🕵️
 0xans/cve-2024-24919
Scans web applications for CVE-2024-24919 vulnerabilities via CLI, supporting a single target or wordlist-based bulk URL scanning.
 z3usx01/cve-2025-0054
Lightweight Python scanner for detecting stored XSS (CVE-2025-0054) in SAP NetWeaver Java. Submits customizable payloads and checks for script…
 nccgroup/argumentinjectionhammer
A Burp Extension designed to identify argument injection vulnerabilities.
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 lfillaz/cve-2024-2997
The tool helps in quickly identifying vulnerabilities by examining a comprehensive list of potential paths on a website, making it useful for…
 0xuho/cve-2024-2997
The tool helps in quickly identifying vulnerabilities by examining a comprehensive list of potential paths on a website, making it useful for…
 abacus-group-rto/legion
Legion is an open source, easy-to-use, super-extensible and semi-automated network penetration testing tool that aids in discovery, reconnaissance…
 johnlodan/wp2shell-rce
WordPress CVE-2026-63030 and CVE-2026-60137 security tool for detecting exposure to the WP2Shell pre-authentication RCE chain.
 dwisiswant0/findom-xss
A fast DOM based XSS vulnerability scanner with simplicity.
 ethicalhackingplayground/bxss
Blind XSS Scanner is a tool that can be used to scan for blind XSS vulnerabilities in web applications.
 ev3rpalestine/0xmiddleware
CVE-2025-29927: Next.js Middleware Exploit
 boreas37/cve-2026-64638-poc-xss2shell-
XSS2Shell (CVE-2026-64638) WordPress pre-auth XSS to RCE chain — PoC exploit + defensive audit tool + nuclei template