
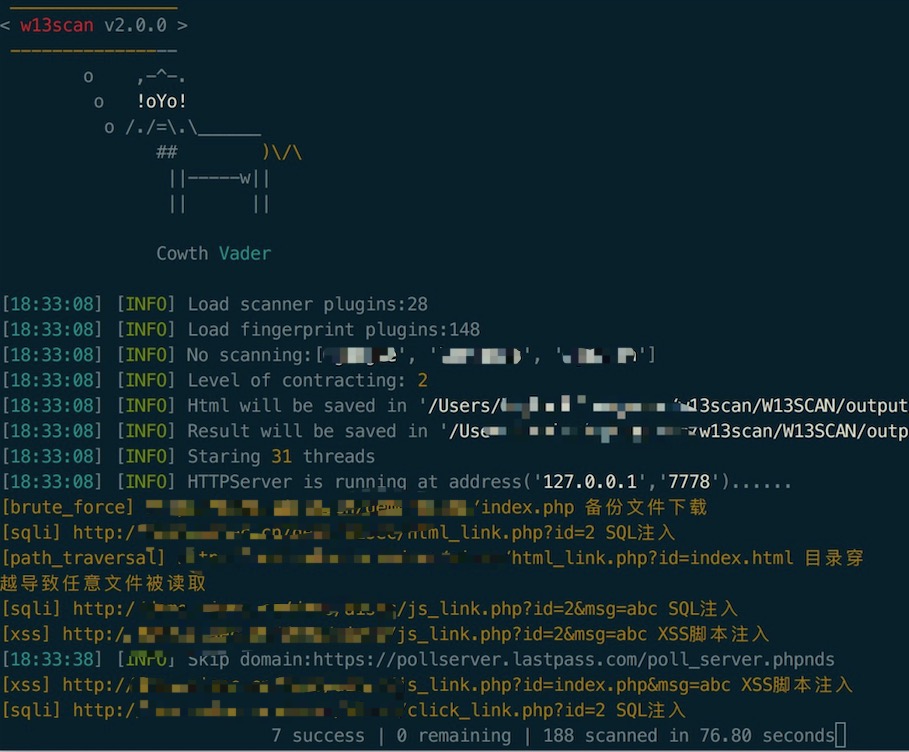
w13scan
 w-digital-scanner/w13scan
Passive and active web vulnerability scanner with plugin-based detection for XSS, SQL injection, command injection, and sensitive file disclosure.…
penetration-testingvulnerability-scannersweb-security+1
1.9k
w-digital-scanner/w13scanPassive and active web vulnerability scanner with plugin-based detection for XSS, SQL injection, command injection, and sensitive file disclosure.…
 strobelpierre/cve-2026-9082
Semi-passive scanner that detects Drupal installations vulnerable to CVE-2026-9082 (PostgreSQL SQL injection) via fingerprinting, version detection,…
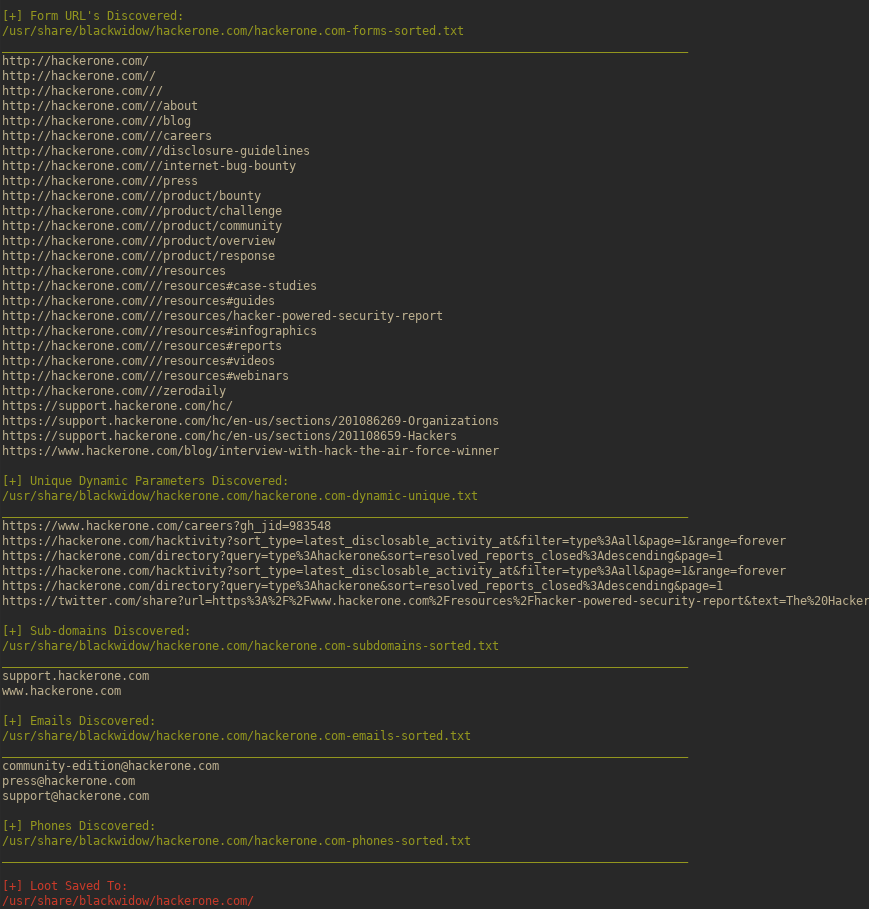 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
 jenderal92/livewire-vuln-scanner
Simple scanner to detect vulnerable Livewire installations.
 vighnesh91/securiscan
Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…
 bugcrowd/hunt
Flags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…
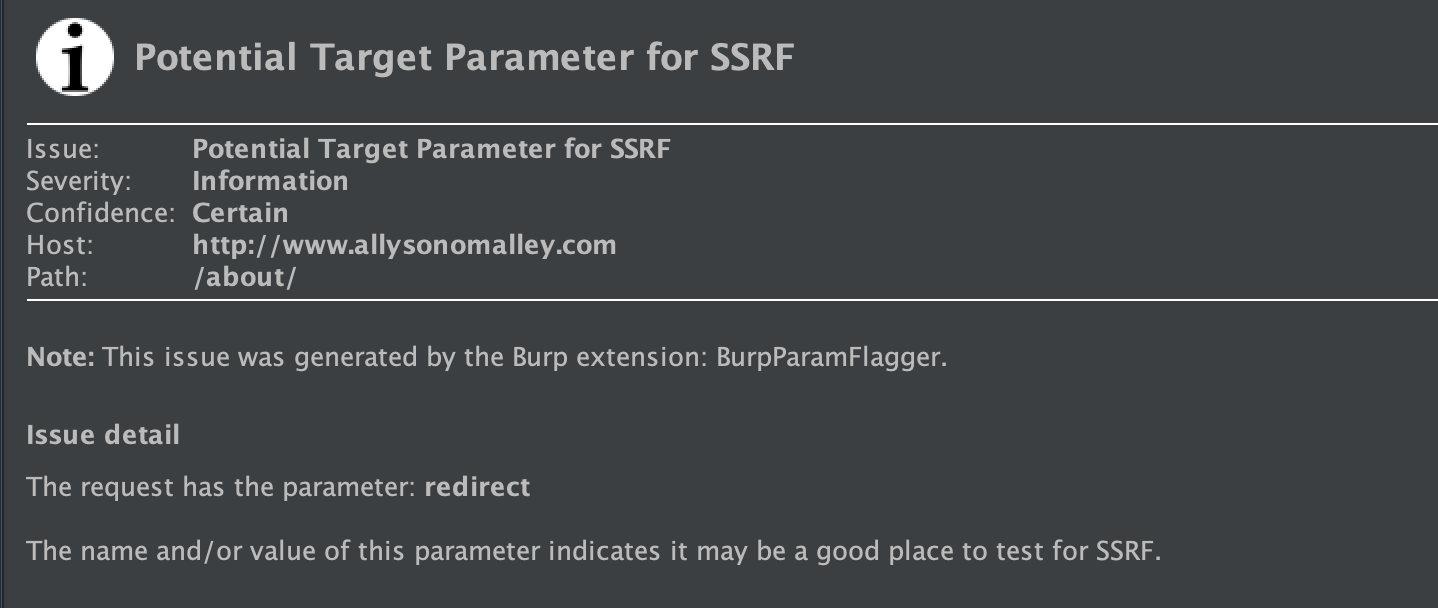 allyomalley/burpparamflagger
A Burp extension adding a passive scan check to flag parameters whose name or value may indicate a possible insertion point for SSRF or LFI.
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 rxerium/cve-2025-58360
Passive detection for CVE-2025-58360
 portswigger/active-scan-plus-plus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…