


 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 oscerd/cve-2026-85315
Runnable proof-of-concept reproducer for CVE-2026-85315, demonstrating camel-grpc consumer exception message disclosure (CWE-209) in Camel Spring…
 valtersit/wordpress-cve-scanner
Scan your WordPress core, themes and plugins for known CVEs from the command line. Open source, auditable, privacy-first — powered by the ValtersIT…

 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 t0xodile/crlf-powered-desync-scanner
Burp extension scanner for CRLF injection and HTTP desync attacks, using mutated probes, WAF false-positive checks, and optional…
 cyber-note/cve-2026-34835-black-box-analysis
A black-box (DAST) security analysis of CVE-2026-34835 focusing on external validation methodology, observable behavior, security impact, and…
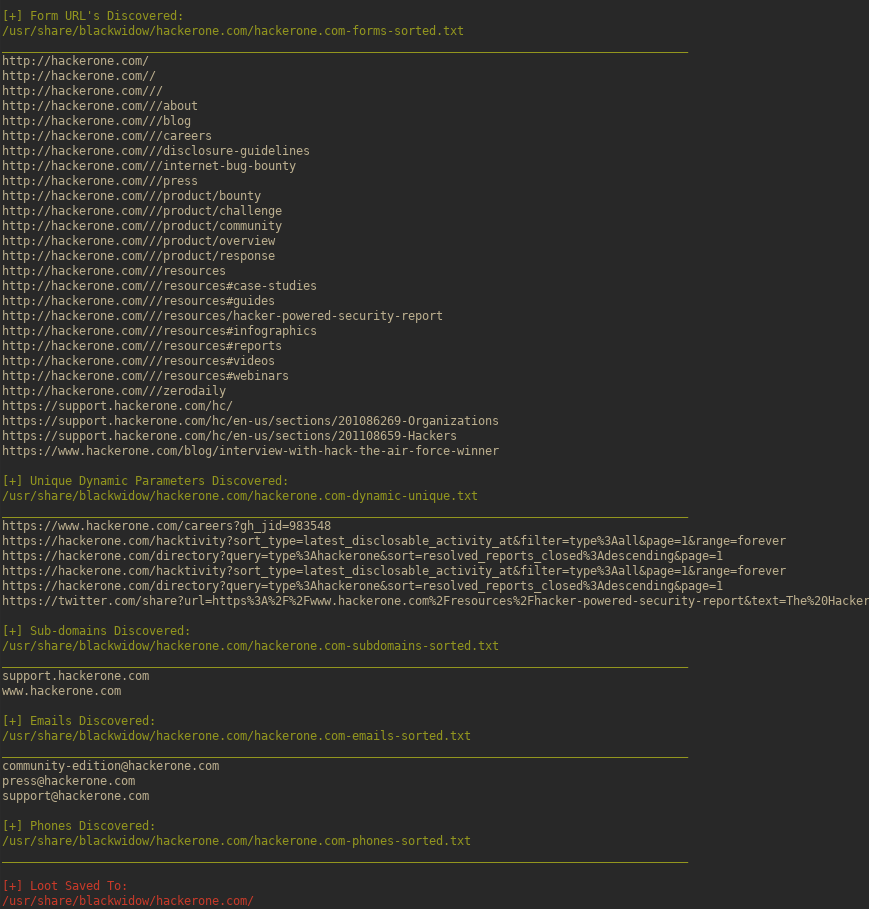 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
 erev0s/vampi
Vulnerable REST API with OWASP top 10 vulnerabilities for security testing
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
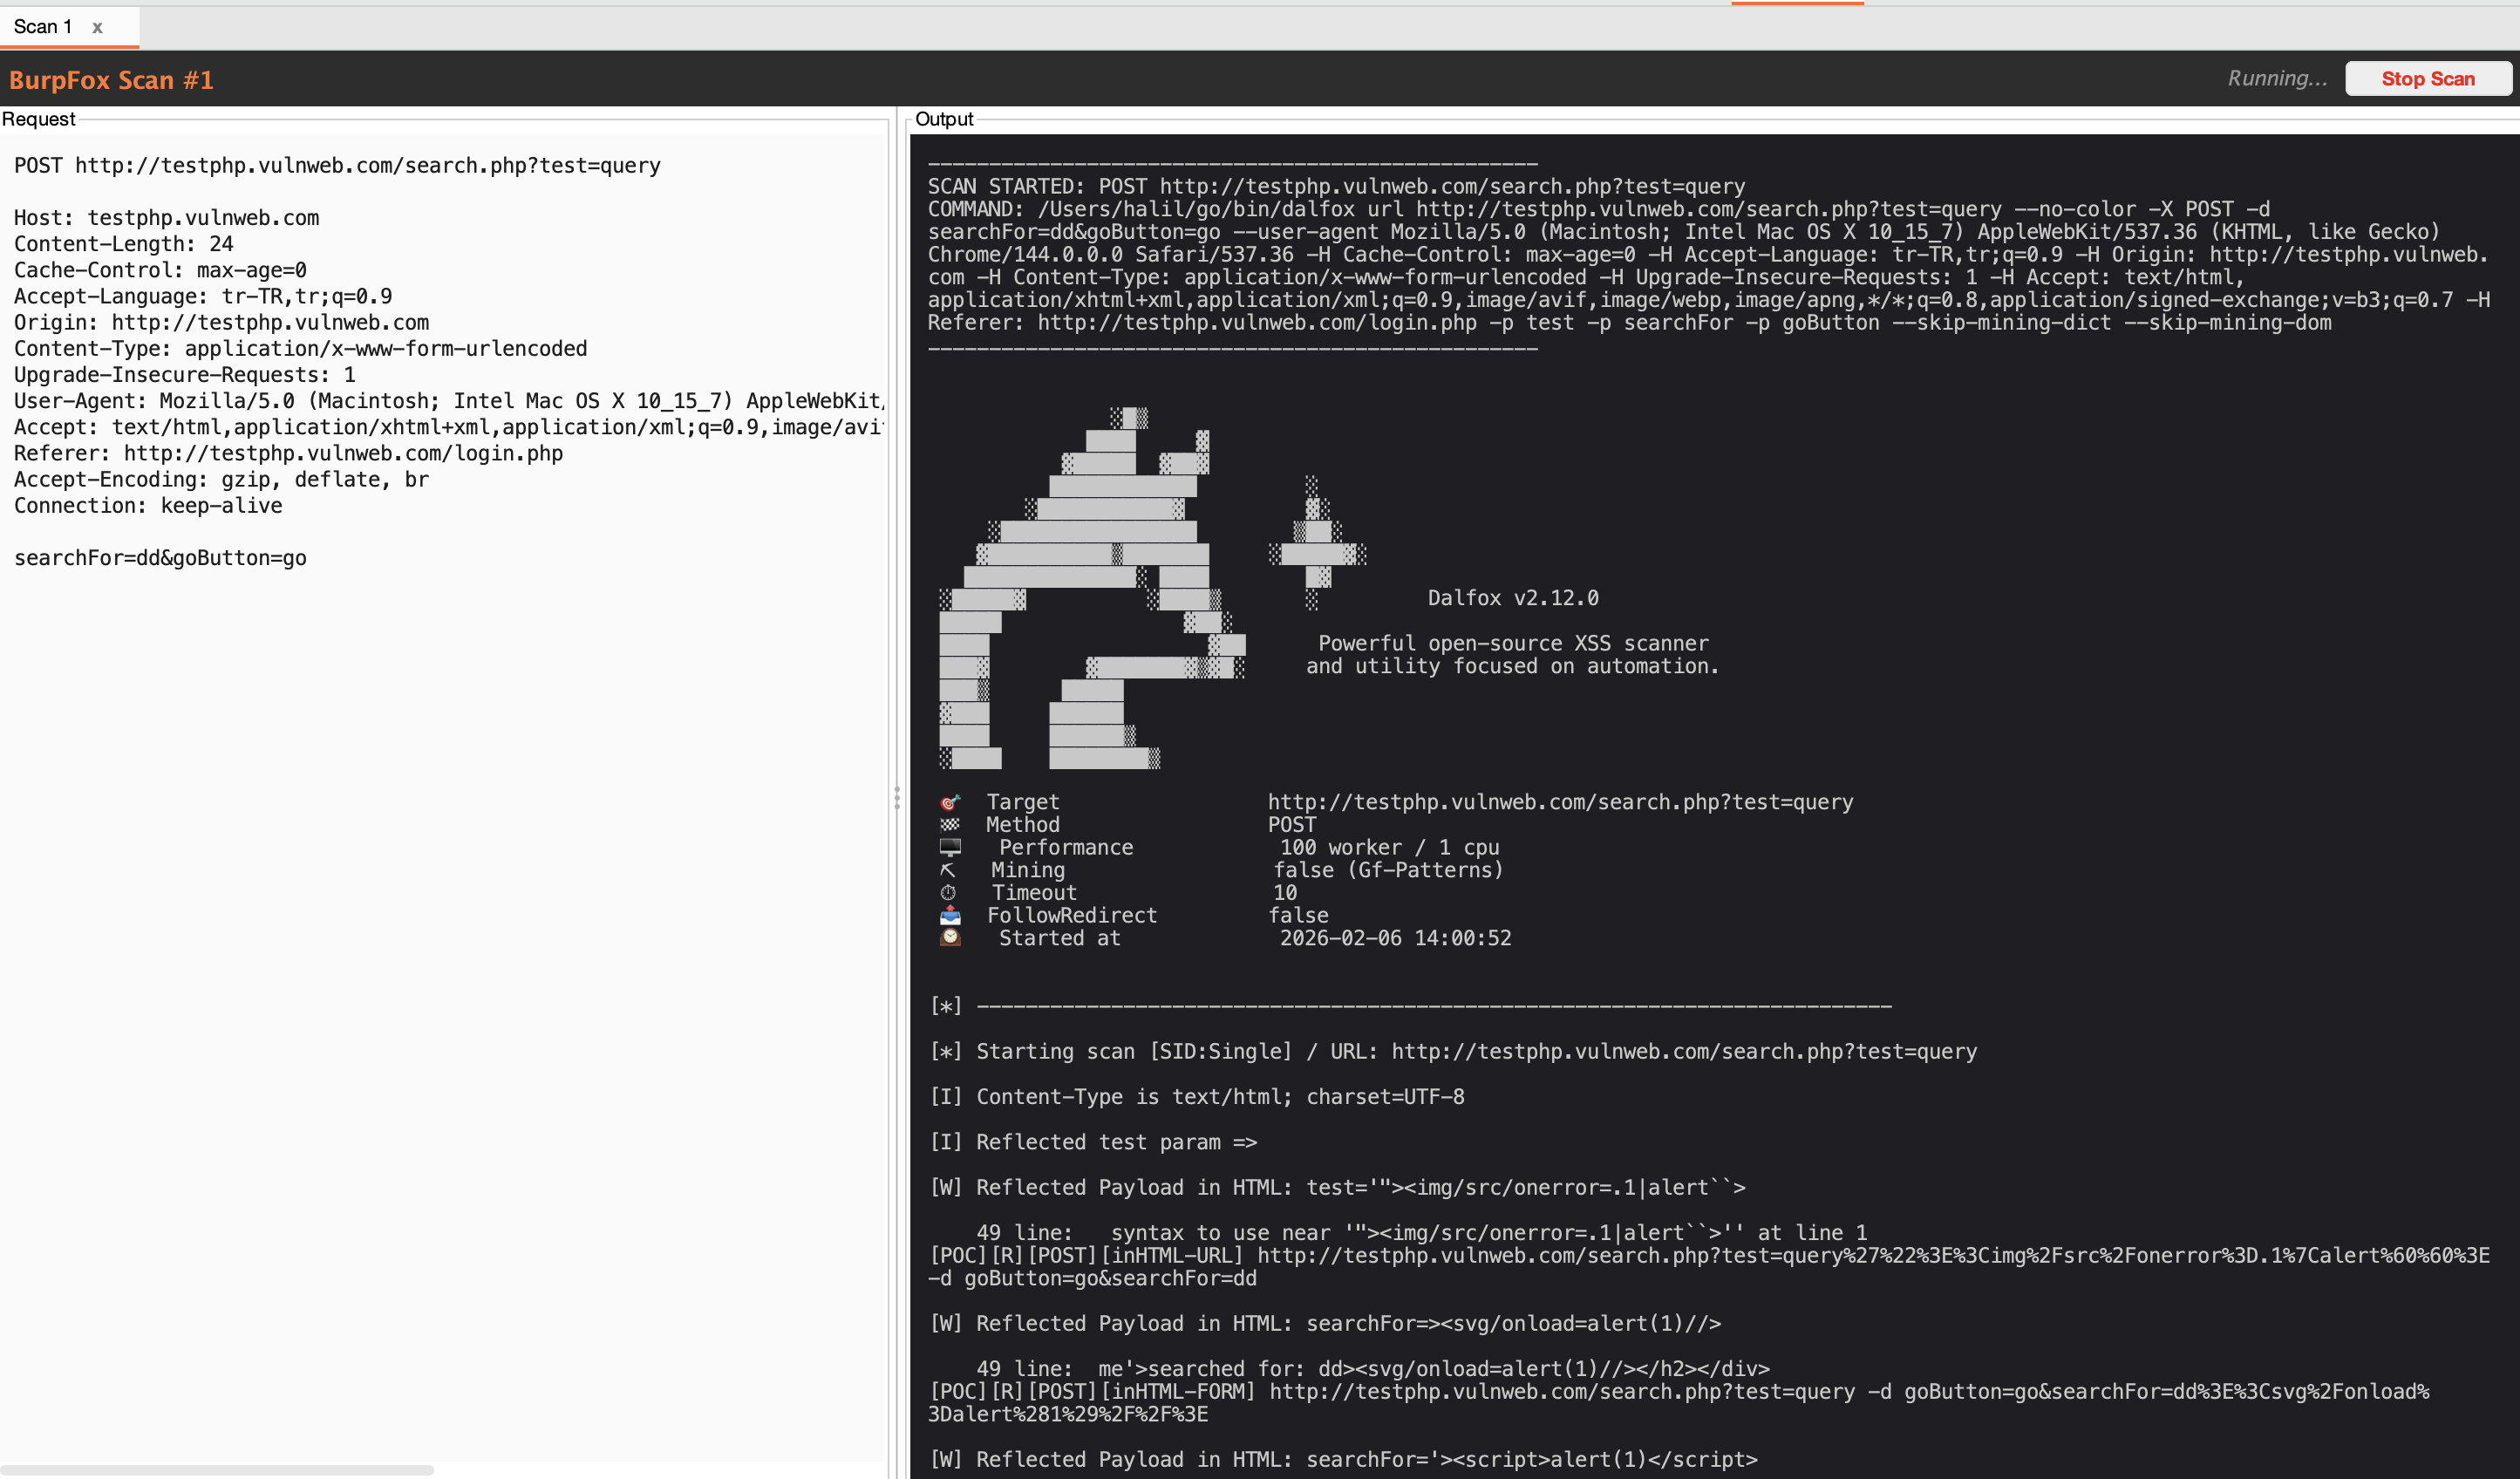 halilkirazkaya/burpfox
A Burp Suite extension that integrates Dalfox XSS scanner directly into your workflow.
 rxerium/n8n-vulnerability-detection
Vulnerability detection scripts for the n8n product.
 gotr00t0day/cve-2025-68461
A C++ security scanner tool to detect Cross-Site Scripting (XSS) vulnerabilities in Roundcube Webmail installations.
 rxerium/cve-2025-68613
Detection for CVE-2025-68613
 rxerium/cve-2025-37164
Detection for CVE-2025-37164
 rxerium/cve-2025-58360
Passive detection for CVE-2025-58360
 rxerium/cve-2025-8110
Detection template for CVE-2025-8110