wordpress-cve-scanner

Scan your WordPress core, themes and plugins for known CVEs from the command line. Open source, auditable, privacy-first — powered by the ValtersIT…

Scan your WordPress core, themes and plugins for known CVEs from the command line. Open source, auditable, privacy-first — powered by the ValtersIT…

Shell PoC for CVE-2026-87915, an unauthenticated stored XSS in the Popup Maker WordPress plugin (<=1.24.0). Fingerprints the plugin and demonstrates…

Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…

CVE-2026-87902 detector. WordPress get_page_template LFI class. Detect-only. Authorized lab.

Reproduction lab + URL-list scanner + PoC for CVE-2026-87902 / GHSA-7hp8-65ch-5whp — WordPress get_page_template() unauthenticated LFI to conditional…

RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…

Laboratório de pentest em rede isolada: enumeração com nmap/nikto e exploração manual do Metasploitable2 (backdoor vsFTPd CVE-2011-2523, bindshell)…

PHP CLI script that scans single hosts or IP ranges to detect Exchange servers vulnerable to CVE-2020-0688 by checking installed cumulative updates.

Nuclei template and detection queries for CVE-2024-27954, a path traversal and SSRF vulnerability in the WP Automatic WordPress plugin up to version…

Python scanner that passively fingerprints exposed BeyondTrust Remote Support and Privileged Remote Access services to detect potential CVE-2026-1731…

Web vulnerability scanner built with C++17 and Qt 6, featuring a GUI, CLI, configurable crawling, and JSON reports. Reconstructed for educational…

Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…

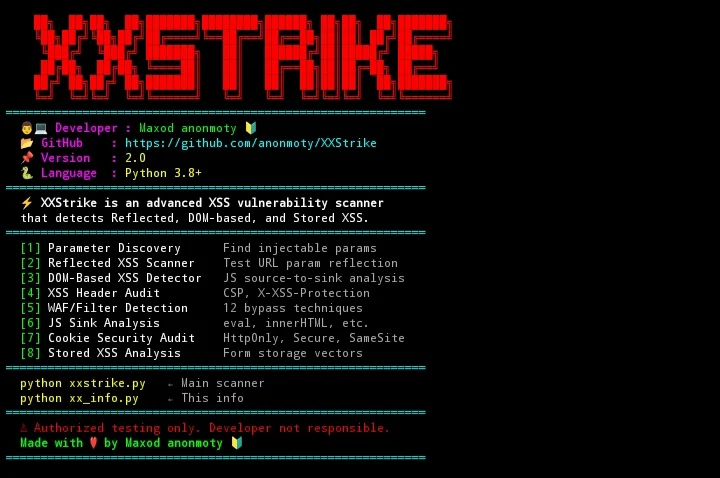
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.

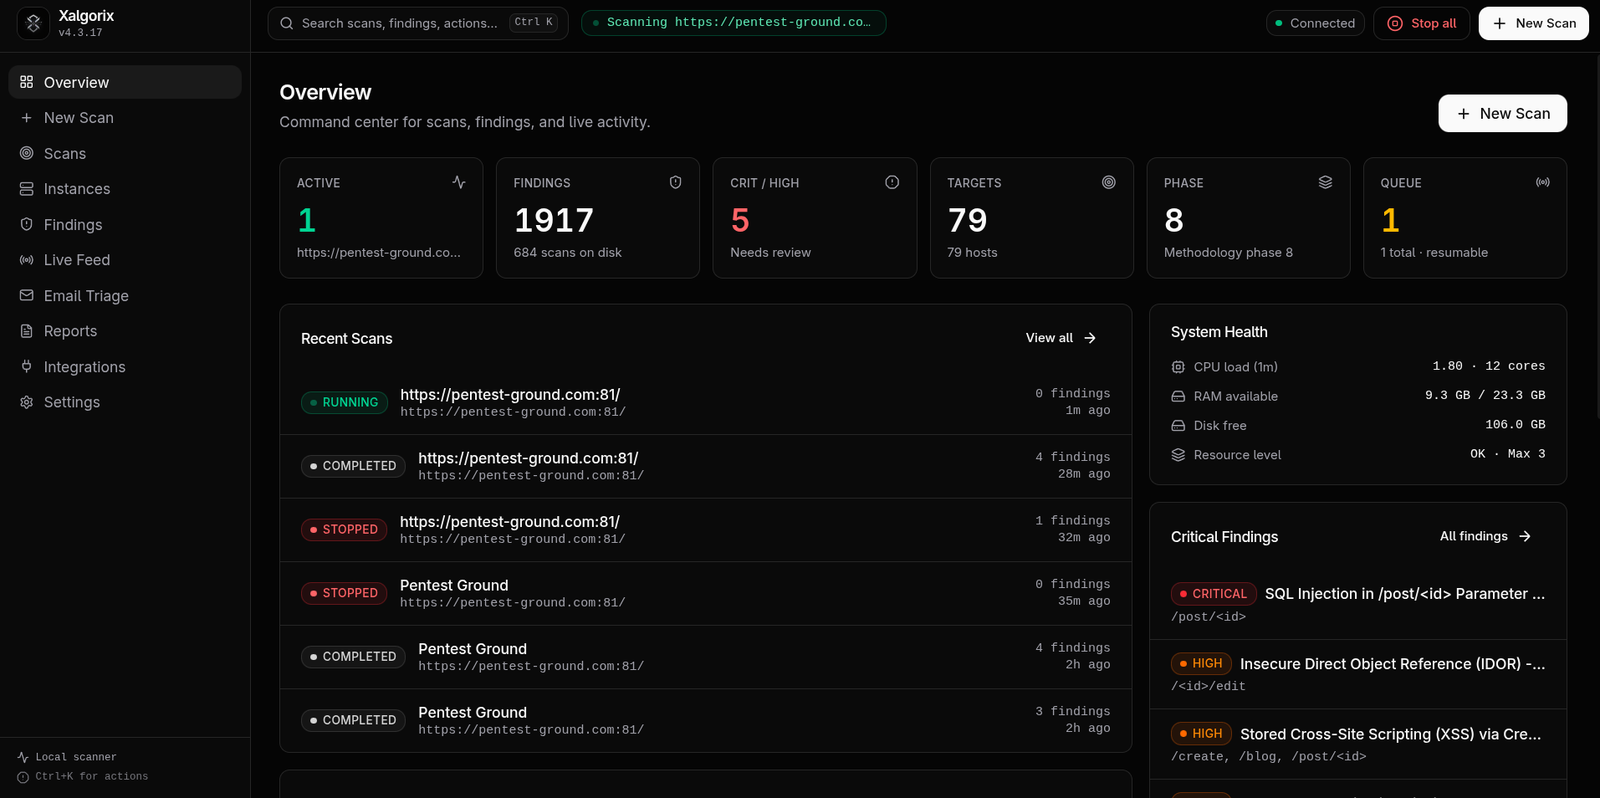
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…

Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.

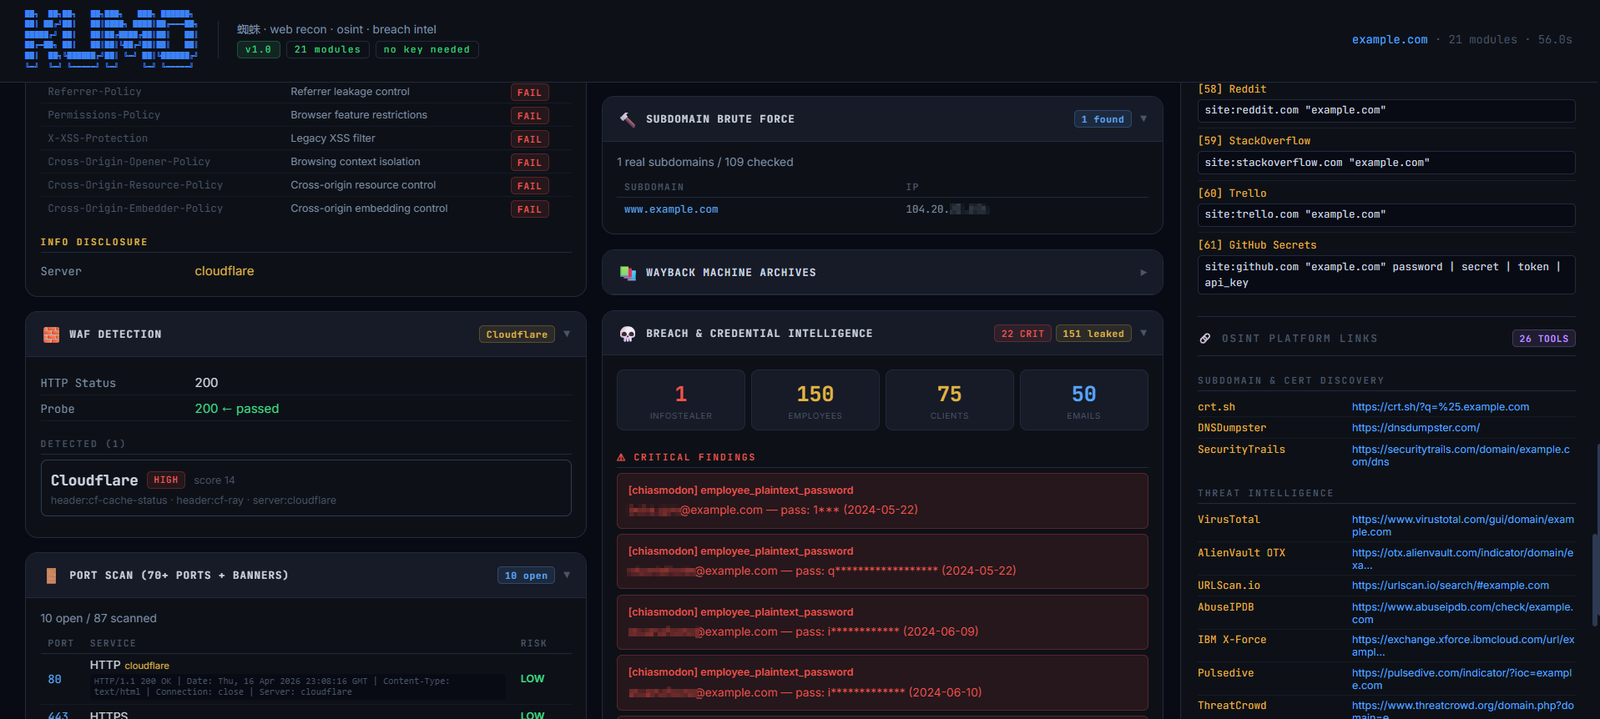
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…

Read-only Python checker that validates CVE-2026-20079 Cisco FMC authentication-bypass behavior by comparing unauthenticated and csm_processes…

Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…