
mcp-idprobe
 hahahahahahahahah6/mcp-idprobe
Runtime probe for MCP cross-tenant response leaking via JSON-RPC id collision (CVE-2026-111770)
api-securityapi-security-testingcode-analysis+6
hahahahahahahahah6/mcp-idprobeRuntime probe for MCP cross-tenant response leaking via JSON-RPC id collision (CVE-2026-111770)
 foxcornlab/mlflow-scorer-scanner
Detection-only triage scanner for MLflow scorer RCE CVE-2026-116692: version check via the /version endpoint. No payloads, no scorer invocation.
 tc4dy/cve-2026-119977-toolkit
Red/blue team toolkit for CVE-2026-119977 WordPress core upgrade-window RCE: version triage, WAF origin discovery, race oracle, staged wp-config…
 gmh5225/sqlmap-gui
基于SQLMap的现代化图形用户界面,提供直观易用的SQL注入检测和利用功能。本GUI版本在保持SQLMap强大功能的同时,为用户提供了友好的可视化操作界面。
 im0xfay/cve-2026-126173
PoC, Docker lab, and root-cause analysis for CVE-2026-126173: unauthenticated arbitrary password reset in AutomatorWP Pro Webhooks <= 1.4.4 leading…
 sadaqaty/cve-2026-1296
Python 3 PoC and detection tool for CVE-2026-1296, an unauthenticated open redirect in the WordPress Frontend Post Submission Manager Lite plugin (<=…
 zahidec0de/cve-2026-12345-poc
Proof of Concept (PoC) for CVE-2026-64638, a reflected XSS in WordPress Core < 7.0.3.
 msmacu/smartpwn
Rust-based vulnerability scanner and exploit tool targeting SmarterMail CVE-2026-23760 — for educational/defensive research only

 kavin-jain/verified-pentest
Self-service pentest platform that only scans domains whose ownership is proven, and re-checks that proof at scan time. OWASP, TLS, DNS and port…
 r4nd0mth1ngs/brainproxy
Fast, AI-first web security testing toolkit in Rust: an open-source alternative to ZAP, Burp Suite and the like. Intercepting proxy, scanner, fuzzer…
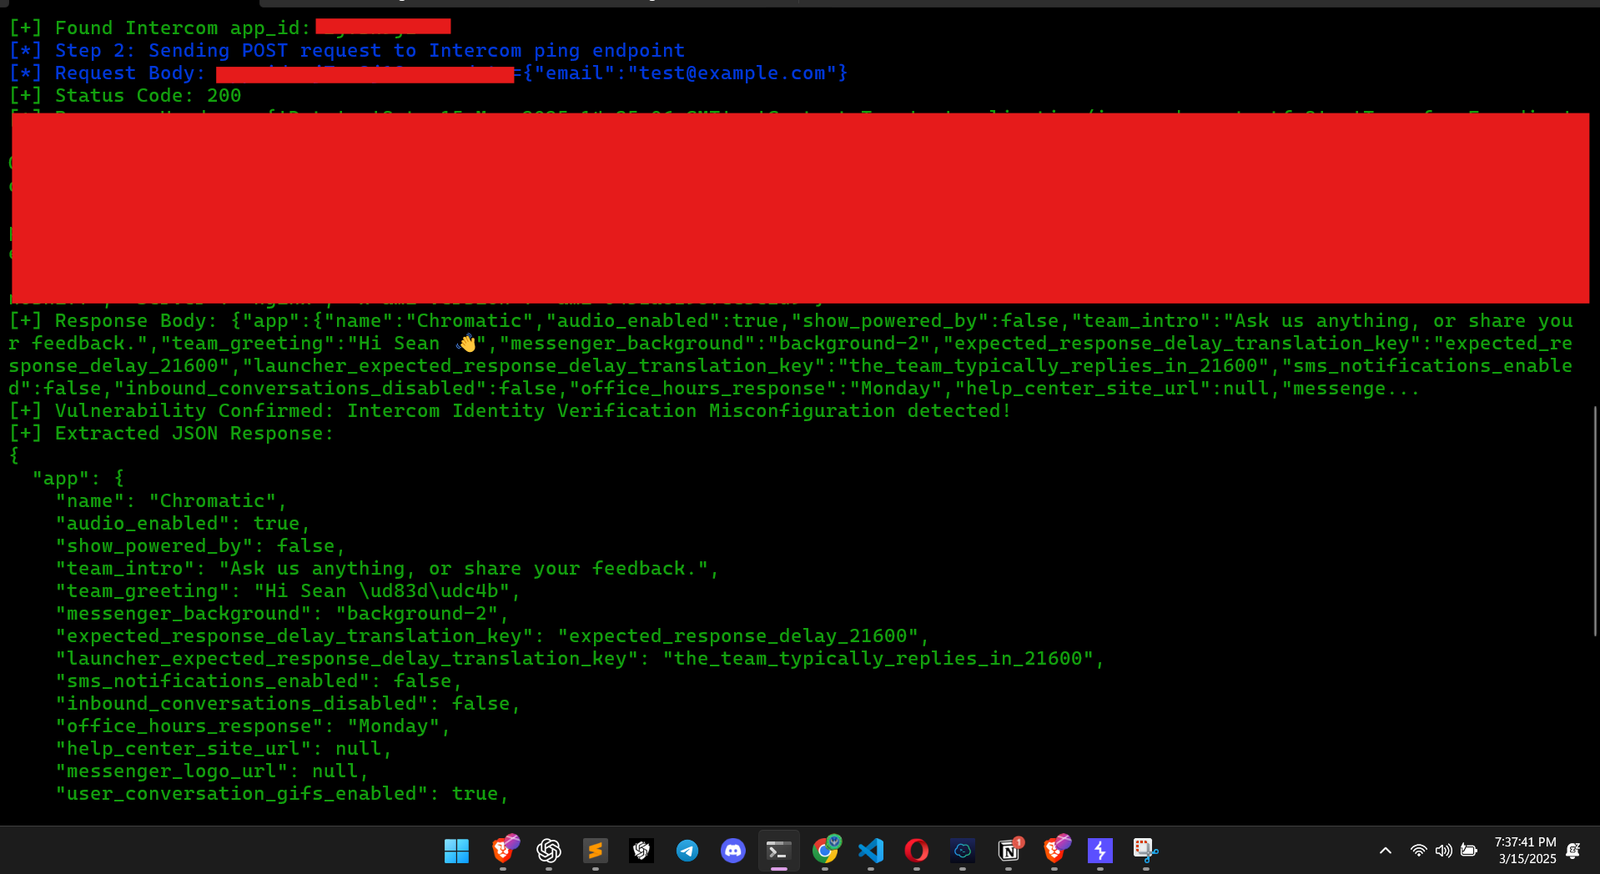 muhammadwaseem29/intercom-exploit
Identity Verification is not setup on the Intercom widget, allowing an attacker to impersonate a user and access their chat history. reference:
 piratesshield/arise-xti
AI-driven external attack surface management pipeline: 28 modules for recon, subdomain/DNS enumeration, web/API/cloud vulnerability scanning, OSINT…
 bugtraceai/bugtraceai
Open-source, self-hosted web pentesting suite with agentic scanning, analyst tools, API testing, model checkpoints and MCP integrations.
 x0xr00t/sl0ppy-riftscan-cve-2026-42945
Metasploit auxiliary scanner that passively fingerprints NGINX Server headers and flags versions within the CVE-2026-42945 affected range without…
 davidvrns/cve-2026-5430-wso2
Detection PoC for CVE-2026-5430 — unauthenticated JWT algorithm bypass (CVSS 10.0) affecting WSO2 API Manager 4.1.0–4.6.0. Read-only assessment tool…
 0xiide231/wp2shell2026
wp2shell - WordPress CVE-2026-63030 Exploit & Scanner well forked
 murrez/cve-2026-76570
Python PoC for CVE-2026-76570: unauthenticated SQL injection in Joomla JCTables (com_jctables) front-end JSON API, with check, exploit and mass-scan…
 murrez/cve-2026-85520
Python PoC for CVE-2026-85520: detects and exploits unauthenticated arbitrary file write in PrestaShop gmfeed feed.php to achieve RCE, with bulk…