
CVE-2026-18143
 wayang1337/cve-2026-18143
Request a Quote for WooCommerce (Addify) <= 2.9.2 Unauthenticated arbitrary file upload via afrfq_submit_quote_via_popup
exploitationvulnerability-analysisweb-application-exploitation+2
wayang1337/cve-2026-18143Request a Quote for WooCommerce (Addify) <= 2.9.2 Unauthenticated arbitrary file upload via afrfq_submit_quote_via_popup
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 pwnvader/cve-2026-87915-poc-pwnvader
Shell PoC for CVE-2026-87915, an unauthenticated stored XSS in the Popup Maker WordPress plugin (<=1.24.0). Fingerprints the plugin and demonstrates…
 babydessy/cve-2024-27954
Nuclei template and detection queries for CVE-2024-27954, a path traversal and SSRF vulnerability in the WP Automatic WordPress plugin up to version…
 fauxrougee/smartscanner-source
Web vulnerability scanner built with C++17 and Qt 6, featuring a GUI, CLI, configurable crawling, and JSON reports. Reconstructed for educational…
 squ1shification/grafana-plugin-enumerator-cve-2021-43798
Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…
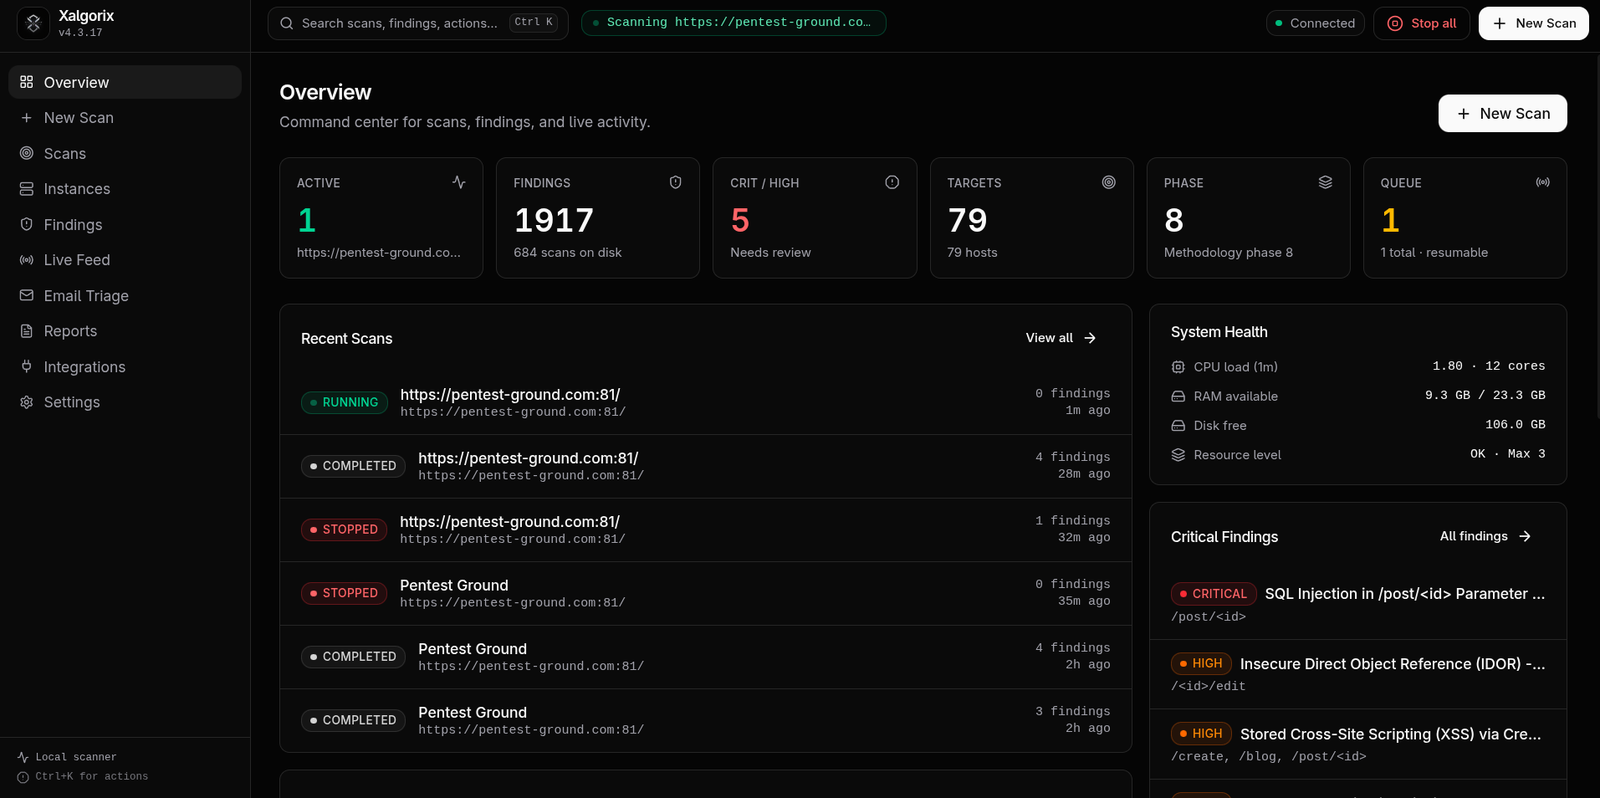 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 diegoarias008/cve-2026-20079-checker
Read-only Python checker that validates CVE-2026-20079 Cisco FMC authentication-bypass behavior by comparing unauthenticated and csm_processes…
 talha1112/fyp
Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
 testardou/cve-2026-65540
Popup for CF7 with Sweet Alert <= 1.6.5 - Cross-Site Request Forgery
 rabbitmask/weblogicscan
Automated vulnerability scanner for Oracle WebLogic Server, detecting historical CVEs including deserialization, SSRF, and arbitrary file upload with…
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 burjoy/cve-2024-40275_scanner
Scanner for CVE-2024-40725 Apache HTTP Server source-code disclosure; probes direct and subrequest paths, fingerprints affected versions, and outputs…
 graysignal/cve-2024-38856-apacheofbiz
Exploit for CVE-2024-38856 affecting Apache OFBiz versions before 18.12.15
 yora1928/cve-2026-15748
Scans WordPress Forminator for CVE-2026-15748 unauthenticated RCE. Detects vulnerable sites, crawls forms, extracts nonces, runs safe upload tests.
 nxploited/cve-2026-18366
Events Manager < 7.4.1 - Unauthenticated Privilege Escalation to Administrator
 nullwhisper/cve-2026-56292-acymailing-sqli
CVE-2026-56292 - AcyMailing for Joomla unauthenticated SQL injection scanner
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.