CVE-2024-40275_Scanner

Scanner for CVE-2024-40725 Apache HTTP Server source-code disclosure; probes direct and subrequest paths, fingerprints affected versions, and outputs…

Scanner for CVE-2024-40725 Apache HTTP Server source-code disclosure; probes direct and subrequest paths, fingerprints affected versions, and outputs…

Nuclei detection template for CVE-2026-41473, an unauthenticated read/write API access flaw in CyberPanel AI Scanner before 2.4.4. Uses two HTTP…

Burp extension scanner for CRLF injection and HTTP desync attacks, using mutated probes, WAF false-positive checks, and optional…

Rust-powered HTTP Request Smuggling Scanner.

Safe PowerShell validator for PHP CVE-2026-17543 exposure via HTTP headers and non-destructive login-form probes.

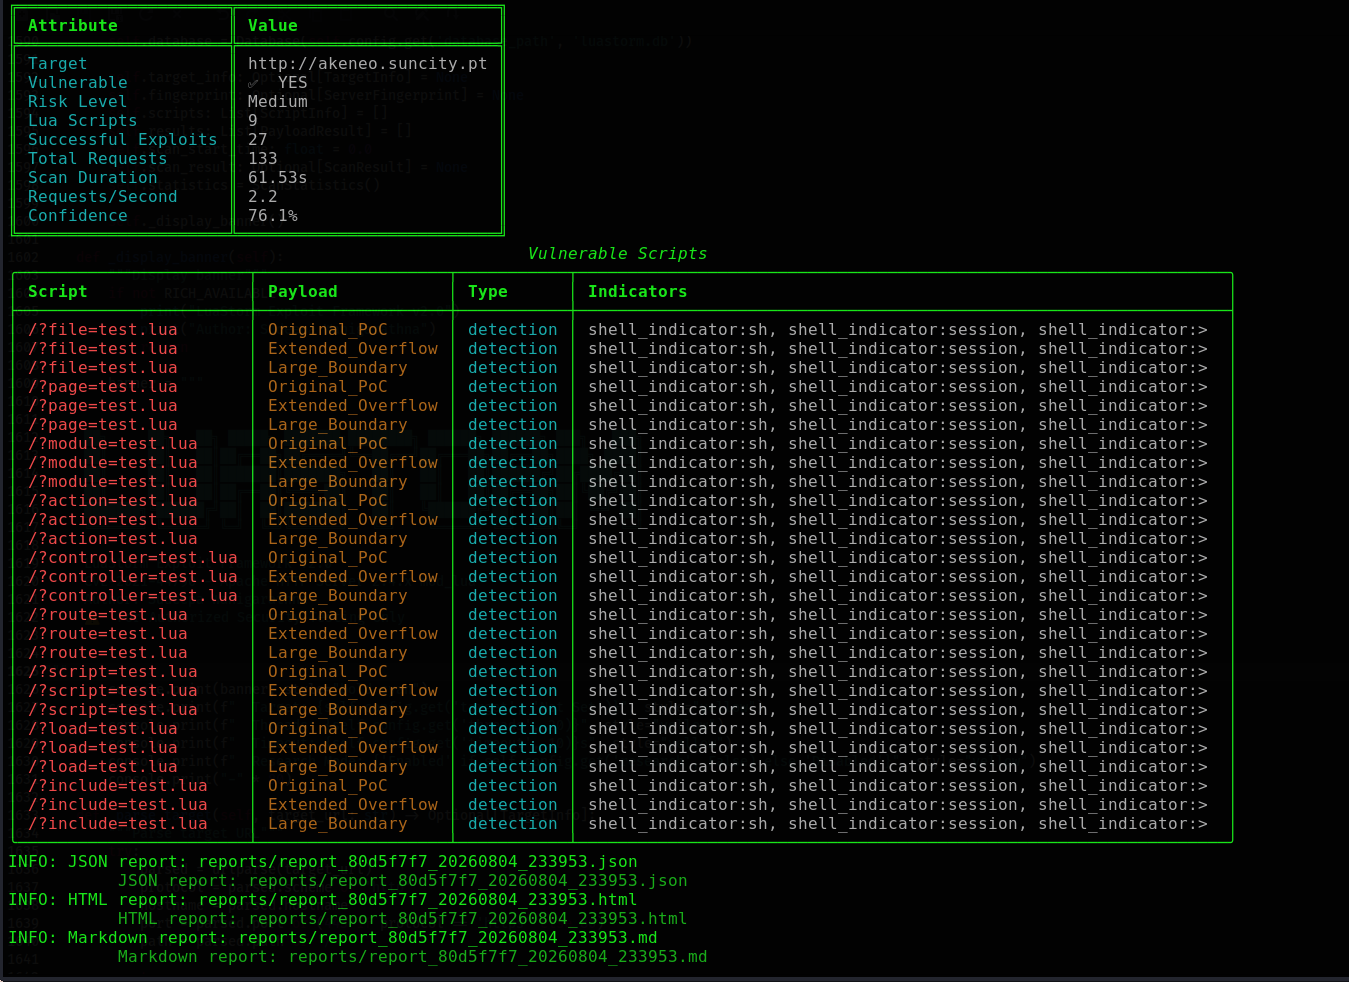
Apache HTTP Server 2.4.x mod_lua Buffer Overflow (CVE-2021-44790) - Advanced exploitation framework with fingerprinting, multi-stage scanning, plugin…

Proof-of-concept scanner for the Optionsbleed vulnerability (CVE-2017-9798) that tests Apache HTTP servers for memory leak via HTTP OPTIONS method.

CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…

Detects Apache HTTP Server path traversal vulnerabilities (CVE-2021-41773, CVE-2021-42013) by checking for exposure of /etc/passwd through…

A script that checks for vulnerable Log4j (CVE-2021-44228) systems using injection of the payload in common HTTP headers.

Detection for CVE-2024-57378

Apache HTTP Server Vulnerability Testing Tool | PoC for CVE-2024-38472 , CVE-2024-39573 , CVE-2024-38477 , CVE-2024-38476 , CVE-2024-38475 ,…

Nuclei template for detecting CVE-2024-28995, a directory traversal vulnerability in Serv-U FTP server, enabling file read via crafted HTTP requests.

Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…

Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…

Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…

CPH:SEC WAES: Web Auto Enum & Scanner - Auto enums website(s) and dumps files as result

Http request smuggling vulnerability scanner