

w3af
 andresriancho/w3af
Open-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
exploitationpenetration-testingvulnerability-scanners+3
4.9k
andresriancho/w3afOpen-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…

 projectdiscovery/katana
A next-generation crawling and spidering framework.
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 jaeles-project/jaeles
The Swiss Army knife for automated Web Application Testing
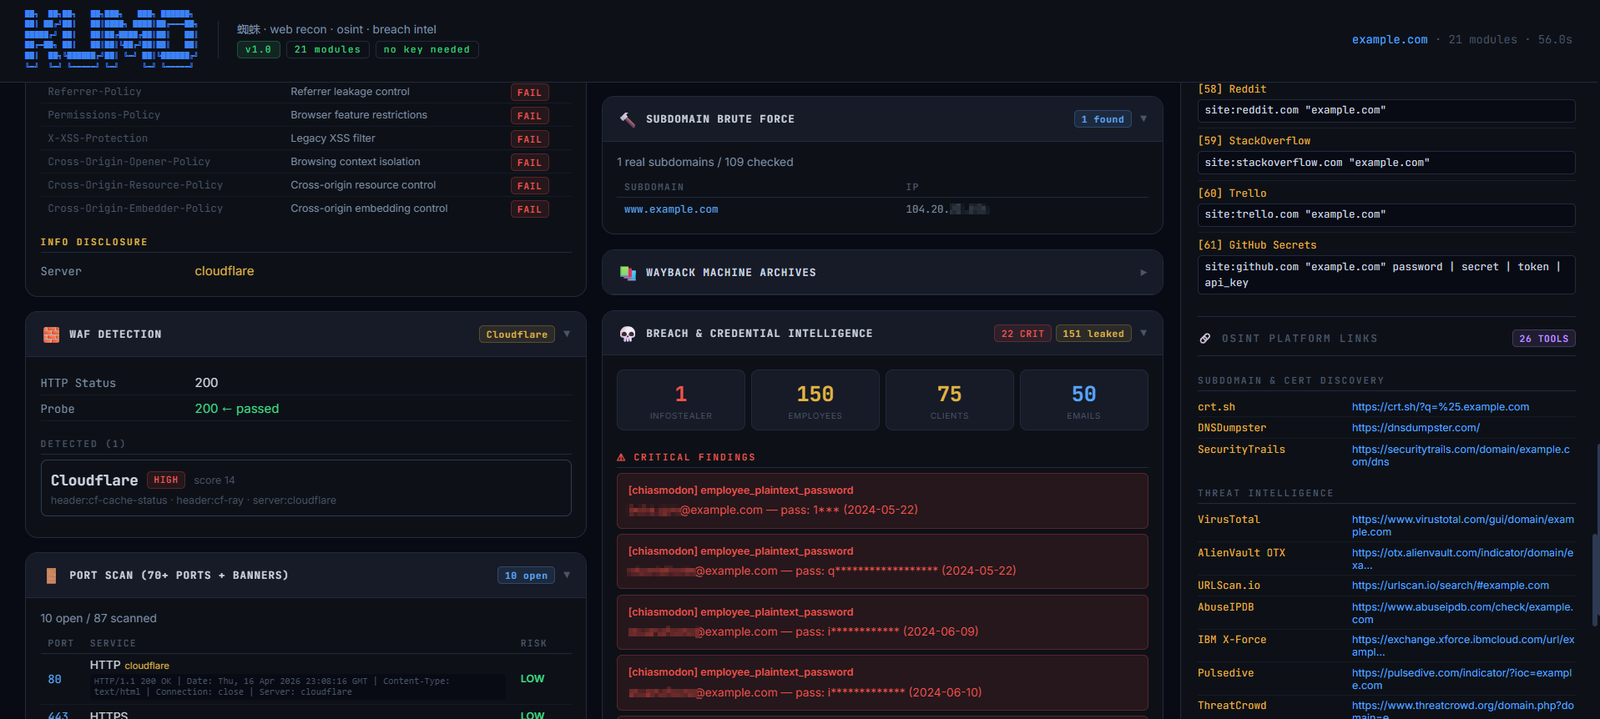 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 1n3/sn1per
Automated penetration testing & attack surface management platform. Recon, scan, exploit, report — 600+ exploits, 90+ integrations, 10K+ detections.
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 projectdiscovery/nuclei-templates
Community curated list of templates for the nuclei engine to find security vulnerabilities.
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 hackmanit/web-cache-vulnerability-scanner
Go-based CLI scanner for web cache poisoning and deception. Supports 10 poisoning techniques, multiple deception methods, built-in crawler, JSON…
 urbanadventurer/whatweb
Next generation web scanner
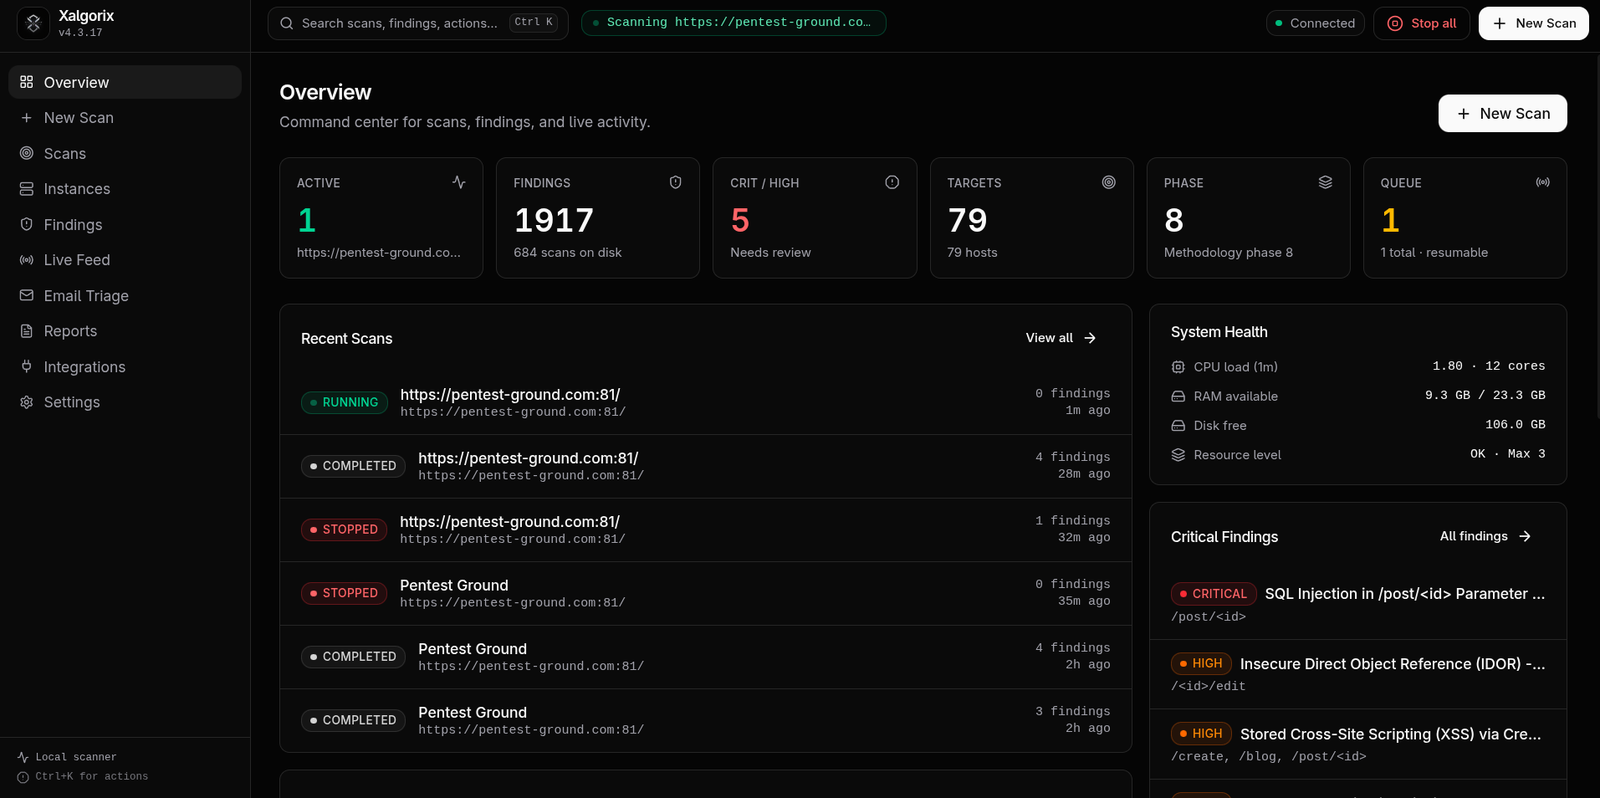 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.

 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…