

bugbounty-lab101
 devcop95/bugbounty-lab101
A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…
api-security-testingeducationinformation-gathering+8
486
devcop95/bugbounty-lab101A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
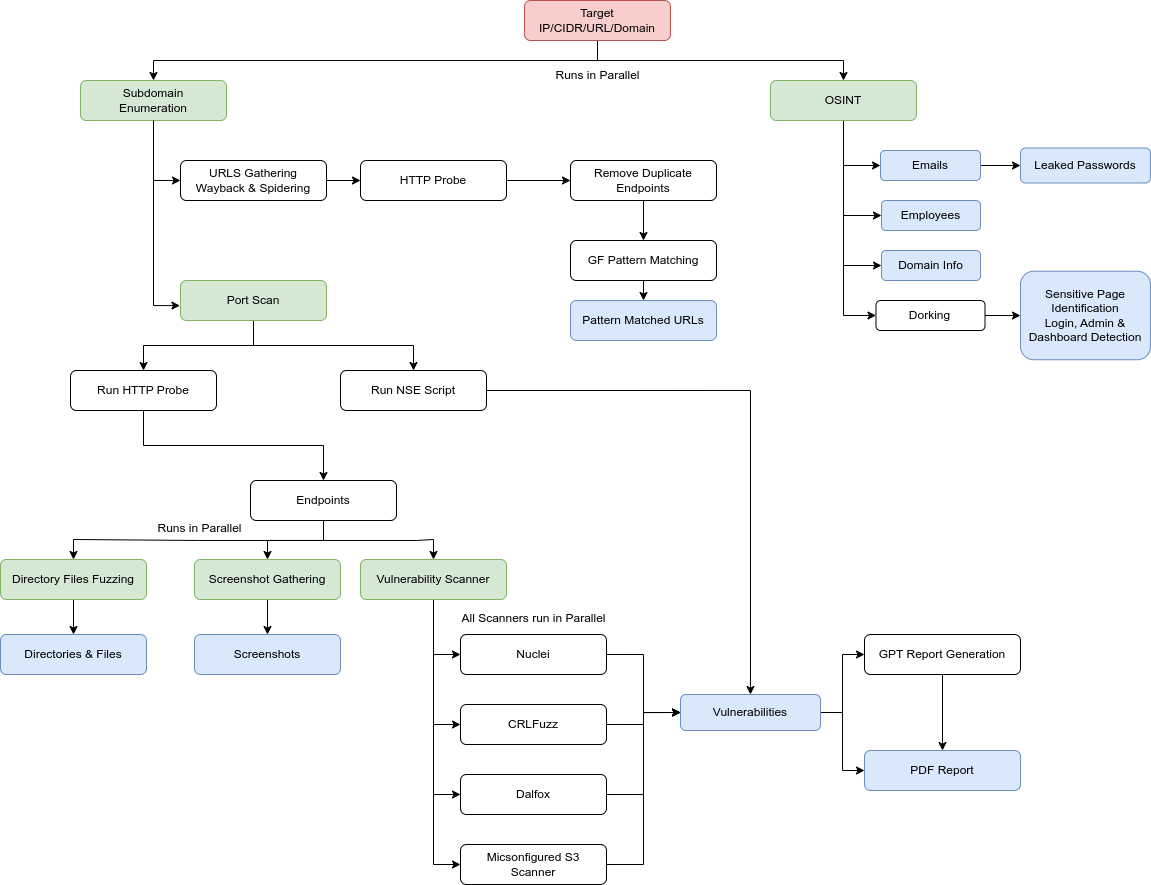 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 v35hr4j/cve-2022-1597
The plugin, used as a companion for the Discy and Himer themes, does not sanitise and escape a parameter on its reset password form which makes it…
 m4xsec/wp2shell-exploit-waf-bypass
WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab
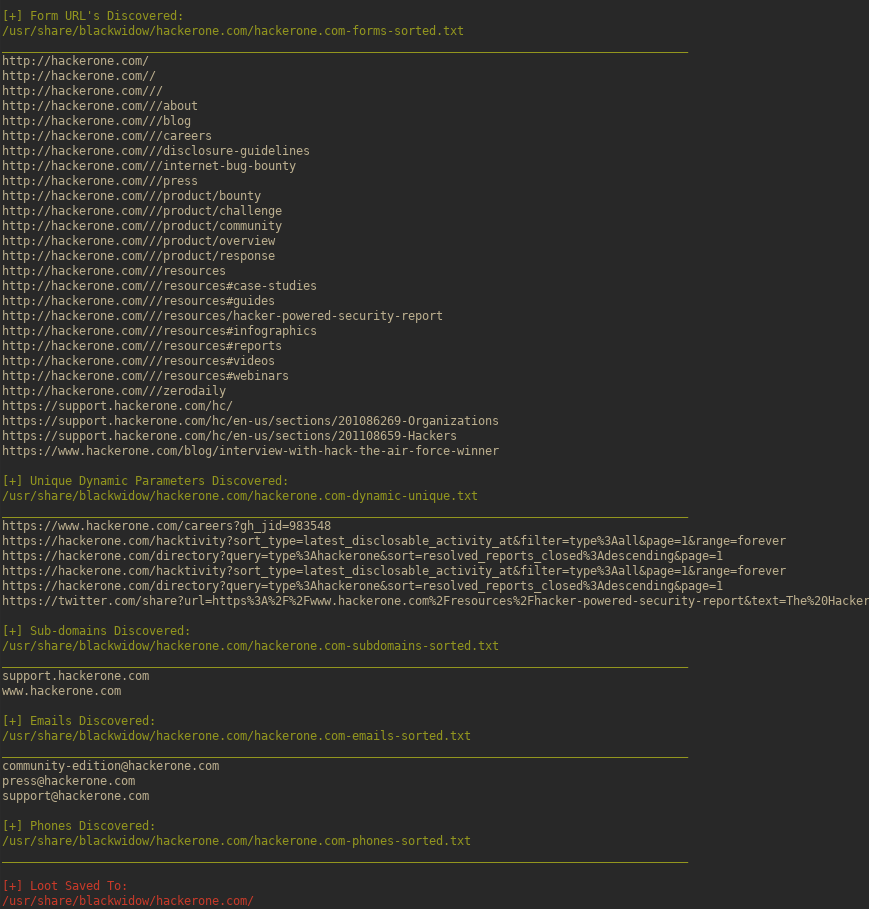 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
 hahwul/xspear
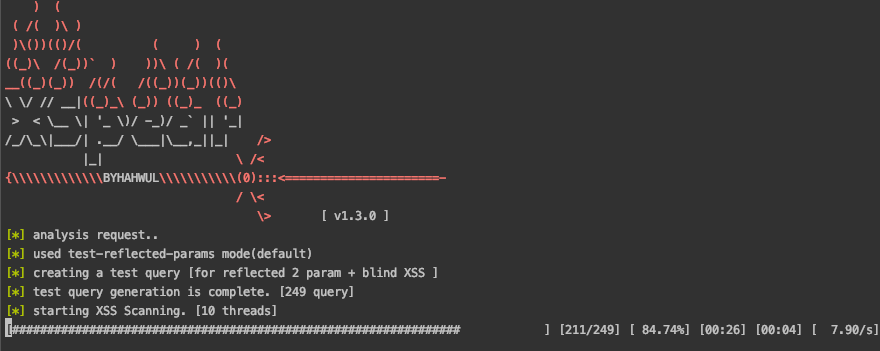
🔱 Powerfull XSS Scanning and Parameter analysis tool&gem
 proviesec/xss-payload-list
Curated collection of cross-site scripting payloads, polyglots, and injection test rules for web application penetration testing and bug bounty…
 zigrin-security/cakefuzzer
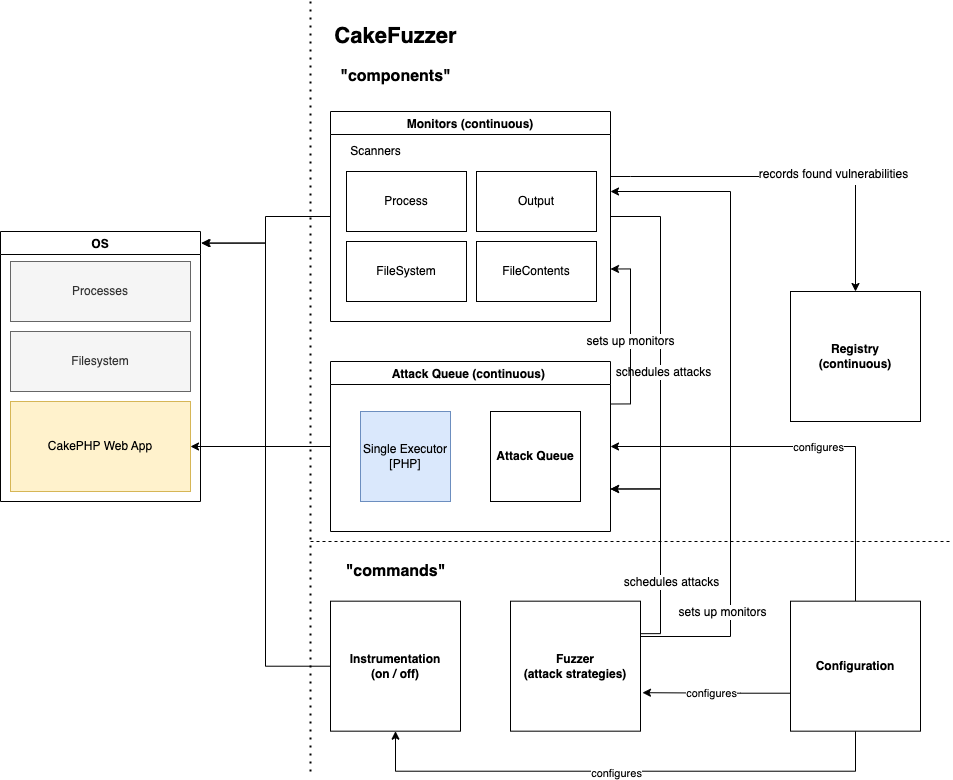
Cake Fuzzer is a project that is meant to help automatically and continuously discover vulnerabilities in web applications created based on specific…
 boreas37/cve-2026-64638-poc-xss2shell-
XSS2Shell (CVE-2026-64638) WordPress pre-auth XSS to RCE chain — PoC exploit + defensive audit tool + nuclei template
 jenkinsci/nuclei-plugin
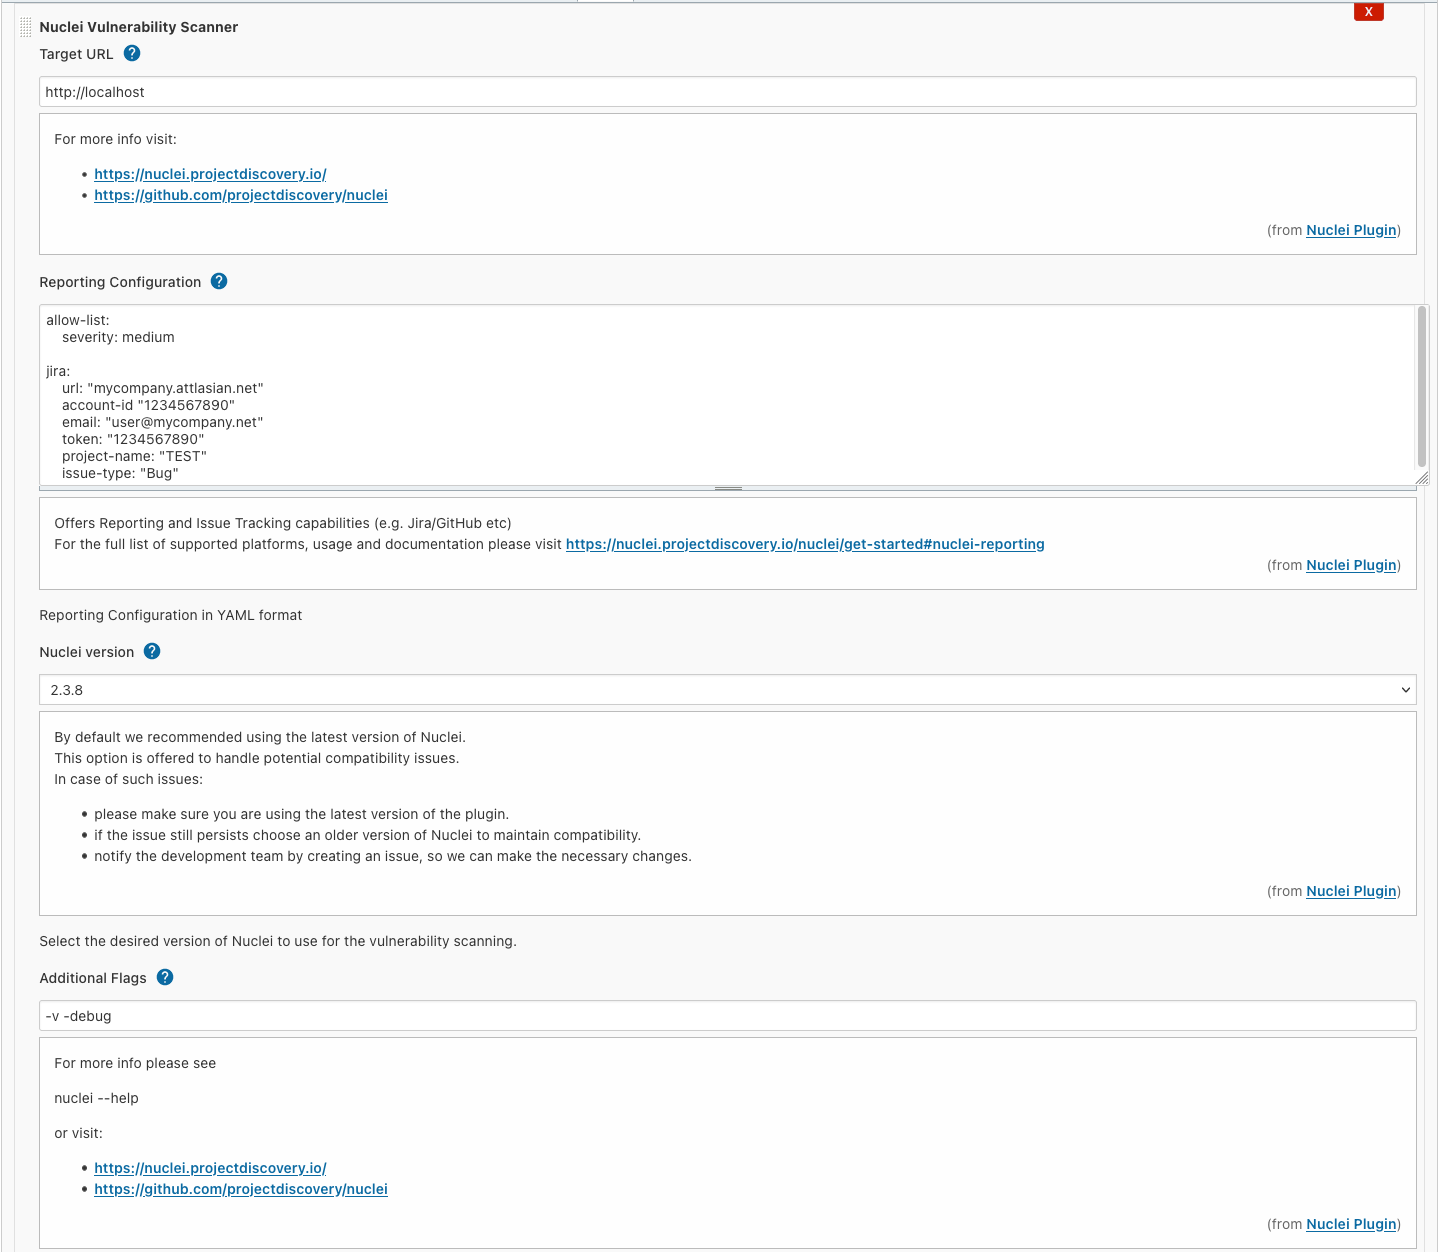
Nuclei is a fast tool for configurable targeted vulnerability scanning based on templates offering massive extensibility and ease of use.
 ekultek/pybelt
The hackers tool belt
 cyber-note/cve-2026-34835-black-box-analysis
A black-box (DAST) security analysis of CVE-2026-34835 focusing on external validation methodology, observable behavior, security impact, and…
 rxerium/cms-exploitation-campaign
Large Scale Exploitation Campaign against CMS devices reported in July 2026
 erman-bolukbasi/web-penetration-drupal
Penetration test of a Drupal web app — CVE-2018-7600 (Drupalgeddon 2) exploited using Nmap, Burp Suite & Metasploit | Internship @ BB CyberSec
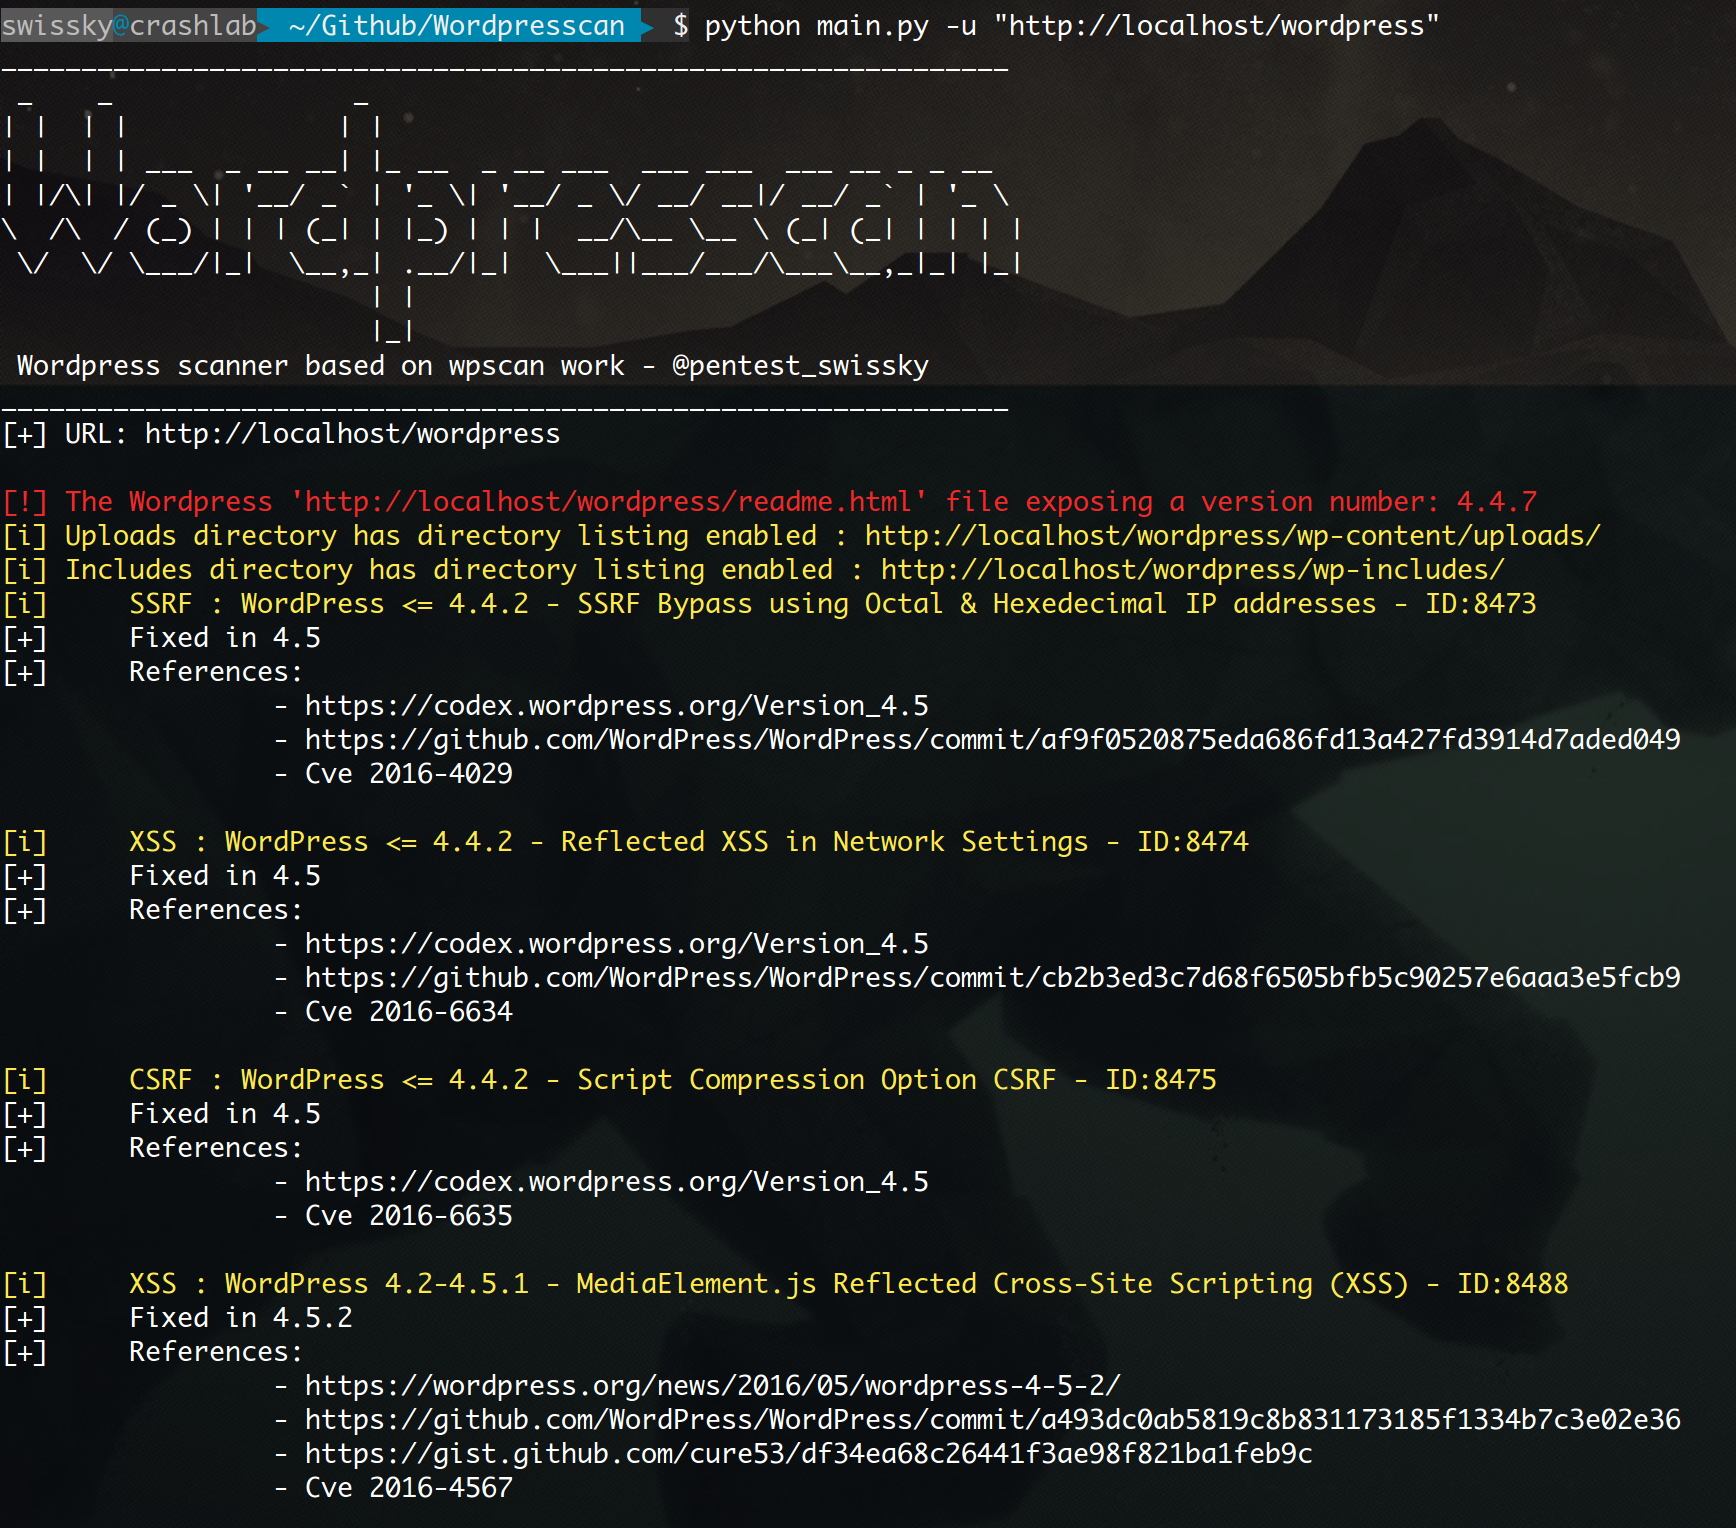 swisskyrepo/wordpresscan
WPScan rewritten in Python + some WPSeku ideas