

CVE-2021-43650
 openxp-research/cve-2021-43650
Webrun <= 3.6.0.42 SQLi
database-securityexploitationpenetration-testing+3
openxp-research/cve-2021-43650Webrun <= 3.6.0.42 SQLi
 z00nx/reversemap
Analyse SQL injection attempts in web server logs
 sqlmapproject/testenv
A collection of web pages vulnerable to SQL injection flaws
 ivanesk315/cve-2023-25157
Local GeoServer/PostGIS lab reproducing OGC Filter SQL injection (CVE-2023-25157/25158) with vulnerable, patched, and mitigated A/B test modes.
 fimtow/cve-2021-24750
Demonstration of the WP Visitor Statistics plugin exploit
 jfs-jfs/cve-2026-37068
Proof-of-concept exploit for CVE-2026-37068: arbitrary file write in Veno File Manager 4.4.9 via authenticated POST request to /vfm-admin/index.php.
 ahrixia/cve-2023-44813
mooSocial v3.1.8 is vulnerable to cross-site scripting on Invite Friend function.
 boroeurnprach/cve-2025-59057-poc
A XSS vulnerability exists in in React Router's meta()/<Meta> APIs in Framework Mode when generating script:ld+json tags which could allow arbitrary…
 shellkraft/cve-2024-27914
Reflected XSS exploit PoC for GLPI (CVE-2024-27914) targeting unauthenticated debug mode. Provides a malicious link to trigger XSS in administrator's…
 raghavd3v/crlfsuite
The most powerful CRLF injection (HTTP Response Splitting) scanner.
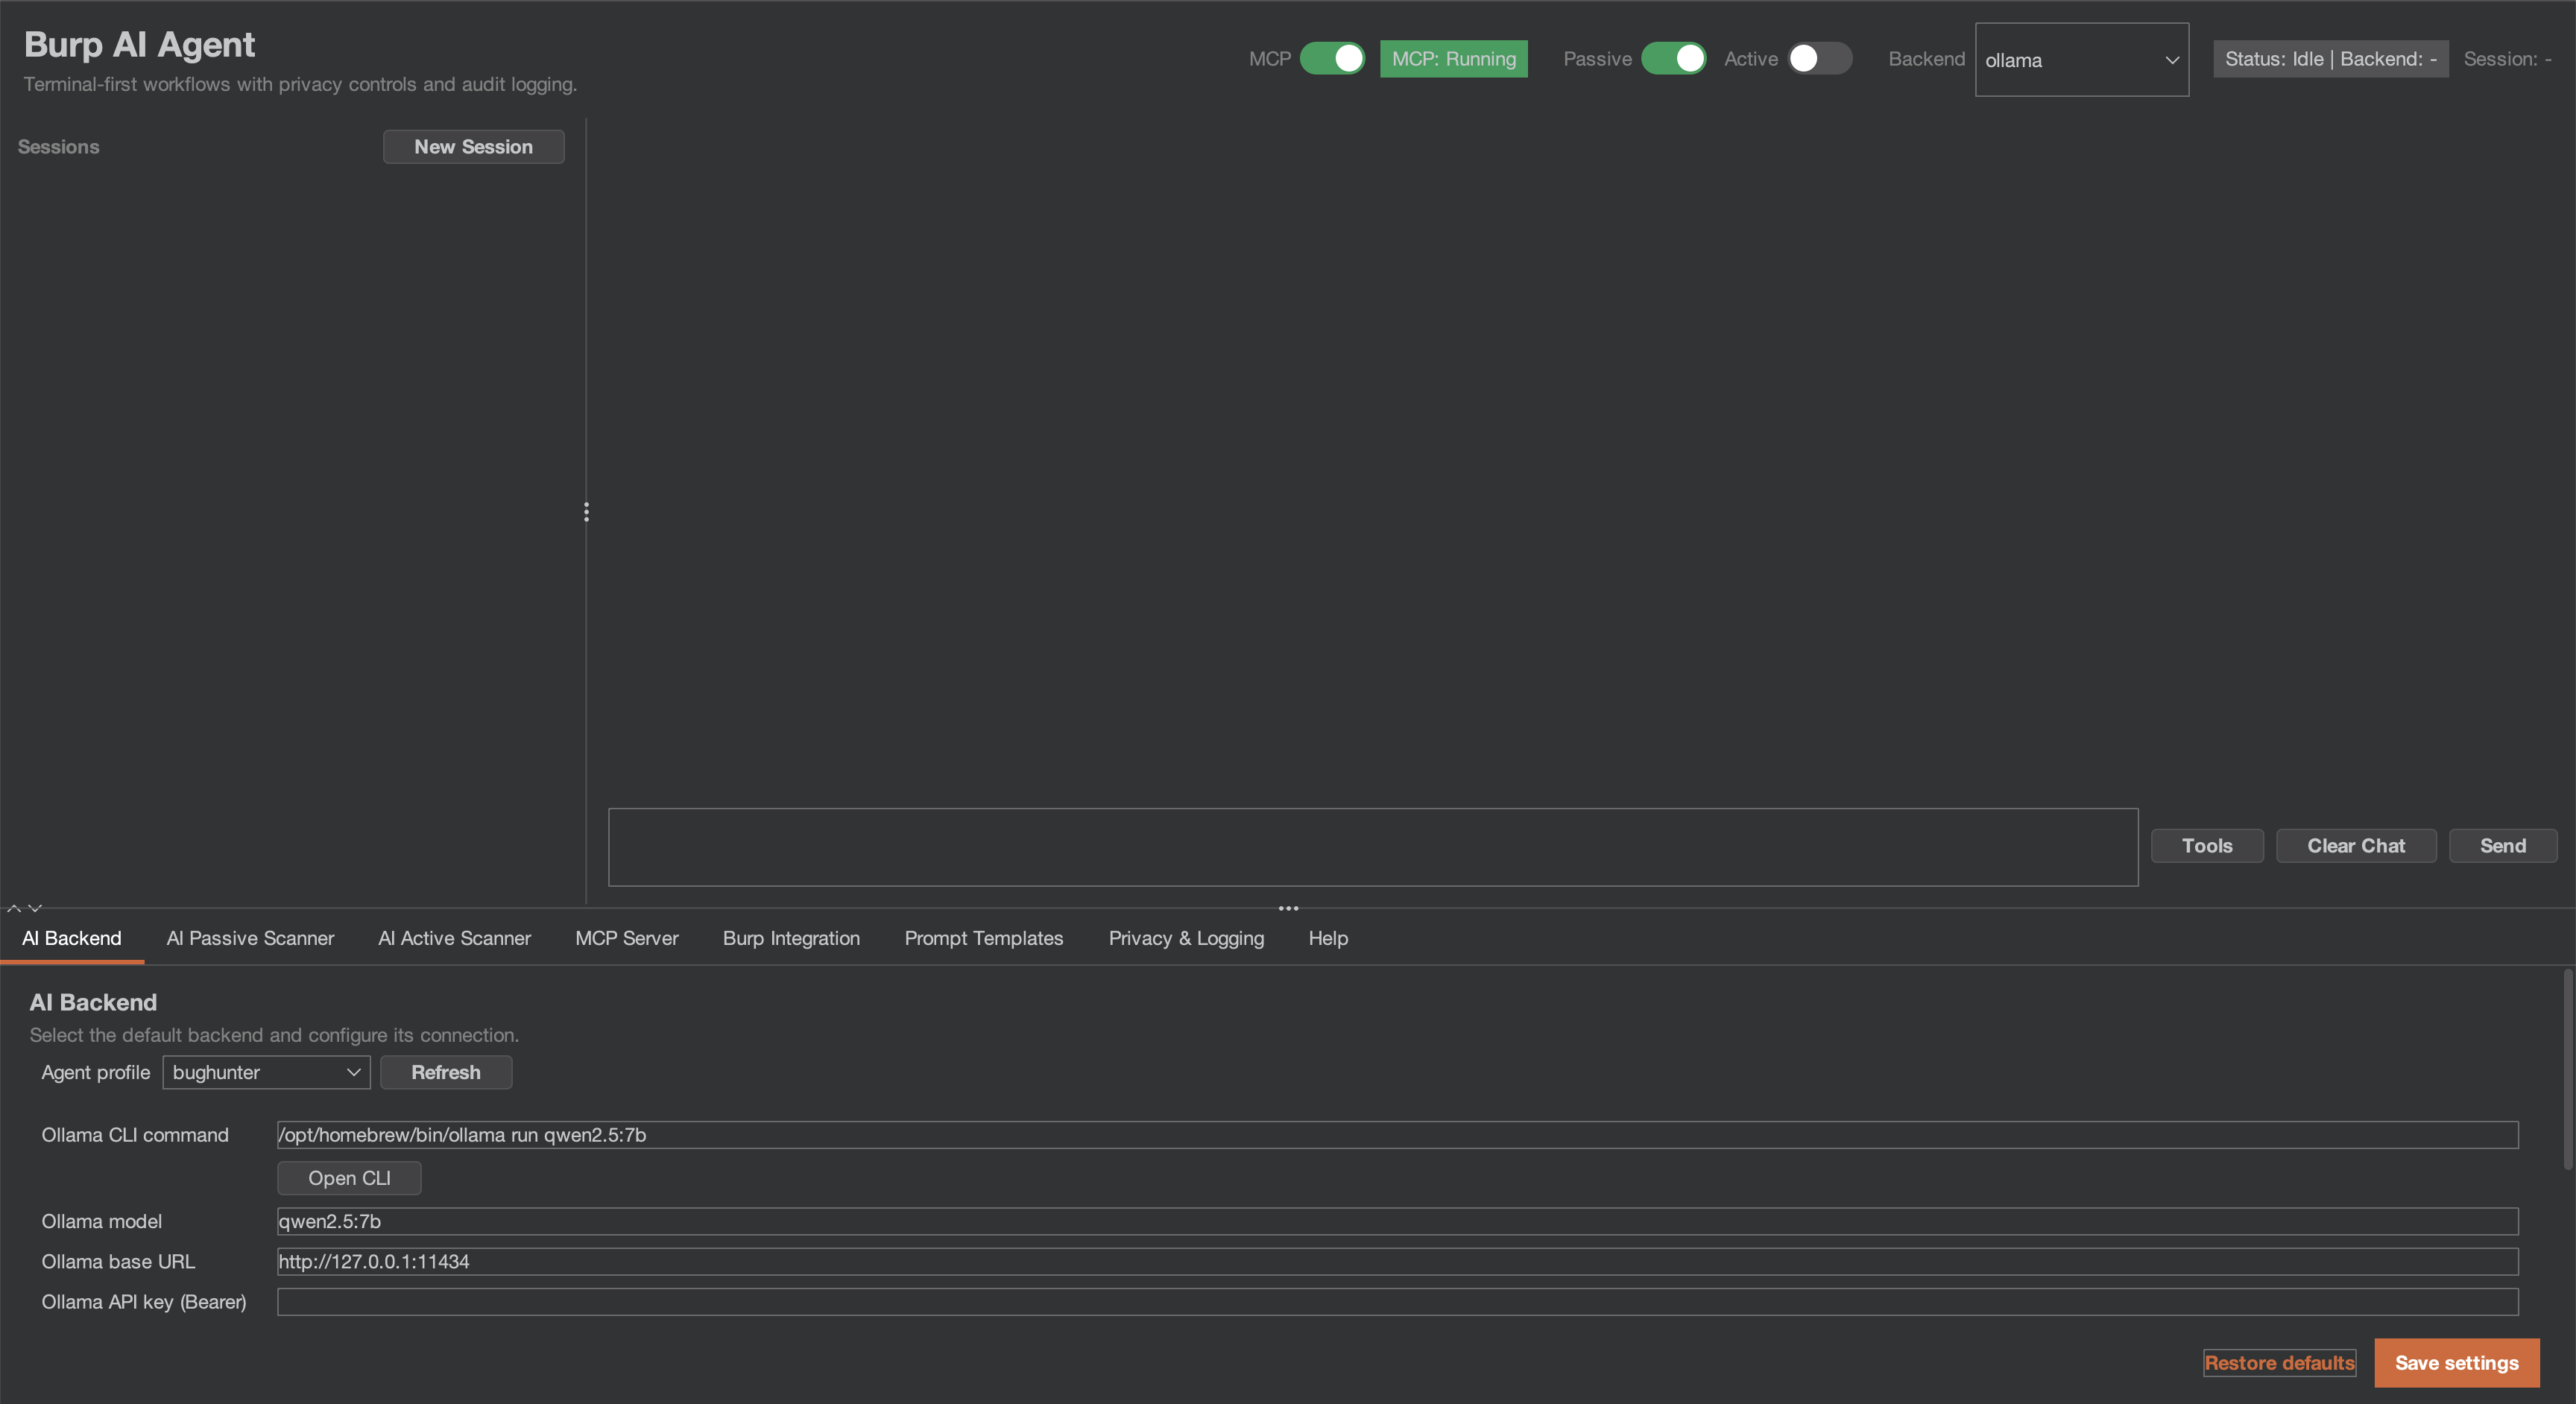 six2dez/burp-ai-agent
Burp Suite extension that adds built-in MCP tooling, AI-assisted analysis, privacy controls, passive and active scanning and more
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
 0ca/boxpwnr
A modular framework for benchmarking LLMs and agentic strategies on security challenges across HackTheBox, TryHackMe, PortSwigger Labs, Cybench,…
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
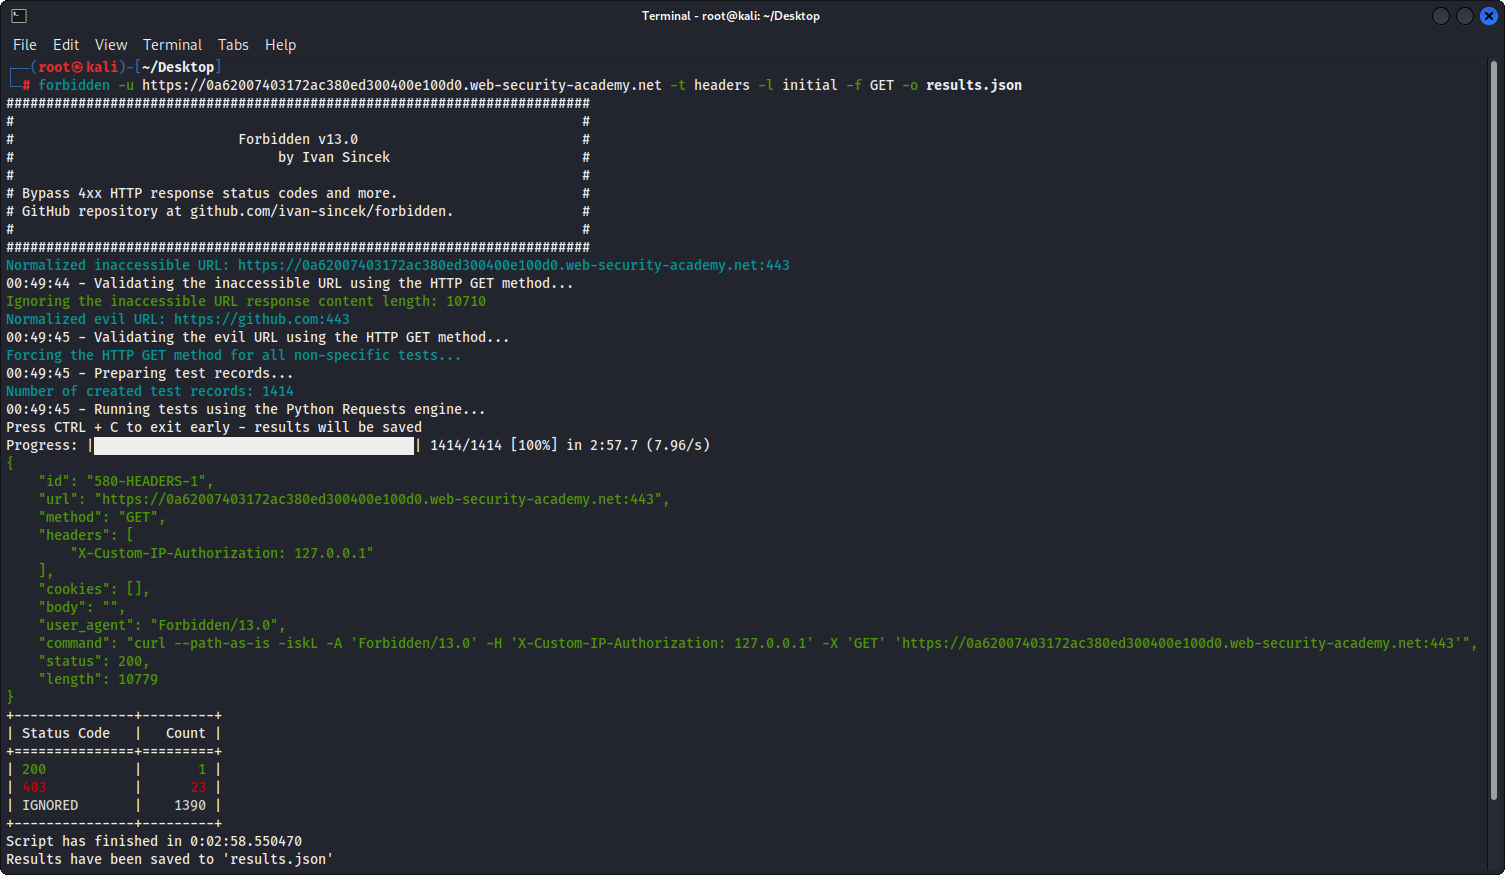 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 fl0ydsec/cve-2026-15989
Mass scanner and exploit for CVE-2026-15989, the unauthenticated privilege escalation in Super Forms <= 6.3.316 that creates administrator accounts…
 shakur1314/cve-2022-22965-spring4shell-security-operations-analysis
A comprehensive Security Operations Centre (SOC) incident response simulation demonstrating threat detection, triage, analysis, and mitigation of the…