
sqlmap-ai
 atiilla/sqlmap-ai
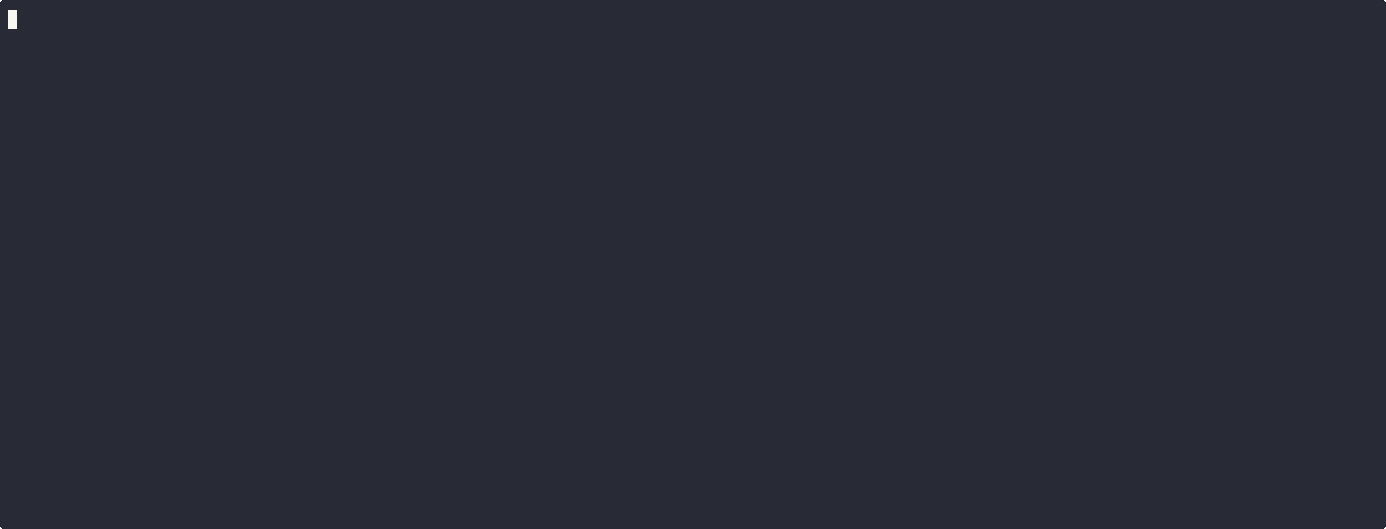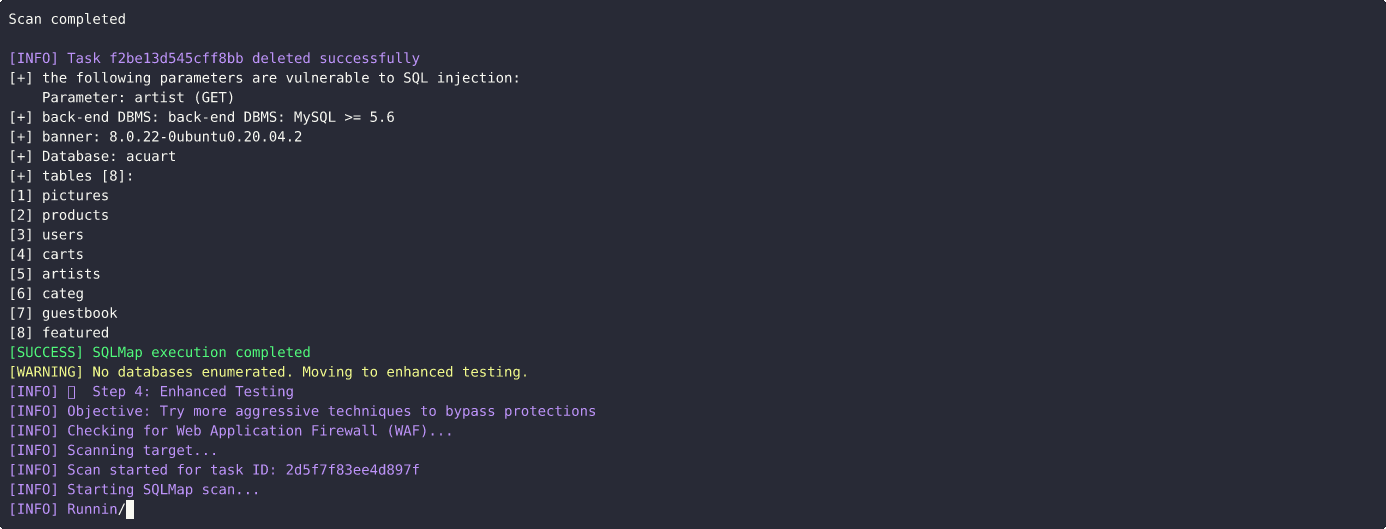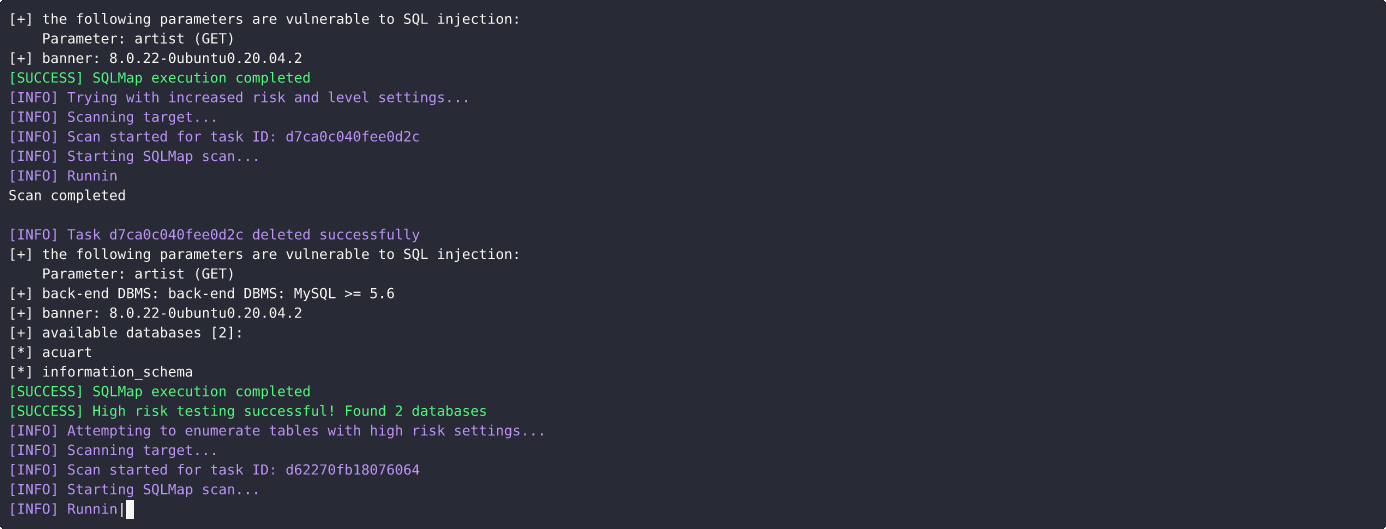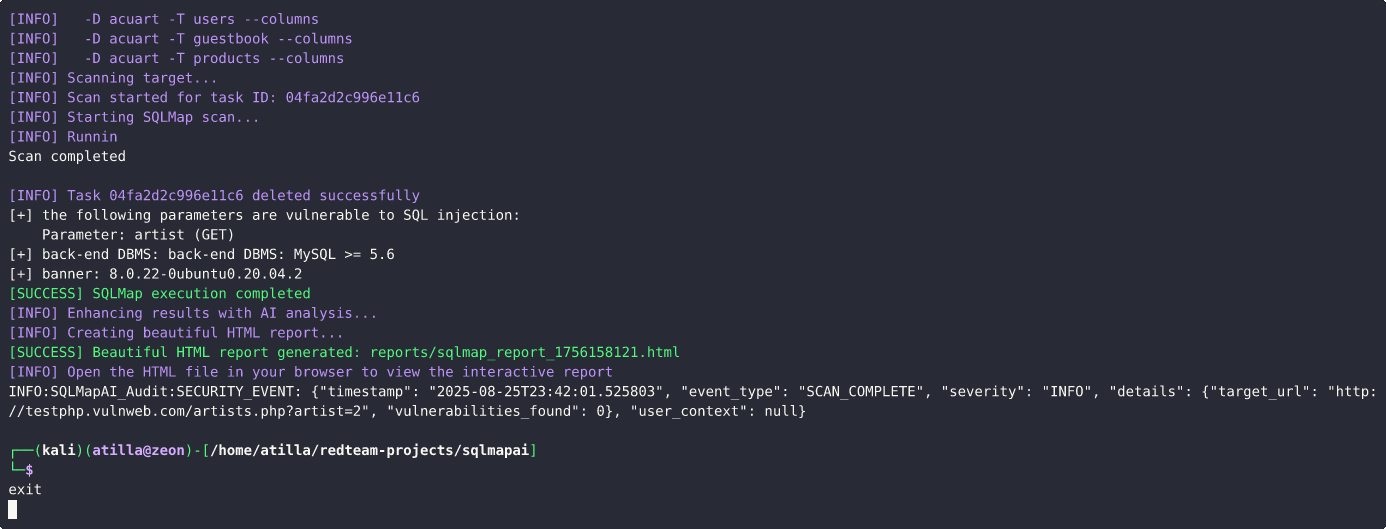
This script automates SQL injection testing using SQLMap with AI-powered decision making.
payload-generationpenetration-testingvulnerability-scanners+3
449
atiilla/sqlmap-aiThis script automates SQL injection testing using SQLMap with AI-powered decision making.
 shaunmclernon/ghostcat-verification
Learnings on how to verify if vulnerable to Ghostcat (aka CVE-2020-1938)
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
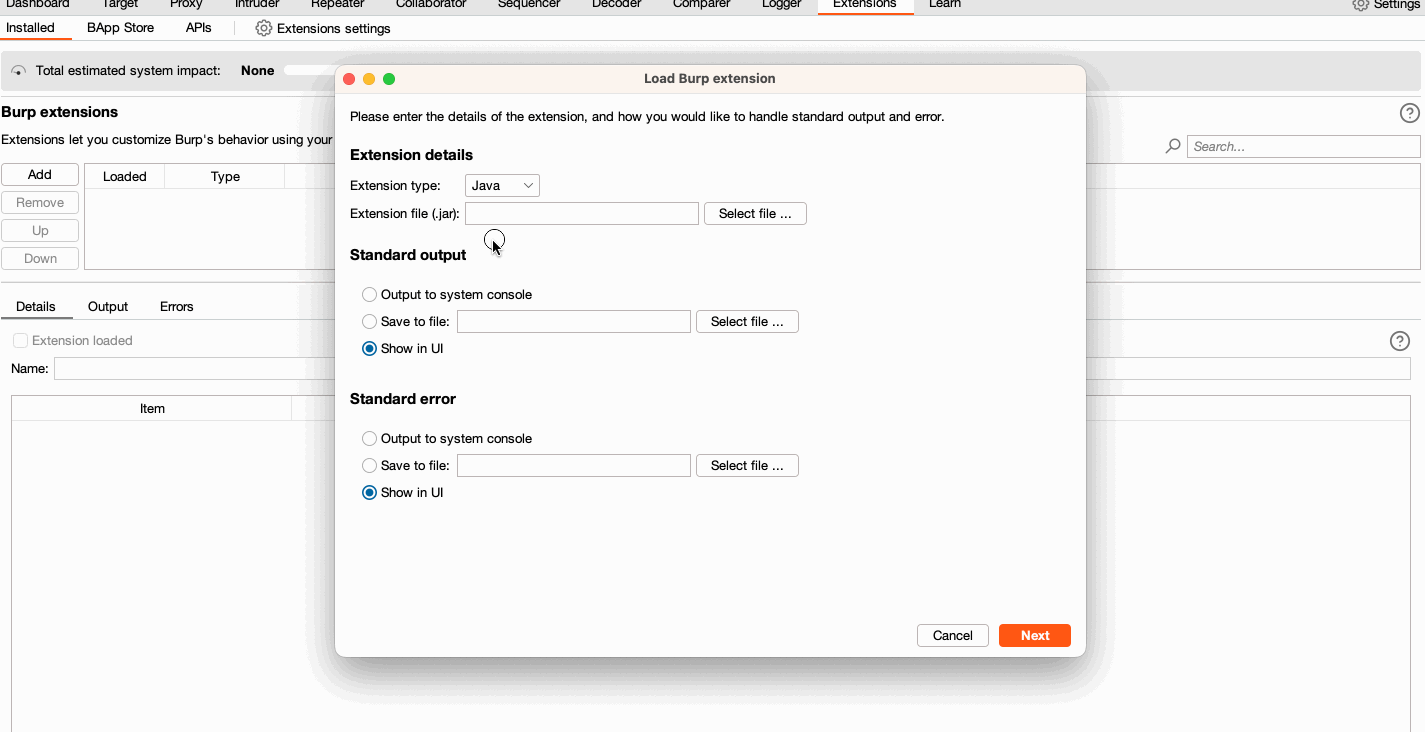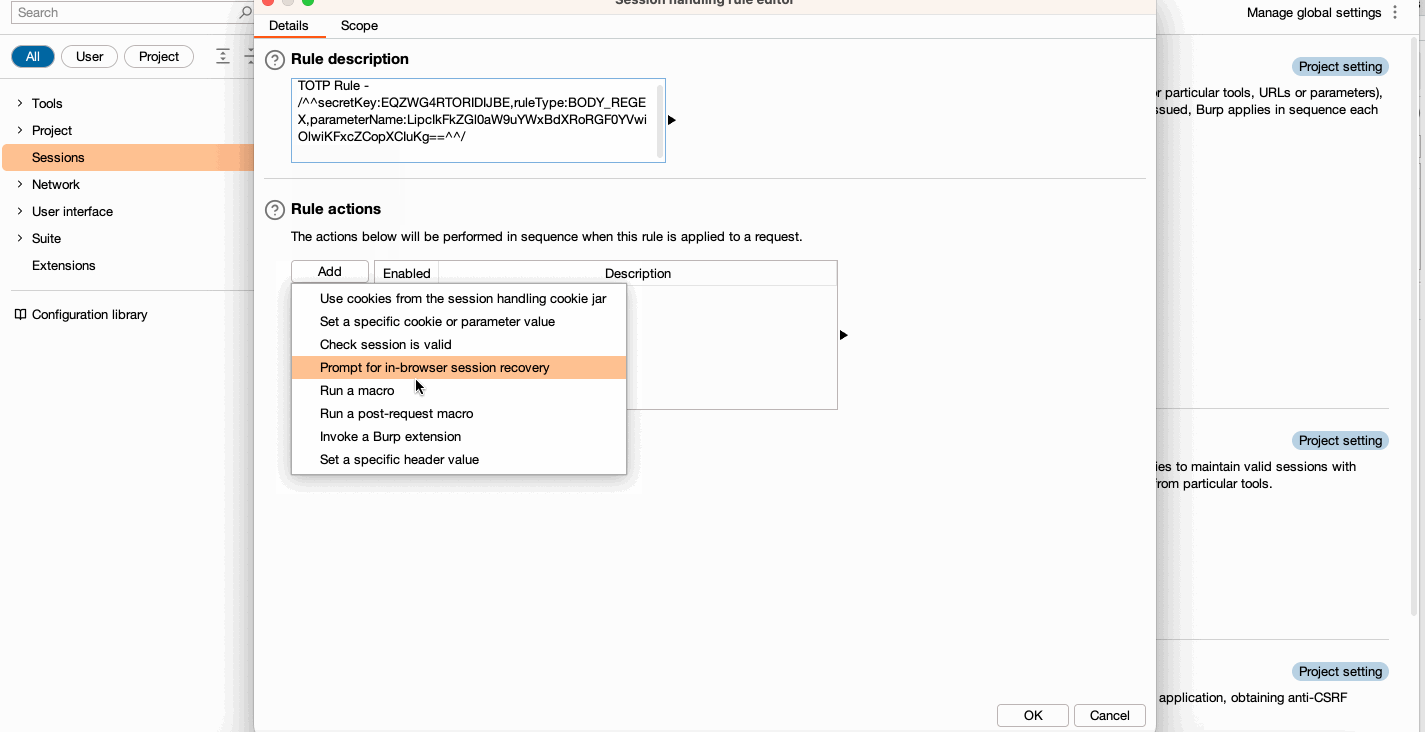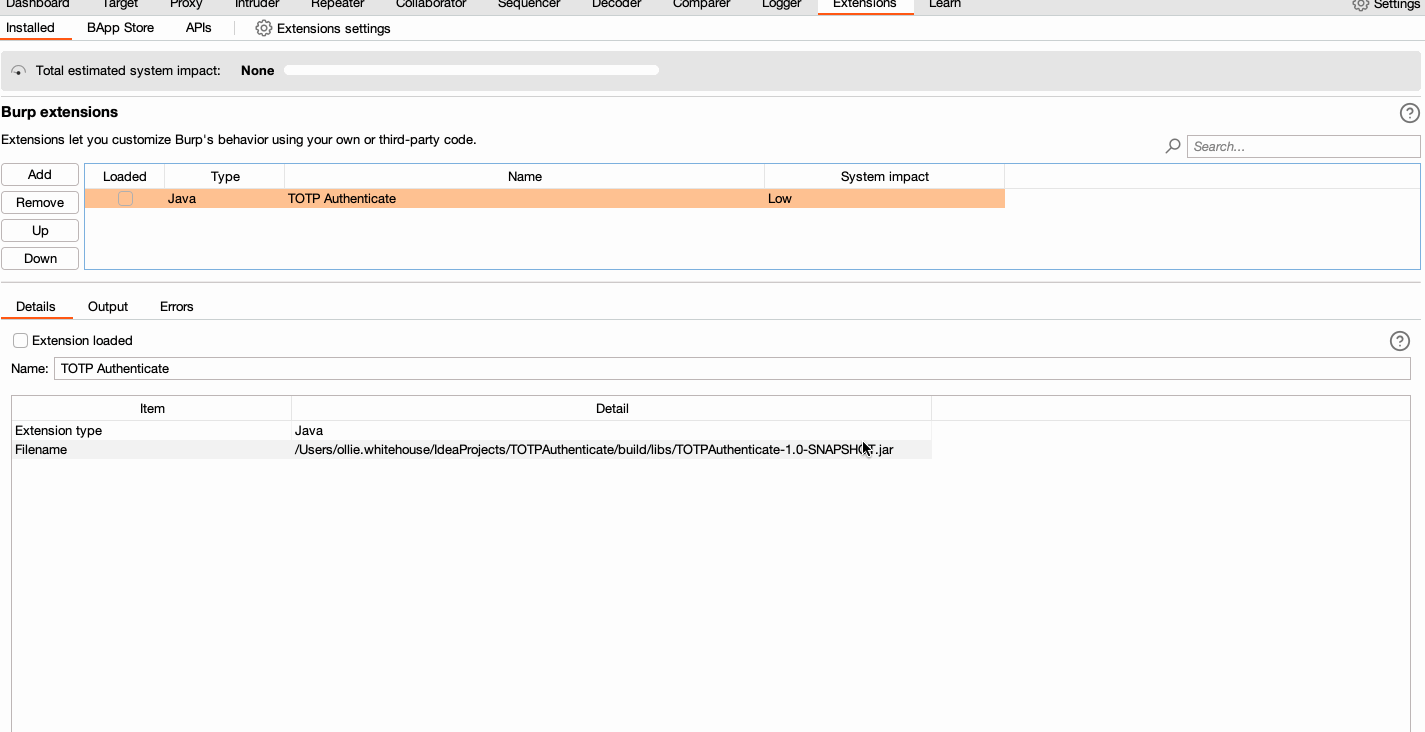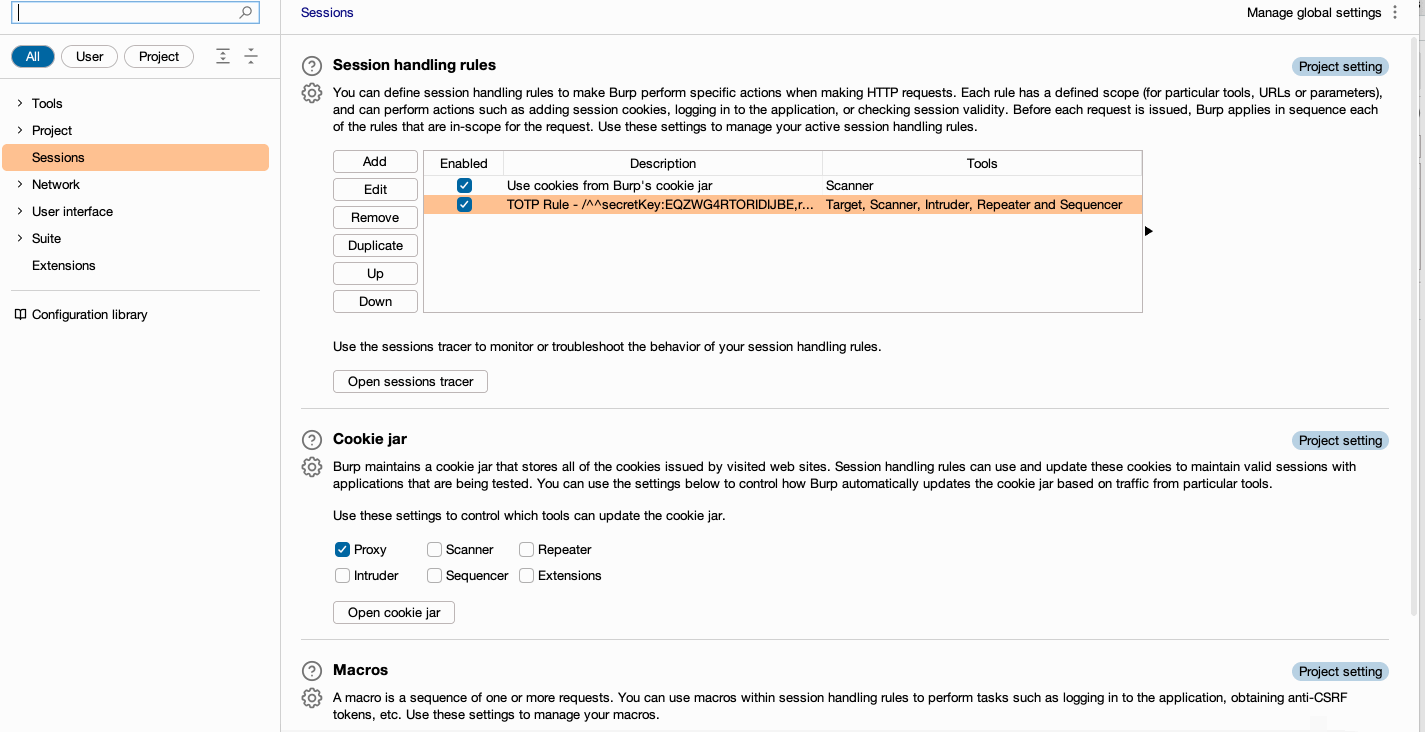 hannah-portswigger/totpauthenticate
This extension, for Burp Suite Enterprise Edition, utilizes session handling rules to provide a TOTP token to outgoing requests.
 0xb1lal/cve-2025-29927
Advisory and information hub for the Next.js middleware authorization bypass CVE-2025-29927, including a link to technical analysis and details.
 bevennyamande/cve-2024-10557
A CSRF POC for Updating the Profile of a Hospital leading to Account Takeover
 chaitanyagarware/cve-2026-54520
Public advisory landing page documenting CVE-2026-54520, a high-severity path traversal vulnerability in ai-agent-automation's workflow executor,…
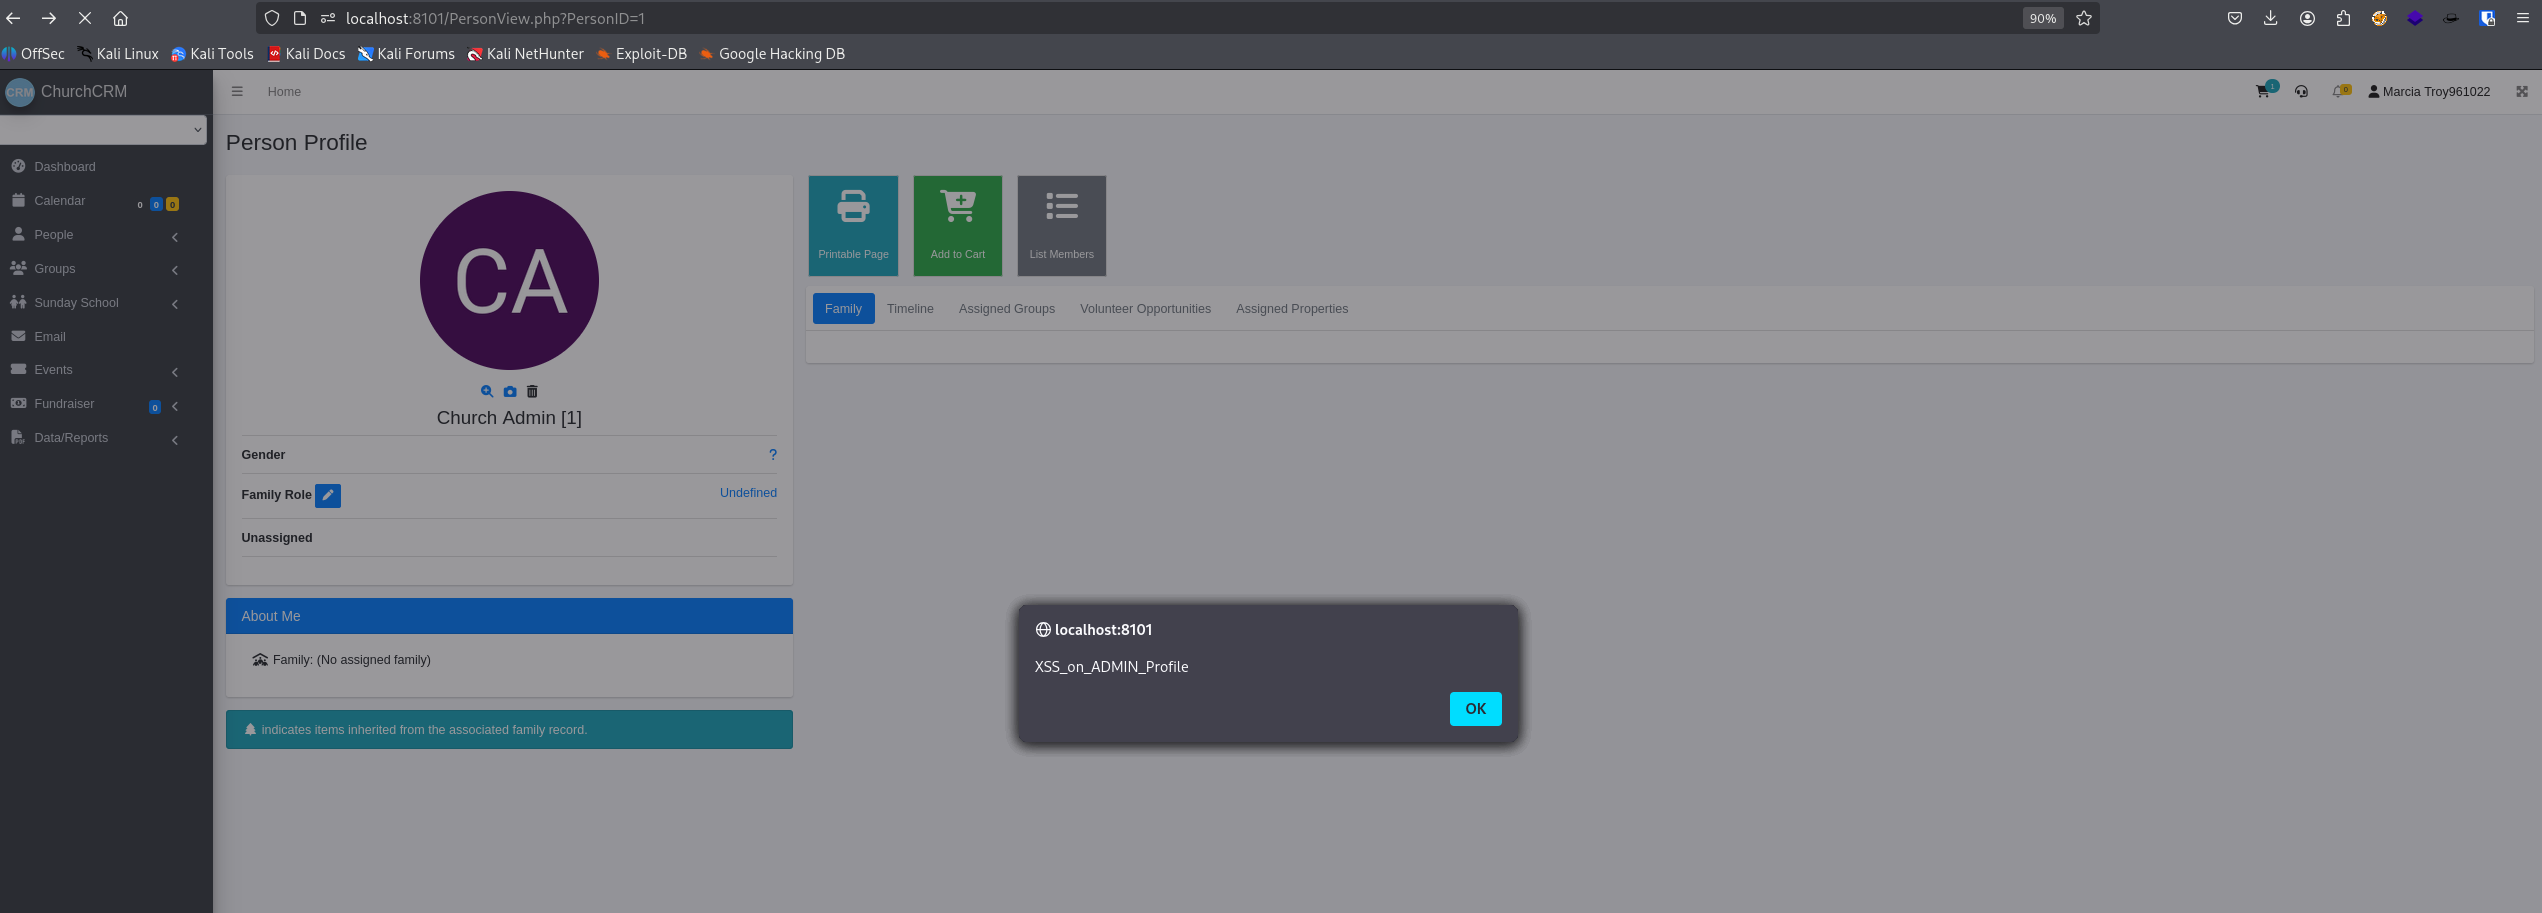 lukasz-rybak/cve-2025-67875
CVE-2025-67875 - ChurchCRM has stored XSS via Person Property Assignment Leading to Admin Session Hijacking
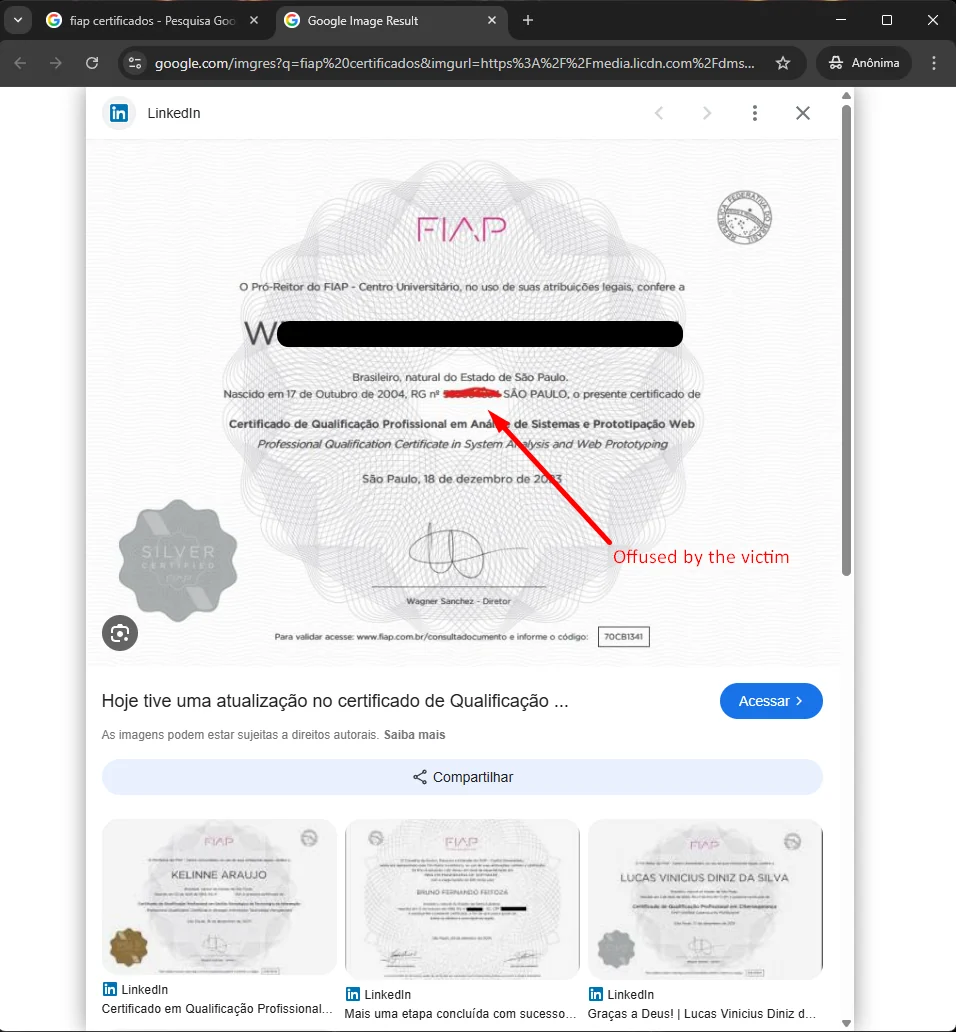 rrespxwnss/cve-2026-36374
Demonstrates an unauthenticated enumeration vulnerability in a public certificate lookup endpoint, exposing personal data such as CPF and RG.…
 ysah44/limbas-4.3.36.1319-is-vulnerable-to-cross-site-scripting-xss-
CVE-2022-28454
 sexyshoelessgodofwar/cve-2025-58780
Disclosure of a SQL injection vulnerability in ScienceLogic web platform (index.em7) affecting versions prior to 12.1.1, with mitigation guidance and…
 lukasz-rybak/cve-2026-23499
CVE-2026-23499 - Saleor vulnerable to stored XSS via Unrestricted File Upload
 xibhi/cve-2025-26206
A critical Cross-Site Request Forgery (CSRF) vulnerability in Sell Done Storefront v.1.0. Discovered by B. Sibhi
 buraksevben/cve-2024-24135
Proof-of-concept exploit for CVE-2024-24135, a cross-site scripting vulnerability in Product Inventory with Export to Excel. Demonstrates the XSS…
 halildeniz/pathfinder
Python-based web reconnaissance tool that extracts site metadata, DNS records, subdomains, firewall names, technologies, and certificate details for…
 d0n601/cve-2025-12721
g-FFL Cockpit <= 1.7.1 - Missing Authorization to Unauthenticated Information Exposure
 l3ragio/cve-2022-29361_werkzeug_client-side-desync-to-xss
Proof-of-concept exploit for CVE-2022-29361, demonstrating client-side desync to XSS in Werkzeug. Tested on Chromium.
 mbanyamer/cve-2026-24854-churchcrm-6.7.2-authenticated-numeric-sql-injection
Proof-of-concept demonstrating authenticated numeric SQL injection in ChurchCRM before 6.7.2, enabling logic manipulation to bypass WHERE clauses and…