

security-research
 mirchr/security-research
Security Research
curated-resourcesexploitationpassword-cracking+5
mirchr/security-researchSecurity Research
 nu11secur1ty/complete-google-dorks
Curated collection of Google dork queries for advanced search engine reconnaissance, uncovering exposed databases, configuration files, admin panels,…
 foospidy/payloads
Git All the Payloads! A collection of web attack payloads.
 taielab/awesome-hacking-lists
A curated collection of top-tier penetration testing tools and productivity utilities across multiple domains. Join us to explore, contribute, and…
 sqlmapproject/testenv
A collection of web pages vulnerable to SQL injection flaws
 tstillz/webshell-analyzer
Web shell scanner and analyzer.
 f5devcentral/cve-2020-5902-ioc-bigip-checker
Local F5 BIG-IP script that scans for Indicators of Compromise (IoCs) related to CVE-2020-5902, checking logs, files, and system integrity to detect…
 onapsis/onapsis-mandiant-cve-2025-31324-vuln-compromise-assessment
CVE-2025-31324 & CVE-2025-42999 vulnerability and compromise assessment tool
 respondiq/jsp-webshell-scanner
🔍 A simple Bash script to detect malicious JSP webshells, including those used in exploits of SAP NetWeaver CVE-2025-31324.
 mhils/honeyproxy
This project is now part of @mitmproxy.
 josue87/burpmetafinder
Burp Suite extension for extracting metadata from files
 jvr2022/cve-2026-29786
Proof-of-concept demonstrating a hardlink path traversal in the tar npm package, allowing overwrite of files outside the extraction directory via…
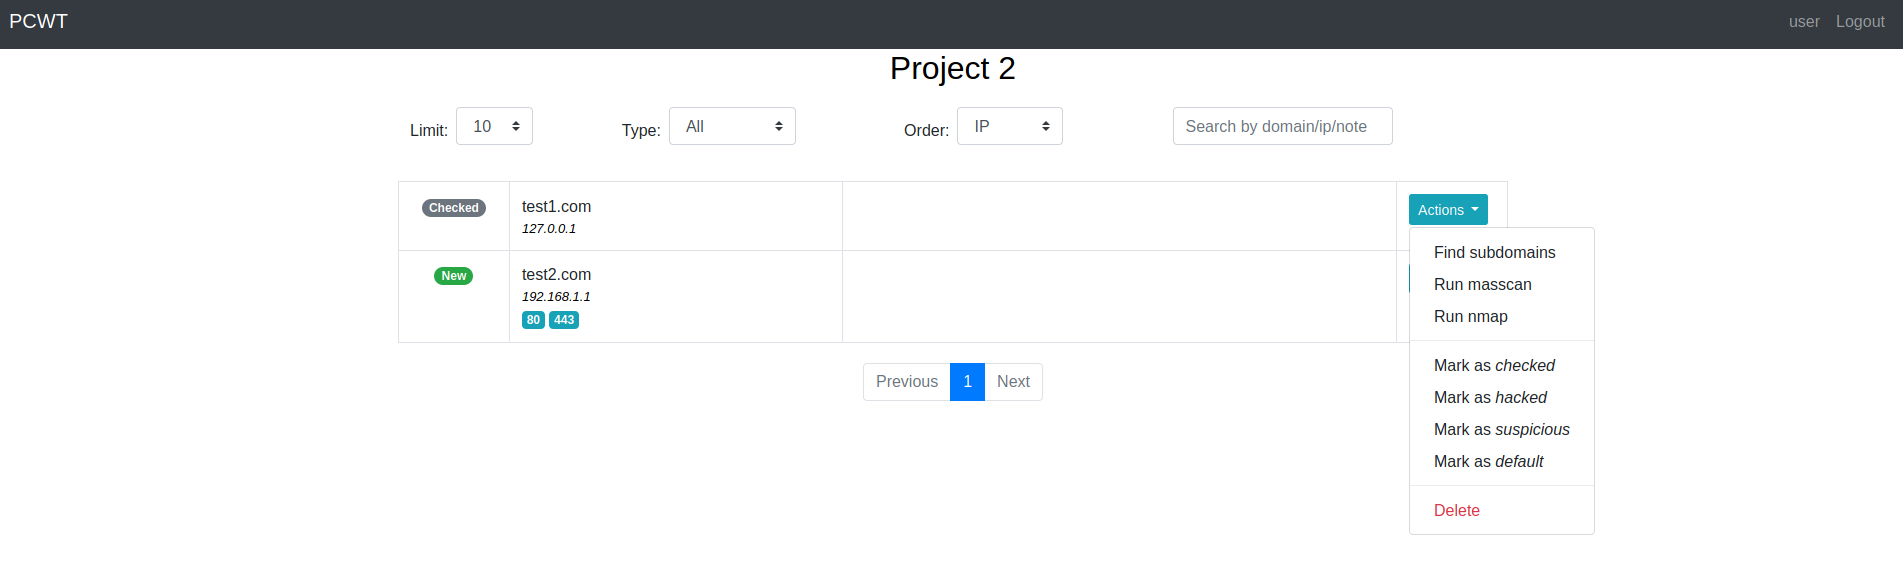 ascr0b/pcwt
Web-based project management interface for penetration testing and bug bounty workflows, automating port scanning with Nmap/Masscan and subdomain…
 pescada-dev/cve-2025-61506
Unrestricted File Upload DoS Vulnerability discovered in MediaCrush thru 1.0.1(CVE-2025-61506)
 saykino/cve-2025-56223
Documentation of CVE-2025-56223, a denial-of-service vulnerability in Ascertia SigningHub's Upload Document API, allowing unrestricted file uploads…
 saykino/cve-2025-66838
Documentation of CVE-2025-66838: a rate-limiting vulnerability in ARIS file upload API allowing authenticated remote attackers to cause denial of…
 amitlttwo/cve-2022-2414-proof-of-concept
A flaw was found in pki-core. Access to external entities when parsing XML documents can lead to XML external entity (XXE) attacks. This flaw allows…
 rnsss/cve-2021-43798-poc
Proof-of-concept exploit for Grafana 8.x arbitrary file read vulnerability (CVE-2021-43798), allowing retrieval of sensitive files via crafted URL.